
GoCD_PoC_Supply_Chain_Attack
 higorgabrieldcf/gocd_poc_supply_chain_attack
CVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
educationexploitationpayload-generation+7
2
higorgabrieldcf/gocd_poc_supply_chain_attackCVE-2021-43287 CVE-2021-43288 CVE-2021-43289 CVE-2021-43290
 hackspeak/cve-2026-64561
Zapscape (CVE-2026-64561) KVM/x86 shadow MMU UAF guest-to-host escape PoC mirror — V4bel/@v4bel, MIT; for authorized security testing
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
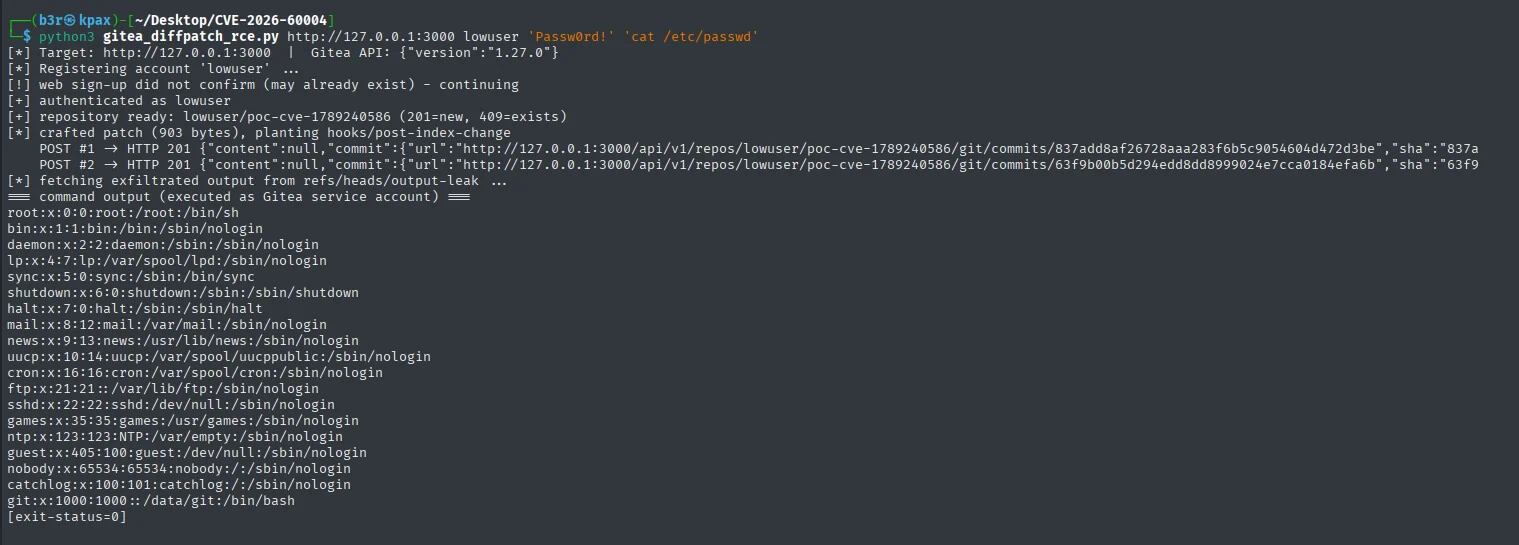 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 bl0odz/jfrog_cve-2026-65615-byglm
JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).
 shivammittal2403/cve-2026-59827-metabase-cyber-range
Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 pauldechassey/cve-2026-21636
Proof-of-concept demonstrating a Node.js permission model bypass (CVE-2026-21636) that allows network access via undici/fetch to local services,…
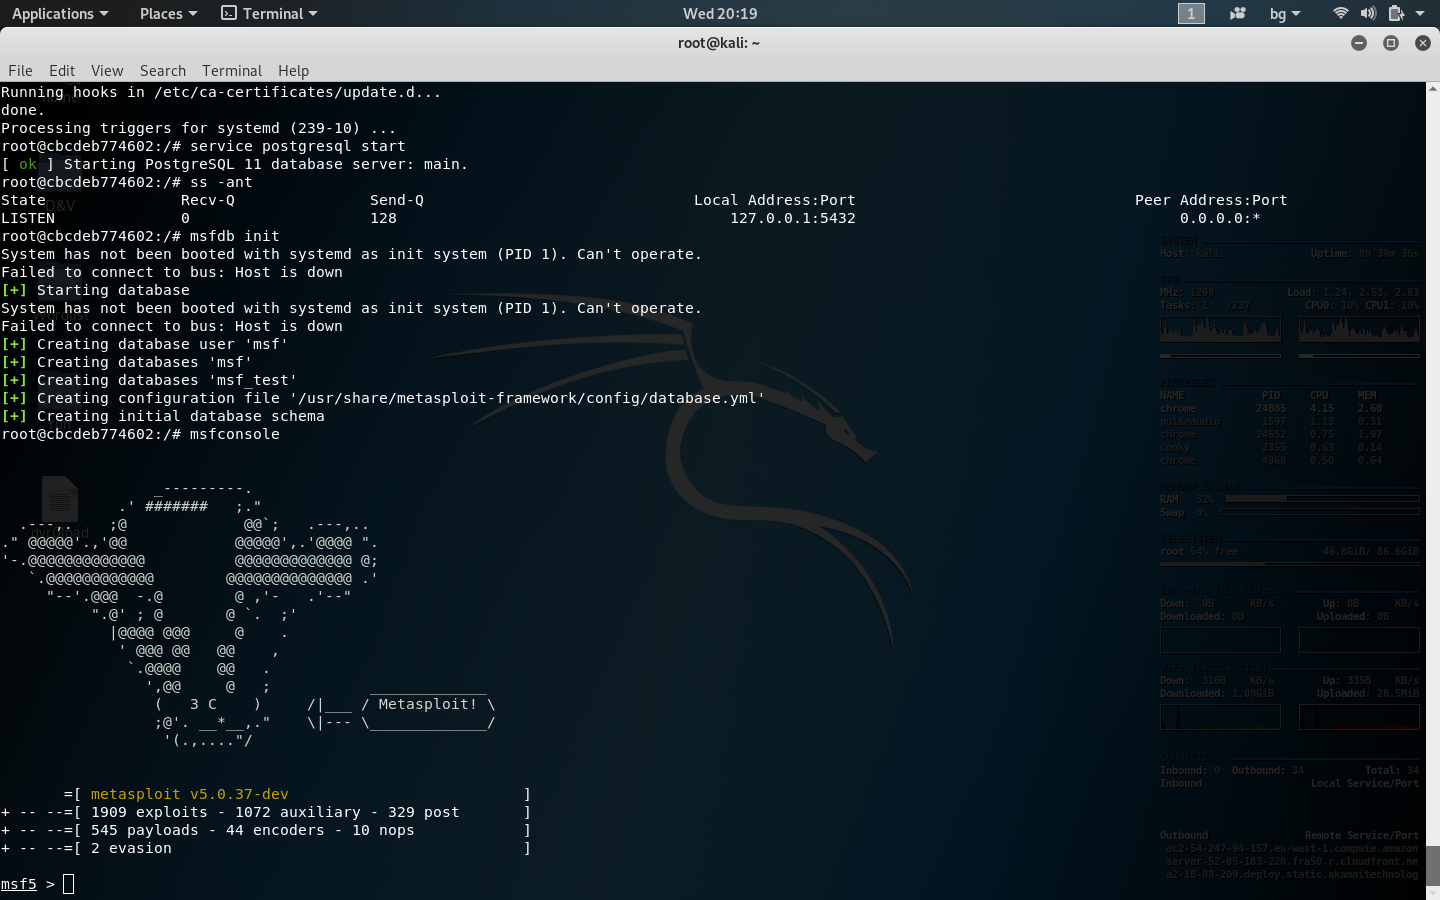 nu11secur1ty/kali-linux-docker
kali-linux-docker
 rianjuniorsf/exploit-js2py
The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.
 gregaskew/speculativeexecutionassessment
Assesses a system for the "speculative execution" vulnerabilities described in CVE-2017-5715, CVE-2017-5753, CVE-2017-5754
 cisagov/esxiargs-recover
A tool to recover from ESXiArgs ransomware