

gvisor
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
cloud-infrastructure-securitycloud-securitycontainer-escape+4
19.9k
google/gvisorSandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
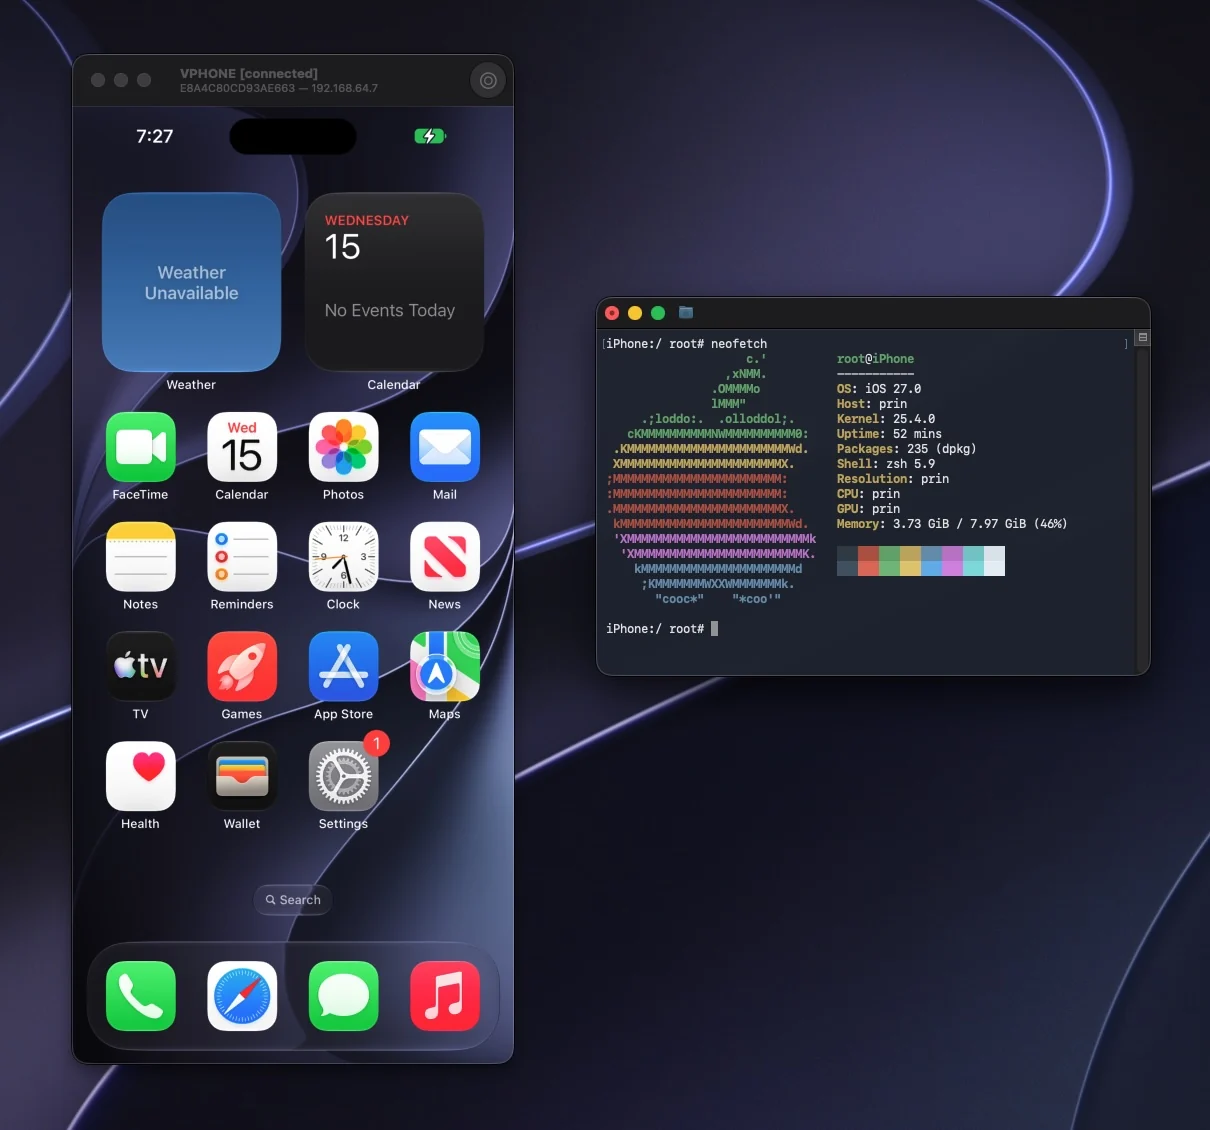 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 microsoft/secureboot_objects
Microsoft's curated repository of secure boot objects (KeK, Db, Dbx) for firmware and runtime, enabling transparent revocation updates and…
 cypherpunkarmory/userland
Main UserLAnd Repository
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 microsoft/mxc
Policy-driven, layered isolation and containment
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…
 anthropics/oss-scanner
Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 openedx/codejail
Secure code execution
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd