
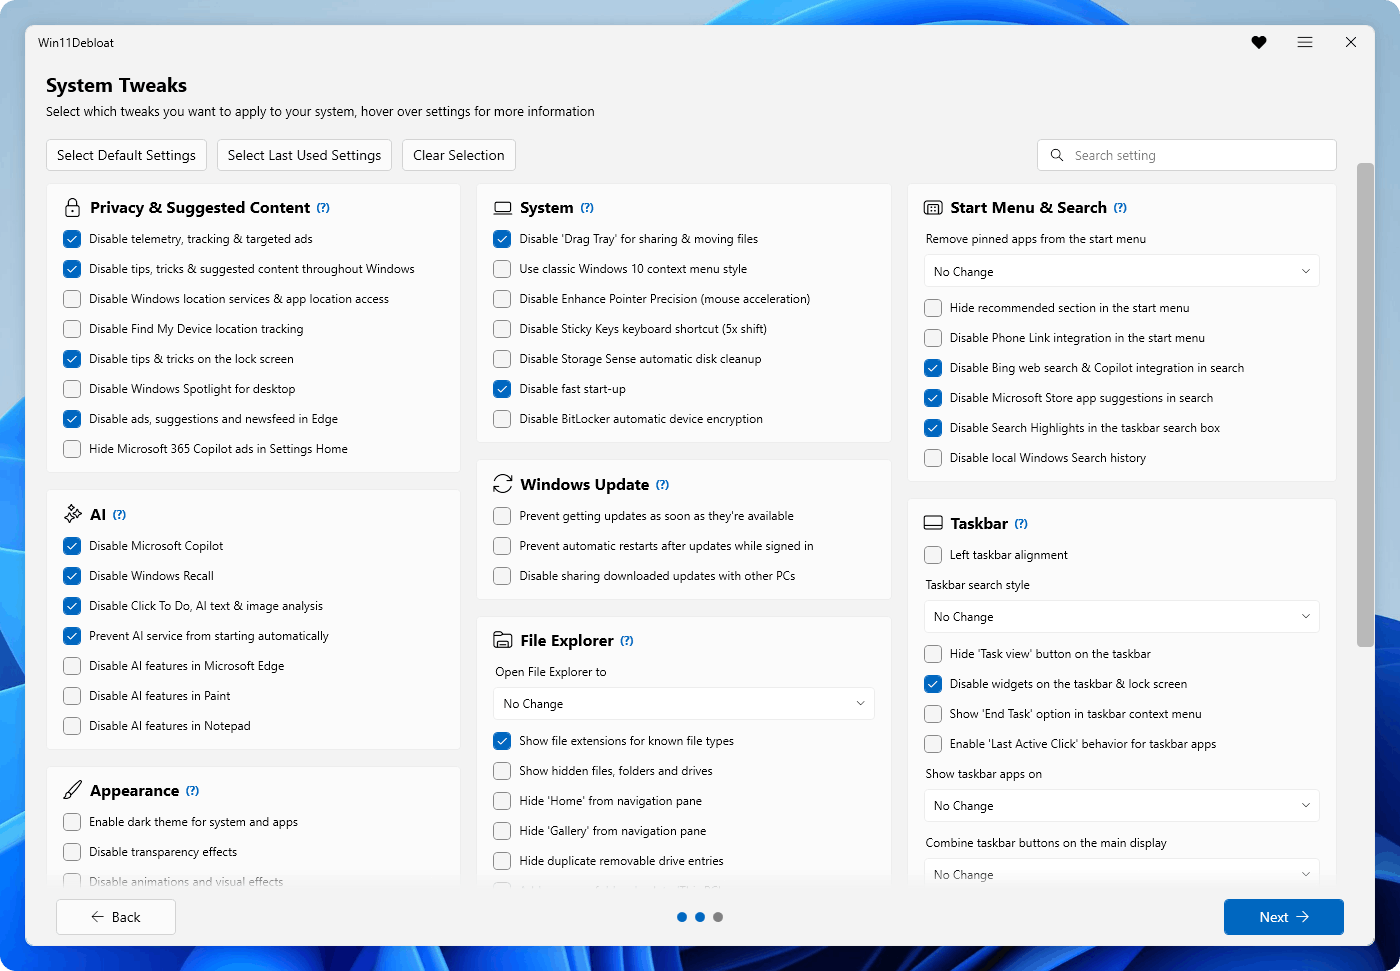
Win11Debloat
 raphire/win11debloat
A simple, lightweight PowerShell script that allows you to remove pre-installed apps, disable telemetry, as well as perform various other changes to…
general-purpose-utilitiesprivacyscripting-automation+1
61.0k
raphire/win11debloatA simple, lightweight PowerShell script that allows you to remove pre-installed apps, disable telemetry, as well as perform various other changes to…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 kalilinux/build-scripts/kali-vm
Kali Linux VM images build script
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 cypherpunkarmory/userland
Main UserLAnd Repository
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 containers/bubblewrap
Low-level unprivileged sandboxing tool used by Flatpak and similar projects
 abraxas/opnsense-uidfield-system-uid0
OPNsense 26.7.6 - High - Remote - Privilege leftover - UidField uid 0
 abraxas/proftpd-sftp-copy-file-write
ProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SFTP copy-file skips dest WRITE
 abraxas/gitea-public-only-pat-org
Proof-of-concept lab for a Gitea authorization bypass where a public-only PAT with write:organization creates a private organization via POST…
 praetorian-inc/capability-sdk
Shared Go SDK defining a standard capability interface for security scanners, with multi-format finding output (terminal, JSON, NDJSON, Markdown,…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 7acini/cve-2026-102261
Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.