
gvisor
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
cloud-infrastructure-securitycloud-securitycontainer-escape+4
19.3k
google/gvisorSandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
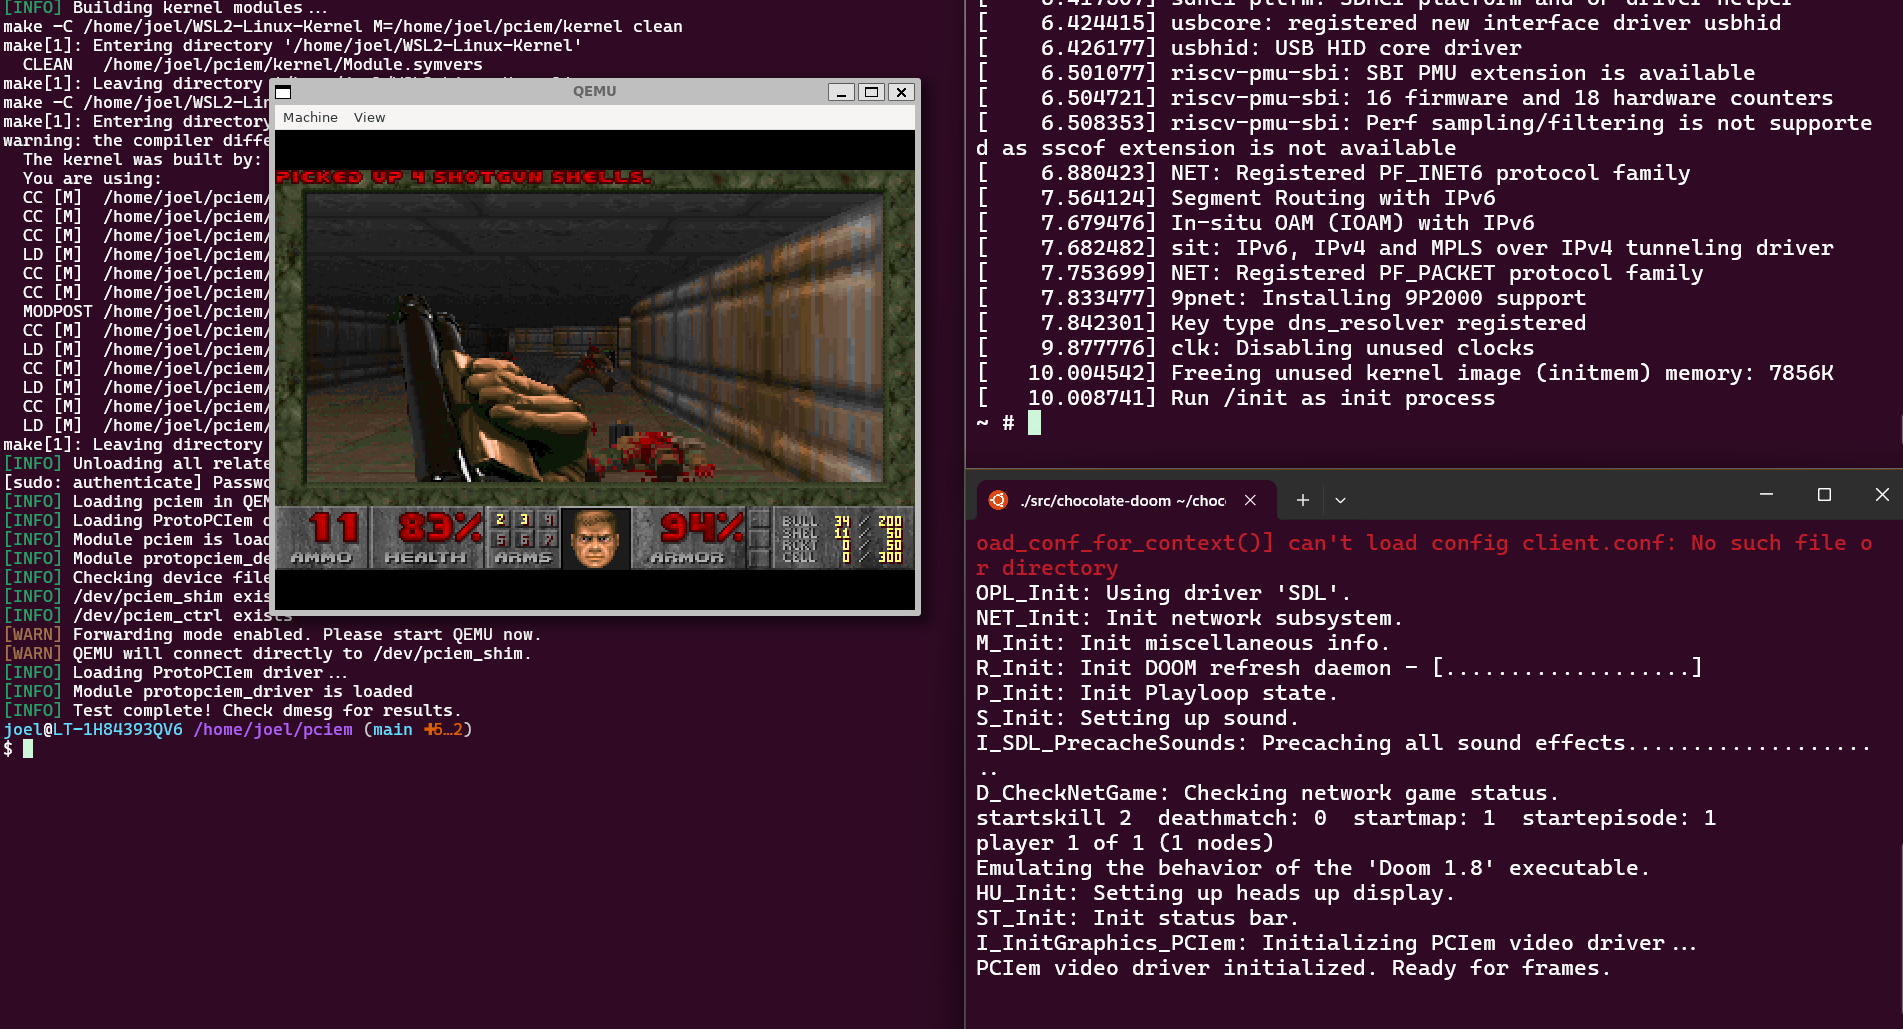 cakehonolulu/pciem
A Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 suominen/januscape
Tracking Januscape (CVE-2026-53359), the KVM/x86 guest-to-host escape
 suominen/itscape
Tracking ITScape (CVE-2026-46316), the KVM/arm64 guest-to-host escape
 0xblackash/cve-2026-64531
Reference analysis of a Linux kernel Open vSwitch memory-corruption vulnerability, covering root cause, impact, detection commands, and mitigation…
 rex-rs/rex
Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 adriancable/eternal
Minimal machine architecture with LLVM compiler backend, Linux port, and virtual machine for creating self-contained software capsules that remain…
 vatson112/deny-af-alg-bpf
eBPF LSM program that blocks AF_ALG socket creation to mitigate CVE-2026-31431, with userspace daemon logging denied attempts via ring buffer.
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 linux-zs/cve-2026-31431-mitigation
Seccomp-based mitigation for CVE-2026-31431, a Linux kernel LPE. Blocks AF_ALG socket via PAM module and standalone wrapper, with auto-detection of…
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
 intellabs/kafl
A fuzzer for full VM kernel/driver targets