
incus-os
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
cloud-infrastructure-securityconfiguration-auditingcontainer-security+3
lxc/incus-osImmutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
 netblue30/firejail
Linux namespaces and seccomp-bpf sandbox
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
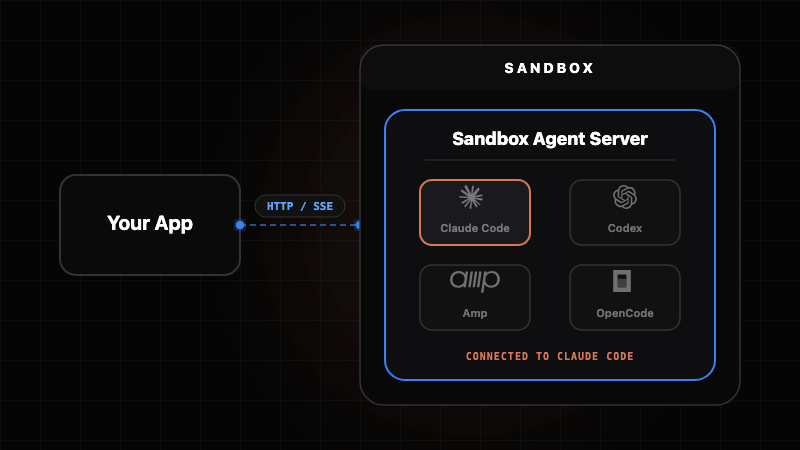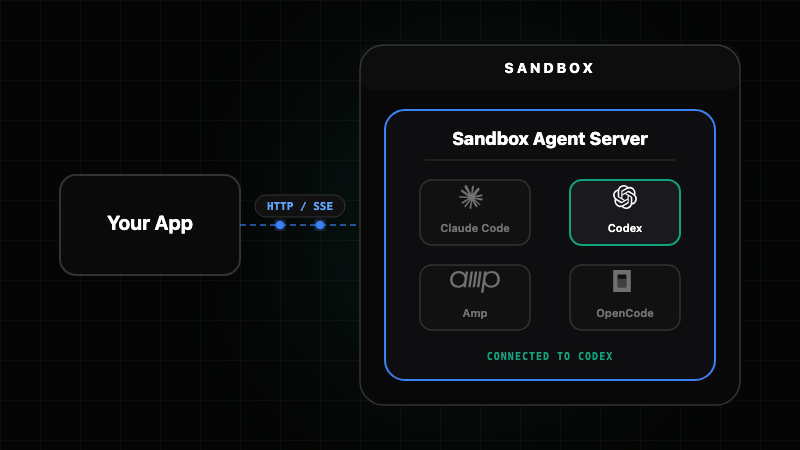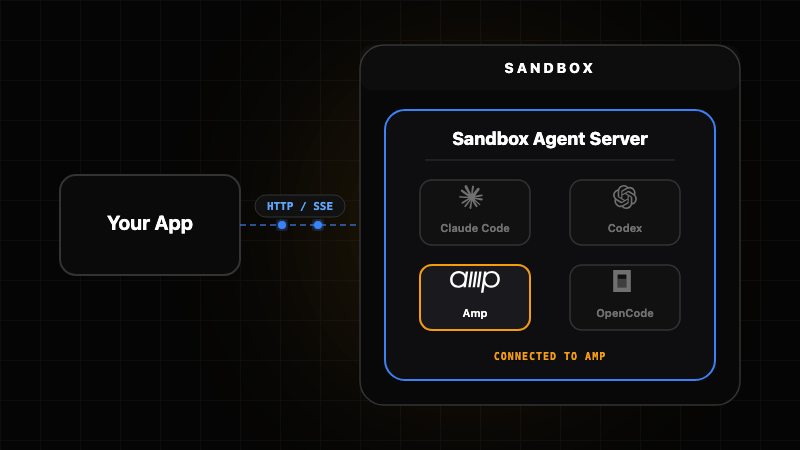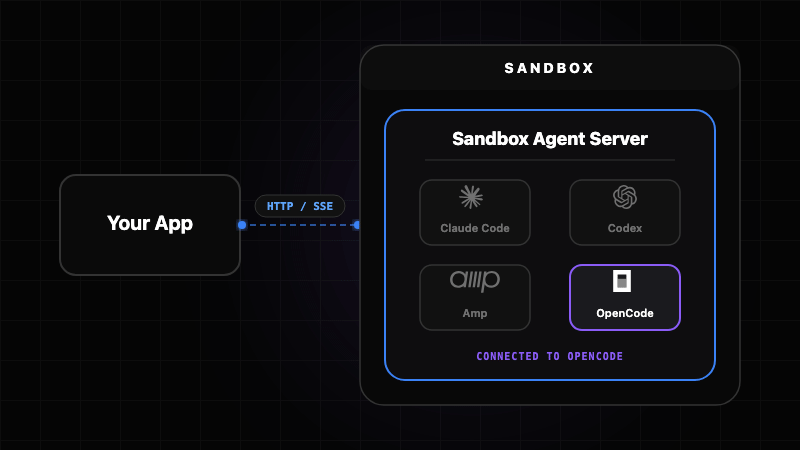 rivet-dev/sandbox-agent
A durable process per agent, with memory that survives restarts
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
 qubesos/qubes-core-admin
Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 dockur/windows
Run Windows inside a Docker container with KVM acceleration, automatic installation, and customizable resources. Supports multiple Windows versions,…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 rahulreddykarne/cve-2026-15911-confluent_kafka
Disabled TLS Certificate Verification for HashiCorp Vault KMS in confluent-kafka