
litebox
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
cloud-securitycontainer-securityembedded-systems-security+1
2.7k
microsoft/liteboxA security-focused library OS supporting kernel- and user-mode execution
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
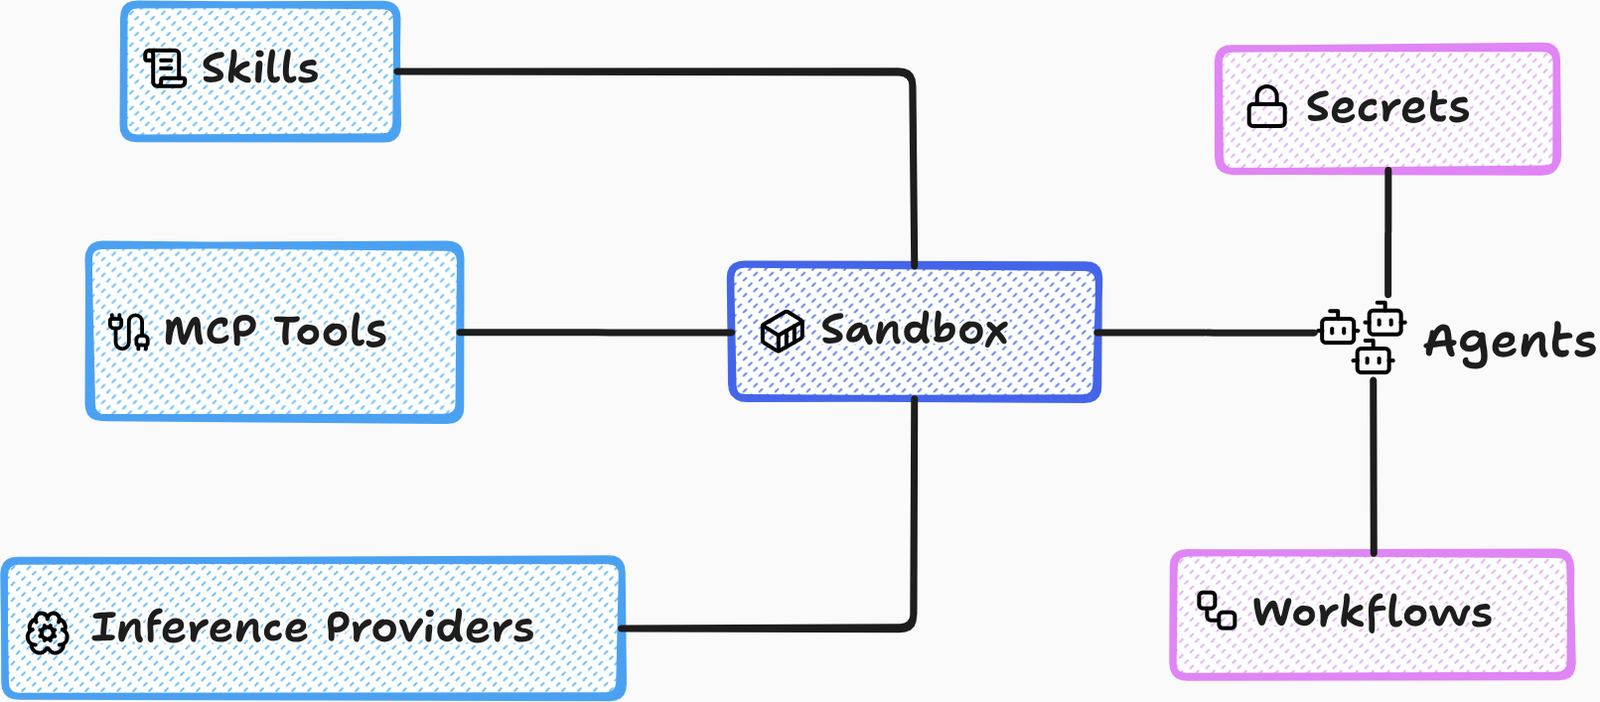 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
 dockur/windows
Run Windows inside a Docker container with KVM acceleration, automatic installation, and customizable resources. Supports multiple Windows versions,…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 falconforceteam/falcondash
Azure workbook dashboard that visualizes and explores detection performance metrics, helping security teams measure and proactively maintain their…
 vera0011/easysec
EasySec helps small and medium-sized enterprises (SMEs) with cybersecurity knowledge and resources
 microsoft/igvm
Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
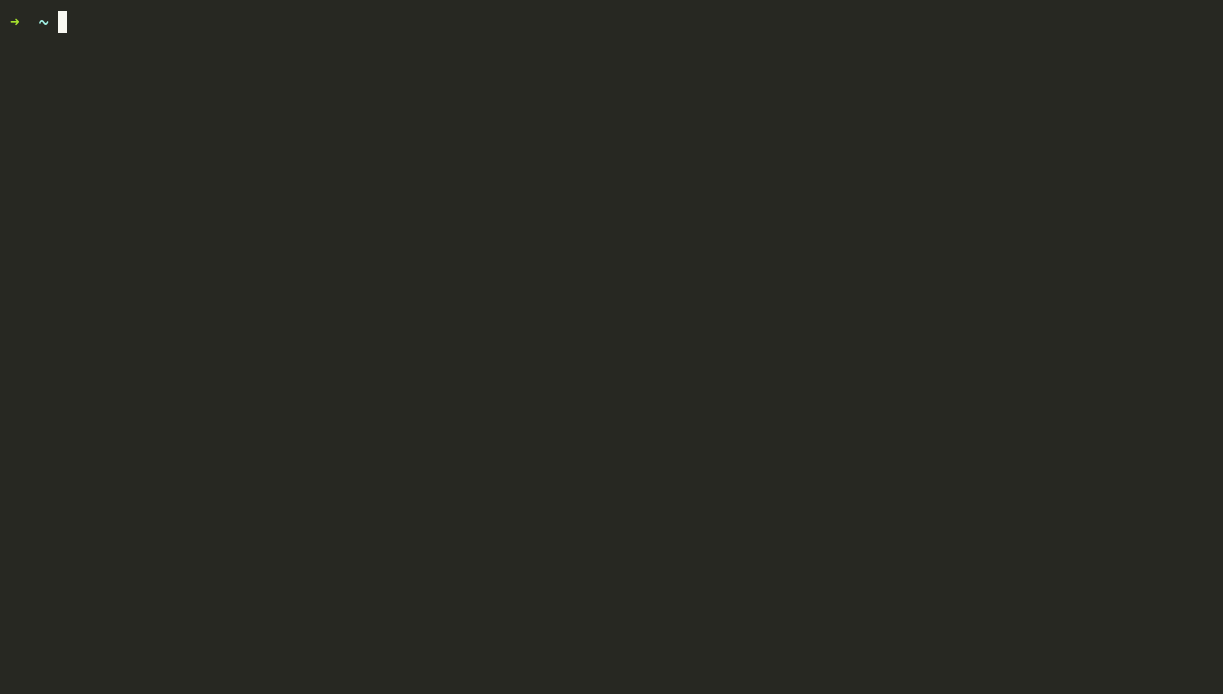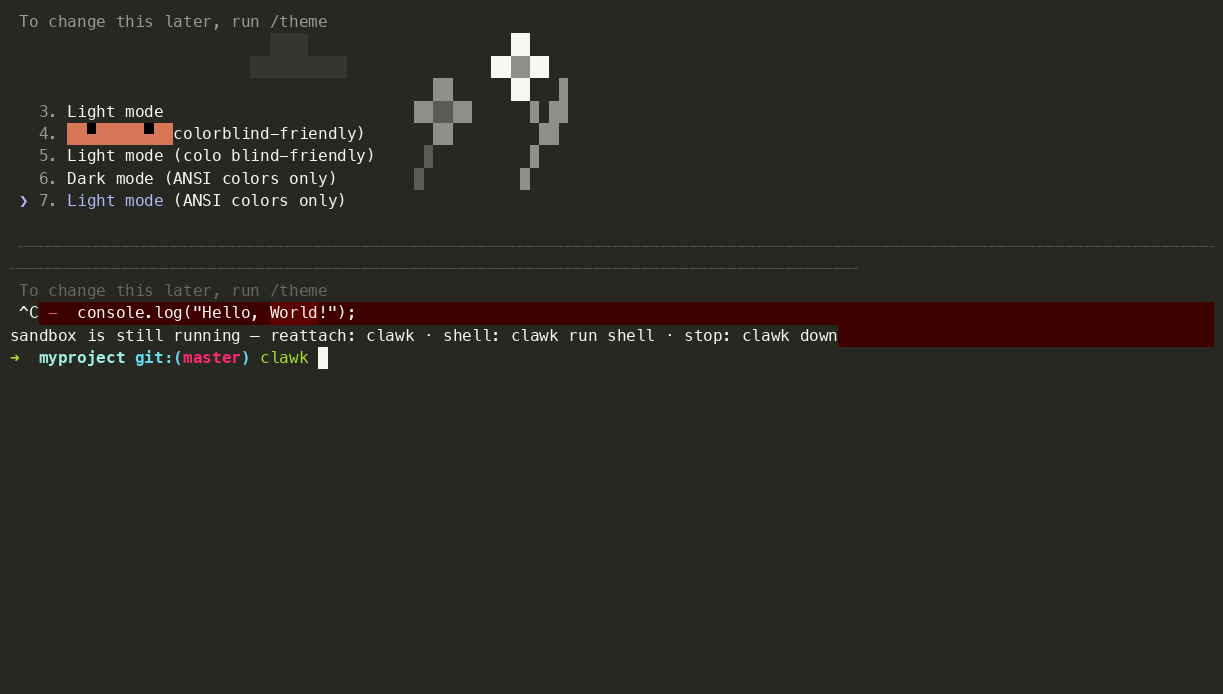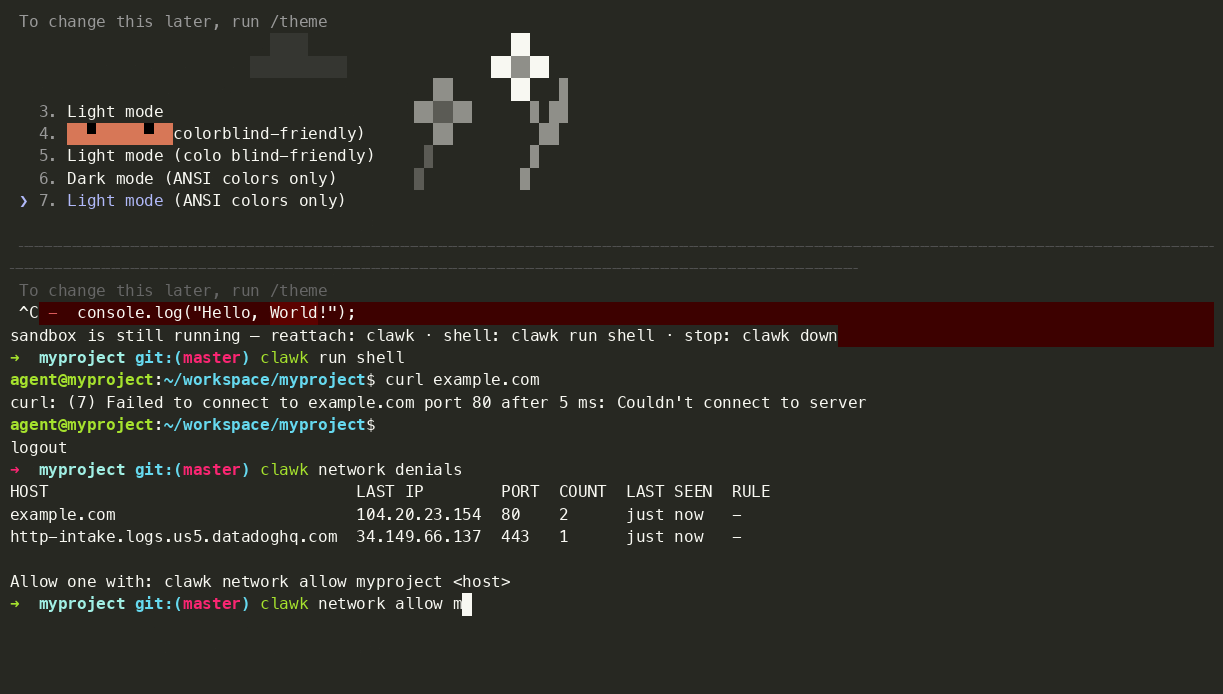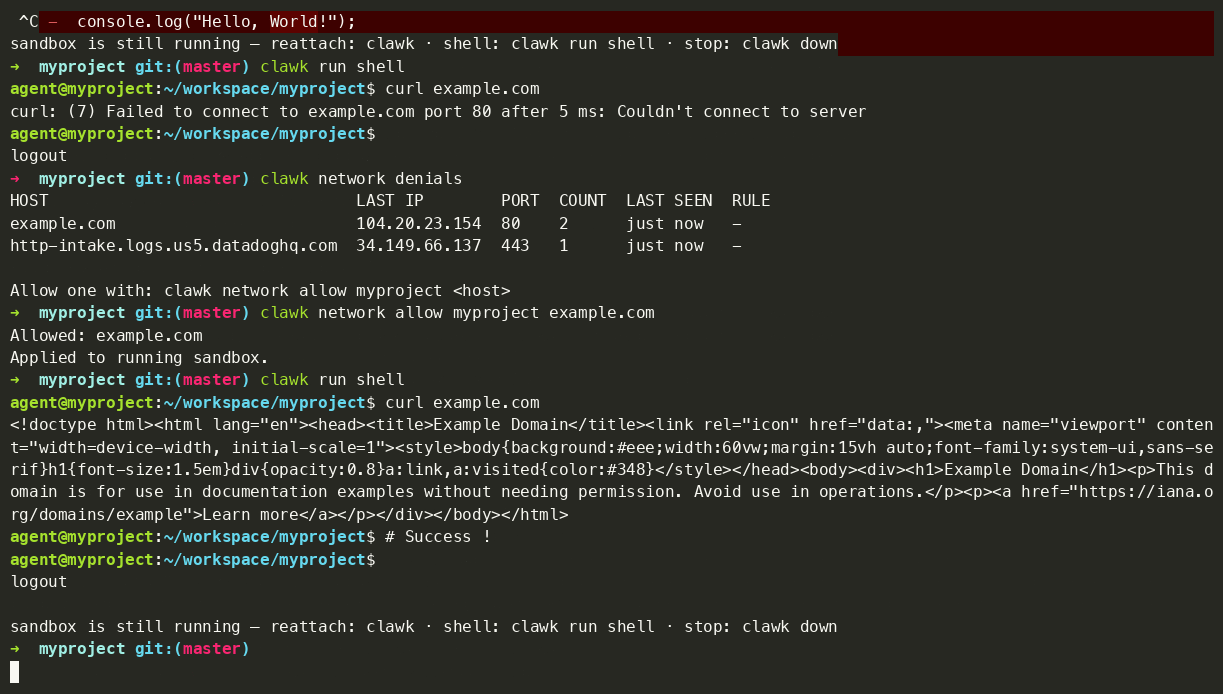 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 mitos-run/mitos
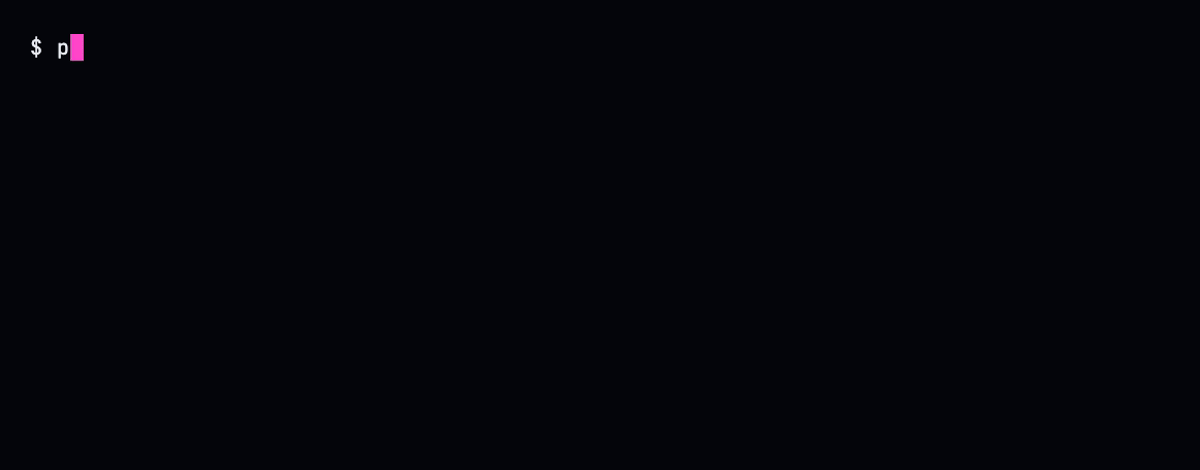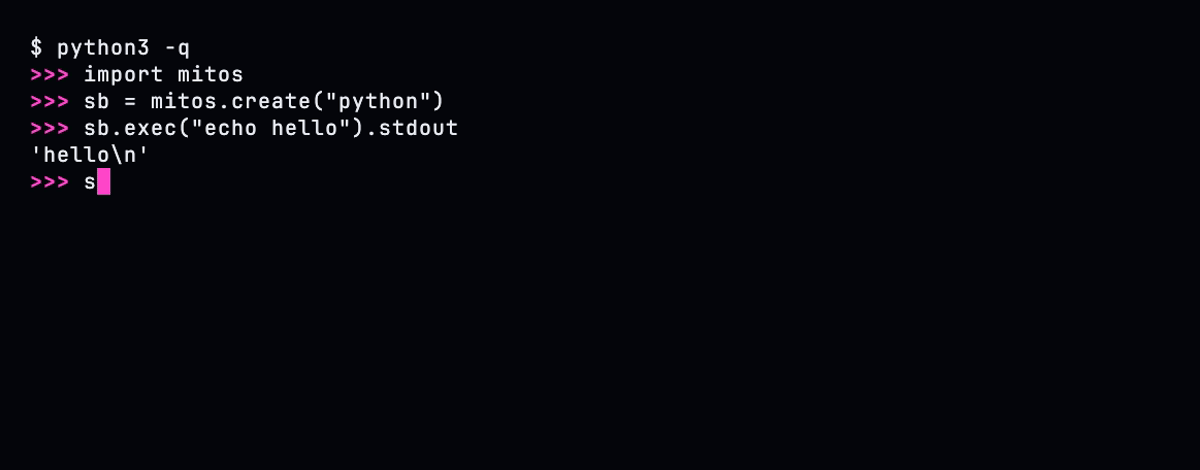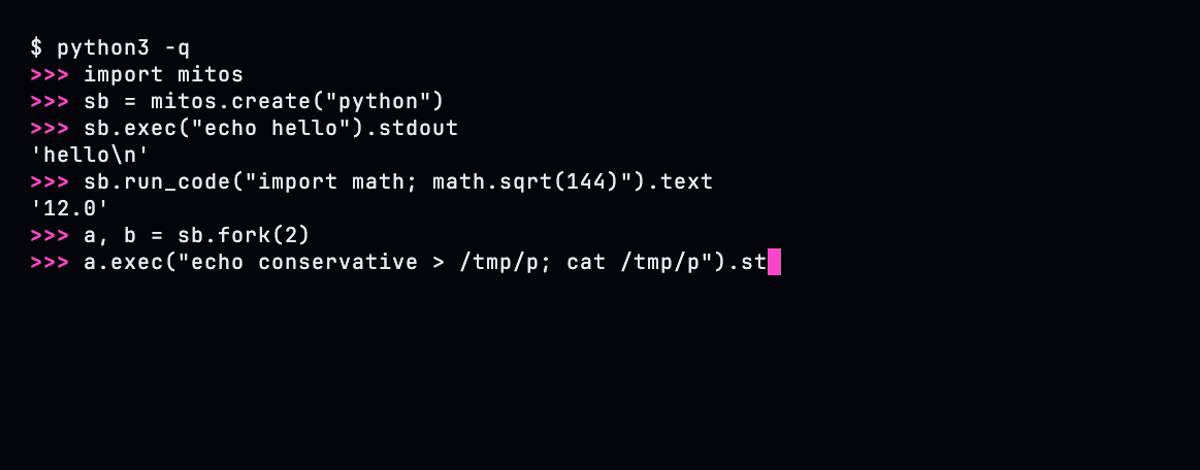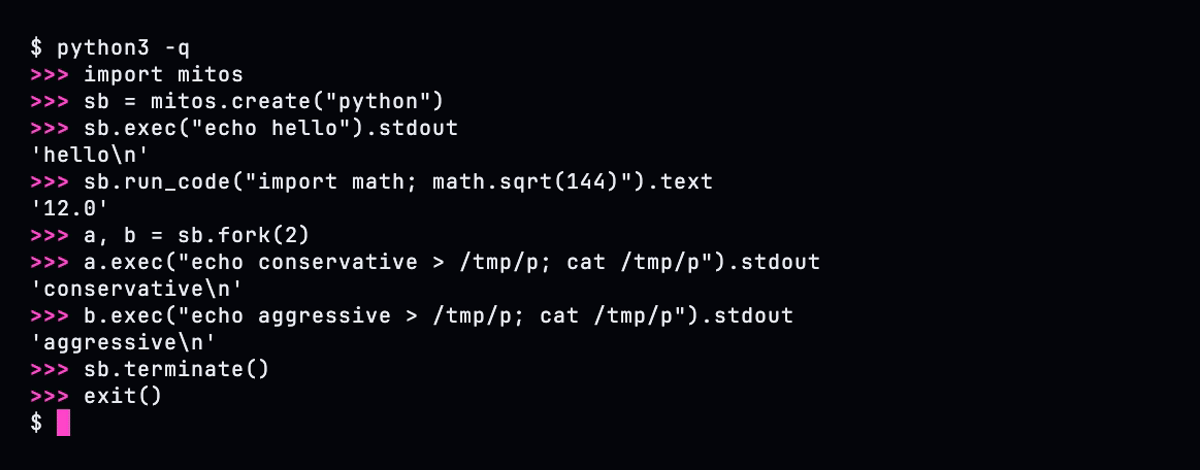
Millisecond microVM sandbox forking for AI agents on Kubernetes. Firecracker VMs that restore from memory snapshots in milliseconds, fork a running…
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking