
CVE-2026-92392
 ashu7ank/cve-2026-92392
Checks local curl/libcurl builds for CVE-2026-92392 HTTP/2 upload use-after-free exposure, with passive inventory, mounted-image scanning, and a…
container-securitydefensive-toolsdynamic-analysis-sandboxing+5
ashu7ank/cve-2026-92392Checks local curl/libcurl builds for CVE-2026-92392 HTTP/2 upload use-after-free exposure, with passive inventory, mounted-image scanning, and a…
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…

 kavryxdev-group/sandboxed-untrusted-code-execution-runner
Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.
 ko0ler/homelab
GNS3 home lab documenting a segmented network with Cisco ASAv firewall, L3 core, DMZ, and an Active Directory domain for practicing networking,…
 abraxas/kafka-connect-filestream-win
Kafka Connect 4.3.1 - High - Windows FileStream classpath leftover - unauth file read/write
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 withsecurelabs/amsidetection
Proof-of-concept tool for detecting AMSI (Antimalware Scan Interface) bypasses and malicious in-memory script activity on Windows endpoints.
 zephrfish/ludus-defender-lab
MDE/MDI Defender setup for Ludus
 nccgroup/wubes
Qubes containerization on Windows
 gregaskew/speculativeexecutionassessment
Assesses a system for the "speculative execution" vulnerabilities described in CVE-2017-5715, CVE-2017-5753, CVE-2017-5754
 dockur/windows
Run Windows inside a Docker container with KVM acceleration, automatic installation, and customizable resources. Supports multiple Windows versions,…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
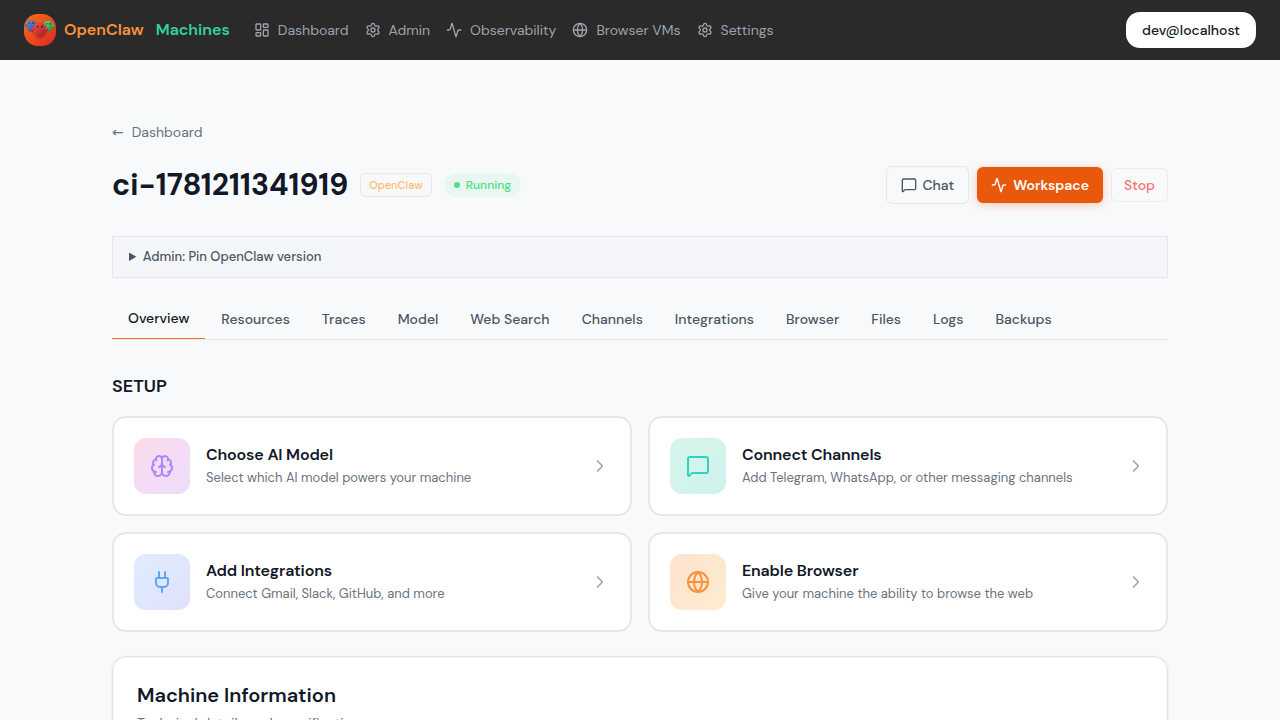 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.