
jellyfin-ffmpeg-colonslash
 abraxas/jellyfin-ffmpeg-colonslash
Jellyfin Server 12.2 - High - Remote after .strm plant - FFmpeg arg injection - EncodingUtils -i leftover of GHSA-wwwm
exploitationlabs-practicepenetration-testing+3
abraxas/jellyfin-ffmpeg-colonslashJellyfin Server 12.2 - High - Remote after .strm plant - FFmpeg arg injection - EncodingUtils -i leftover of GHSA-wwwm
 abraxas/pfsense-config-readonly-restore
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - readonly config_install
 abraxas/pfsense-dhcpd-conf
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - ISC dhcpd filename
 abraxas/pfsense-igmp-type
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - IGMP type newline
 abraxas/pfsense-unbound-sock-timeout
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - RCE - Unbound sock-queue-timeout CRLF
 abraxas/pfsense-uploadconfig
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - hidden uploadconfig
 yv1ing/secbox
Conducting cybersecurity testing using the pi agent in a pre-built sandbox environment.
 abraxas/gitea-restore-file-open
Proof-of-concept for a Gitea restore-repo file:// local file inclusion (CWE-73) that copies symlink targets outside an untrusted dump into release…
 abraxas/n8n-databricks-path-join
Proof-of-concept for an n8n path-traversal (CWE-22) in Databricks nodes: unauthenticated webhook input escapes the Genie path to leak workspace PAT…
 abraxas/kafka-connect-filestream-win
Kafka Connect 4.3.1 - High - Windows FileStream classpath leftover - unauth file read/write
 abraxas/moodle-grades-feedback-idor
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_feedback skips separate-groups checks
 cisagov/vulnrichment
A repo to conduct vulnerability enrichment.
 bombobombone/cve-2026-102971
Sanitized report and loopback-only PoC for CVE-2026-102971, a MediaWiki REST revision response leaking hidden revision author user IDs.
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
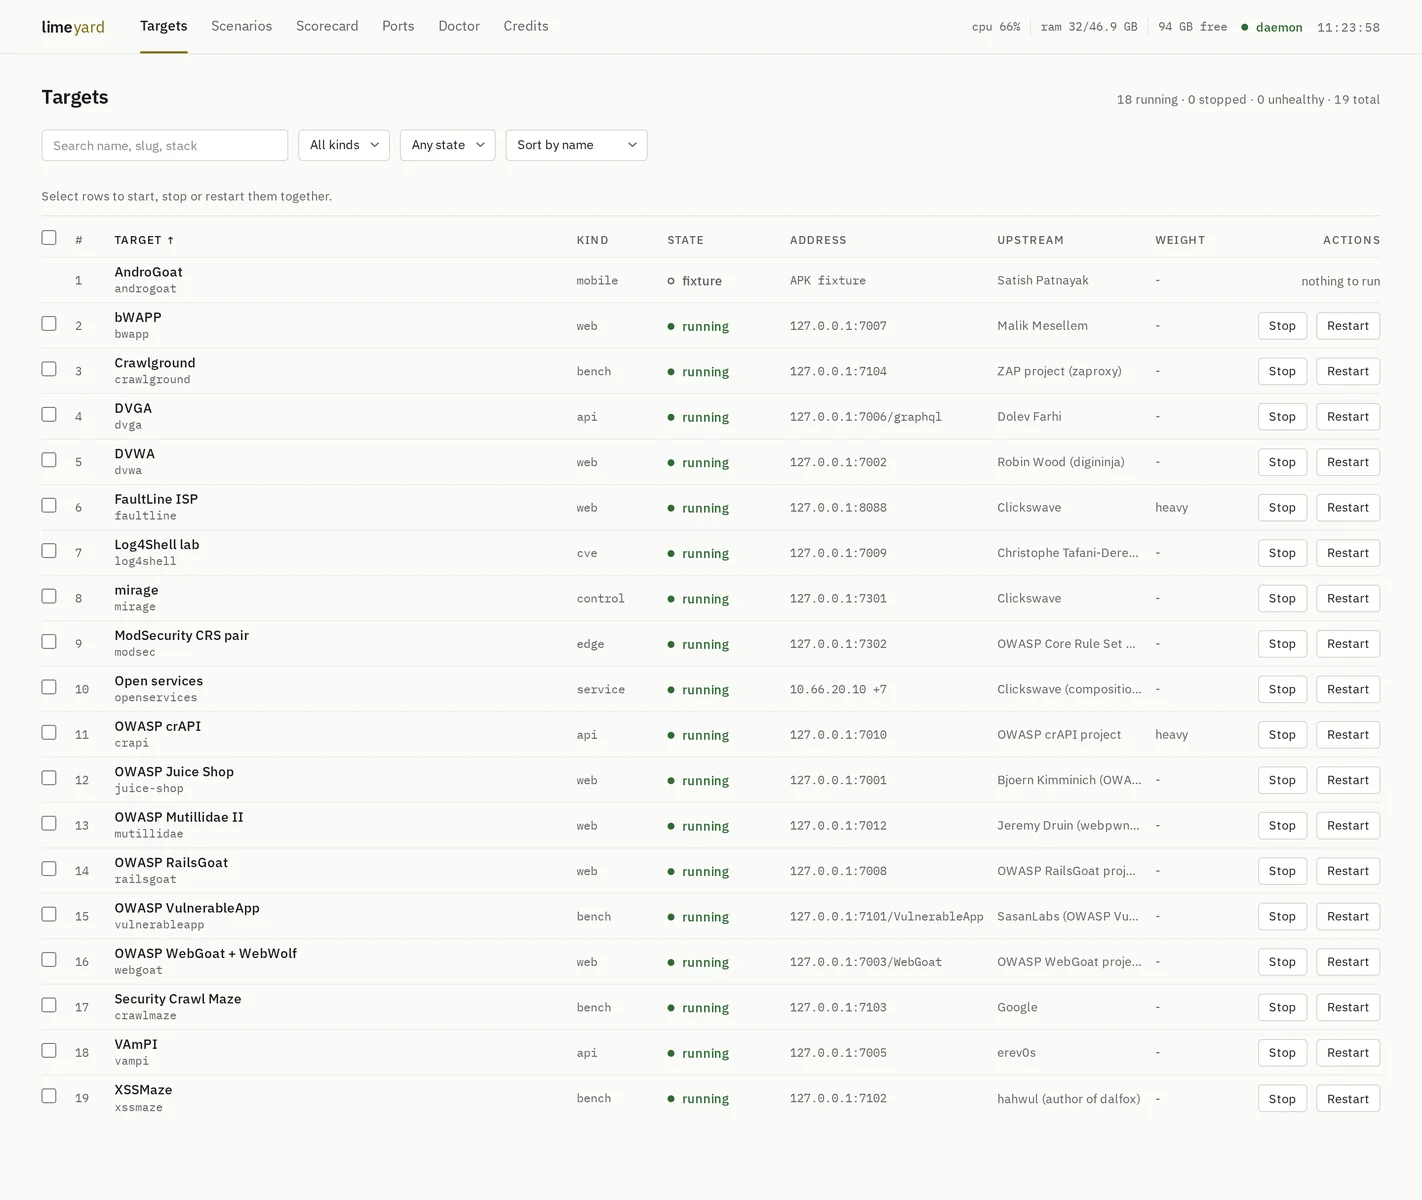 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…