
kali-installer
 kalilinux/build-scripts/kali-installer
Builds official Kali Linux installer ISO images with simple-cdd and debian-cd, supporting multiple architectures, variants, mirrors, and…
container-securitydevsecopsgeneral-purpose-utilities+4
5
kalilinux/build-scripts/kali-installerBuilds official Kali Linux installer ISO images with simple-cdd and debian-cd, supporting multiple architectures, variants, mirrors, and…

 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 kavryxdev-group/sandboxed-untrusted-code-execution-runner
Executes untrusted Python, JavaScript, and Bash in a hardened jail with 5-second, 128 MB, 0.5-core, PID and output limits.
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 abraxas/pfsense-config-readonly-restore
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - readonly config_install
 abraxas/opnsense-ntp-gps-fudge
OPNsense 26.7.6 - High - Remote - Config line injection - NTP GPS fudge
 abraxas/opnsense-tunables-loader
OPNsense 26.7.6 - High - Remote - Config line injection - tunables loader
 abraxas/spark-connect-copy-local
Apache Spark 4.2.0 - High - Remote - File write - Connect session SET copyFromLocalToFs.allowDestLocal
 opposum0112/decretum
Contract LinkML compiler for a security researchers
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
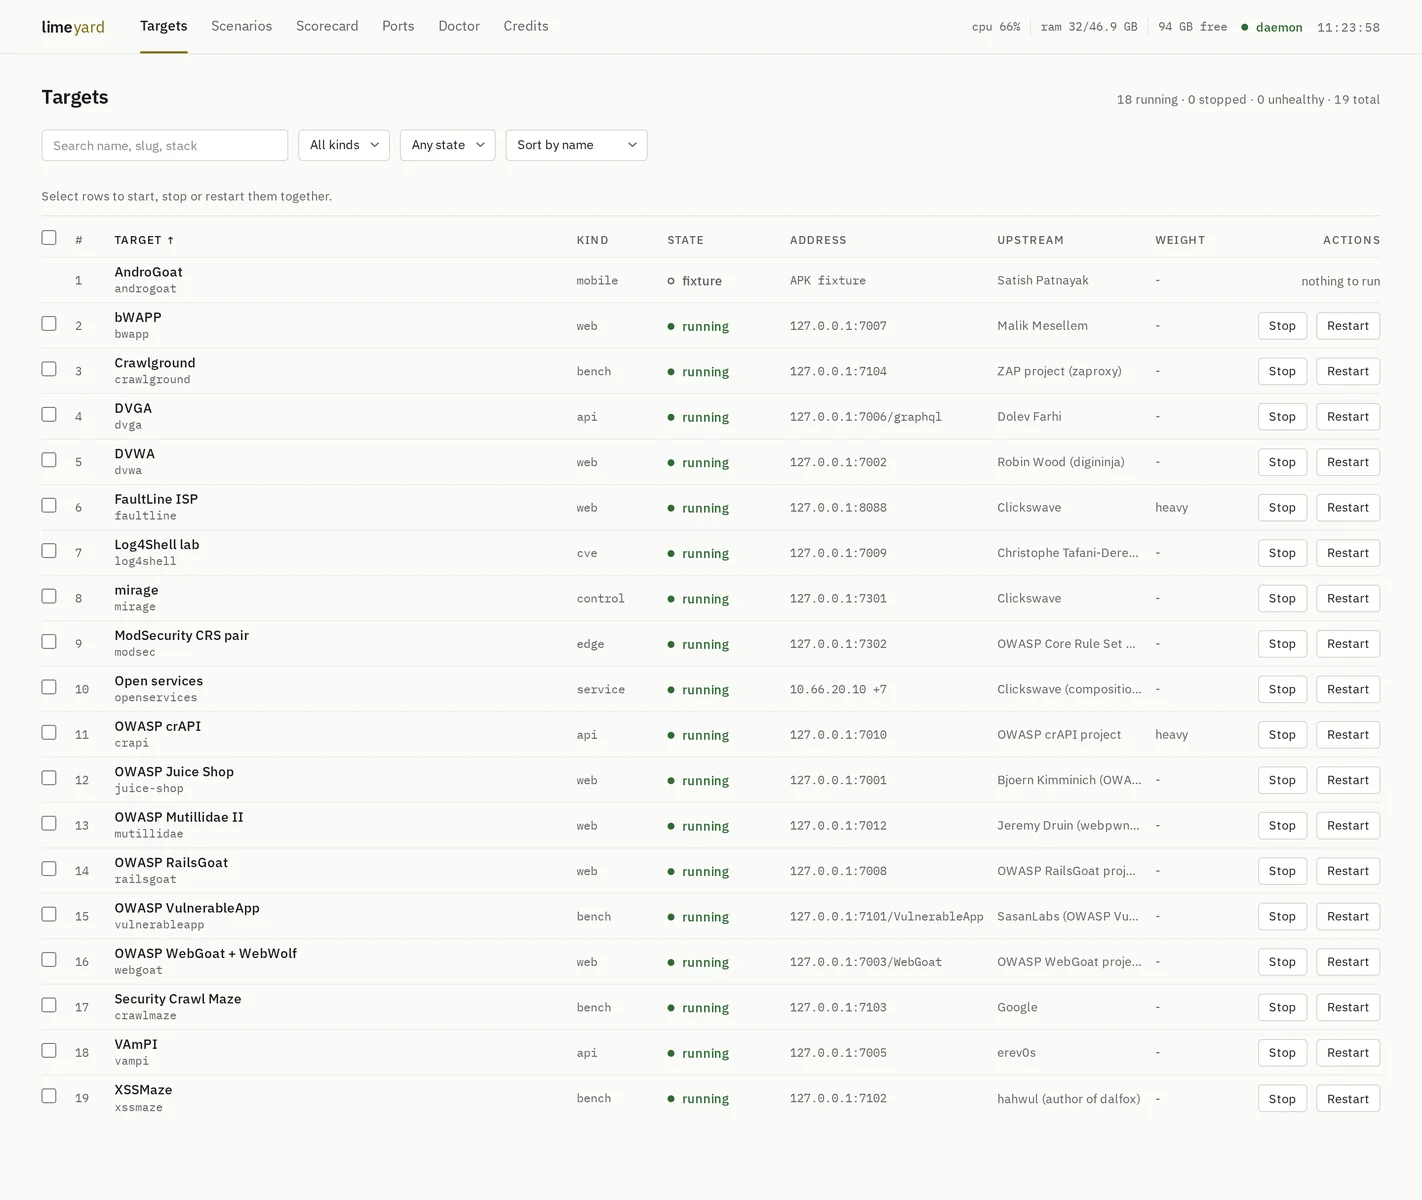 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 abhishek2512mishra/claude-code-security-audit
Security scanner auditing Claude Code environments for CVE-2026-21852 pre-trust execution, hook hijacking, and eBPF lockdown.
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…