
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
57 results
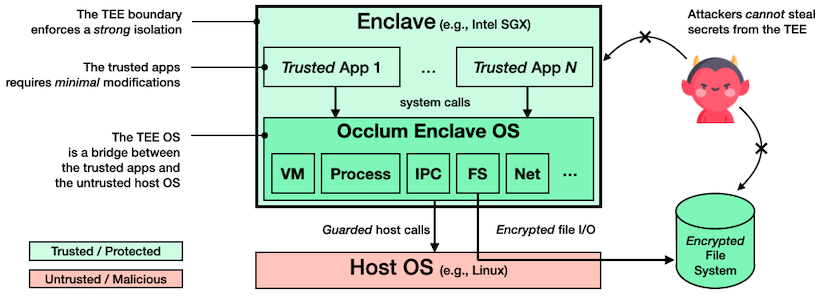
occlum preview

occlum

GitHubocclum/occlum

Memory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…

cloud-infrastructure-securitycloud-securitycryptography+5
1.5k
8 months ago
Agentic-Vulnerability-Discovery-and-Validation-Harness preview

Agentic-Vulnerability-Discovery-and-Validation-Harness

GitHubowasp/agentic-vulnerability-discovery-and-validation-harness

Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.

ai-securitypenetration-testingscripting-automation+3
12 days ago
Xpsd preview

Xpsd

GitHubowasp/xpsd

Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
ai-securitycode-analysisdevsecops+6
47 days ago
gitea-restore-file-open preview

gitea-restore-file-open

GitHubabraxas/gitea-restore-file-open

Proof-of-concept for a Gitea restore-repo file:// local file inclusion (CWE-73) that copies symlink targets outside an untrusted dump into release…
exploitationinformation-gatheringlabs-practice+4
3 days ago
exploit-js2py preview

exploit-js2py

GitHubrianjuniorsf/exploit-js2py

The CVE-2024-28397 vulnerability affects versions of js2py up to v0.74, a Python library that allows JavaScript code to be executed within the Python…

exploitationpayload-developmentpenetration-testing+3
110 months ago
oss-scanner preview

oss-scanner

GitHubanthropics/oss-scanner

Service that builds enrolled open-source repositories in isolated offline VMs and scans them for security vulnerabilities, emailing findings with…

ai-securitycode-analysisdefensive-tools+7
1.7k14h 8m ago
p0tools preview

p0tools

GitHubgoogleprojectzero/p0tools

Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
binary-analysiscurated-resourceseducation+5
8568 months ago
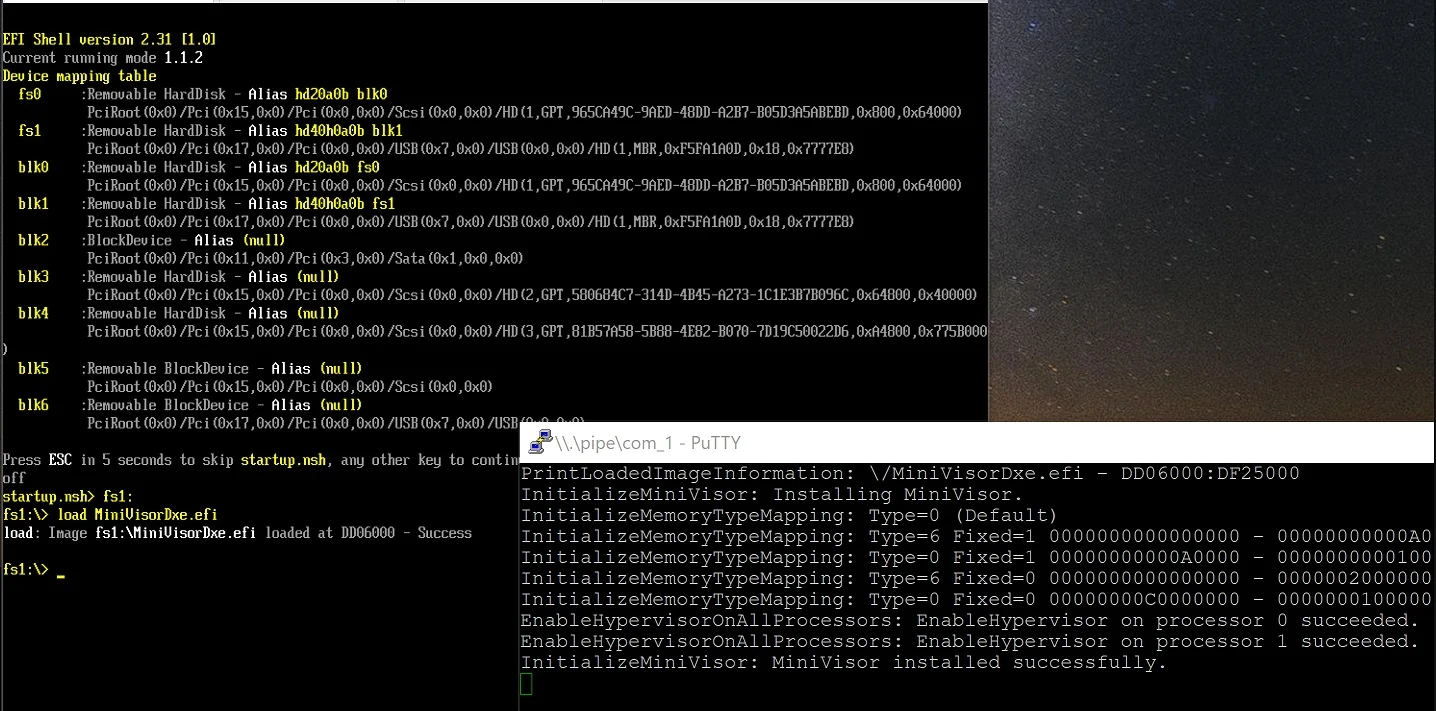
MiniVisorPkg preview

MiniVisorPkg

GitHubtandasat/minivisorpkg

The research UEFI hypervisor that supports booting an operating system.

binary-analysisdefensive-toolseducation+5
7652 years ago
seclab-taskflows preview

seclab-taskflows

GitHubgithubsecuritylab/seclab-taskflows

Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…

ai-assisted-reversingai-securityandroid-security+8
8910 days ago
SimpleVisor preview

SimpleVisor

GitHubionescu007/simplevisor

Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…

binary-analysiseducationhardware-security+4
2.0k2 years ago
GateX preview

GateX

GitHubabraxas/gatex

FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
binary-analysisbinary-exploitationcryptography+8
125 days ago
CVE-2026-102261 preview

CVE-2026-102261

GitHub7acini/cve-2026-102261

Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
authentication-authorizationdefensive-toolspenetration-testing+5
1 month ago
CVE-2026-15583 preview

CVE-2026-15583

GitHubabraxas/cve-2026-15583

Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…
api-securitydata-exfiltrationexploitation+6
3 days ago
CVE-2026-34990 preview

CVE-2026-34990

GitHubpredyy/cve-2026-34990

Minimal PoC for CVE-2026-34990: local privilege escalation in CUPS <= 2.4.16 that leaks cupsd's Local auth token and writes a NOPASSWD sudoers…
exploitationpenetration-testingprivilege-escalation+2
291 month ago
CVE-2026-49869 preview

CVE-2026-49869

GitHubeqstlab/cve-2026-49869

PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
authenticationexploitationlabs-practice+6
41 month ago
CVE-2026-52782 preview

CVE-2026-52782

GitHubabraxas/cve-2026-52782

Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
exploitationinformation-gatheringlabs-practice+5
3 days ago
CVE-2026-87902-PoC-pwnVader preview

CVE-2026-87902-PoC-pwnVader

GitHubpwnvader/cve-2026-87902-poc-pwnvader

Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
exploitationpayload-developmentpenetration-testing+5
1 month ago
gmh5225 preview

gmh5225

GitHubgmh5225/gmh5225

LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…

ai-assisted-reversingbinary-analysisbinary-exploitation+4
2 months ago
Previous1234Next