
cve-2026-87902-poc
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
exploitationlabs-practicepenetration-testing+4
38
ressl/cve-2026-87902-pocPoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 bara-almustafa/cve-2026-34990-poc
CVE-2026-34990 — CUPS <= 2.4.16 Local Privilege Escalation
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 huzjie/aegisagent
Runtime security gateway for AI agents: cryptographically attests tool calls, enforces policies, sandboxes execution, and logs tamper-evident audit…
 hassham1/cve-2026-12227-visualcomposer-lfi-poc
Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 ungabunga-ctf/cve-2026-34990
Python proof-of-concept for CVE-2026-34990 in OpenPrinting CUPS, coercing cupsd to leak a Local auth token and overwrite root files via a file://…
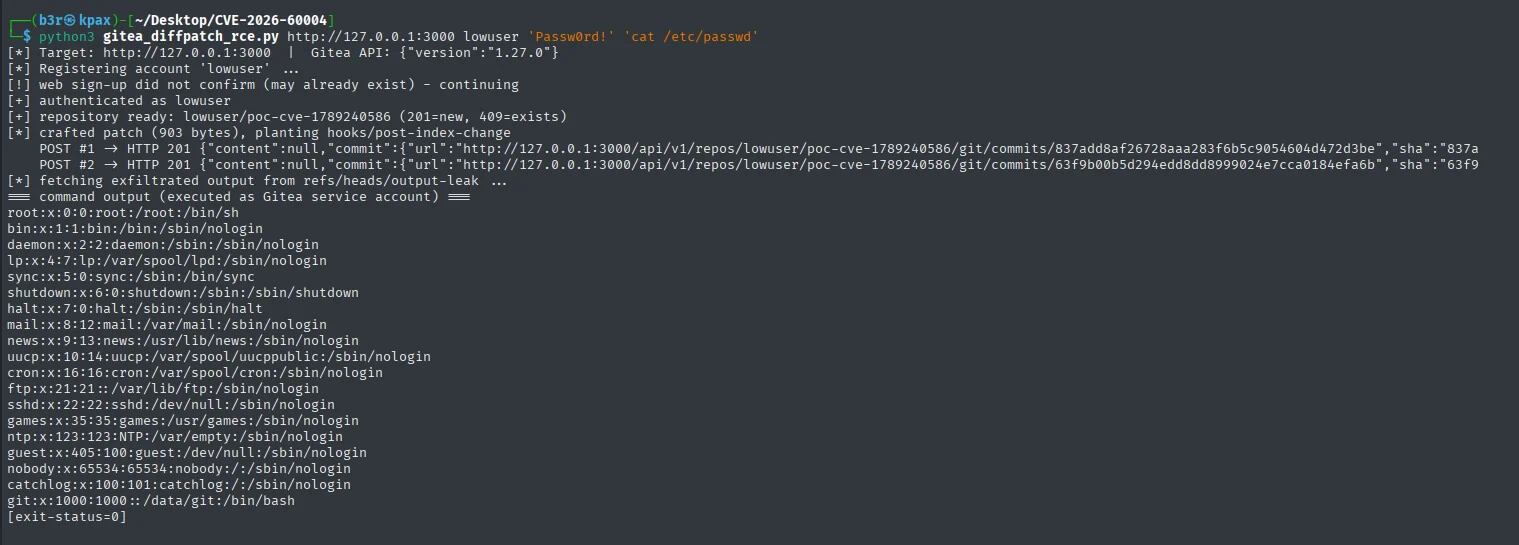 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 hackspeak/cve-2026-64561
Zapscape (CVE-2026-64561) KVM/x86 shadow MMU UAF guest-to-host escape PoC mirror — V4bel/@v4bel, MIT; for authorized security testing
 phalanx-ccs/copy-fail
Passive diagnostic tool that checks if a Linux system is vulnerable to CVE-2026-31431 by testing AF_ALG socket reachability, providing mitigation…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 abraxas/cve-2026-96512
Disclosure pack and PoC for CVE-2026-96512, a sudo NOTBEFORE/NOTAFTER TZ time-window bypass enabling local privilege escalation, with lab…
 hassham1/cve-2026-89274-wp-recipe-maker-poc
Docker validation lab and Python PoC for CVE-2026-89274, proving arbitrary shortcode execution in WP Recipe Maker <= 10.8.1 via rating-comment…
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 abraxas/cve-2026-62062
Proof-of-concept and lab pack for CVE-2026-62062, an unauthenticated CSRF REST nonce bypass in Elementor 4.3.0-4.3.1 enabling administrator account…
 shivammittal2403/cve-2026-59827-metabase-cyber-range
Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…