

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
30.4k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 mustafabilgici/sucoshscanny
"Sucosh" is an automated Source Code vulnerability scanner and assessment framework for Python(Flask-Django) & NodeJs capable of performing code…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 eilonh/s3crets_scanner
Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…
 redhuntlabs/bucketloot
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…
 molly/gh-dork
Automated GitHub dorking tool that searches user, organization, and repository code for exposed secrets, credentials, and security misconfigurations…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks
 divyanshukumar0014/shipproof
Automated SOC 2 change management for GitLab CI.
 arpsyndicate/kenzer
automated web assets enumeration & scanning [DEPRECATED]
 r3curs1v3-pr0xy/vajra
Vajra is a highly customizable target and scope based automated web hacking framework to automate boring recon tasks and same scans for multiple…
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
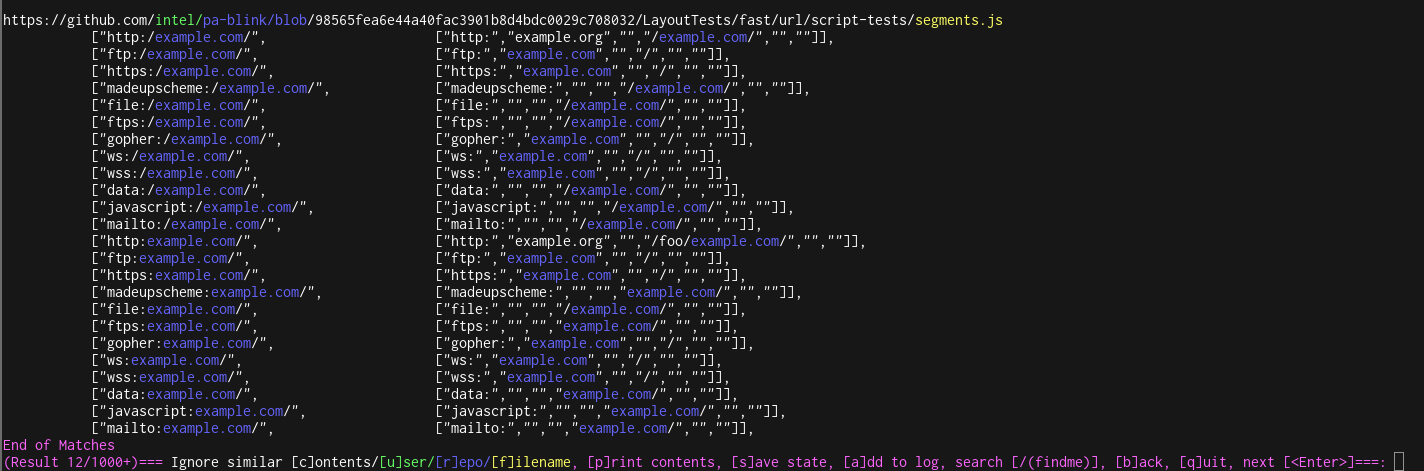 bishopfox/gitgot
Semi-automated, feedback-driven tool to rapidly search through troves of public data on GitHub for sensitive secrets.
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
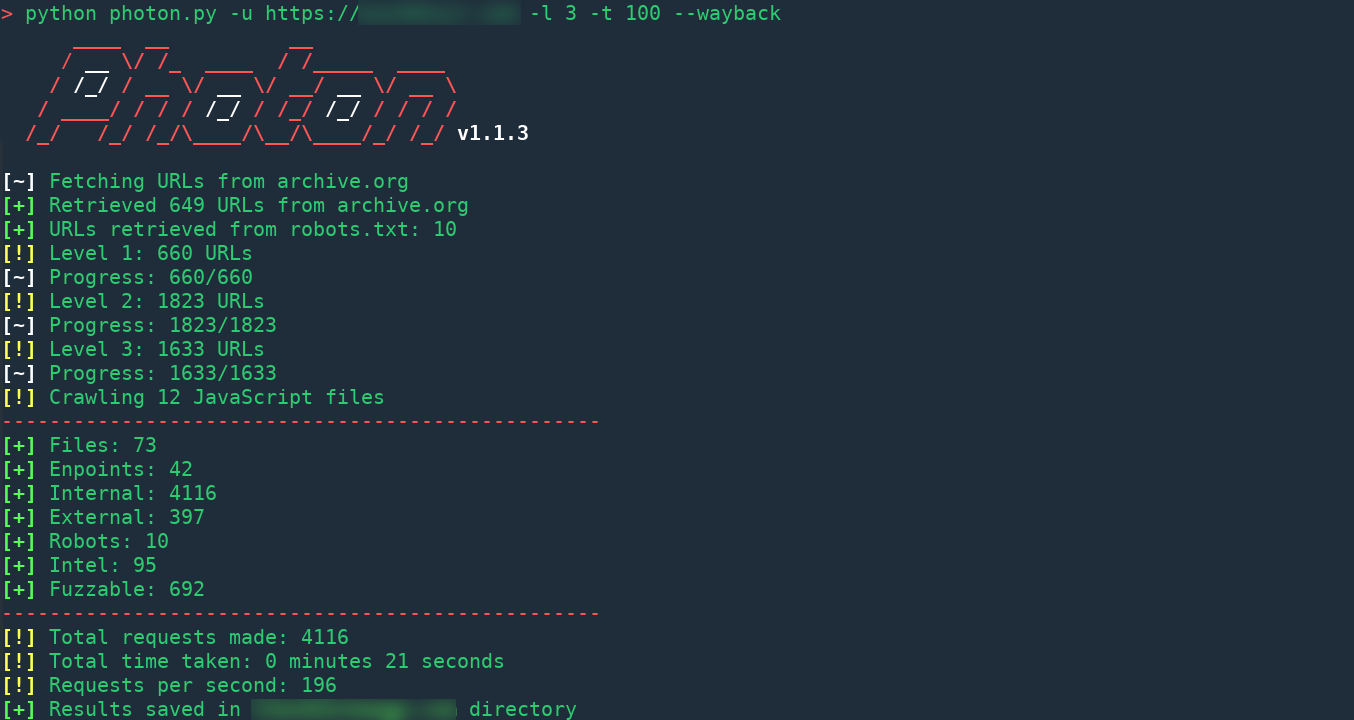 s0md3v/photon
Incredibly fast crawler designed for OSINT.
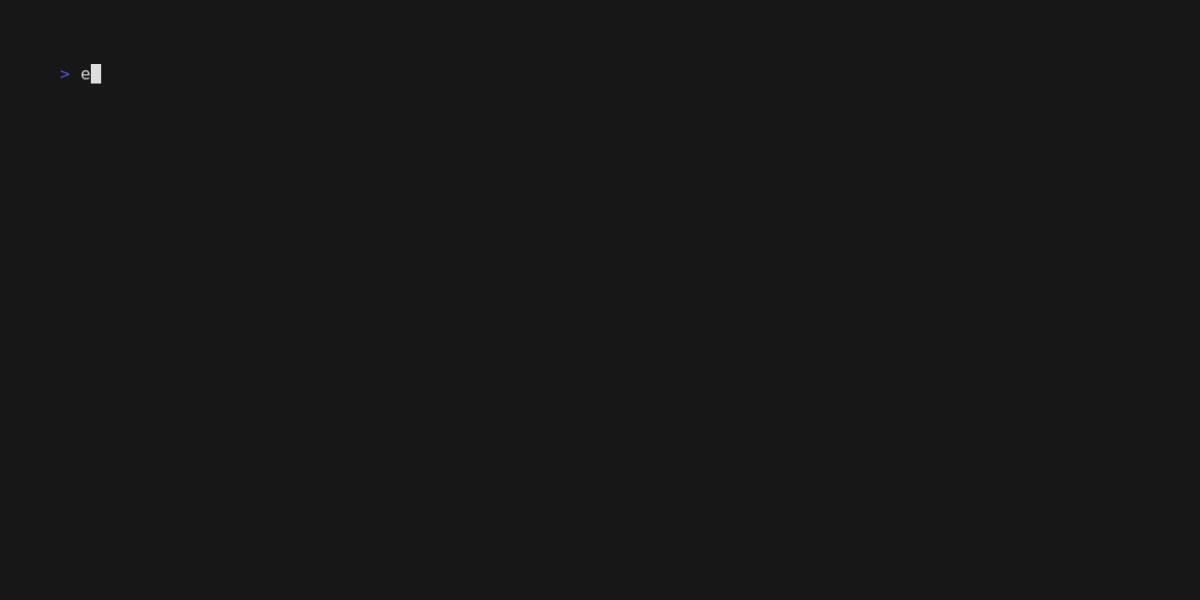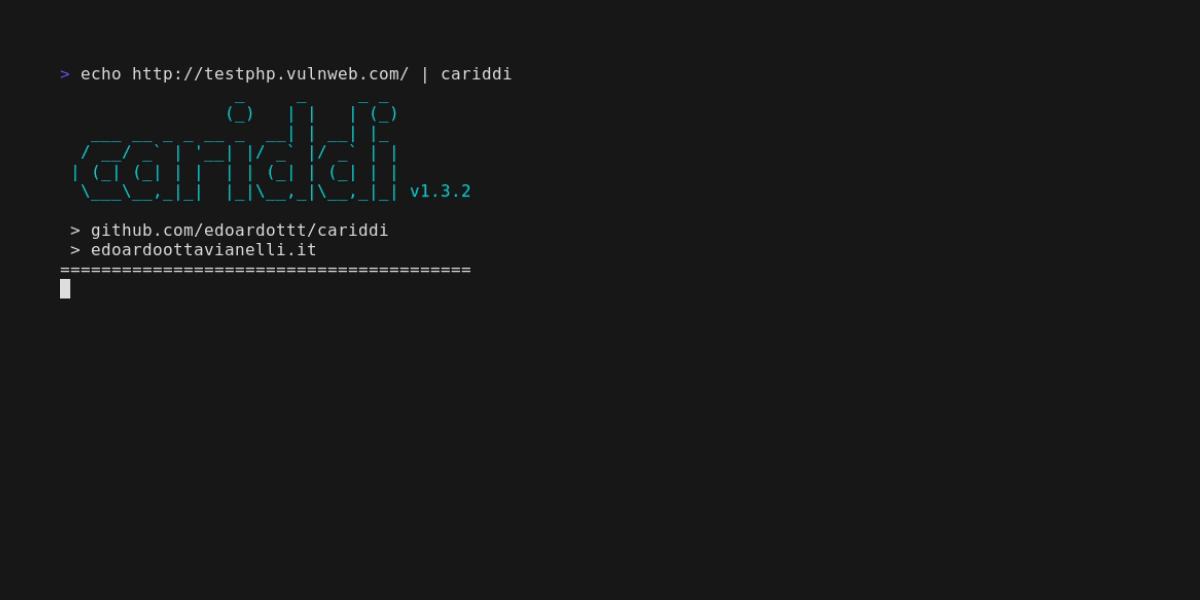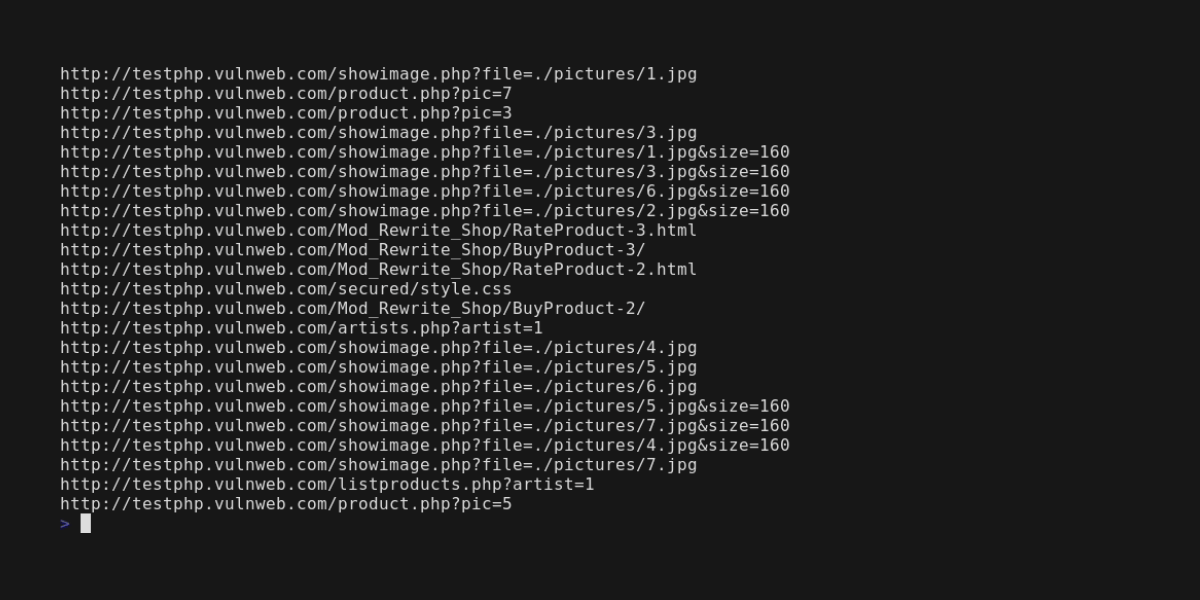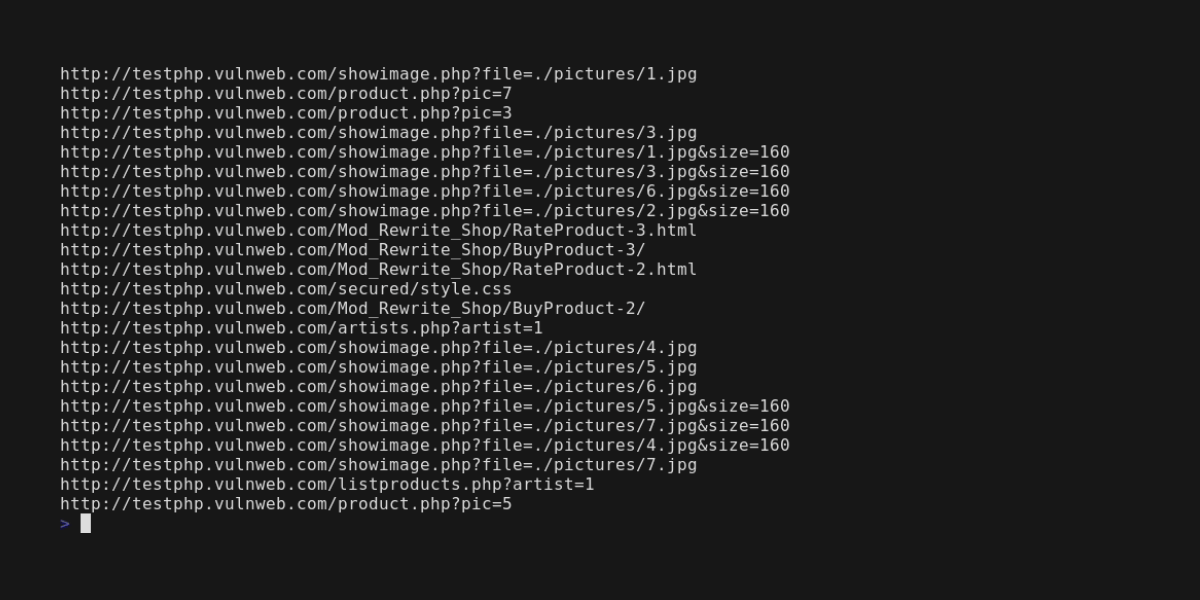 edoardottt/cariddi
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 tomnomnom/gf
A wrapper around grep, to help you grep for things