
smokedmeat
 boostsecurityio/smokedmeat
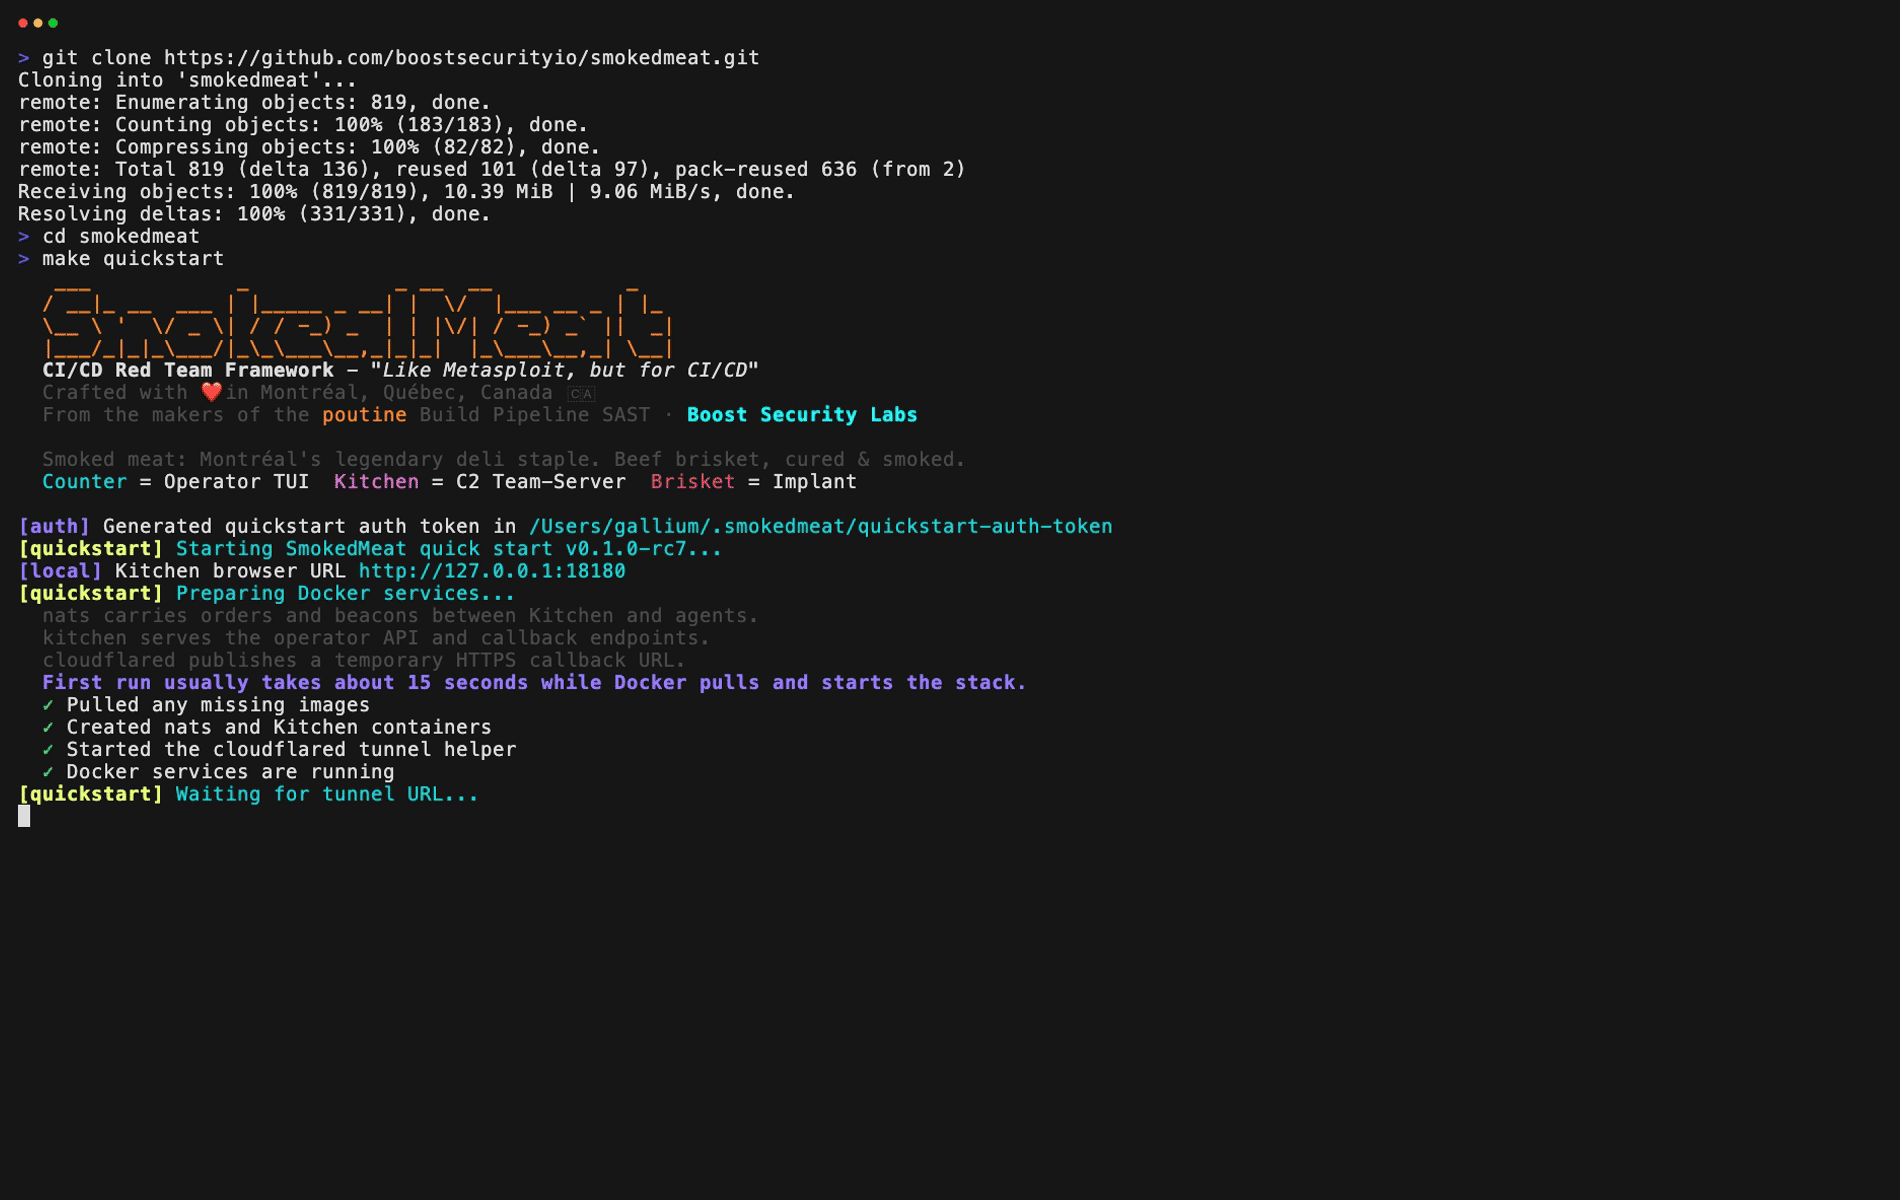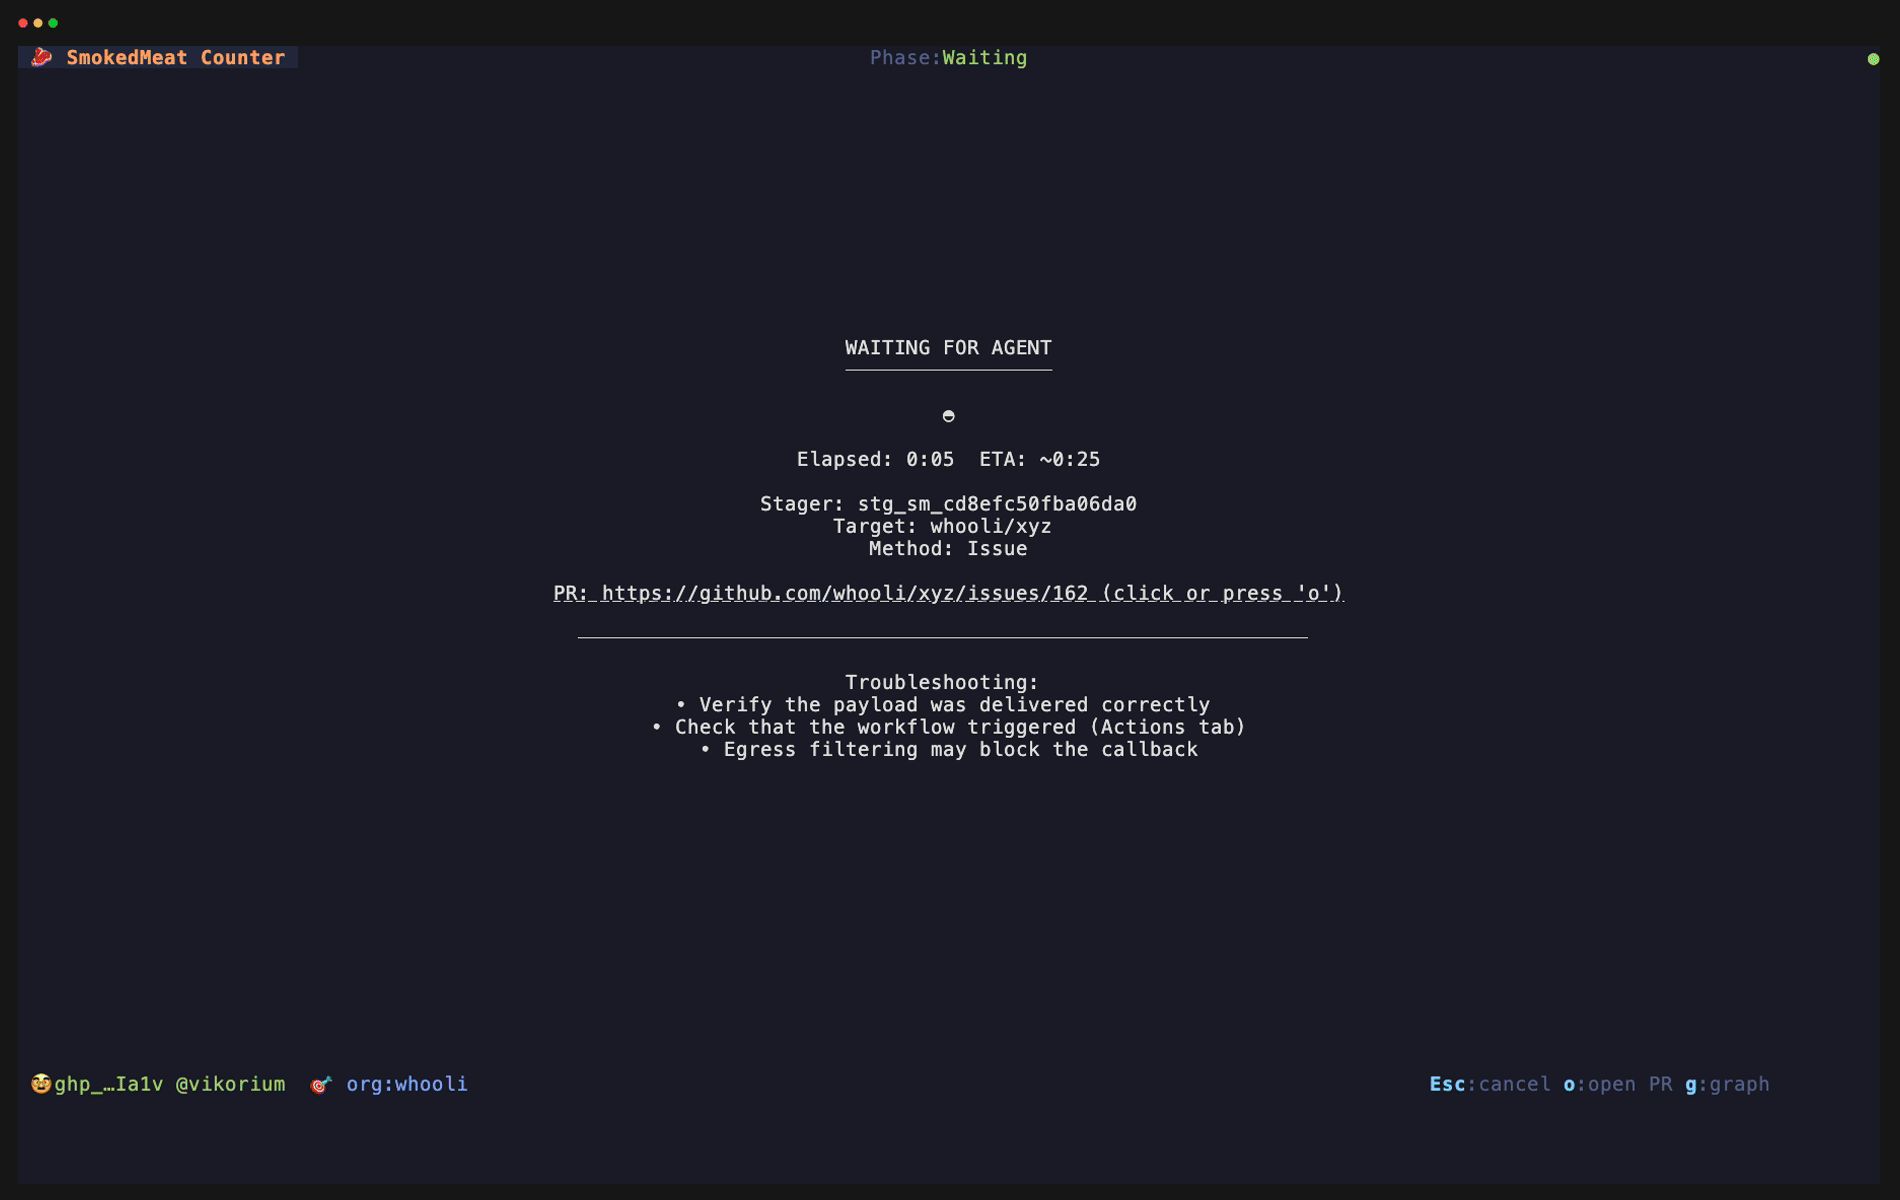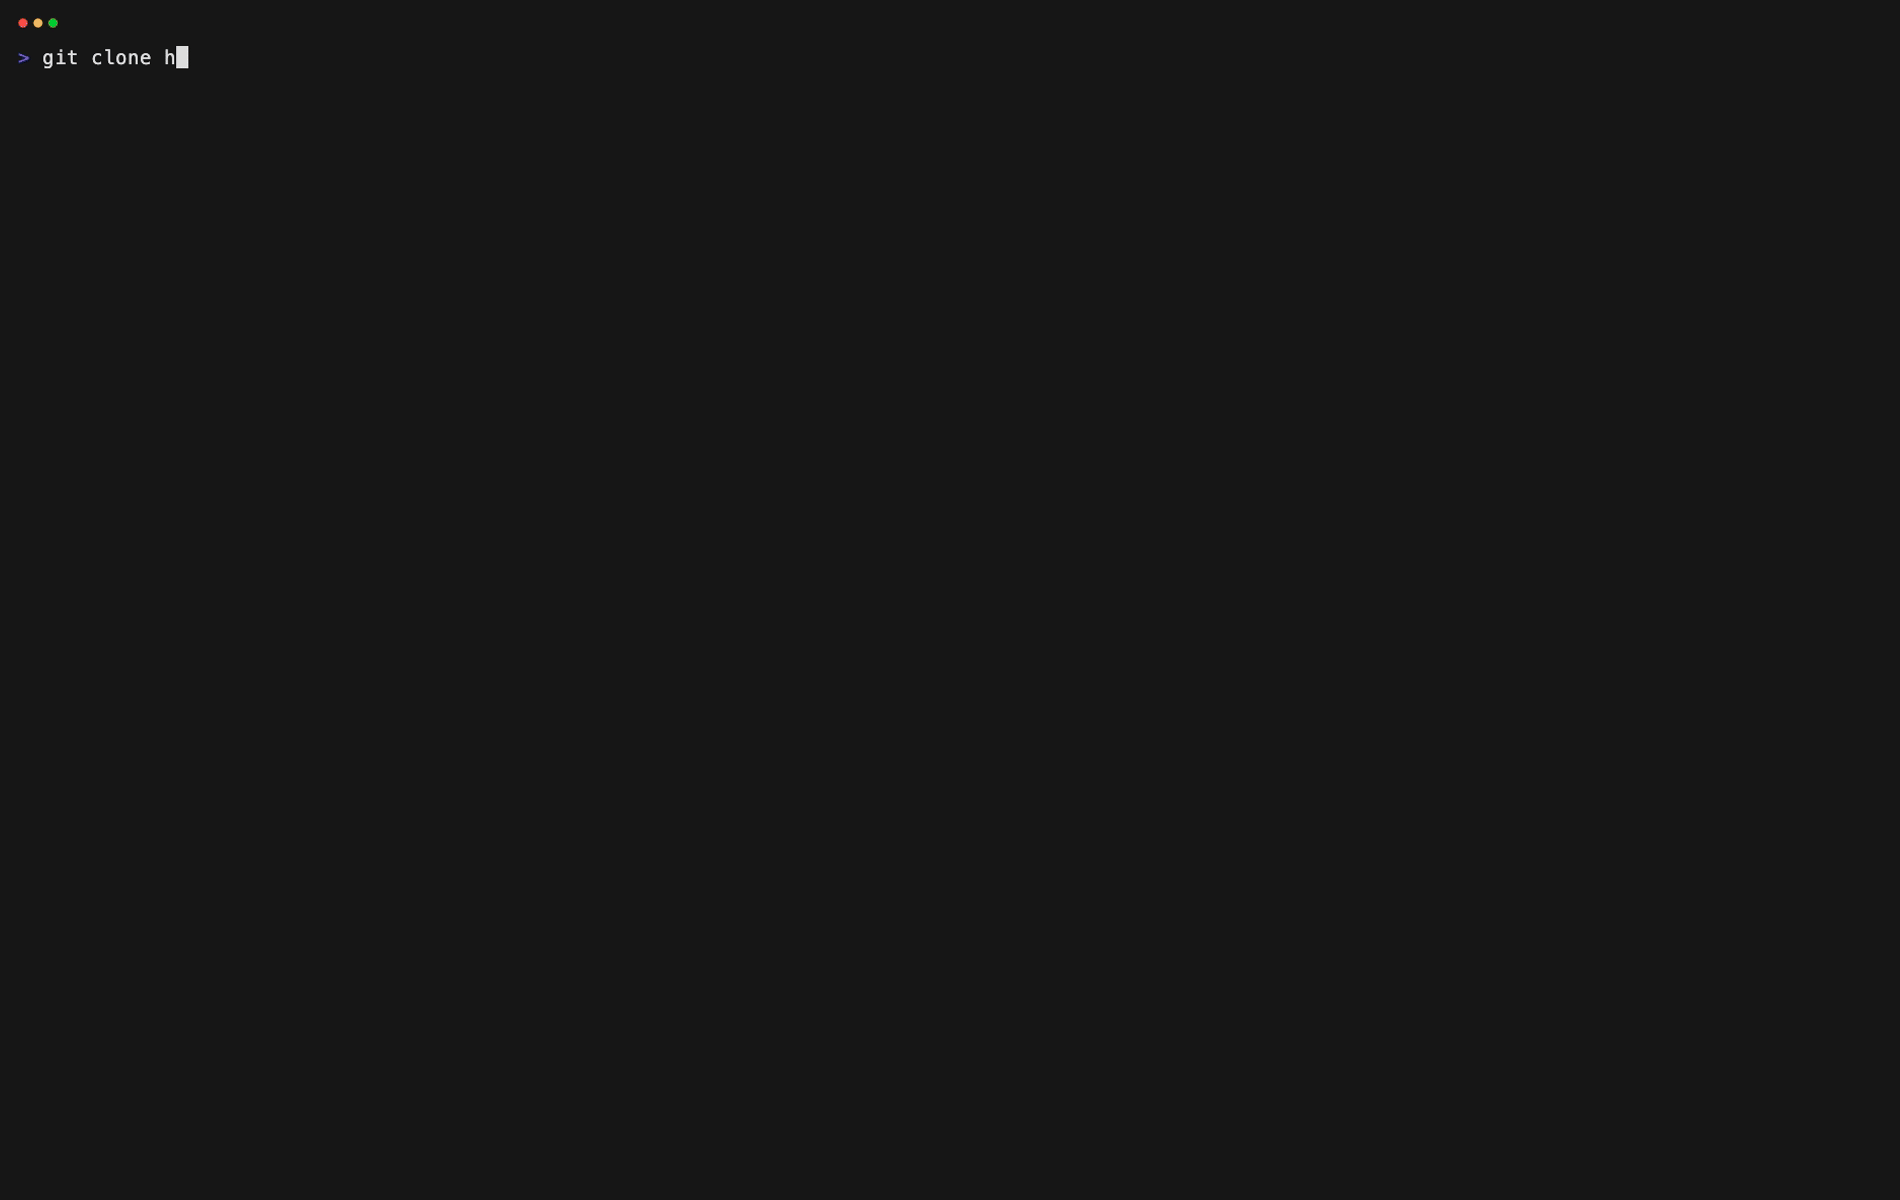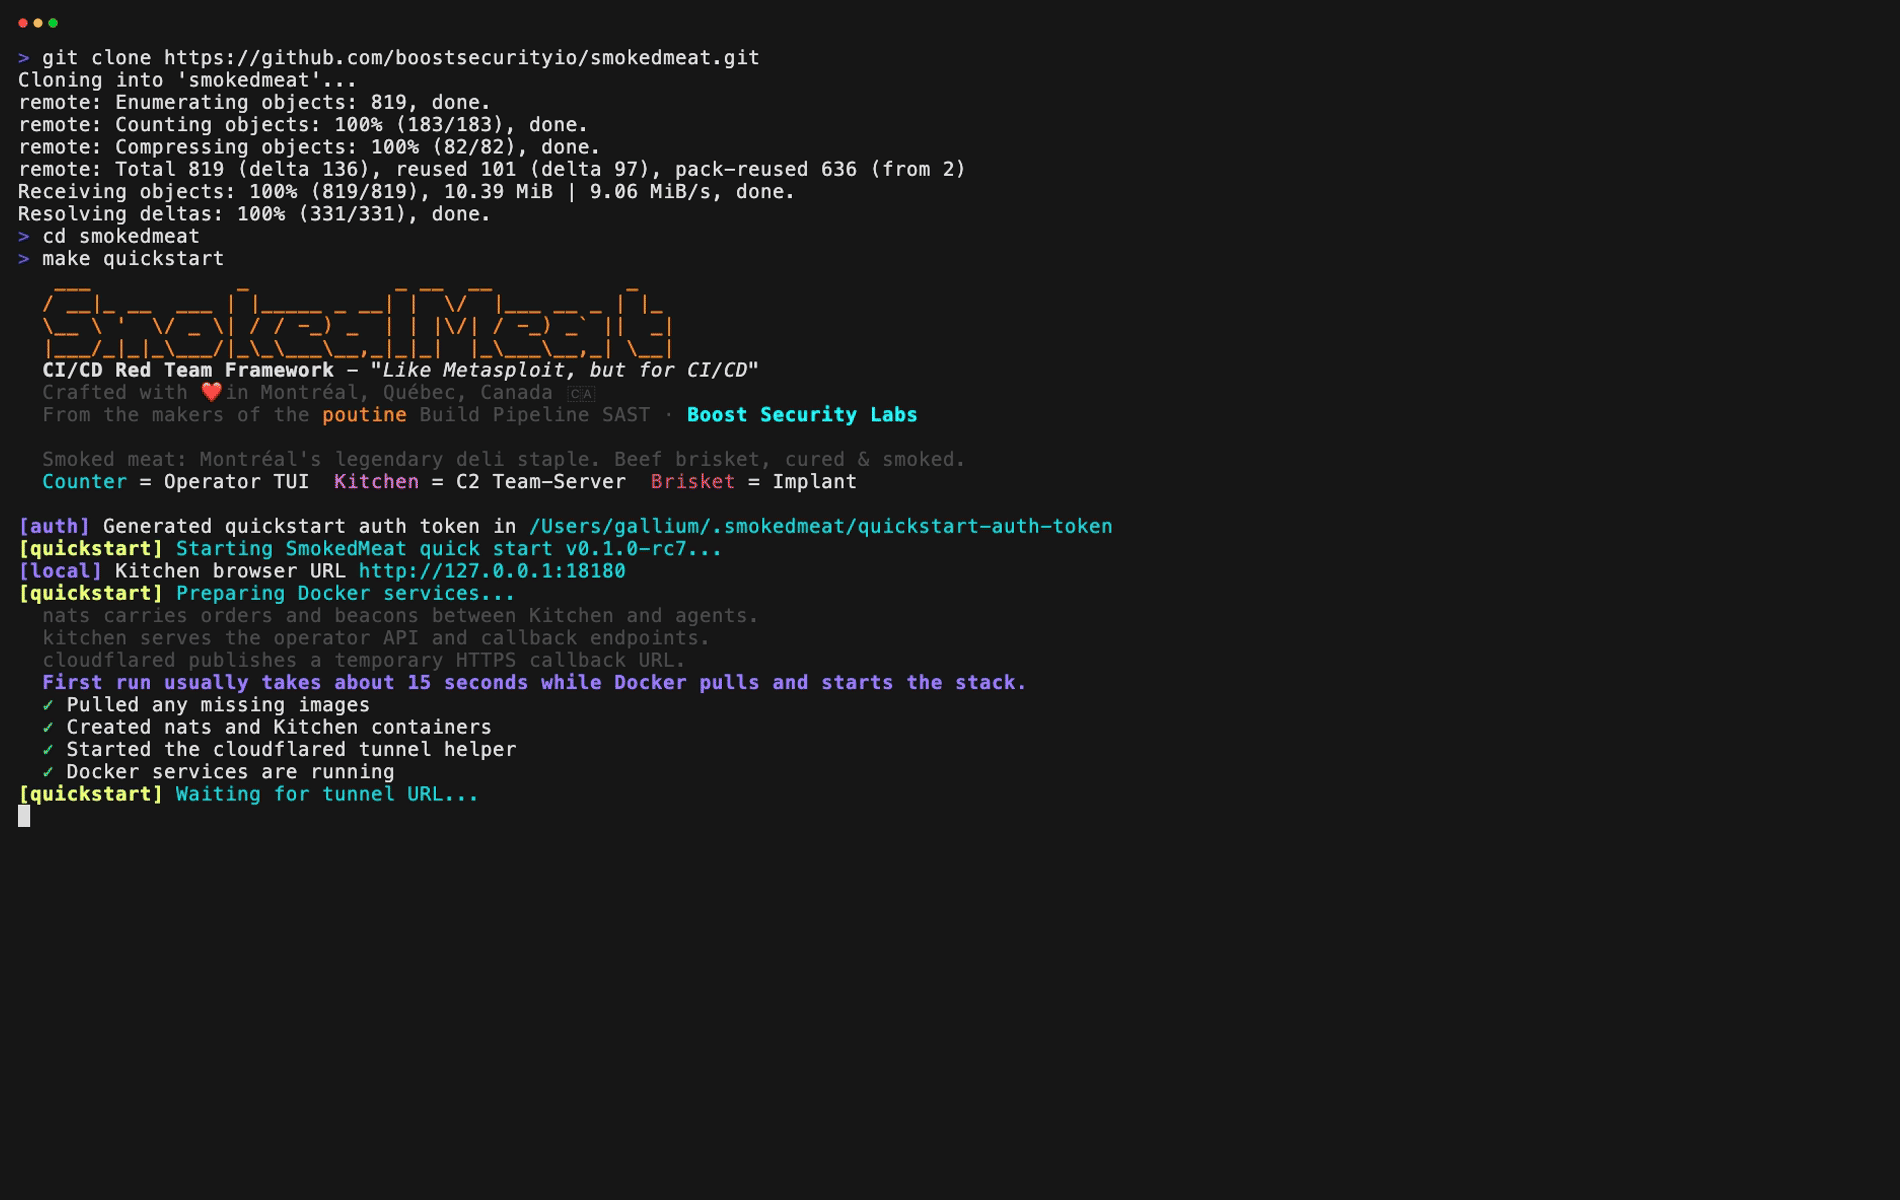
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
cloud-securitycommand-and-controleducation+9
396
boostsecurityio/smokedmeatA CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
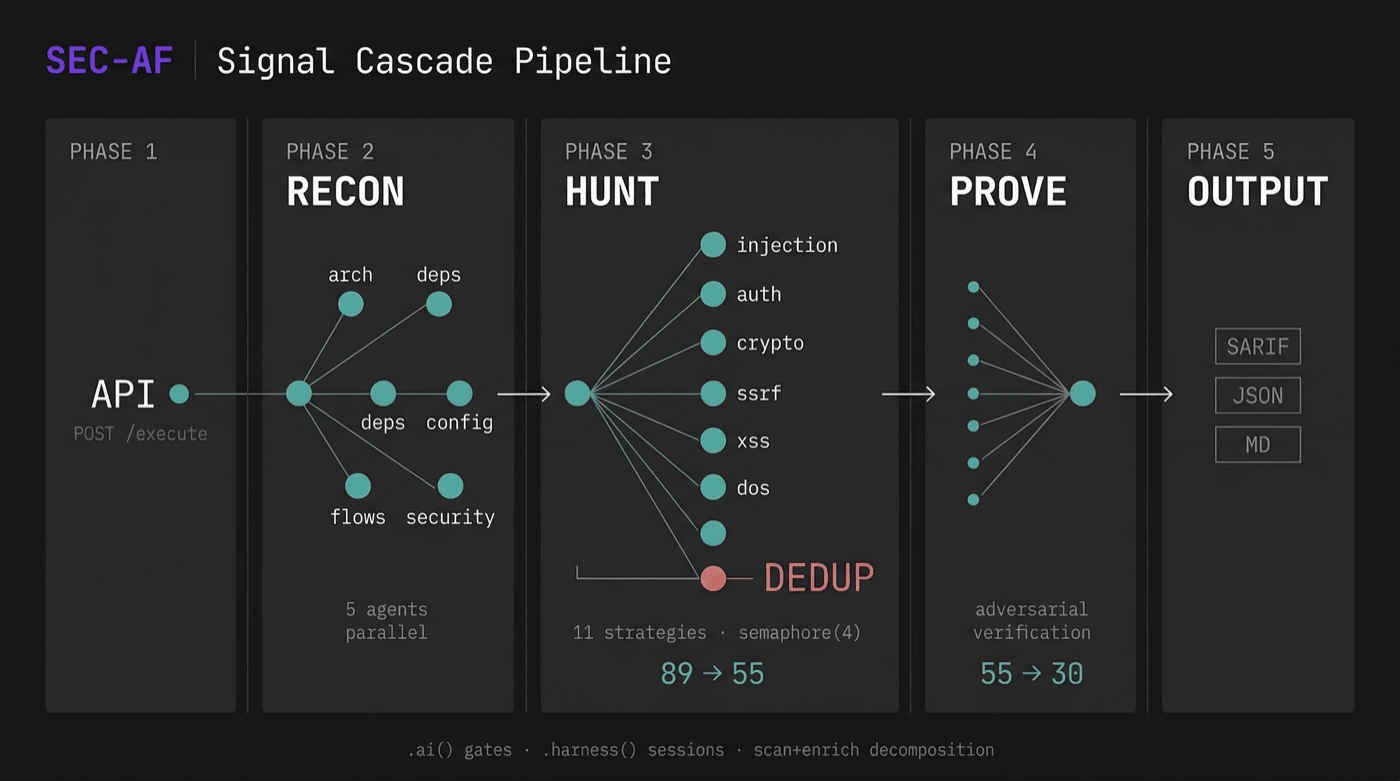 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 abraxas/pfsense-api-acme-key-dump
pfSense Plus MIM API toolkit b4acd7ca - High - Remote - Privilege leftover - GET /services/acme dumps keys
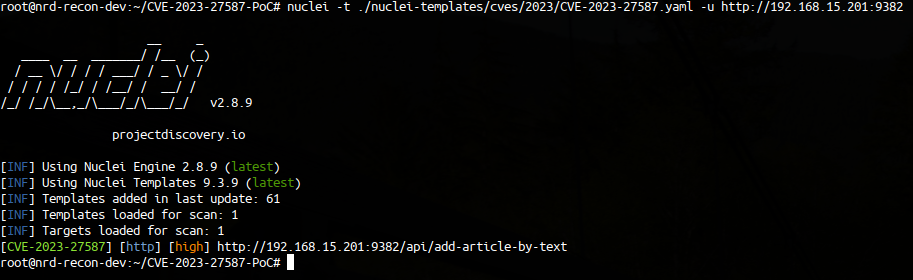 vagnerd/cve-2023-27587-poc
The simple PoC of CVE-2023-27587
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
 saturate/cve-2025-55183
A CVE-2025-55183 secret miner
 im-hanzou/mongobleed
CVE-2025-14847 PoC exploit for MongoDB heap memory disclosure
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
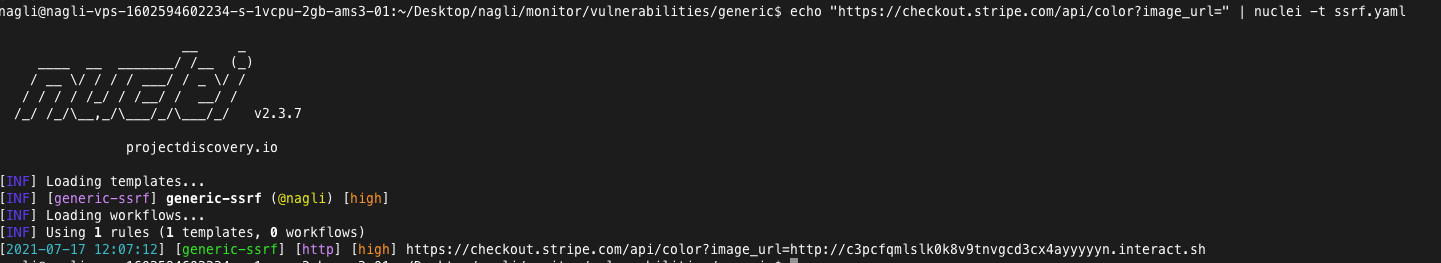 gal-nagli/shockwave-oss
Curated collection of bug bounty tips, one-liners, and automation workflows for recon, fuzzing, and web exploitation, with private nuclei templates…
 watchdogsecurity/porch-pirate
Porch Pirate is the most comprehensive Postman recon / OSINT client and framework that facilitates the automated discovery and exploitation of API…