
horusec
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
cloud-securitycode-analysiscontainer-security+5
1.3k3 years ago
zupit/horusecHorusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 teycir/diffcatcher
A Rust CLI tool that recursively discovers Git repositories, captures state changes, generates diffs, extracts code elements with full snippets, and…
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 playtikaoss/leaktopus
Automated secret and leak detection scanner for GitHub and paste sites, with heuristic filtering, IOL enrichment via Shhgit/TruffleHog, and ELK-based…
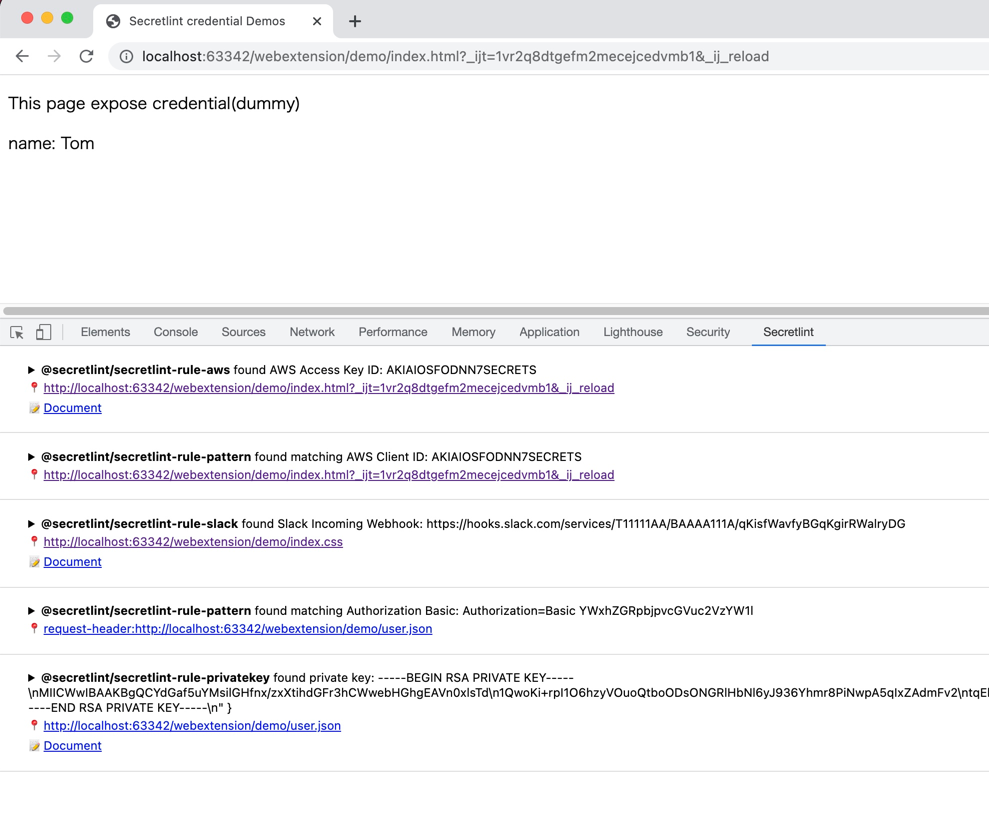 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 unkl4b/gitminer
Tool for advanced mining for content on Github
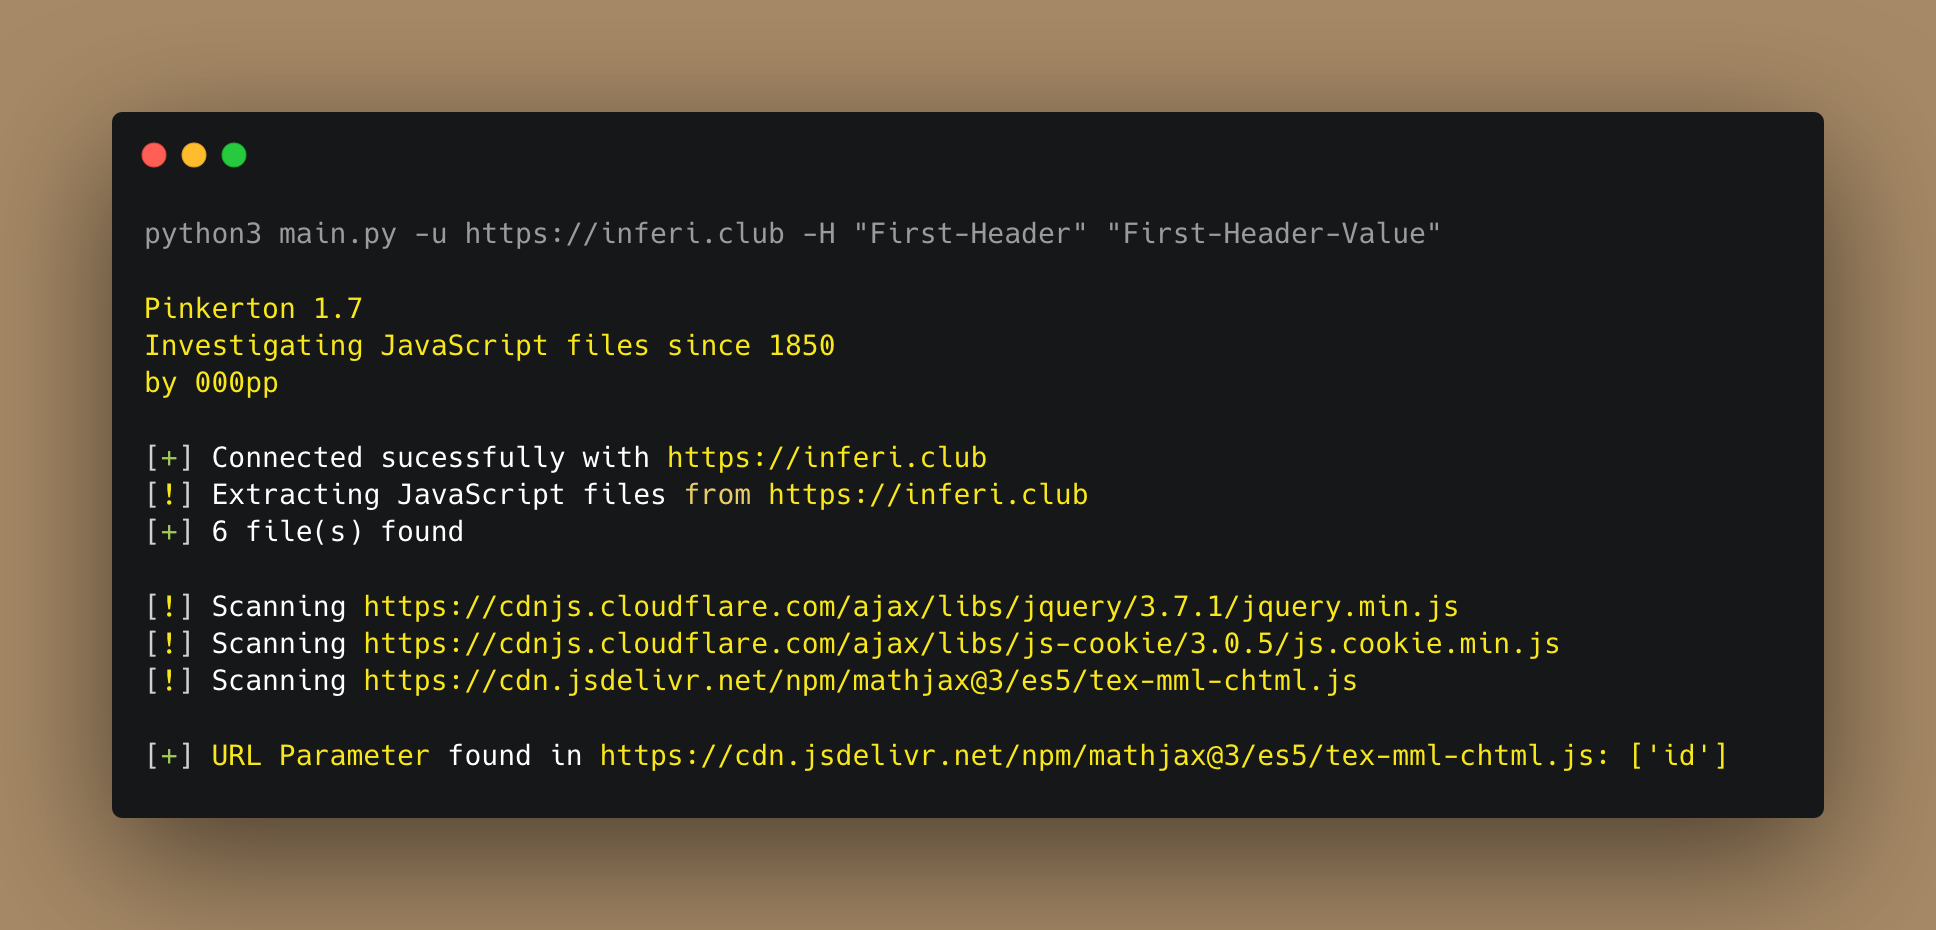 0xdsm/pinkerton
🕵️ Python project to crawl for JavaScript files and search for secrets like API keys, authorization tokens, hardcoded credentials, etc.
 owasp/secure-agent-playbook
OWASP Secure Agent Playbook Project
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
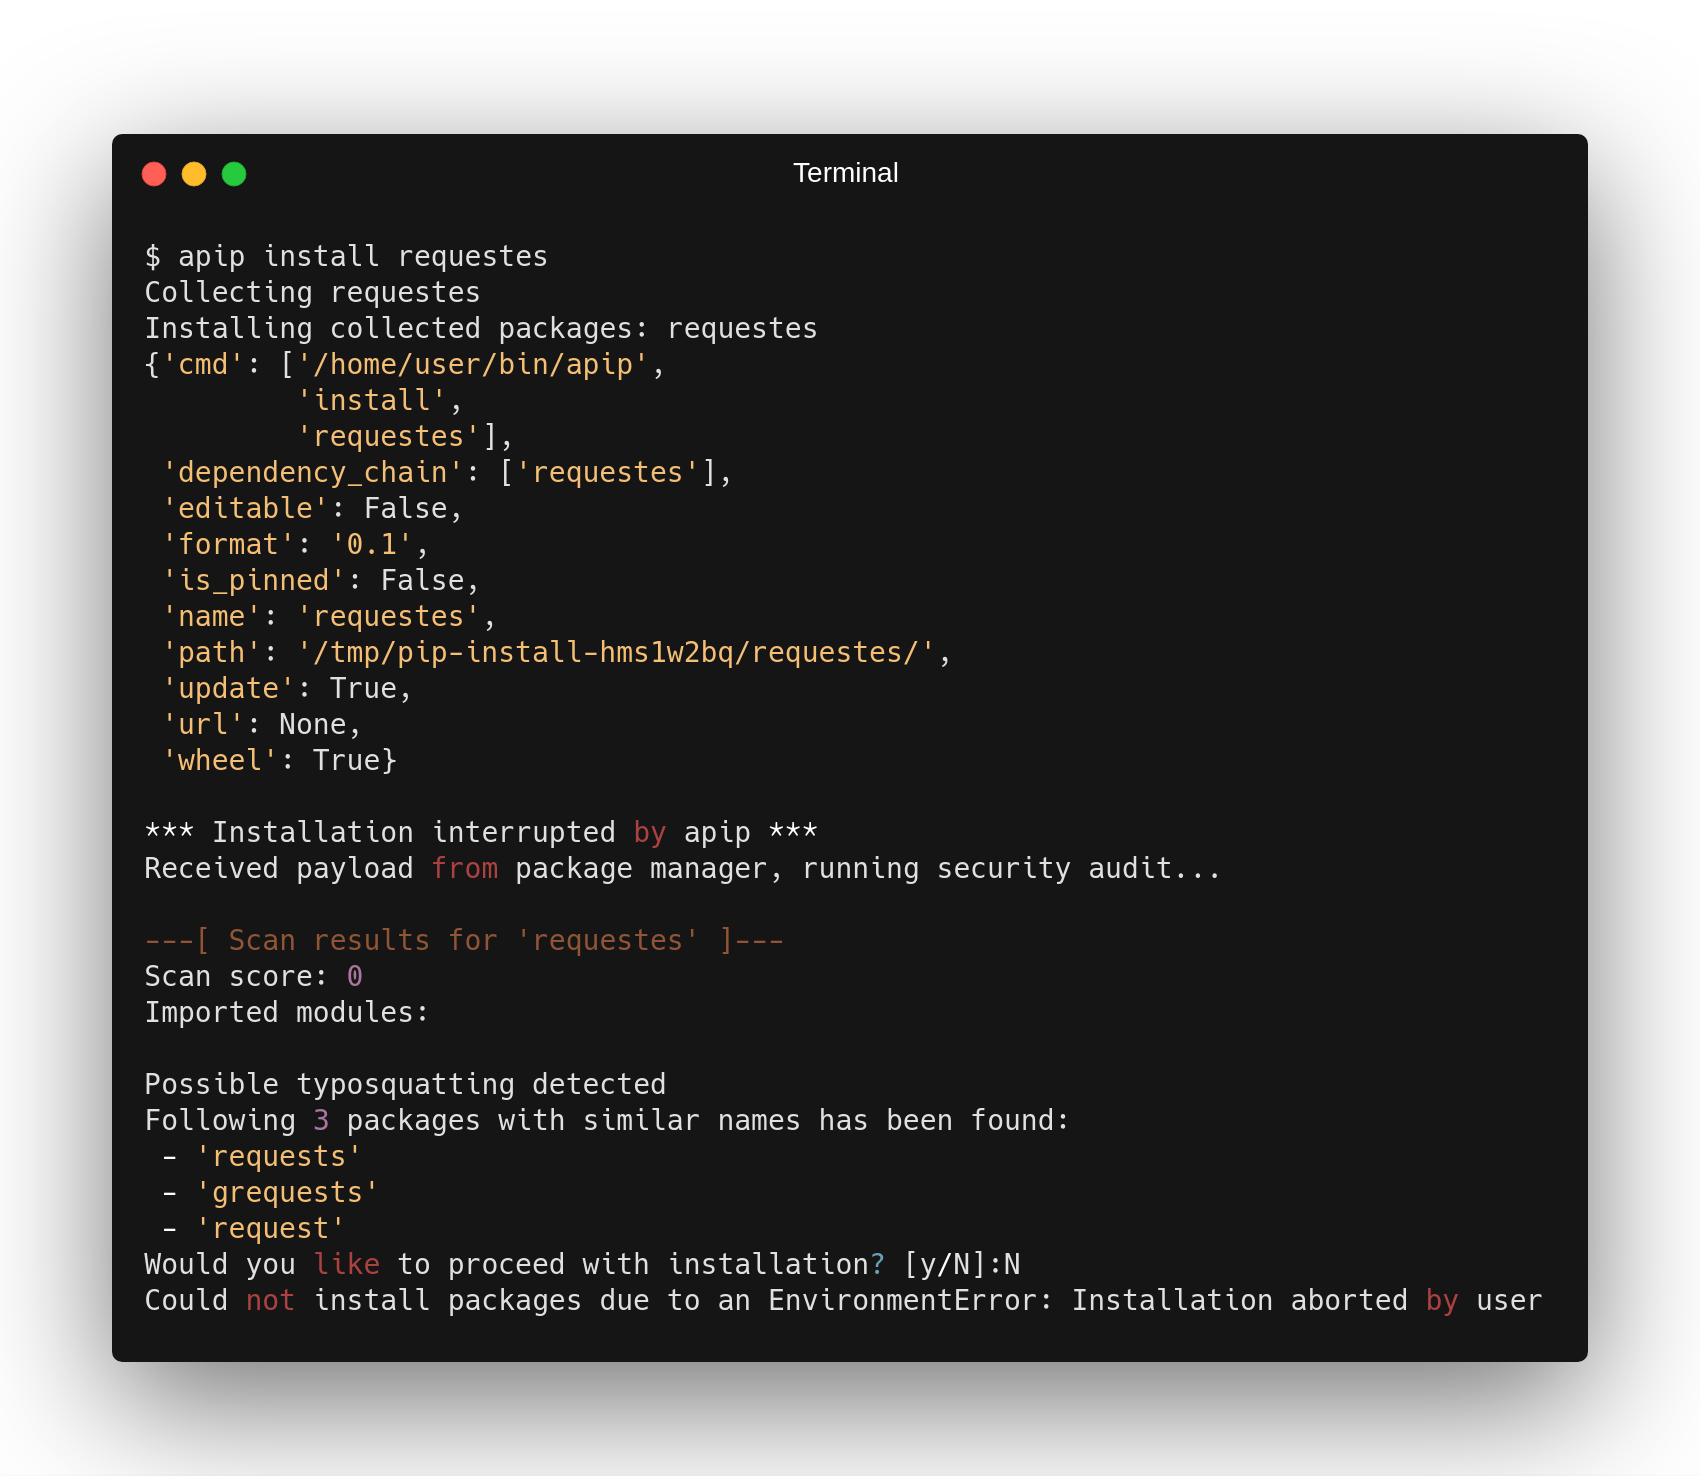 rootlug/aura
Project Aura: Security auditing and code introspection
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency.
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…