
BFScan
 blackfan/bfscan
Tool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
android-securityapi-securityinformation-gathering+5
257
blackfan/bfscanTool for finding URLs, paths, secrets and generating raw HTTP requests and OpenApi specifications from config files and annotations used in JAR / WAR…
 kalix127/secret-stripper
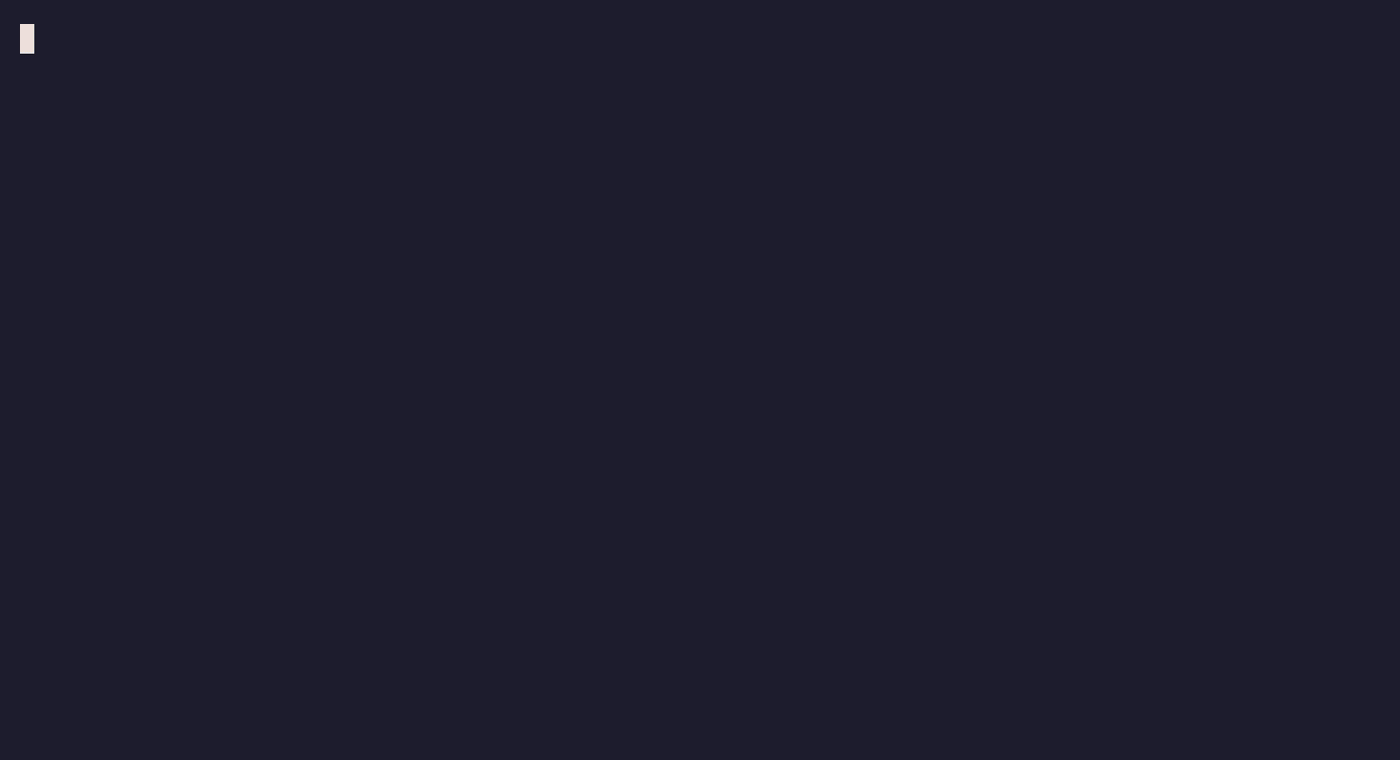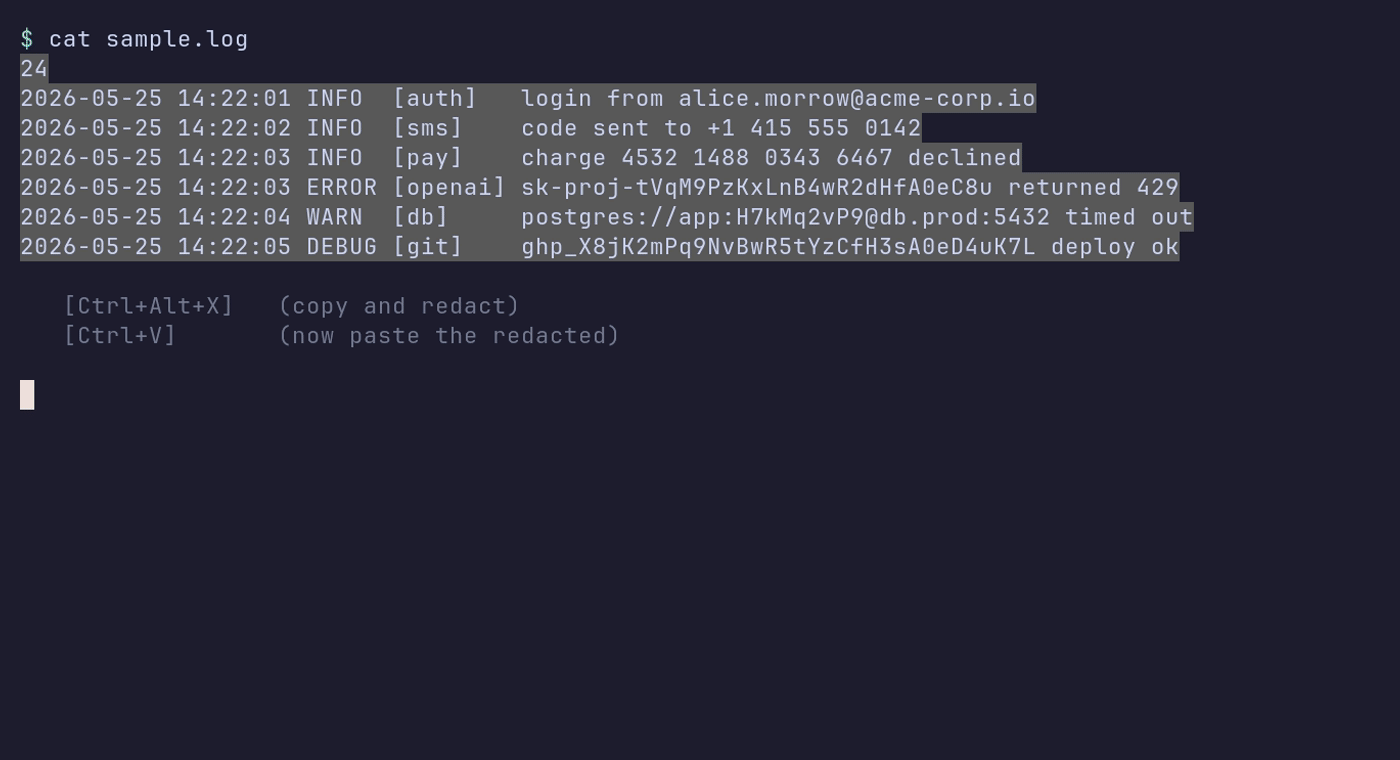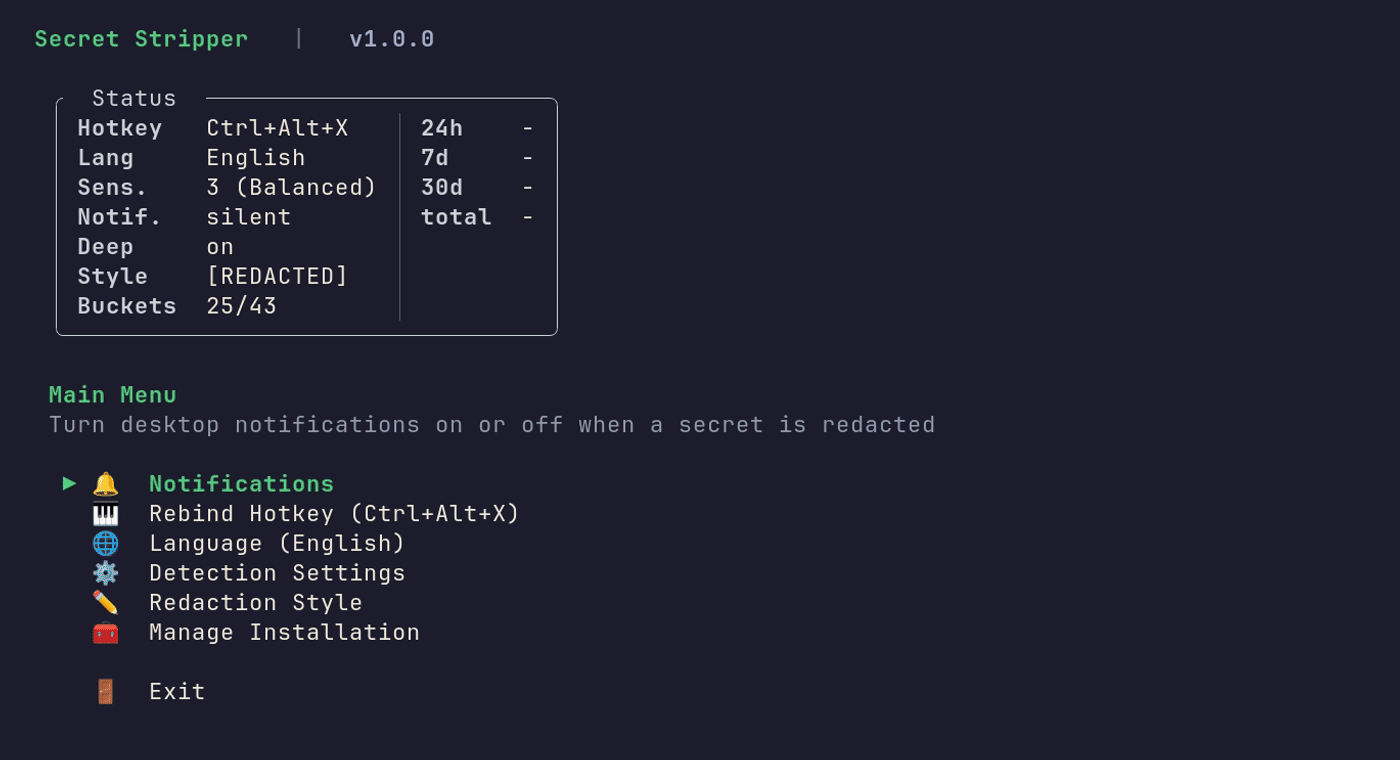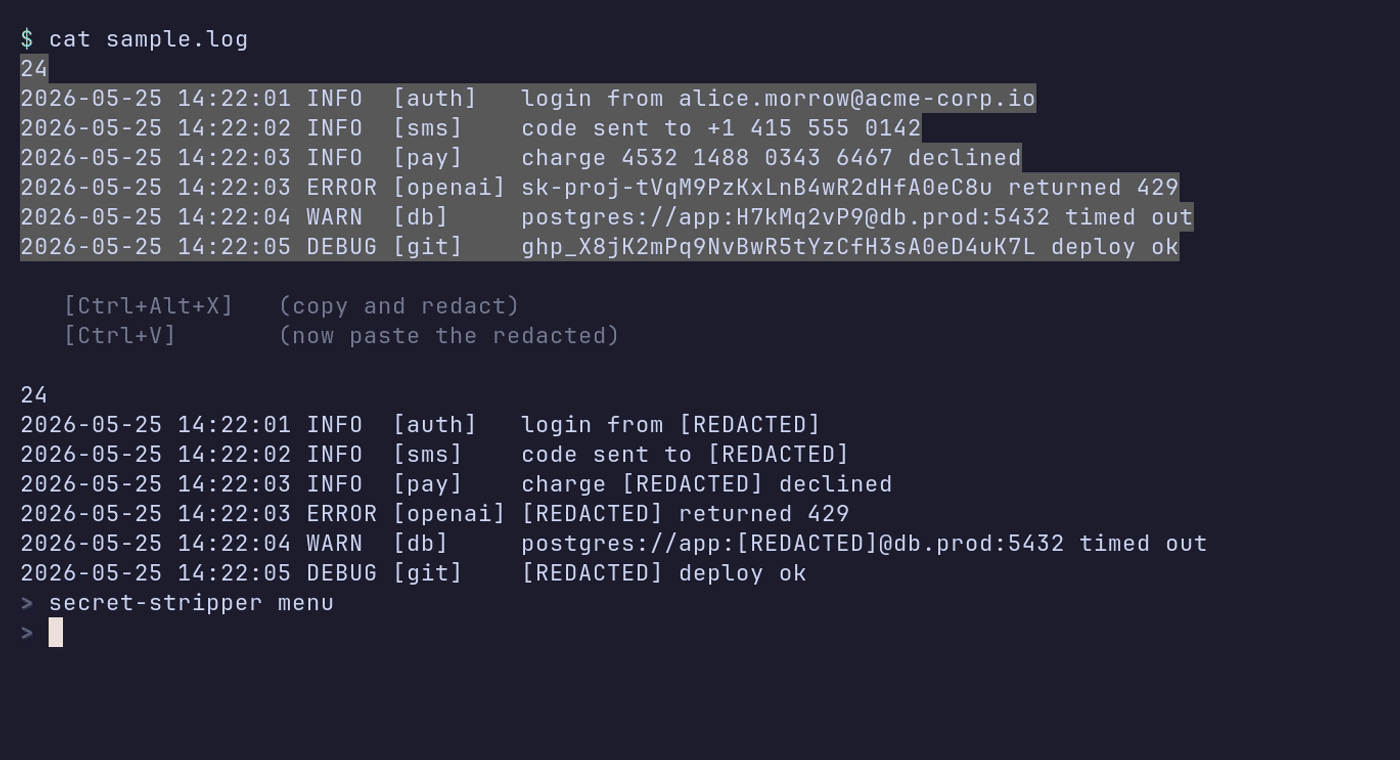
A small Rust CLI that strips secrets from your clipboard on demand.
 cybertechajju/cve-2025-14847_expolit
a critical memory disclosure vulnerability in MongoDB's zlib compression handling. This tool allows security researchers to extract sensitive data…
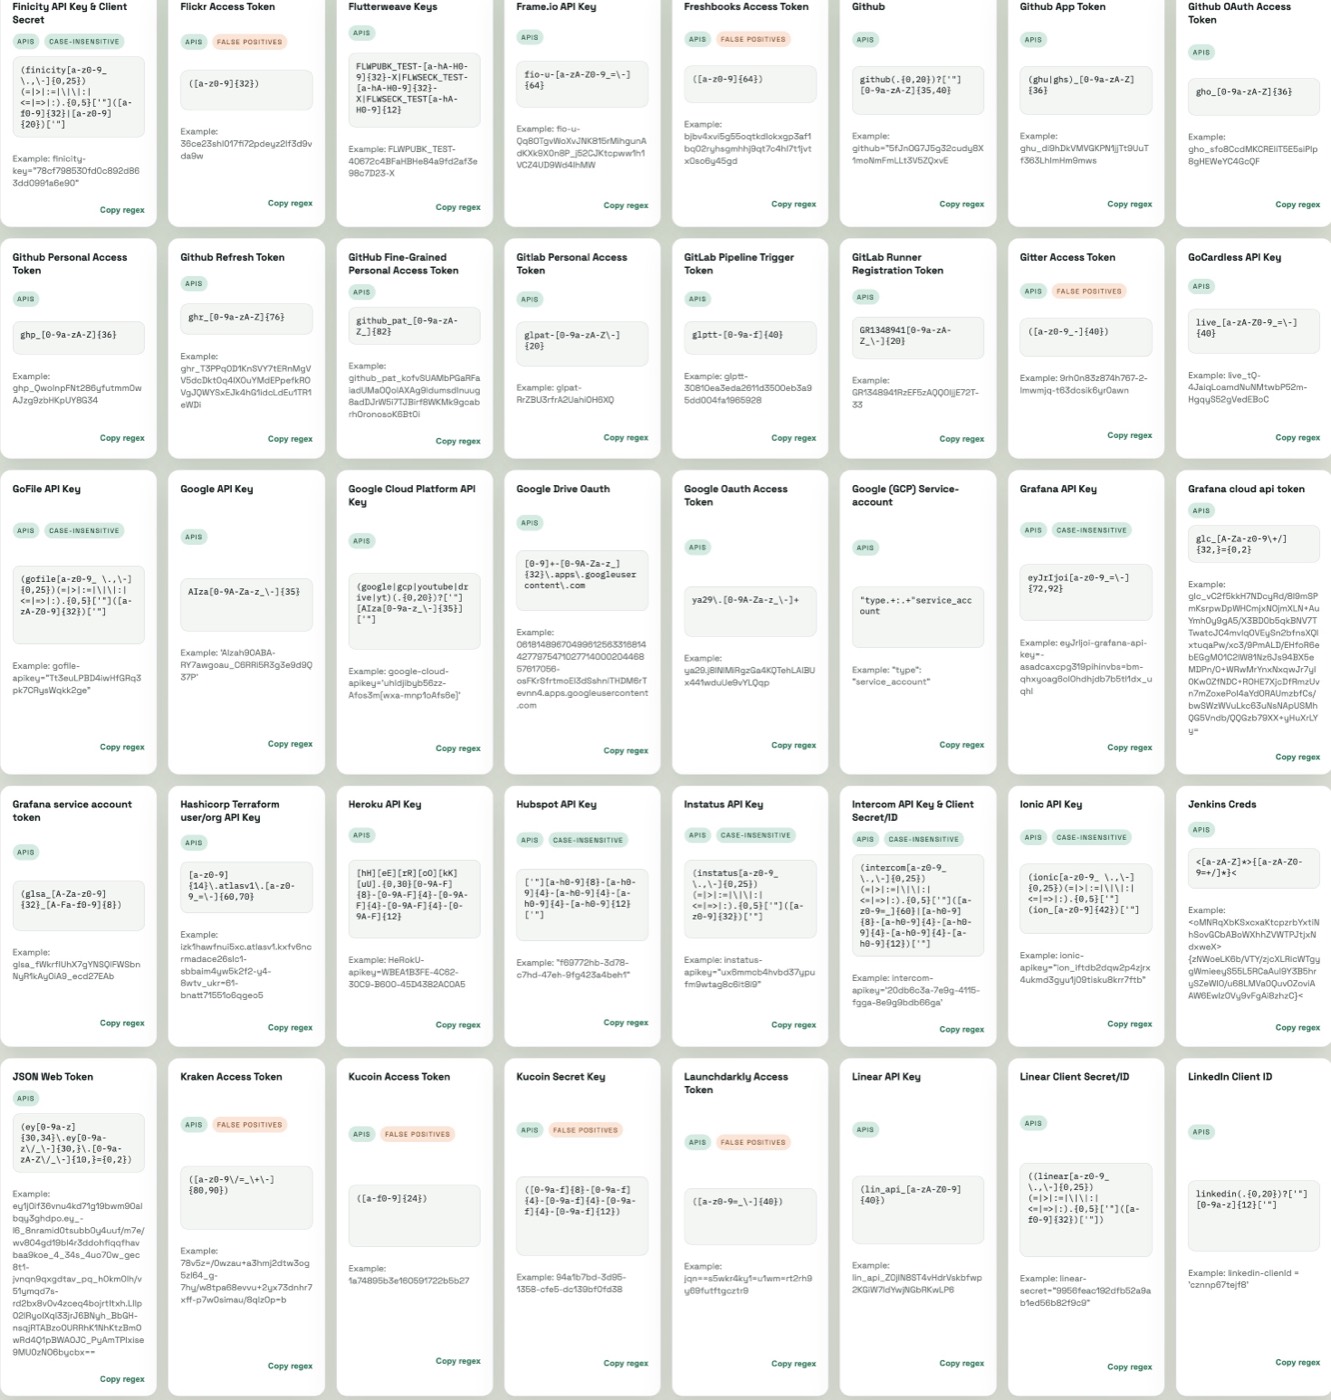 adversis/screenscrub
Find credentials in screenshots, save them to your secret manager, and irreversibly redact them from the image — local, offline, OCR-based.
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
 streaak/keyhacks
Curated collection of commands to validate leaked API keys from bug bounty programs and penetration tests, covering 80+ services including AWS,…
 devsecops/awesome-devsecops
An authoritative list of awesome devsecops tools with the help from community experiments and contributions.
 awslabs/git-secrets
Prevents you from committing secrets and credentials into git repositories
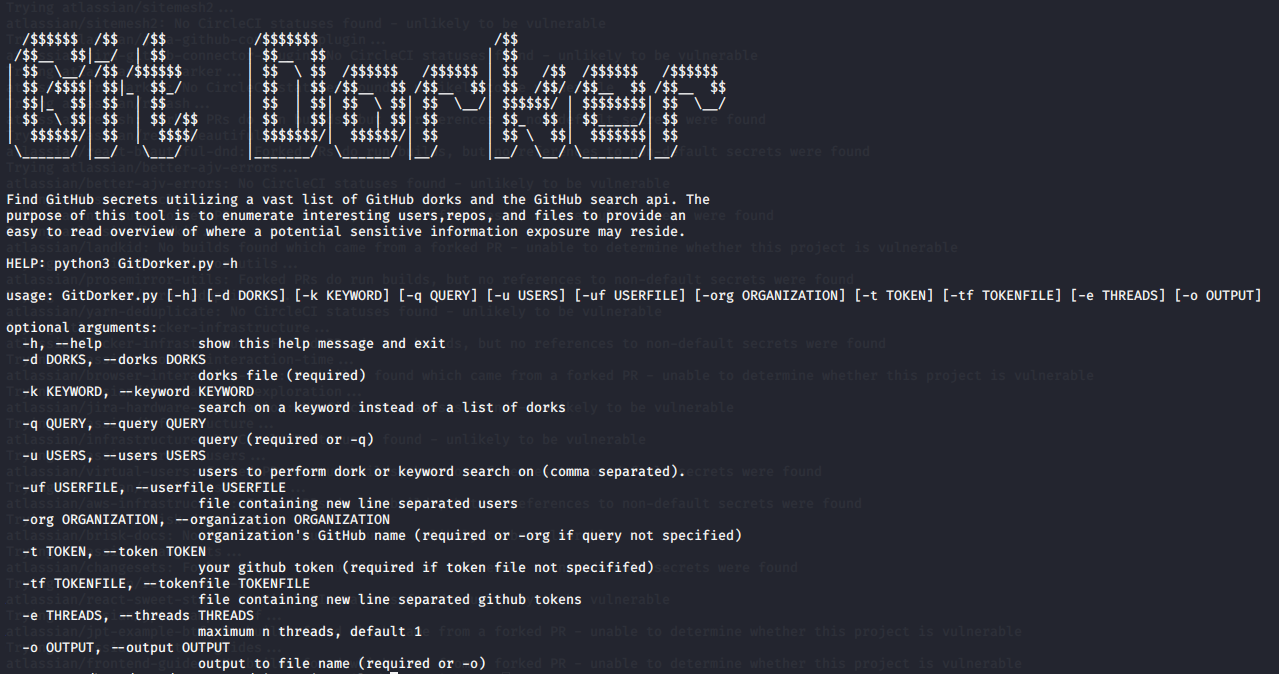 obheda12/gitdorker
A Python program to scrape secrets from GitHub through usage of a large repository of dorks.
 bishopfox/jsluice
Extract URLs, paths, secrets, and other interesting bits from JavaScript
 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 safedep/pmg
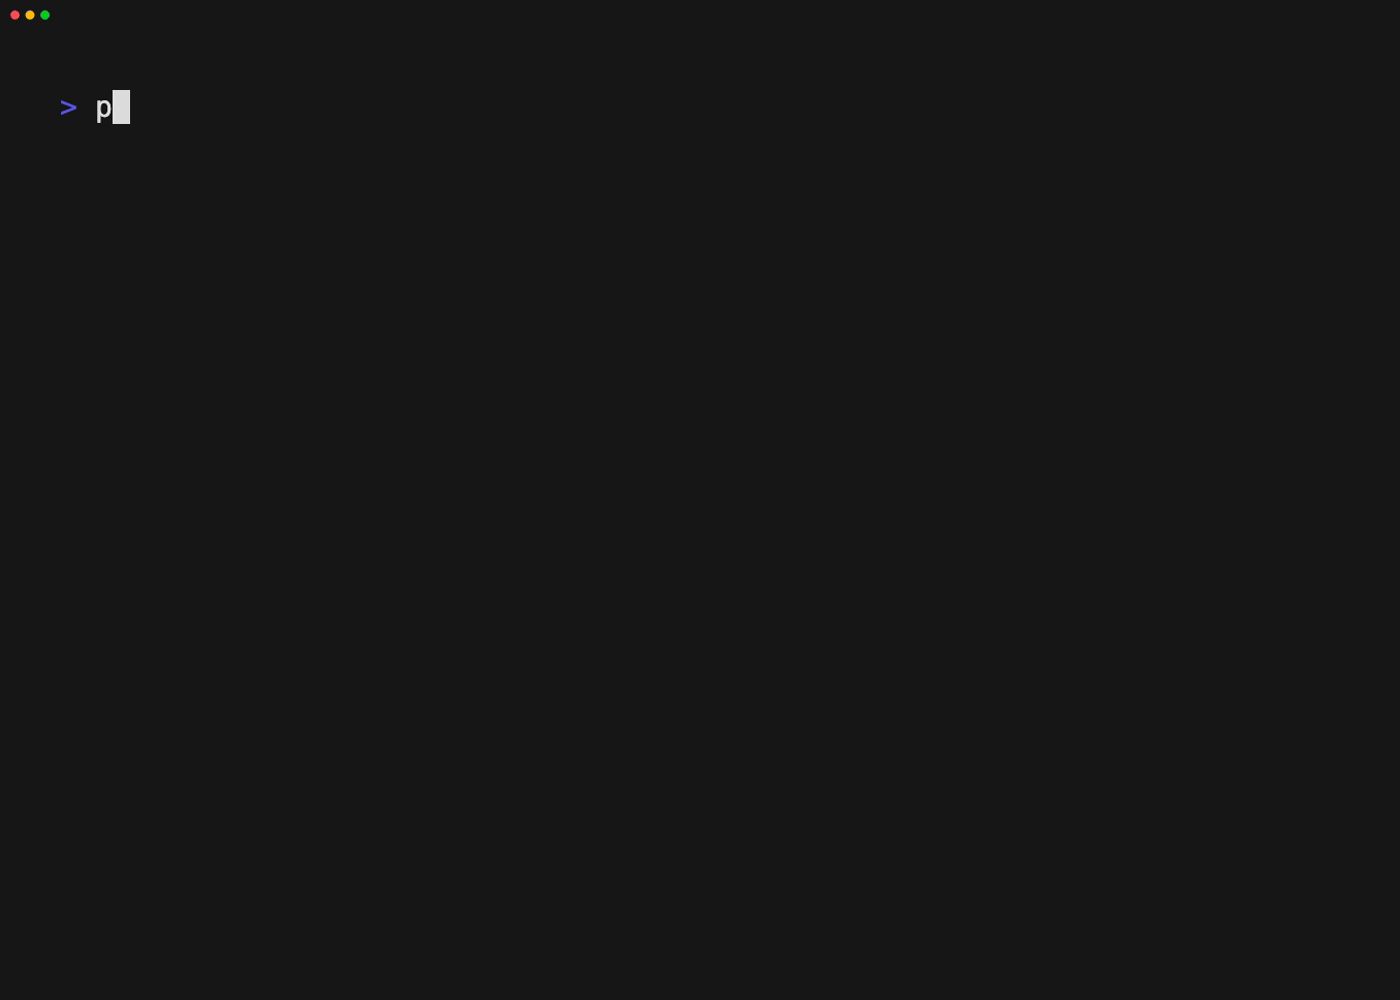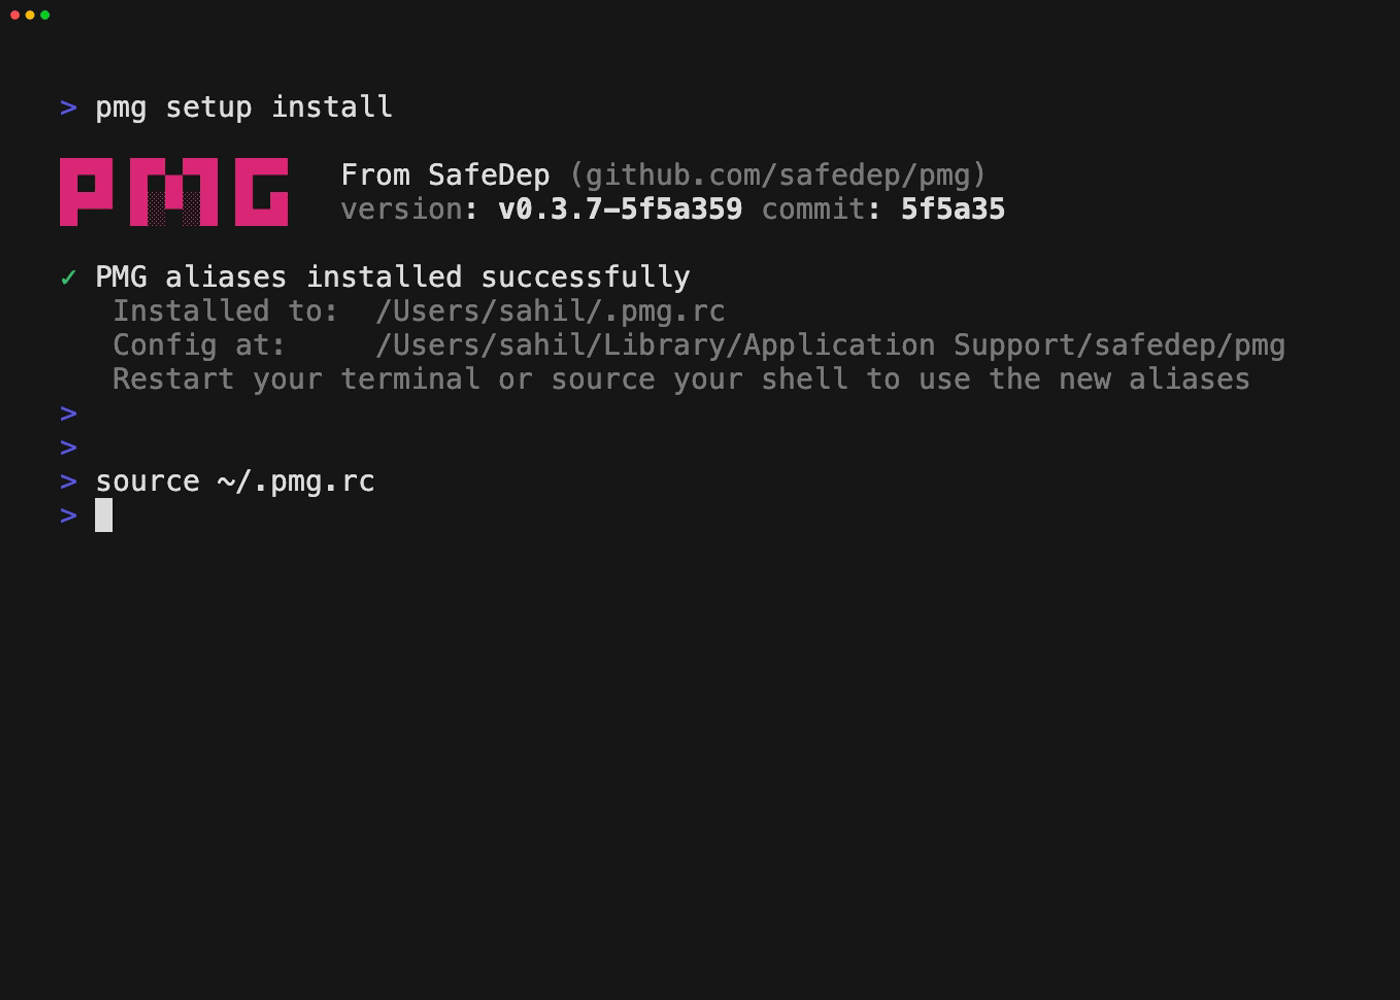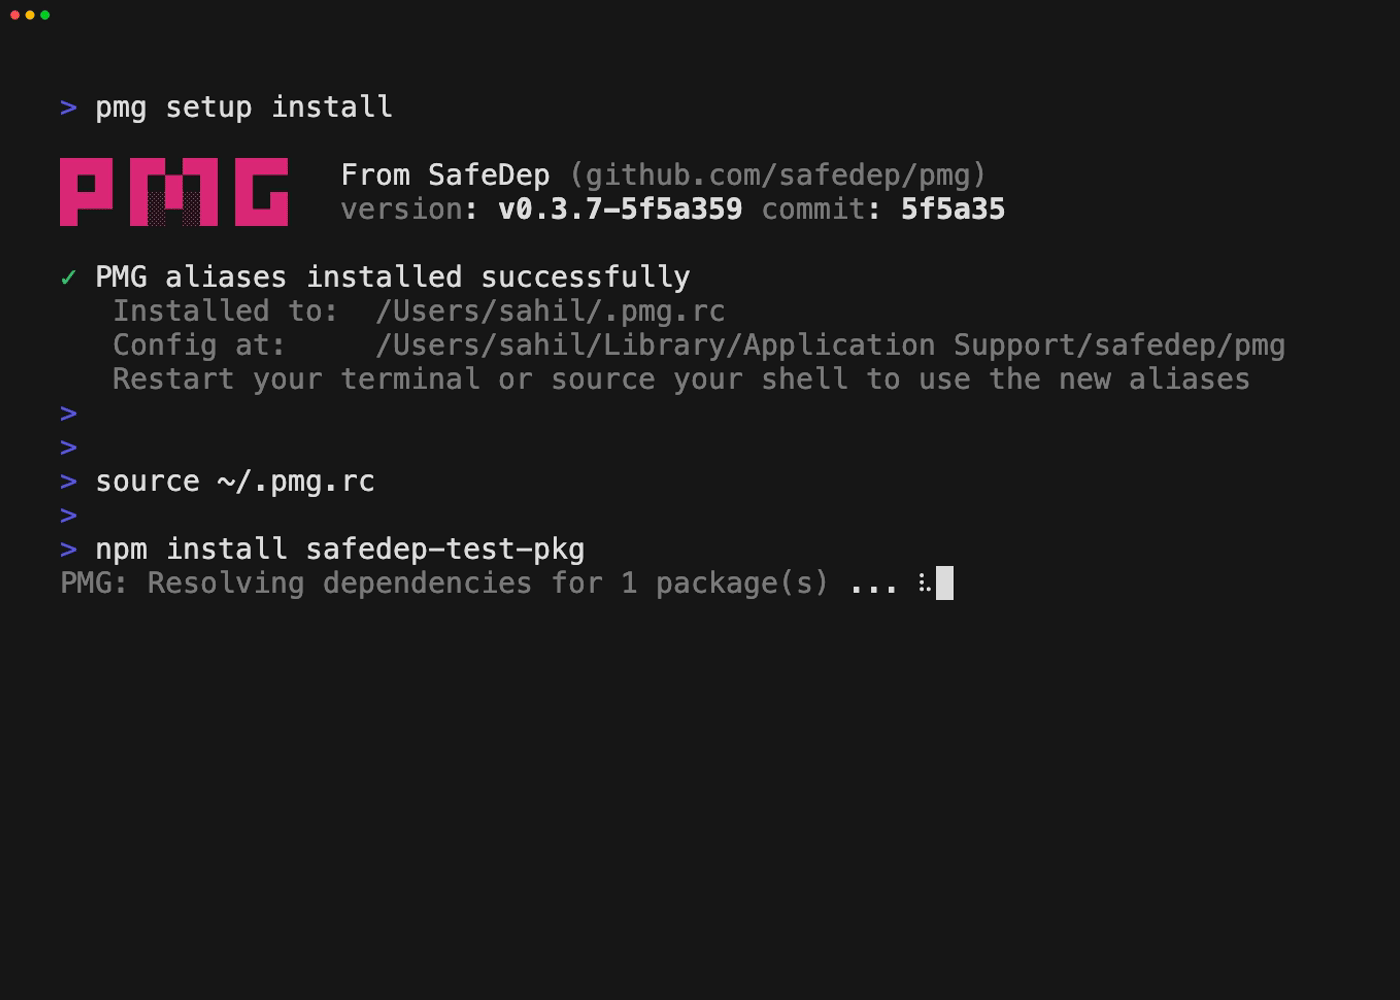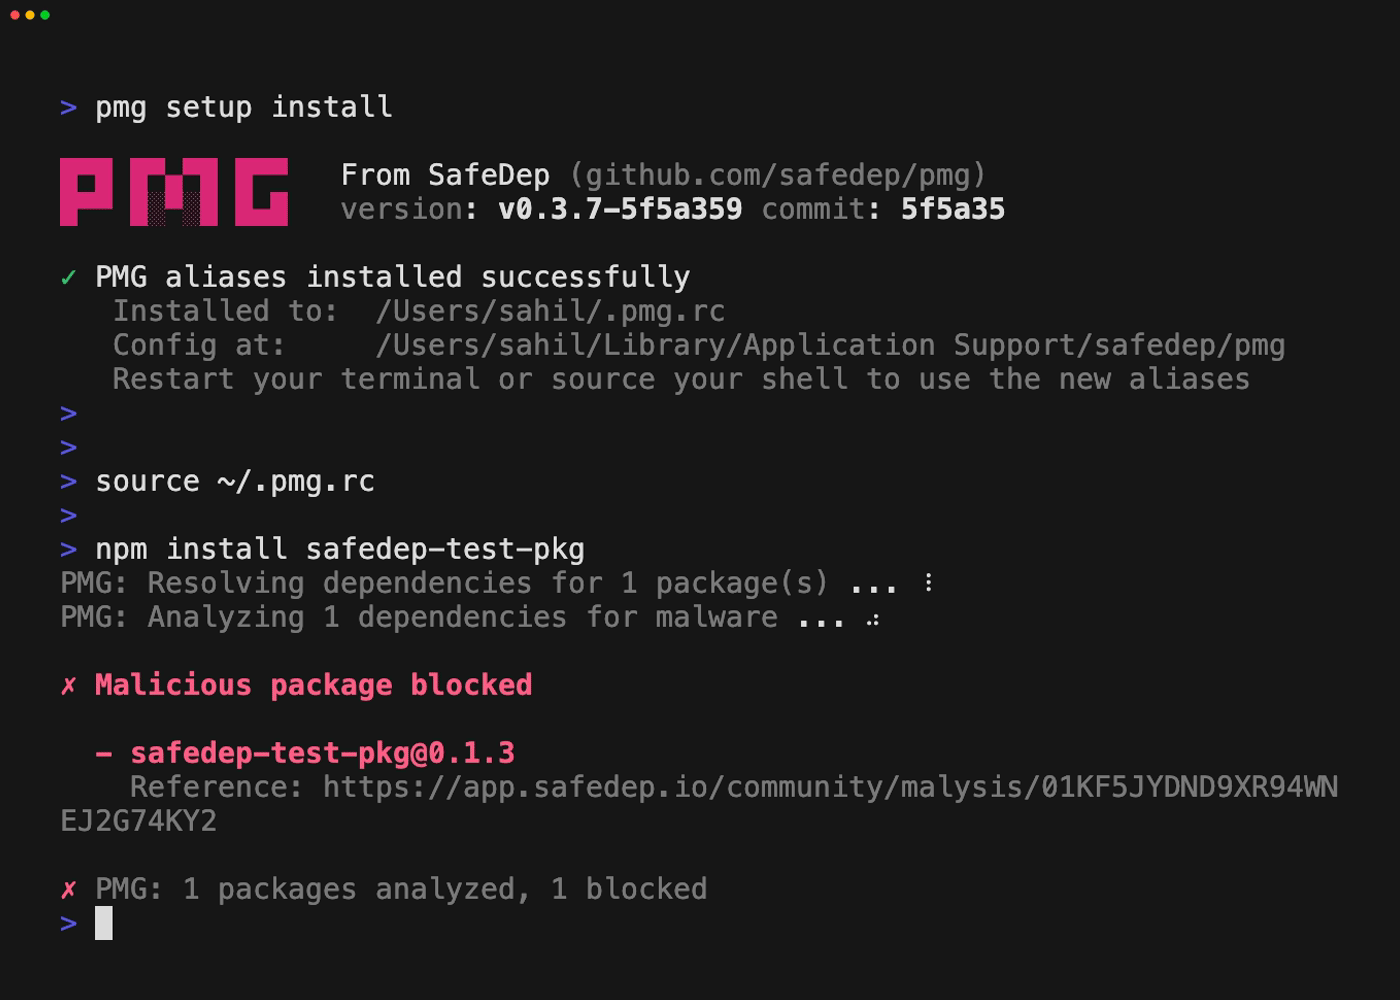
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
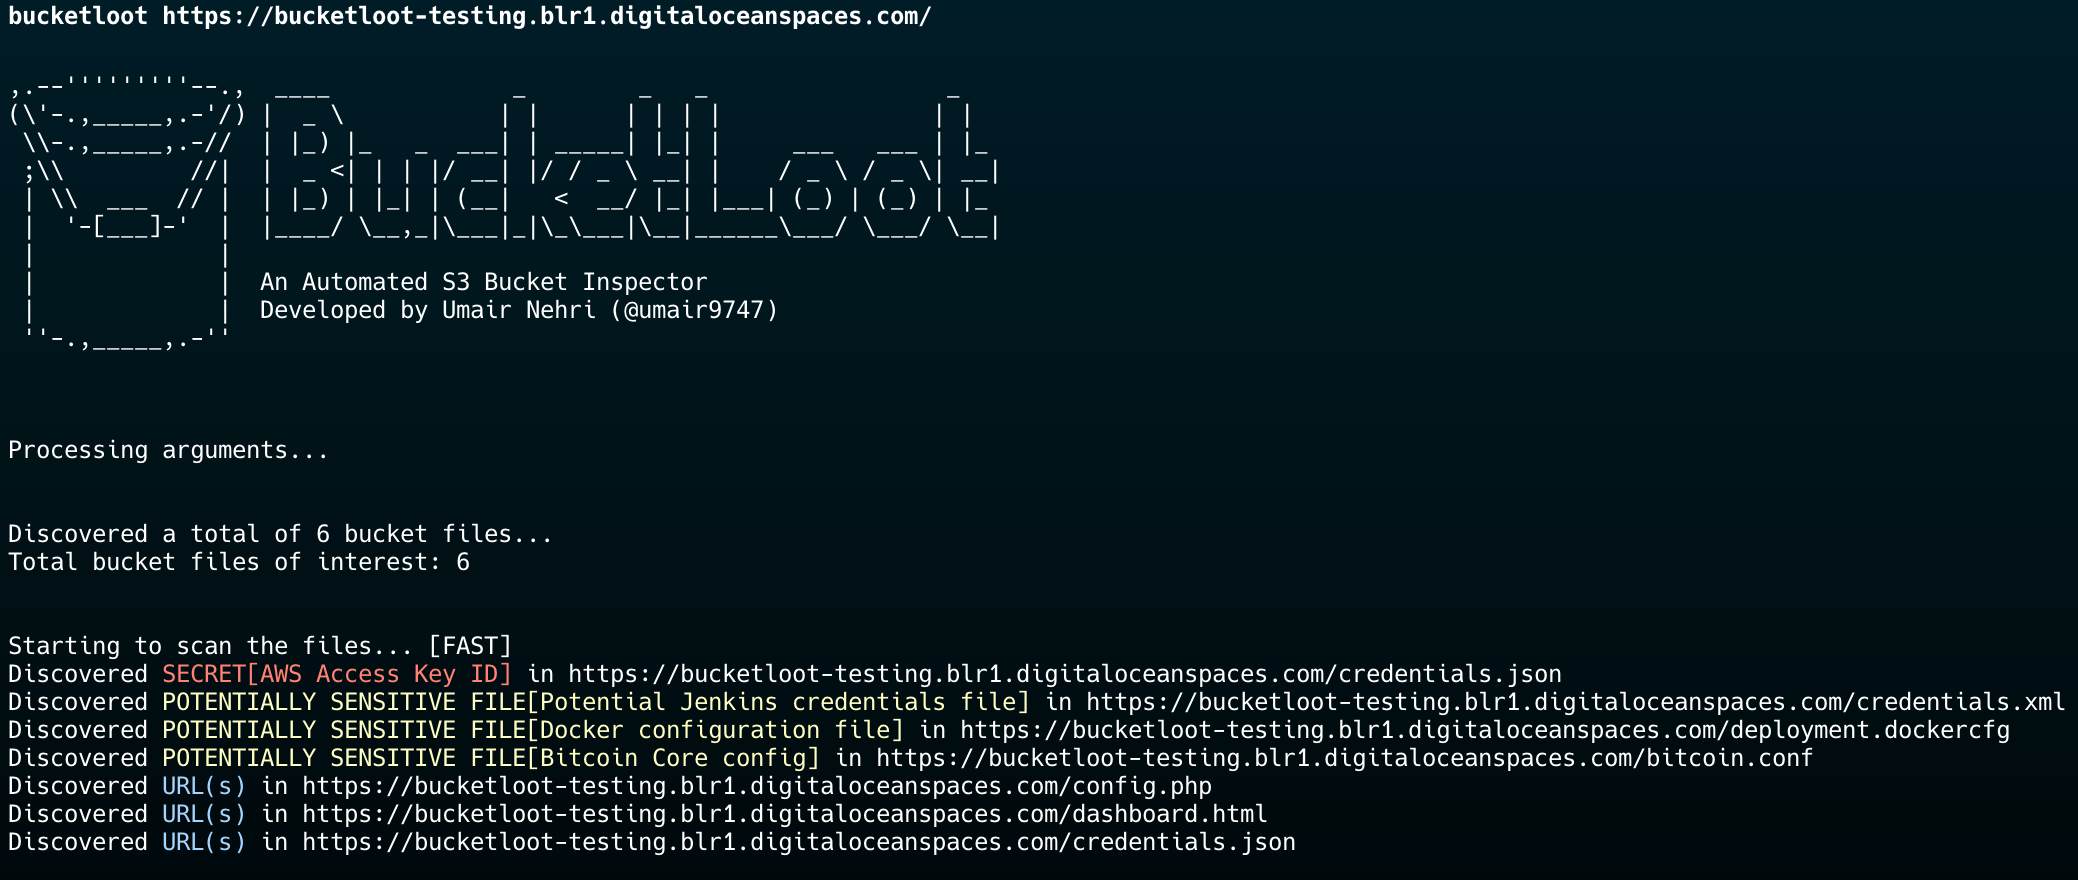 redhuntlabs/bucketloot
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…
 greatscott/enject
enject: Hide .env secrets from prAIng eyes: secrets live in local encrypted stores (per project) and are injected directly into apps at runtime,…
 s0md3v/hardcodes
find hardcoded strings from source code
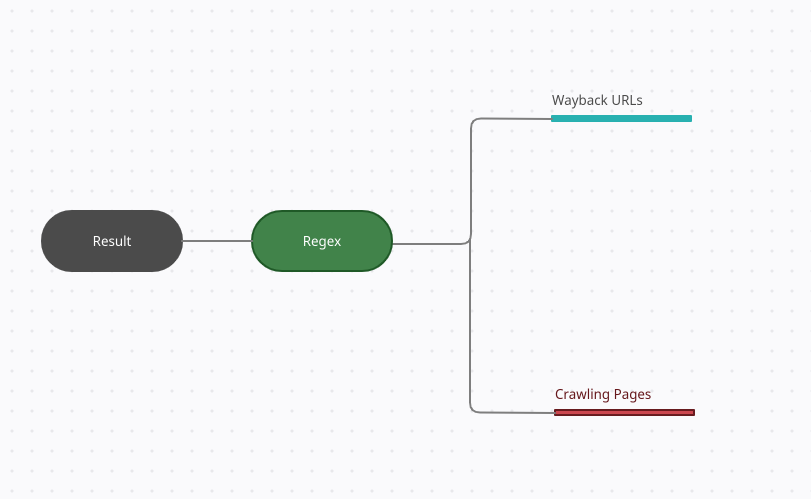 h33tlit/jbin-website-secret-scraper
Jbin will gather all the URLs from the website and then it will try to expose the secret data from them such as API keys, API secrets, API tokens and…
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
 piratesshield/apiharvester
The one shot API attacker tool - finds the API url from the given root simulate the automated attacks