
Archived
jsleak
 0xteles/jsleak
a Go code to detect leaks in JS files via regex patterns
information-gatheringosintreconnaissance+3
0xteles/jsleaka Go code to detect leaks in JS files via regex patterns
 brosck/mantra
「🔑」A tool used to hunt down API key leaks in JS files and pages
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
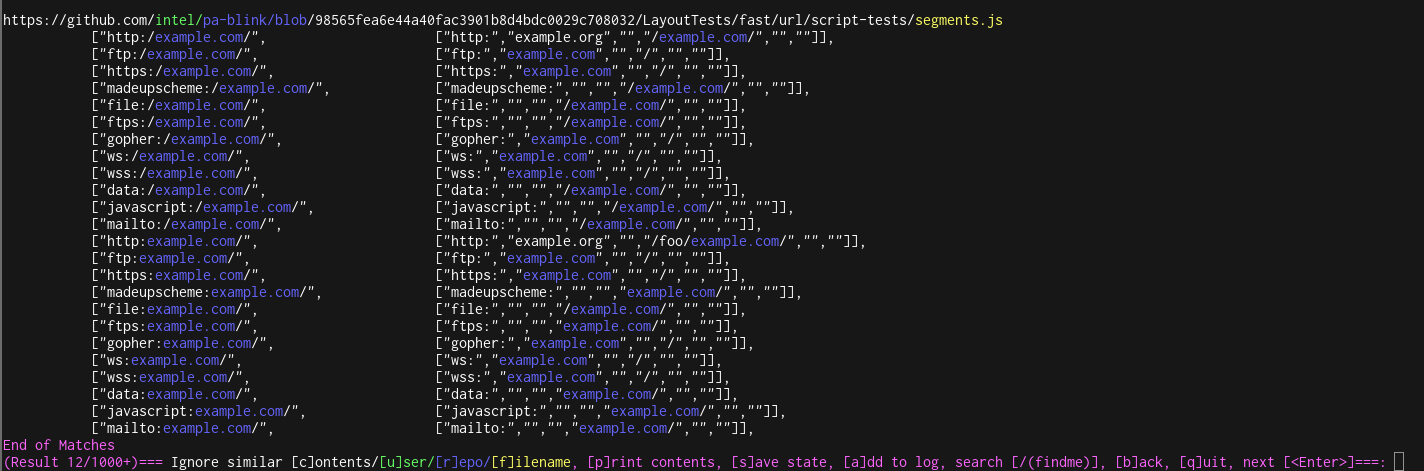 bishopfox/gitgot
Semi-automated, feedback-driven tool to rapidly search through troves of public data on GitHub for sensitive secrets.
 michenriksen/gitrob
Reconnaissance tool for GitHub organizations
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 ustayready/golddigger
Recursively searches files for sensitive information using customizable regex patterns, designed for penetration testers to rapidly discover secrets…
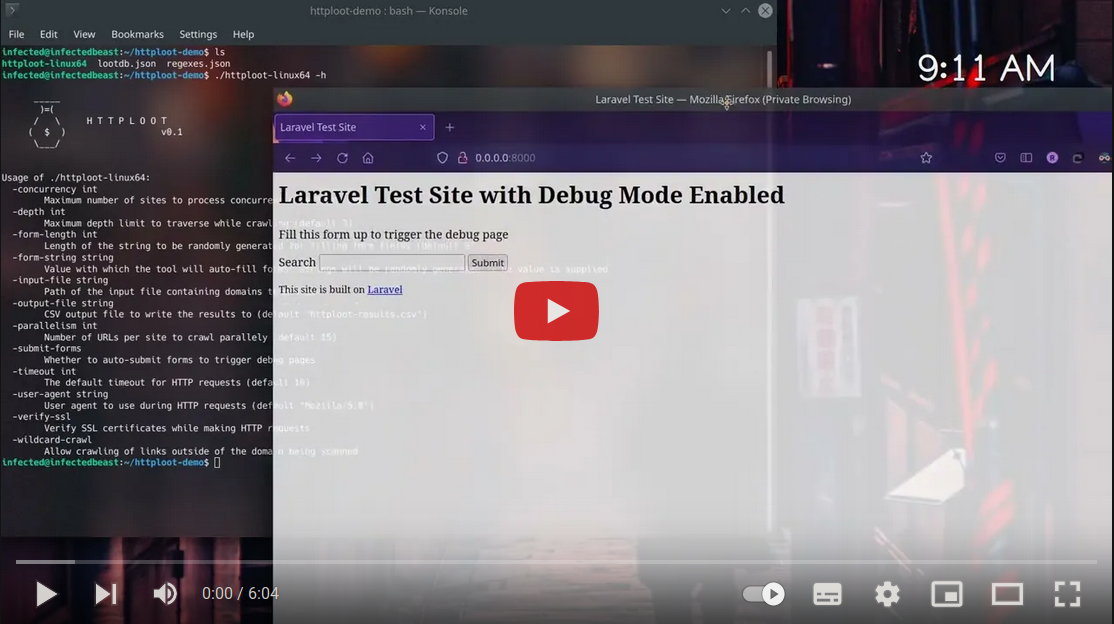 redhuntlabs/httploot
An automated tool which can simultaneously crawl, fill forms, trigger error/debug pages and "loot" secrets out of the client-facing code of sites.
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
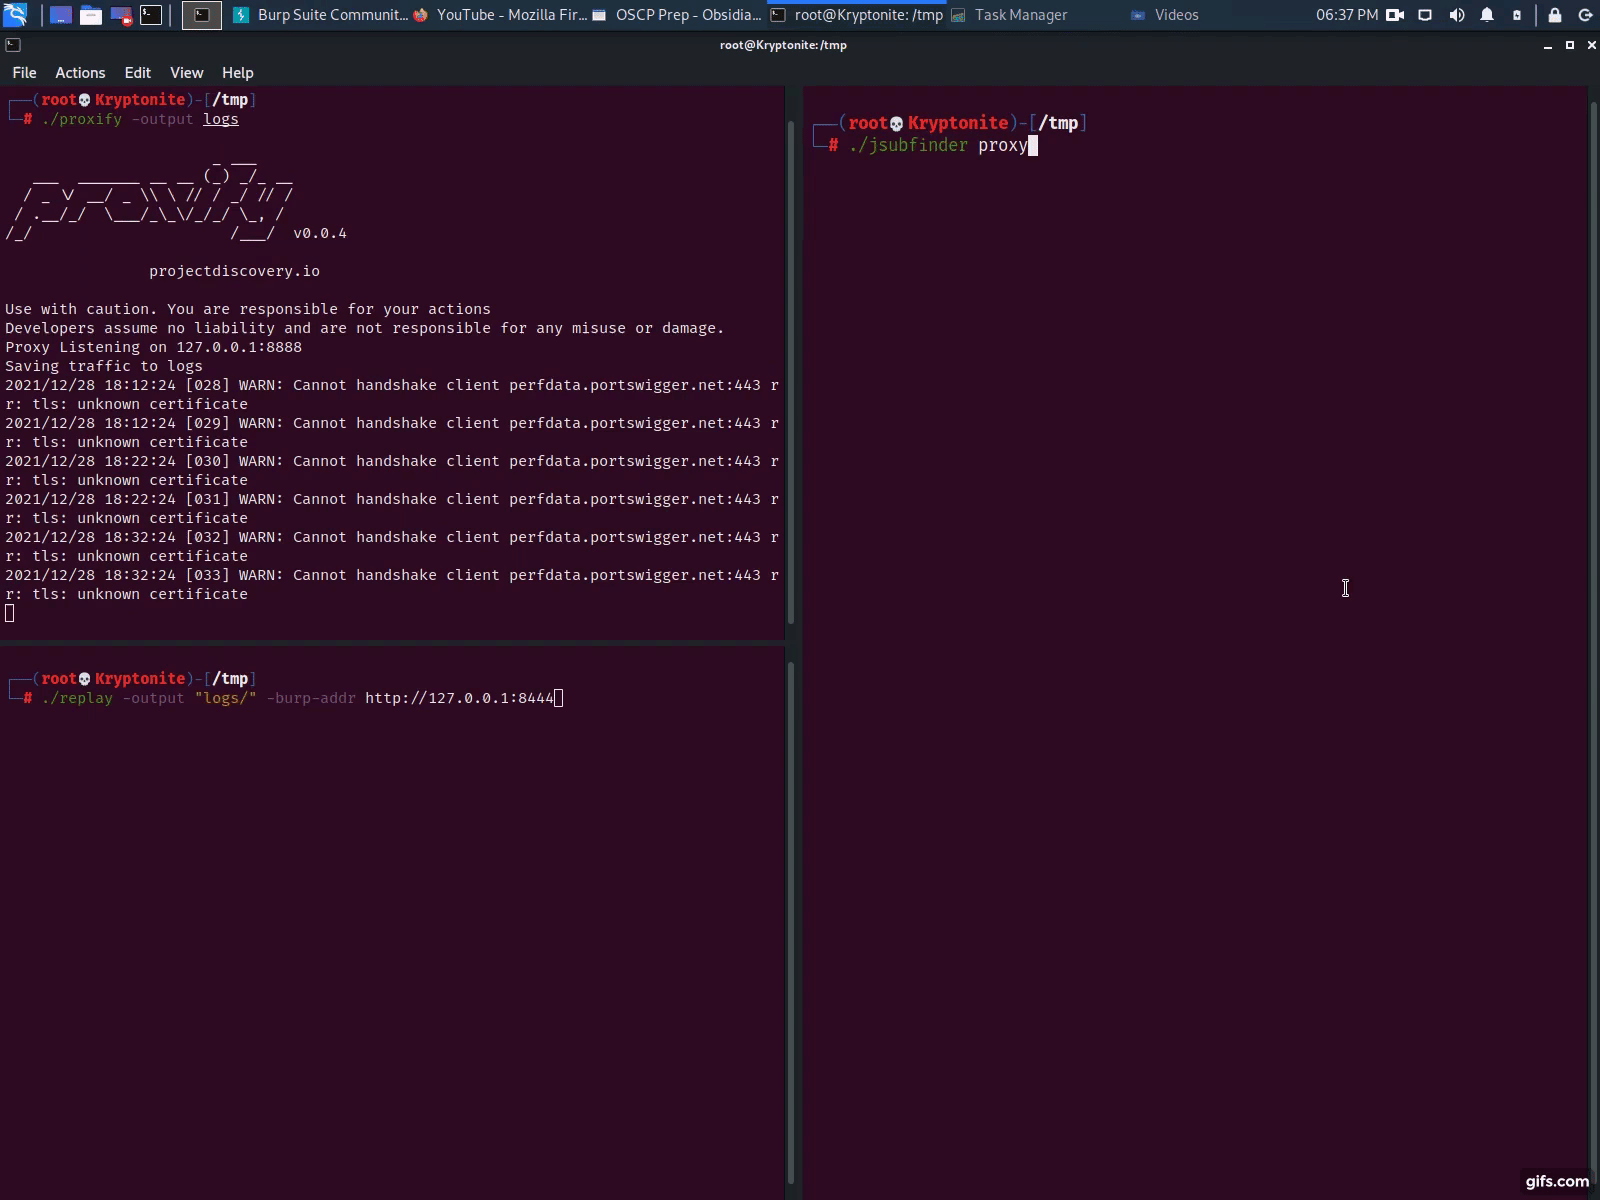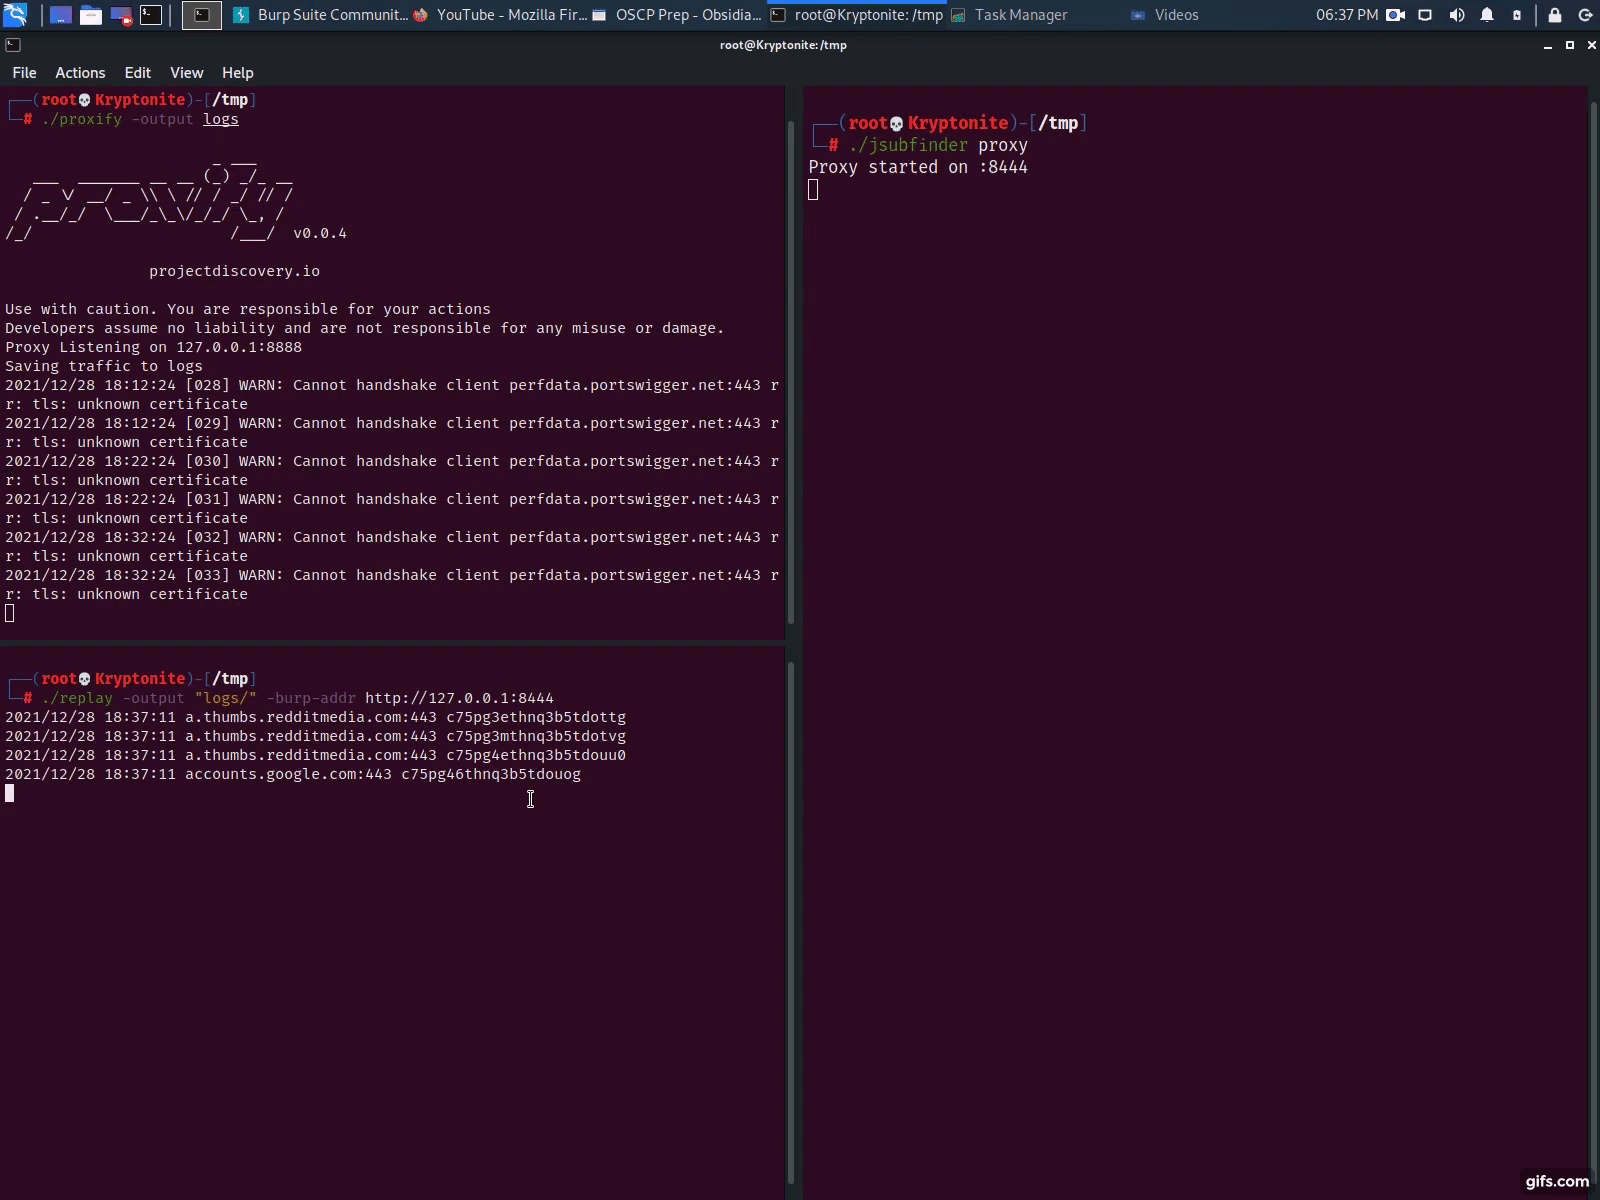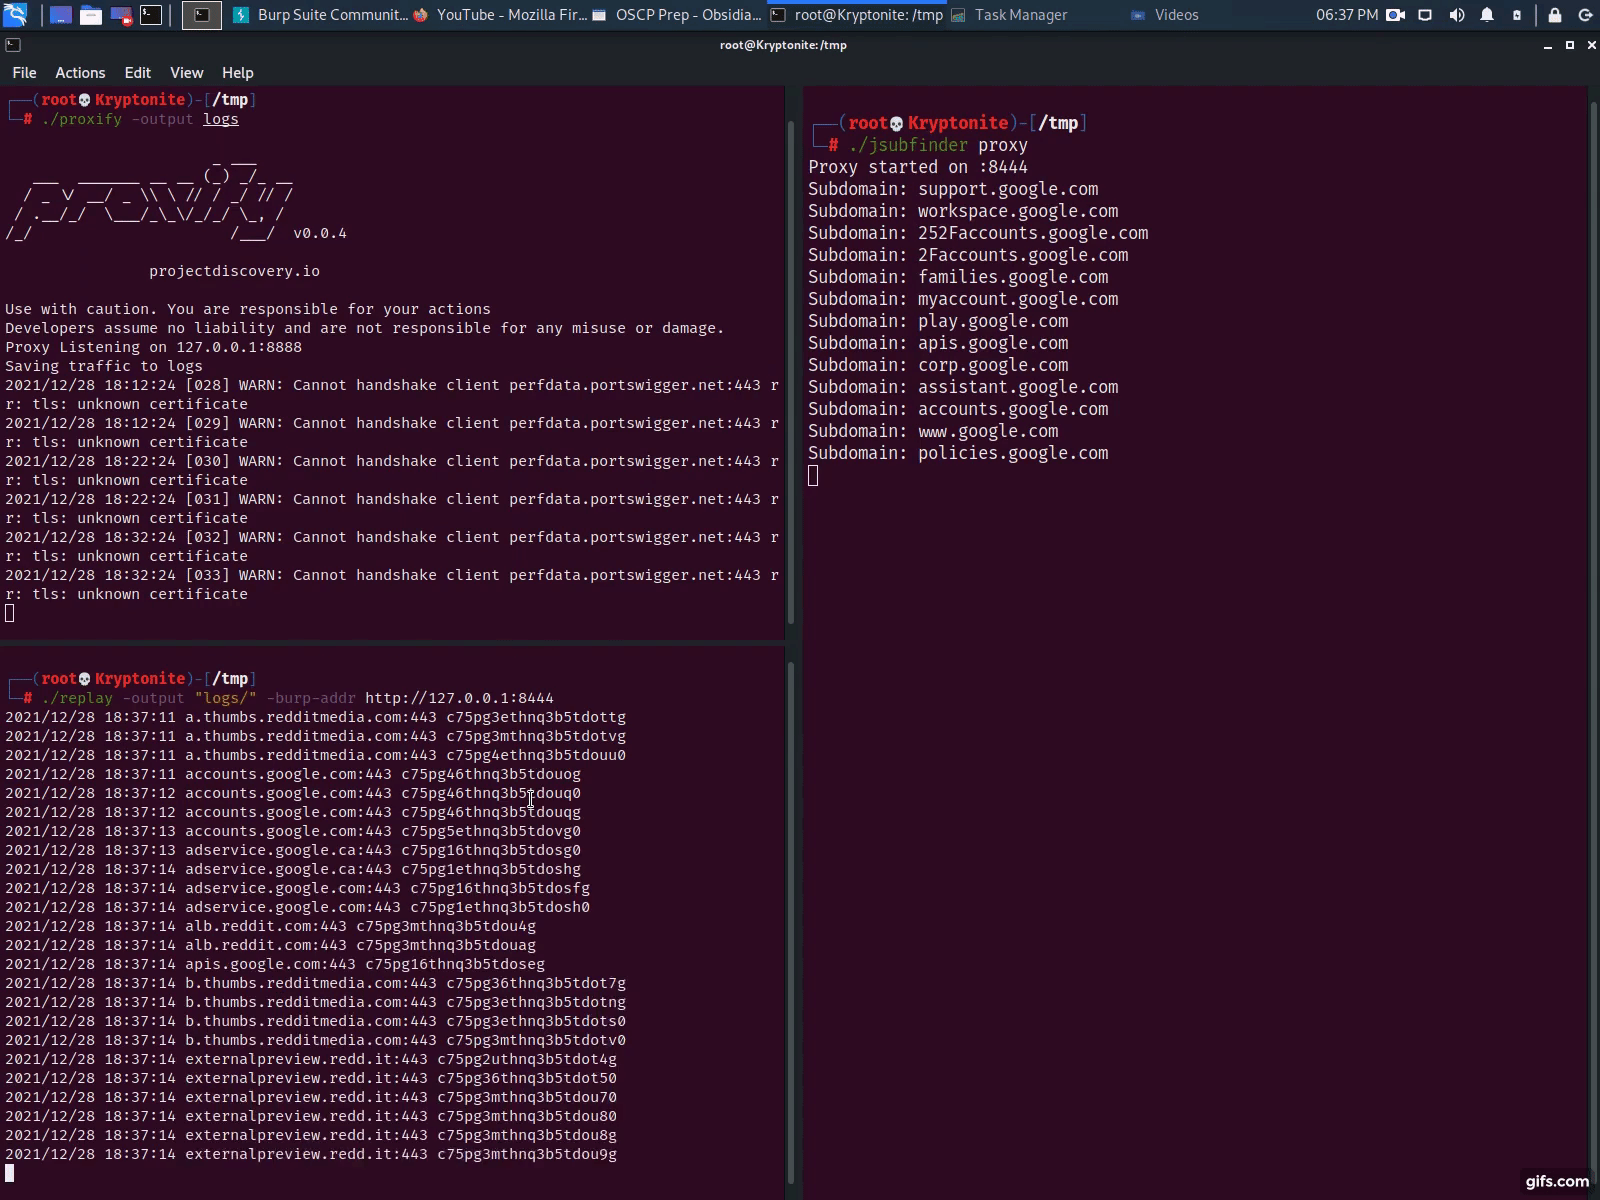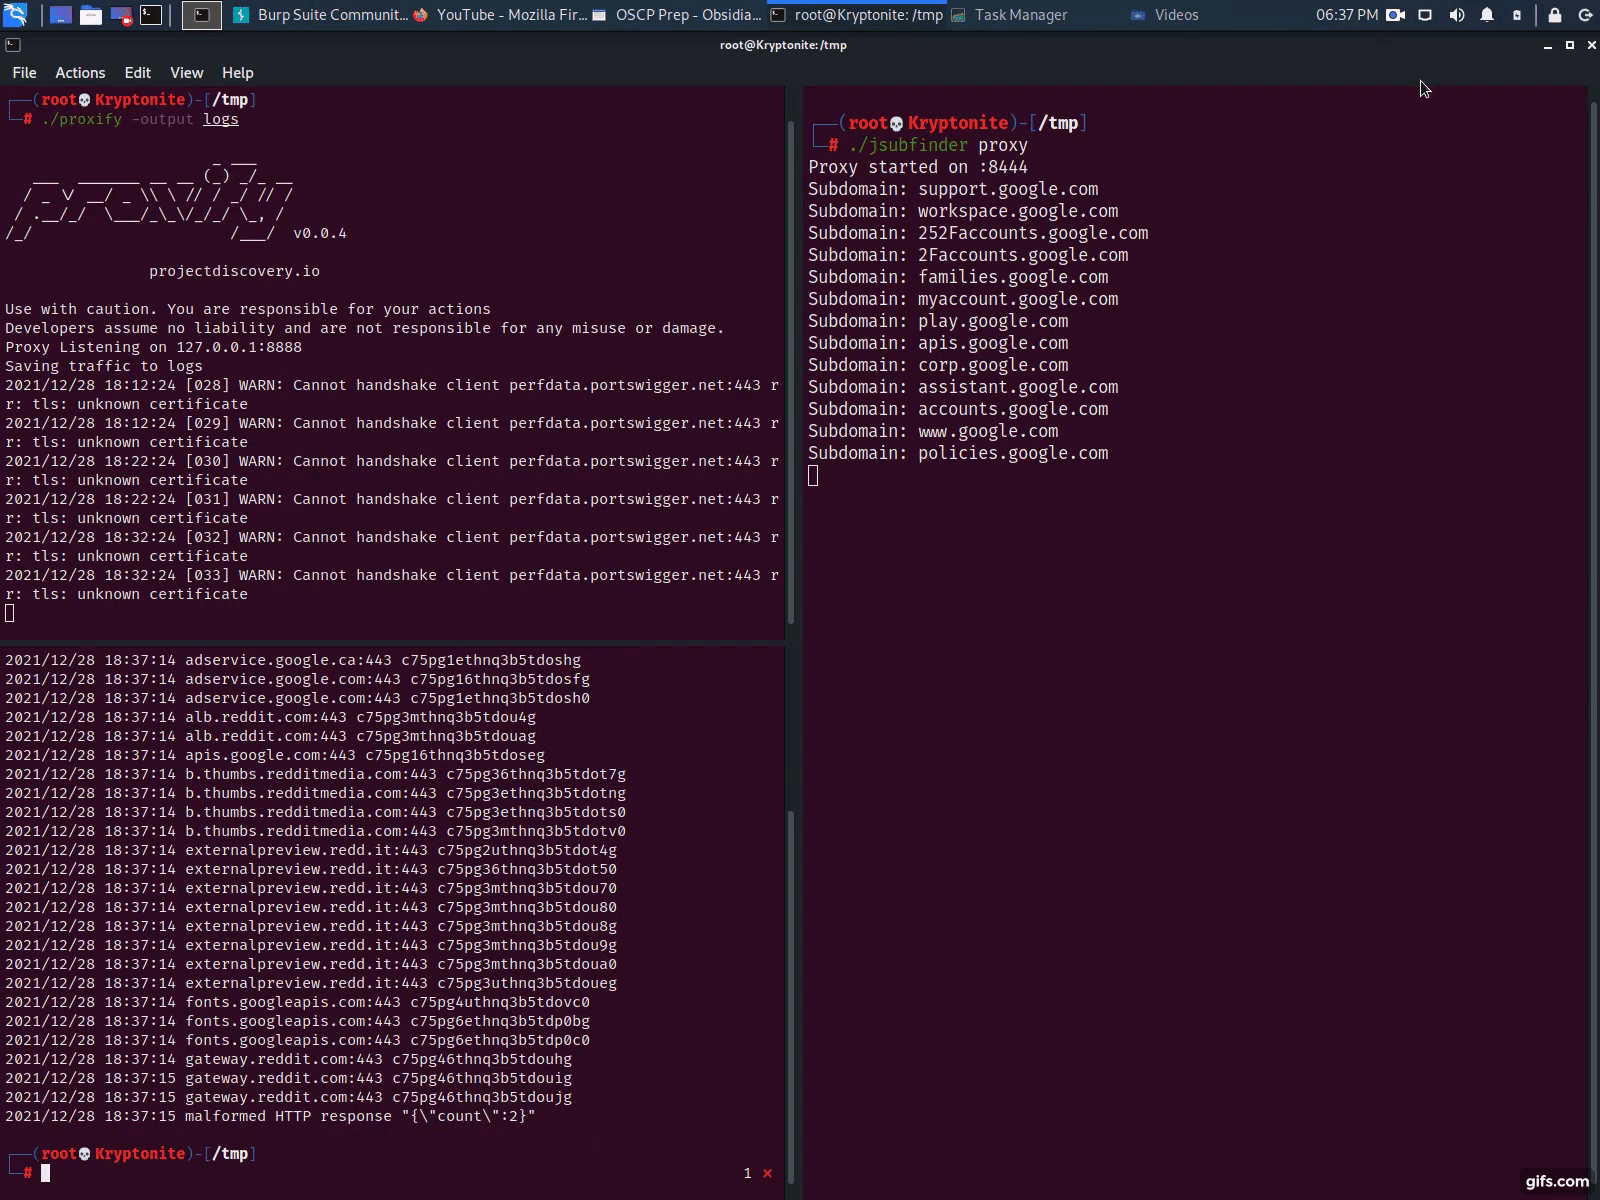 threatunknown/jsubfinder
Go-based tool that scans webpages and JavaScript files to discover hidden subdomains and secrets, with optional crawling and real-time proxy analysis…
 gitleaks/gitleaks
Fast, open-source static analysis tool for detecting hardcoded secrets like passwords, API keys, and tokens in git repositories, files, and stdin…
 brittonhayes/pillager
Pillage filesystems for sensitive information with Go 🔍
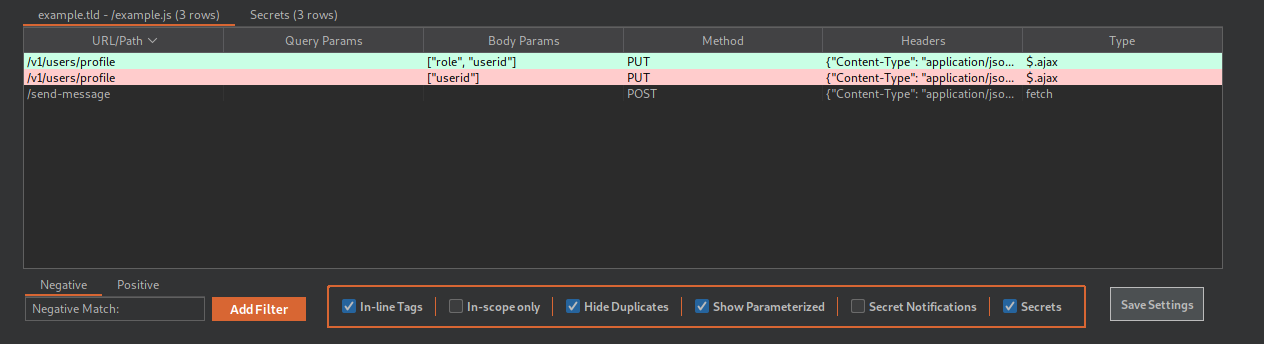 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 ewenquim/entropy
CLI tool that scans codebases for high-entropy lines to detect potential secrets, with customizable file extension and top-N filtering.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.