
CVE-2026-22038
 sivaadityacoder/cve-2026-22038
Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
code-analysiseducationlog-analysis+2
sivaadityacoder/cve-2026-22038Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
 simoesctt/ctt-heartbleed-temporal-resonance-memory-leak-exploit-heartbleed-cve-2014-0160
Heartbleed (CVE-2014-0160) was devastating because it leaked adjacent memory. CTT-Heartbleed goes further—it uses 33-layer temporal resonance to map,…
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
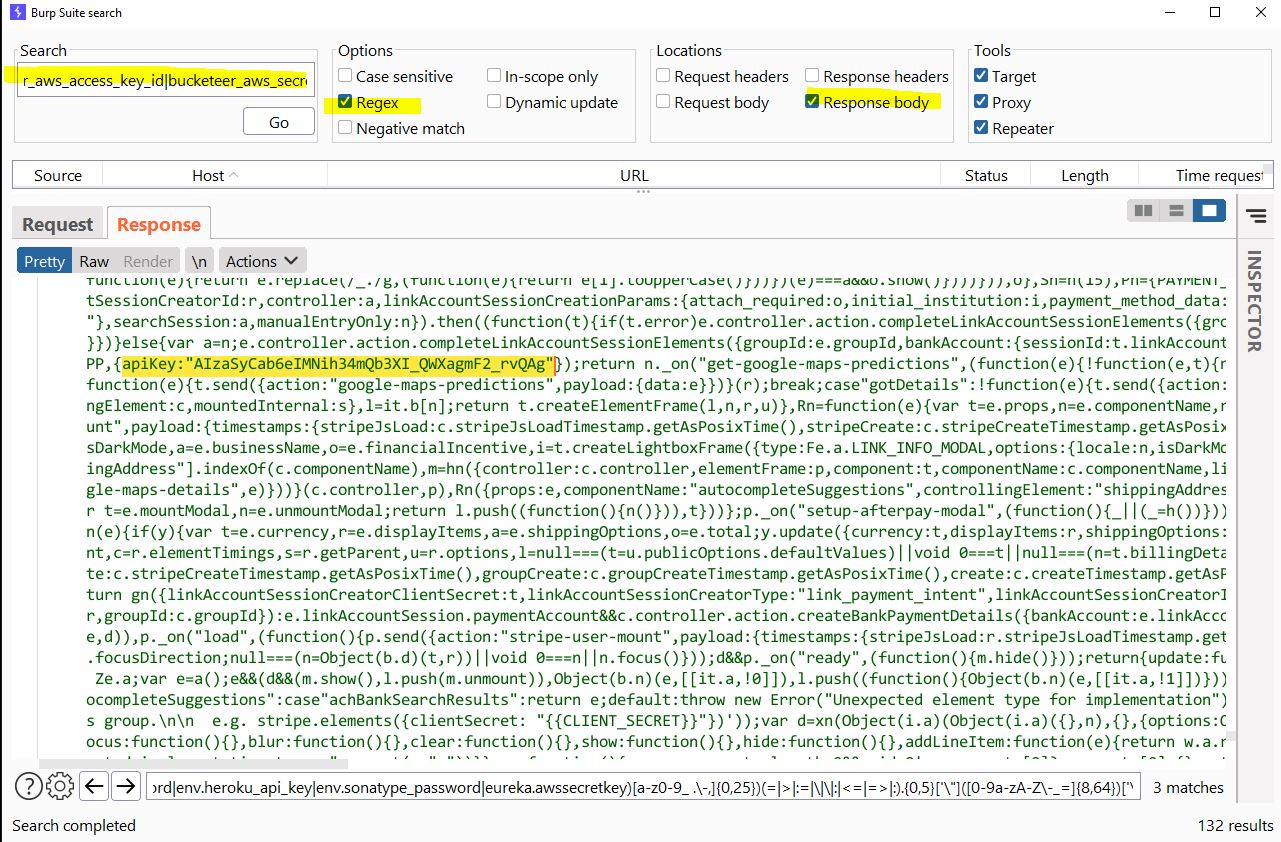 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
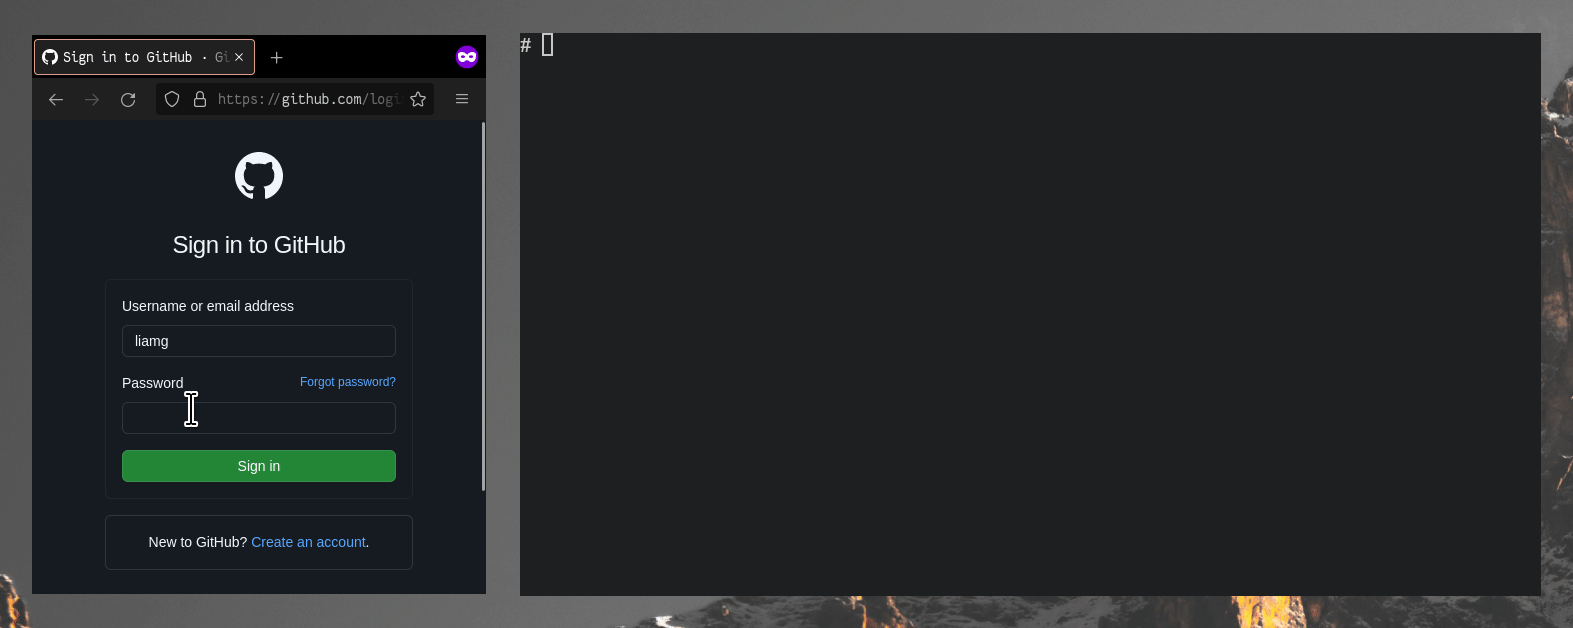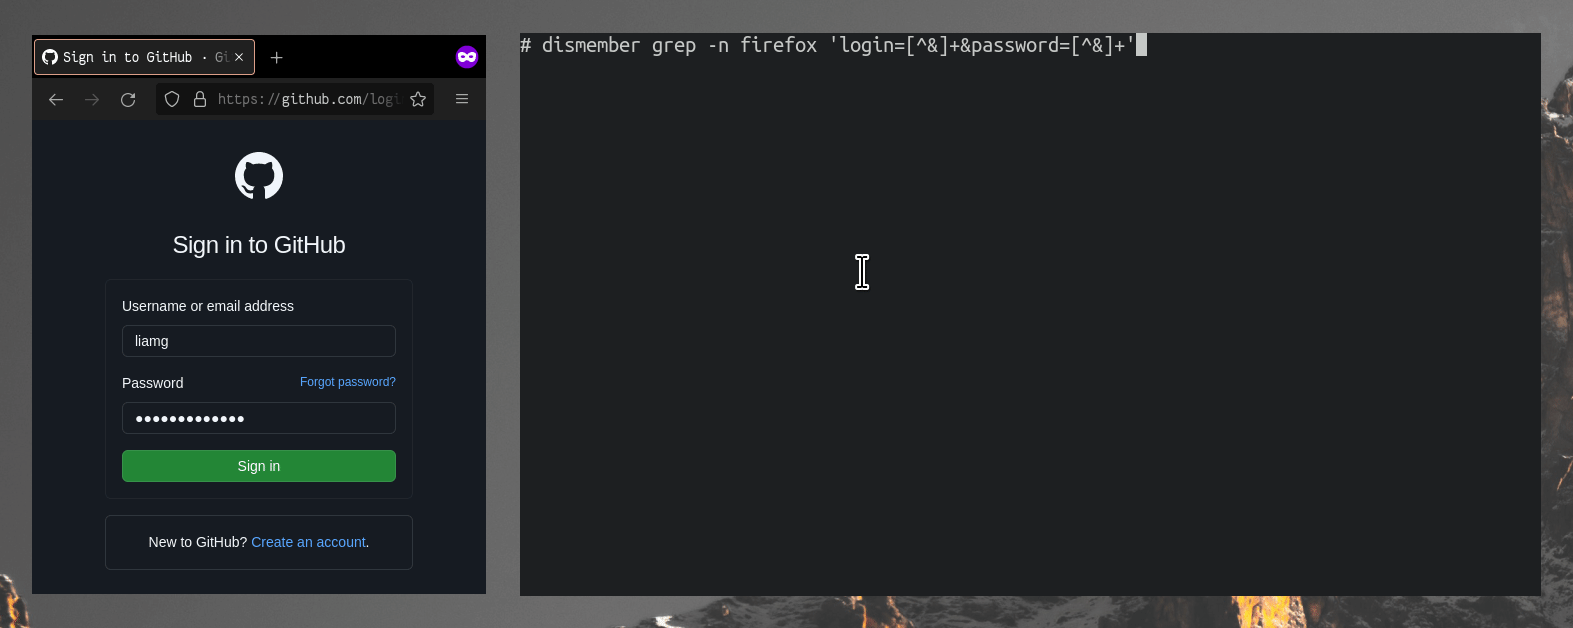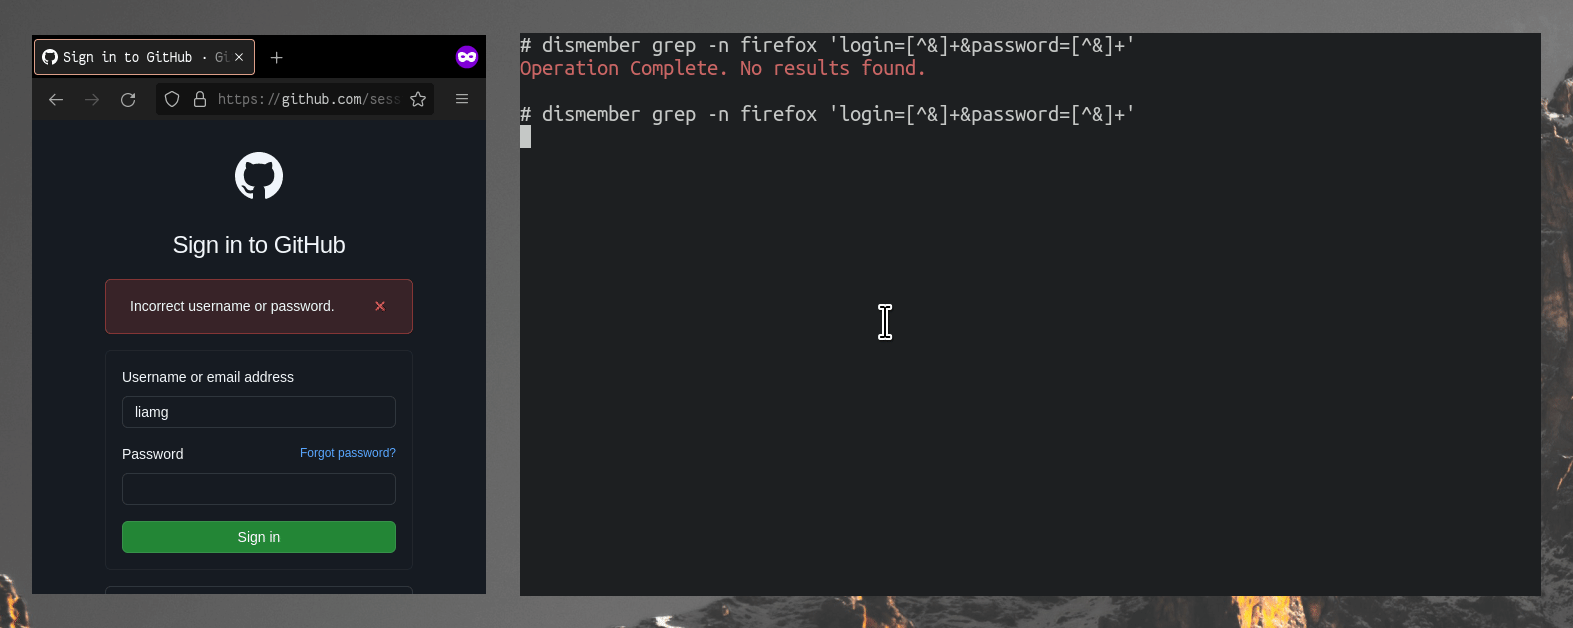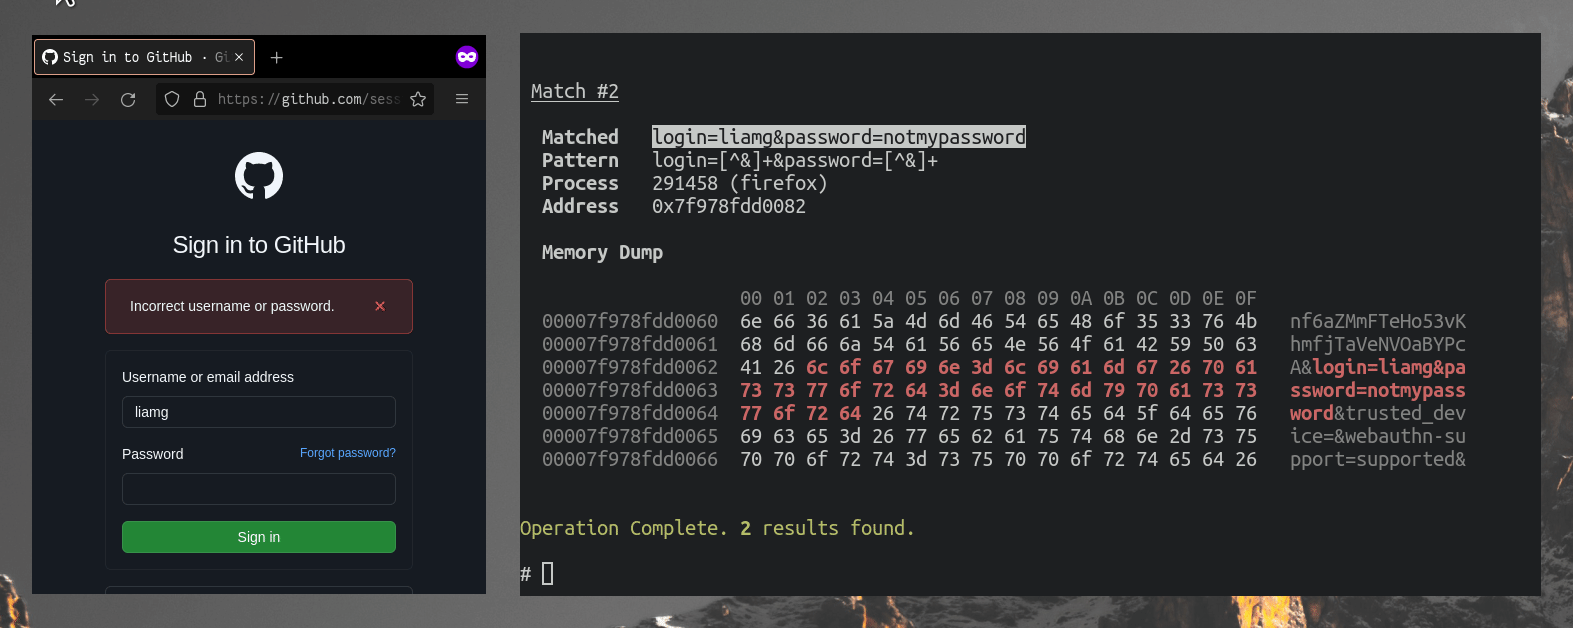 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 thewhiteh4t/llmreaper
Passive LLM Conversation Capture & Sensitive Data Exposure Research
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 randomrobbiebf/cve-2024-0368
Hustle Plugin <= 7.8.3 contains hardcoded HubSpot API credentials in inc/providers/hubspot/hustle-hubspot-api.php