
SnaffPoint
 nheiniger/snaffpoint
A tool for pointesters to find candies in SharePoint
cloud-securityinformation-gatheringpenetration-testing+3
nheiniger/snaffpointA tool for pointesters to find candies in SharePoint
 talkaboutcybersecurity/gitmonitor
One way to continuously monitor sensitive information that could be exposed on Github
 karim852/kumo-domain-recon-tool
Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…
 molly/gh-dork
Automated GitHub dorking tool that searches user, organization, and repository code for exposed secrets, credentials, and security misconfigurations…
 shubhamshubhankar/dumpthegit
Scans public GitHub repositories for accidentally uploaded sensitive data like credentials, secret keys, and tokens using a personal access token.
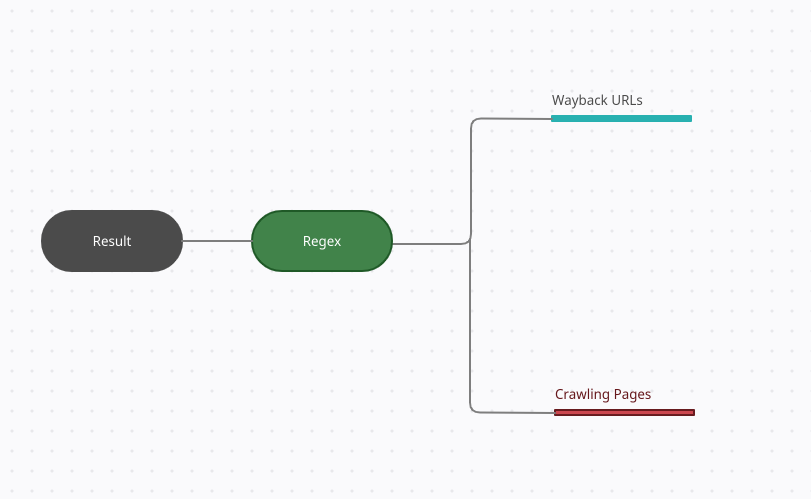 h33tlit/jbin-website-secret-scraper
Jbin will gather all the URLs from the website and then it will try to expose the secret data from them such as API keys, API secrets, API tokens and…
 zomato/vinifera
A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
 sebastian-mora/aws-loot
Enumerates AWS environments for secrets by scanning EC2 userdata, Lambda environment variables and source code, and CodeBuild instances for…
 liodeus/swaggerhole
A python3 script searching for secret on swaggerhub
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
 nightwatchcybersecurity/gitbleed_tools
Shell scripts to clone and mirror Git repositories, compute deltas, and run gitleaks to detect secrets hidden in deleted or reset commits.
 unkl4b/gitminer3
Tool for advanced mining for content on Github
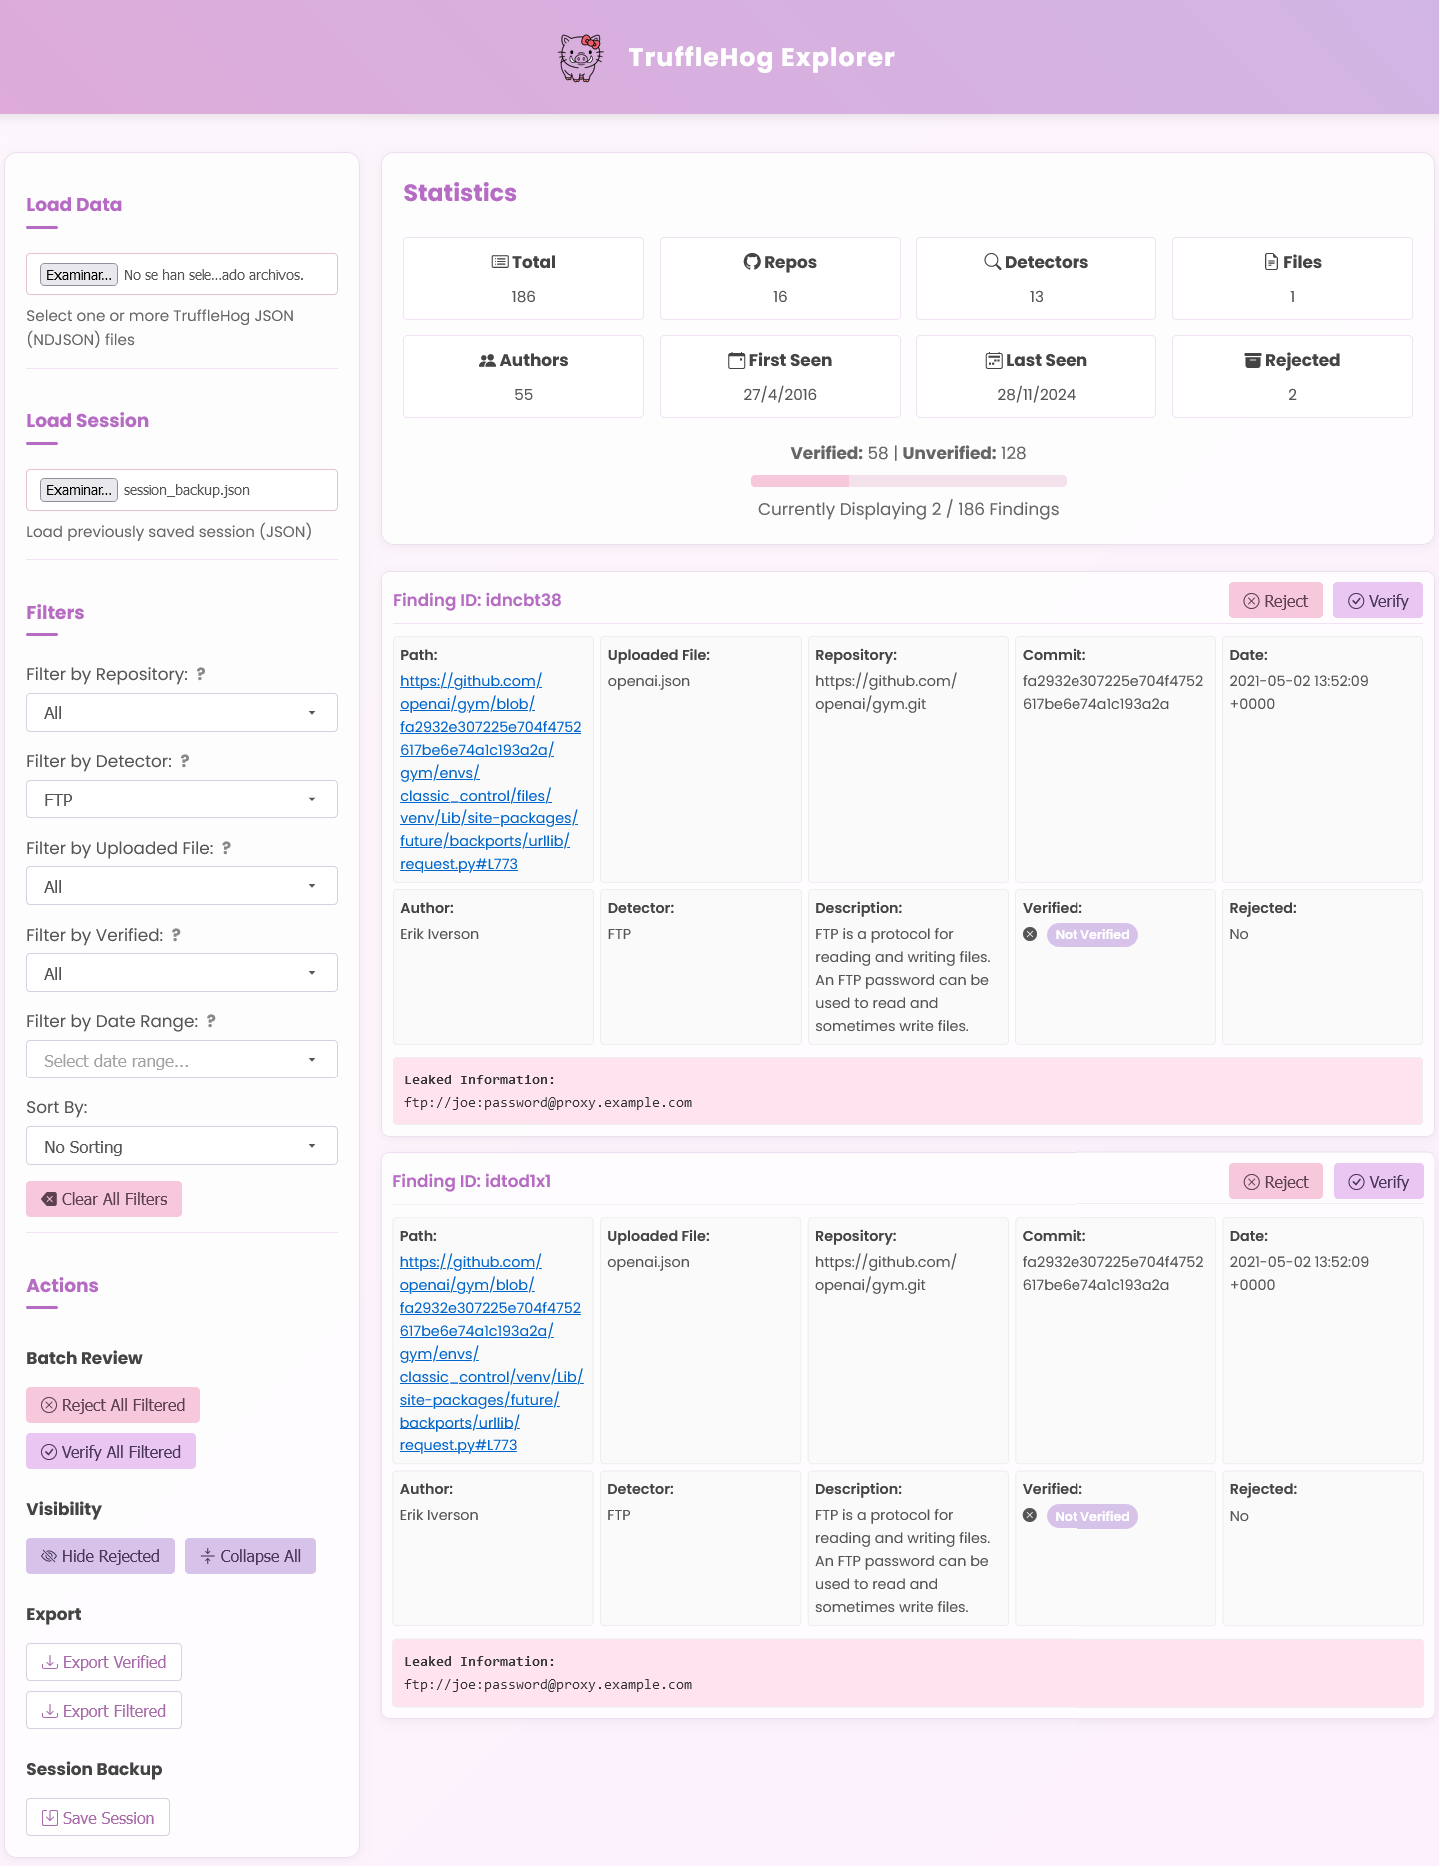 gonzosint/trufflehog-explorer
Web-based dashboard to visualize, filter, and analyze secrets discovered by TruffleHog, with batch verification, export, and session management for…
 josue87/givemesecrets
Use regular expressions to get sensitive information from a given repository (GitHub, pip or npm).
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent

 gitlab-com/gl-security/security-operations/redteam/redteam-public/tools/gitrob
This is a mirror of a forked repository. It adds several features to gitrob including GitLab support, commit content searching, in-memory repository…
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing