
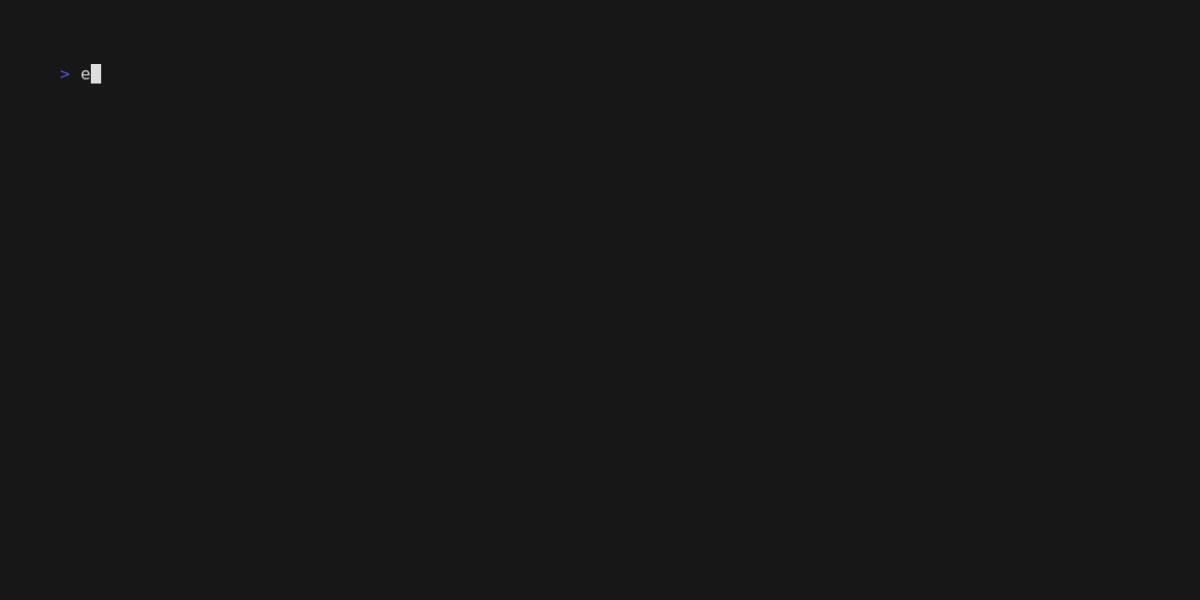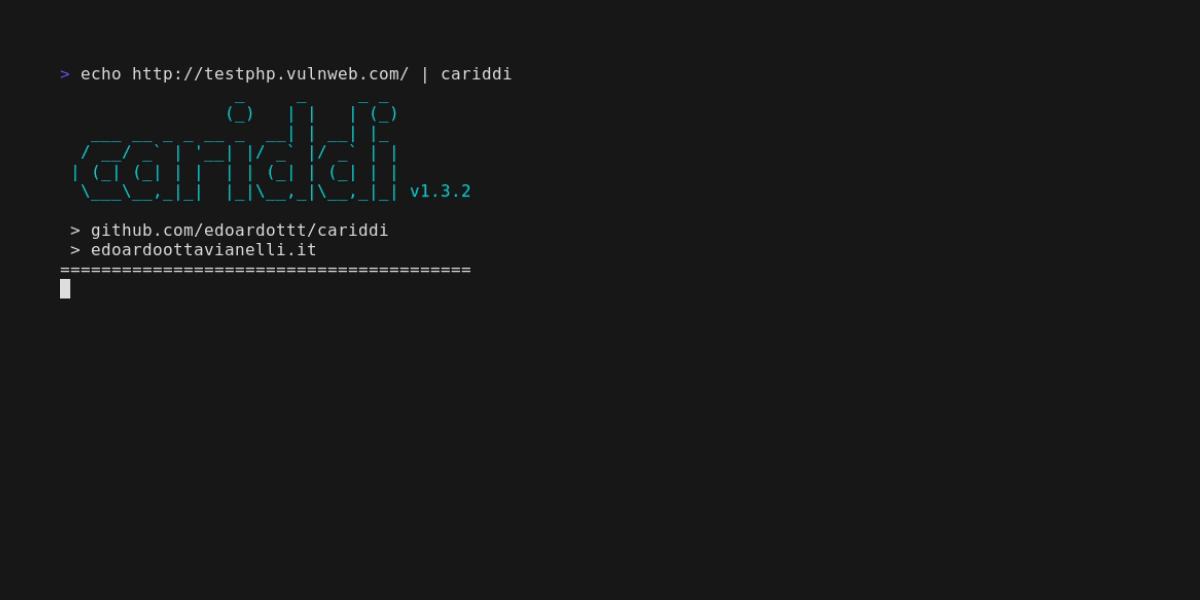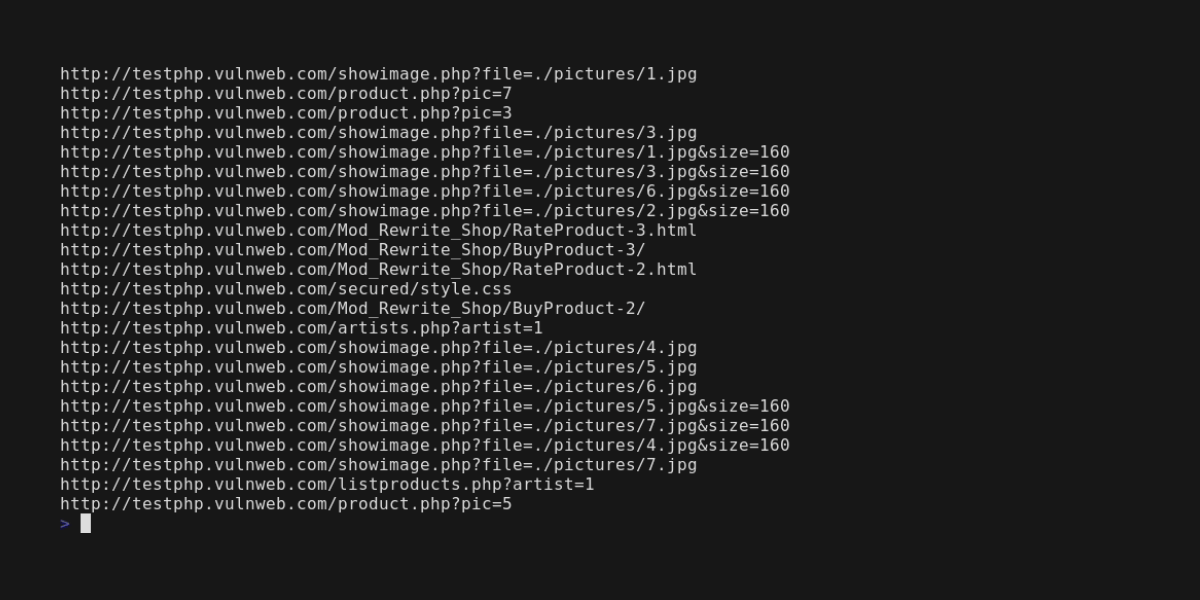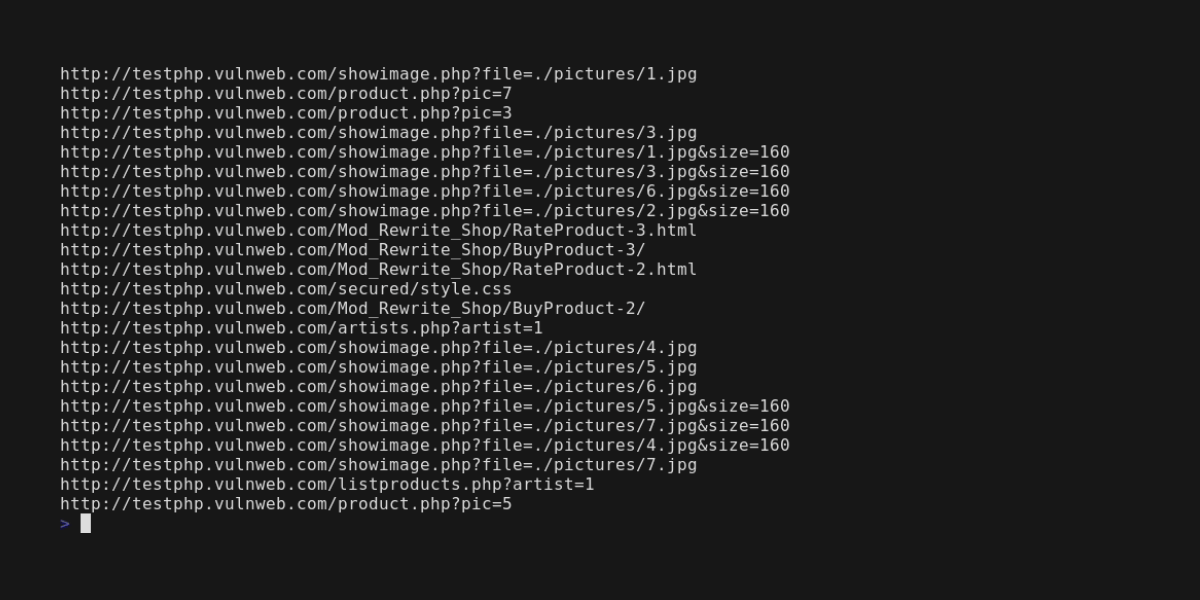
cariddi
 edoardottt/cariddi
Take a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
crawlerinformation-gatheringosint+4
edoardottt/cariddiTake a list of domains, crawl urls and scan for endpoints, secrets, api keys, file extensions, tokens and more
 techgaun/github-dorks
Find leaked secrets via github search
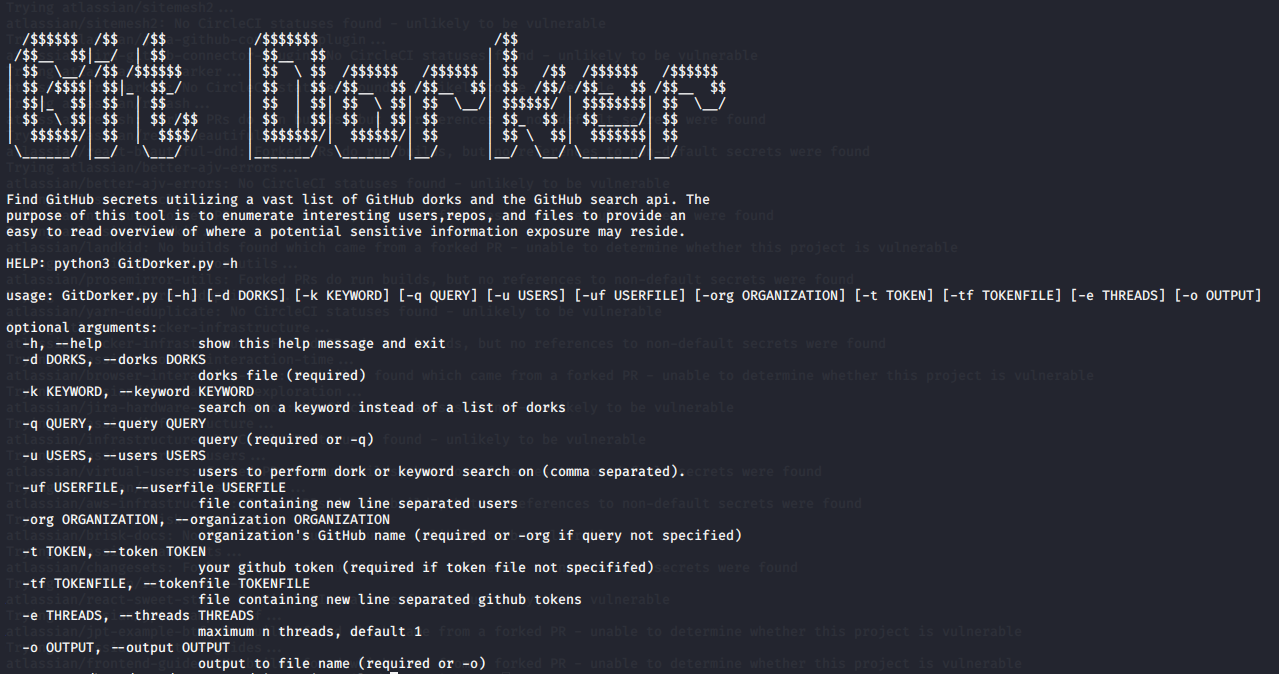 obheda12/gitdorker
A Python program to scrape secrets from GitHub through usage of a large repository of dorks.
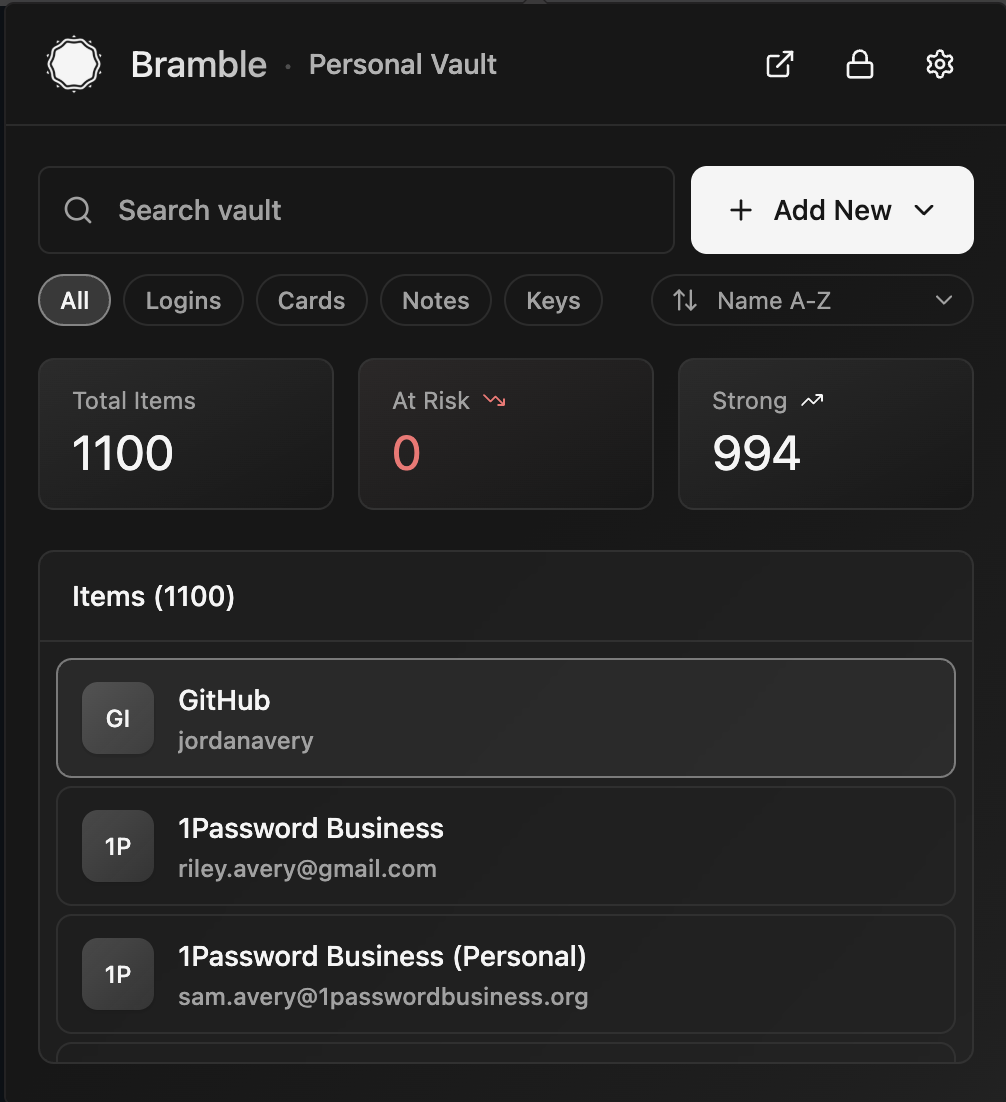 flythenimbus/bramble
Local-first password manager with direct device-to-device sync
 newrelic/rusty-hog
Multi-source secret scanner detecting API keys, passwords, and PII across Git repos, S3 buckets, filesystems, Confluence, JIRA, Slack, and Google…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 undeadsec/swaggerspy
Automated OSINT tool that scans SwaggerHub API documentation to discover exposed secrets, credentials, and sensitive information using regex-based…
 arnica/depsguard
Harden your package manager configs against supply chain attacks.
 santhreal/keyhog
Open-source secret scanner in Rust
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…

 gitlab-com/gl-security/security-operations/redteam/redteam-public/tools/gitrob
This is a mirror of a forked repository. It adds several features to gitrob including GitLab support, commit content searching, in-memory repository…
 anee769/conduit
On-prem API gateway for AI coding agents with per-engineer cost attribution, hard budgets, egress governance (secrets/entity scanning), context-rot…
 mhaggis/package-inferno
A Public Package Scanner for The Community
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 appomni-labs/heisenberg-ssc-gha
GitHub Action for Heisenberg SSC
 caixa-git/tanstack-shield
🛡️ One-command scanner for CVE-2026-45321 — TanStack npm supply-chain attack