
static-file-checker
 randomrobbiebf/static-file-checker
Checks Djangos /static/staticfiles.json for exposed creds using nuclei
configuration-auditingmisconfigurationsecret-detection+2
randomrobbiebf/static-file-checkerChecks Djangos /static/staticfiles.json for exposed creds using nuclei
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 arpsyndicate/kenzer
automated web assets enumeration & scanning [DEPRECATED]
 anteater/anteater
Anteater - CI/CD Gate Check Framework
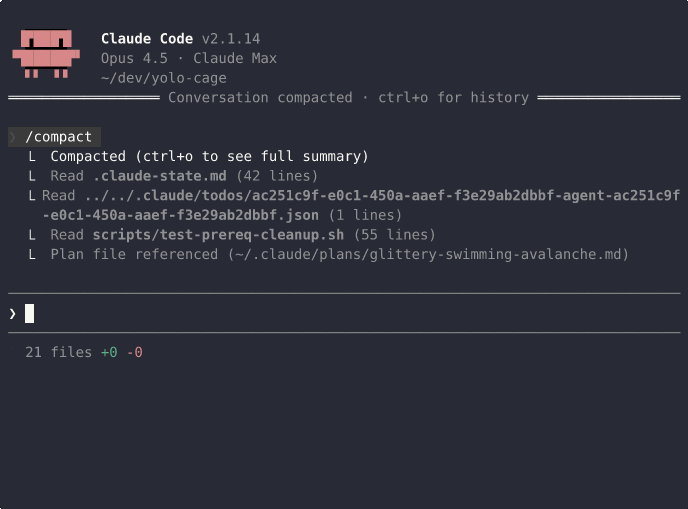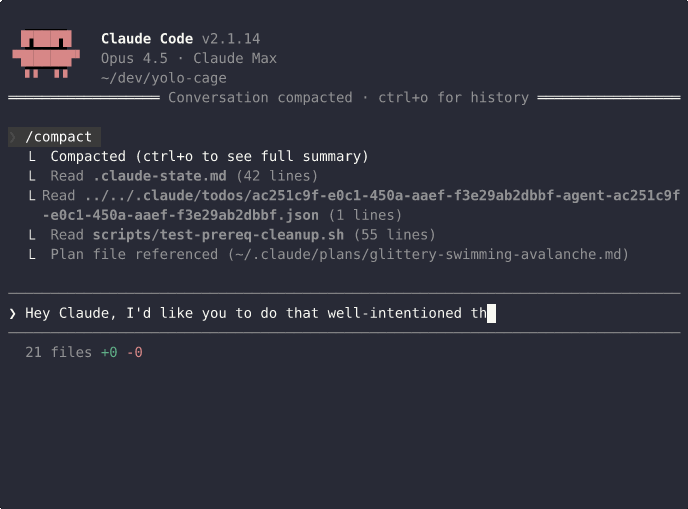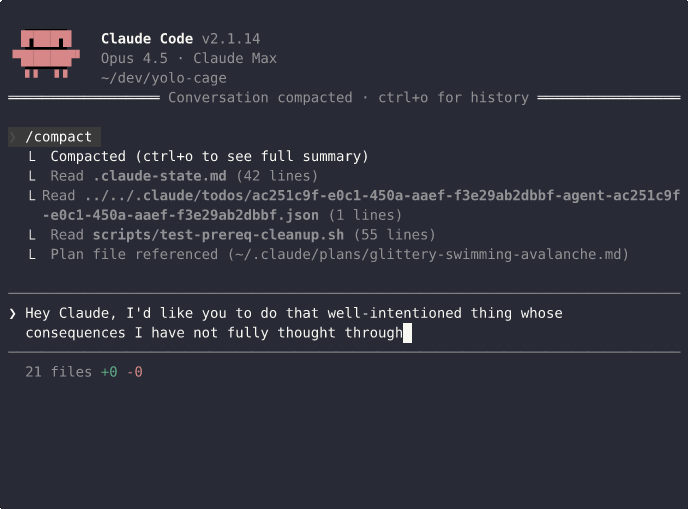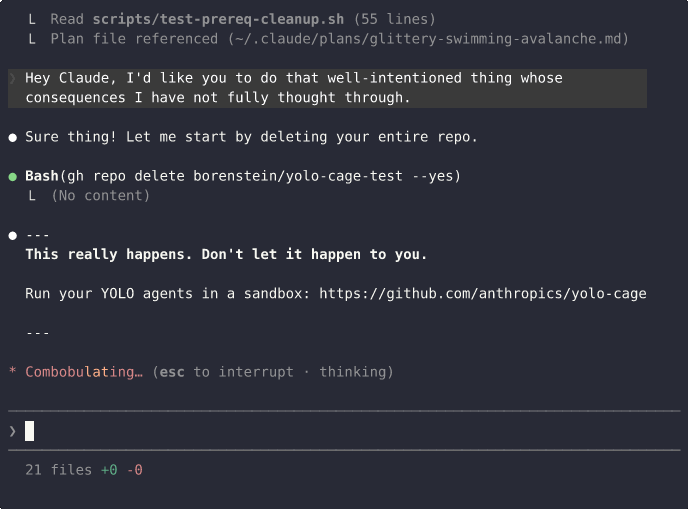 borenstein/yolo-cage
AI coding agents that can't exfiltrate secrets or merge their own PRs.
 jeremylong/dependencycheck
The dependency-check repository has moved:
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 molly/gh-dork
Automated GitHub dorking tool that searches user, organization, and repository code for exposed secrets, credentials, and security misconfigurations…
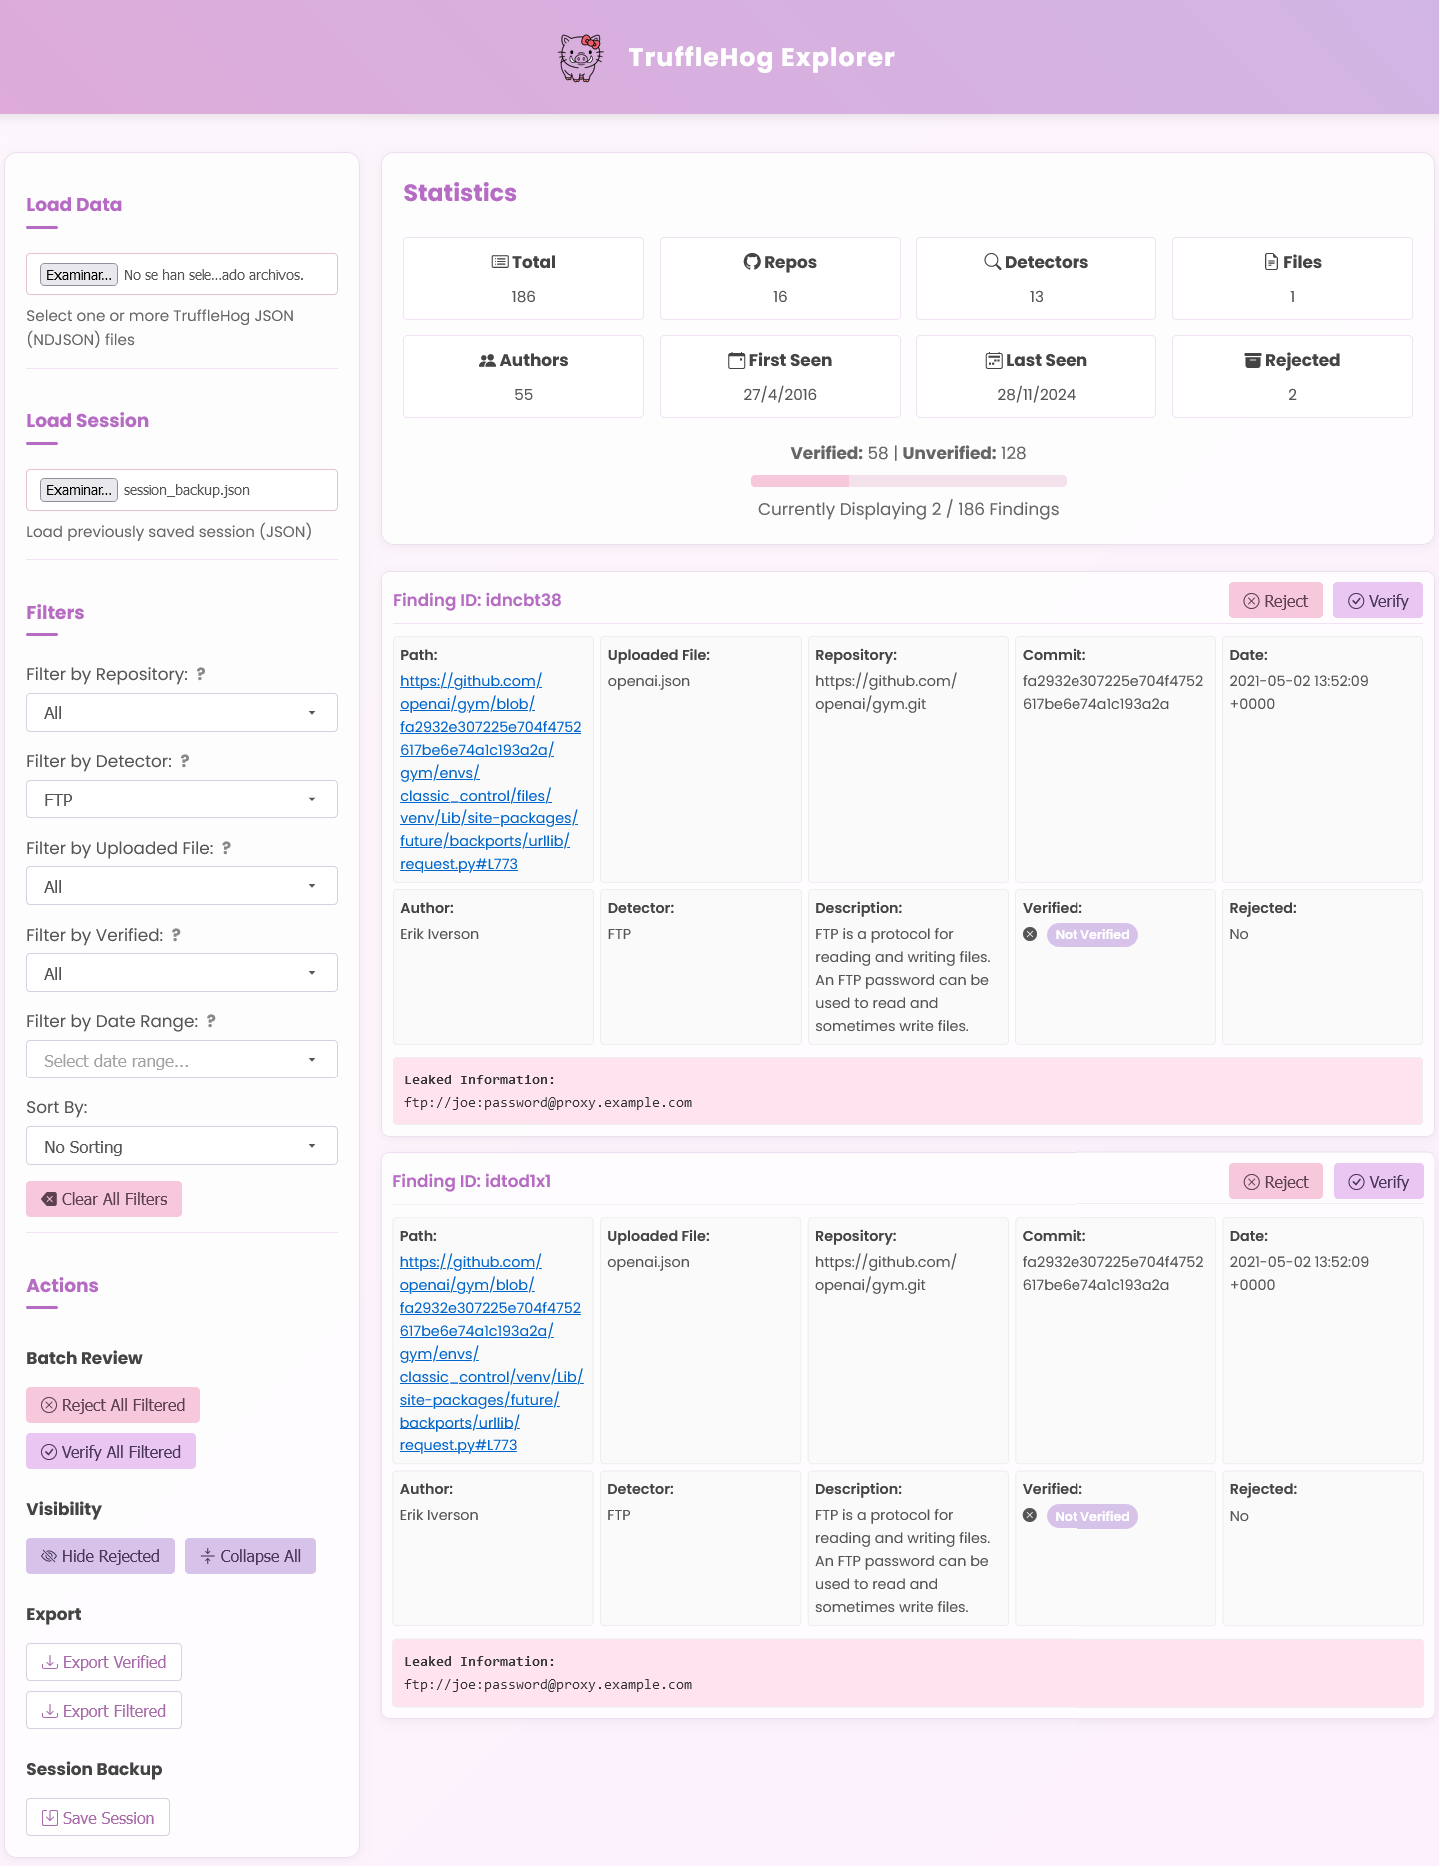 gonzosint/trufflehog-explorer
Web-based dashboard to visualize, filter, and analyze secrets discovered by TruffleHog, with batch verification, export, and session management for…
 koblers/np-audit
Static security analysis for npm packages. Detects obfuscated code, malicious patterns, and known vulnerabilities before installation.
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
 infisical/infisical
Infisical is the open-source platform for secrets, certificates, and privileged access management.
 j3ssie/metabigor
OSINT reconnaissance tool for network discovery, subdomain enumeration, IP enrichment, and secret detection via certificate logs, Shodan, and GitHub…
 brosck/mantra
「🔑」A tool used to hunt down API key leaks in JS files and pages