
 manuelschipper/nah
a guard that blocks catastrophic agent actions
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
 pigyon/mcpwner
Model Context Protocol server for autonomous vulnerability discovery
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
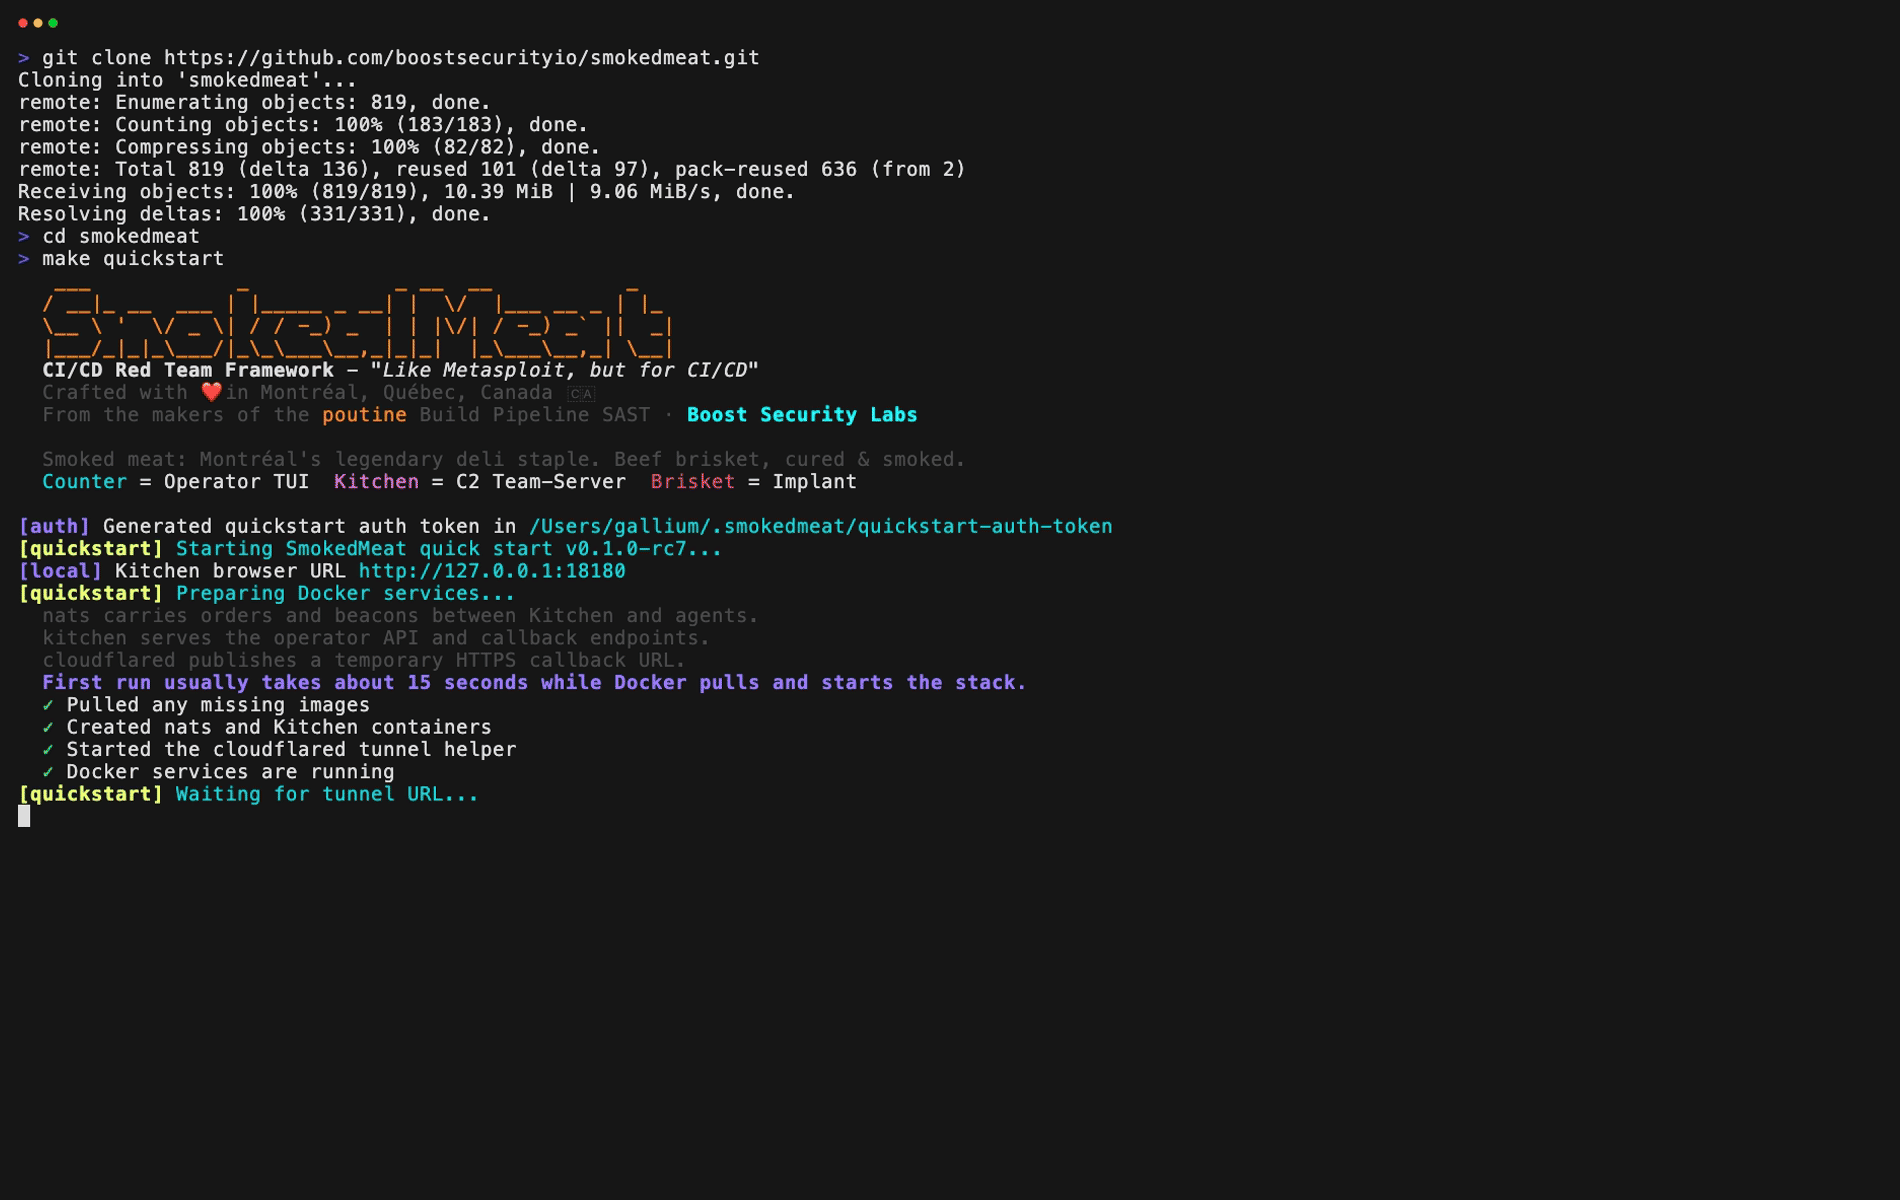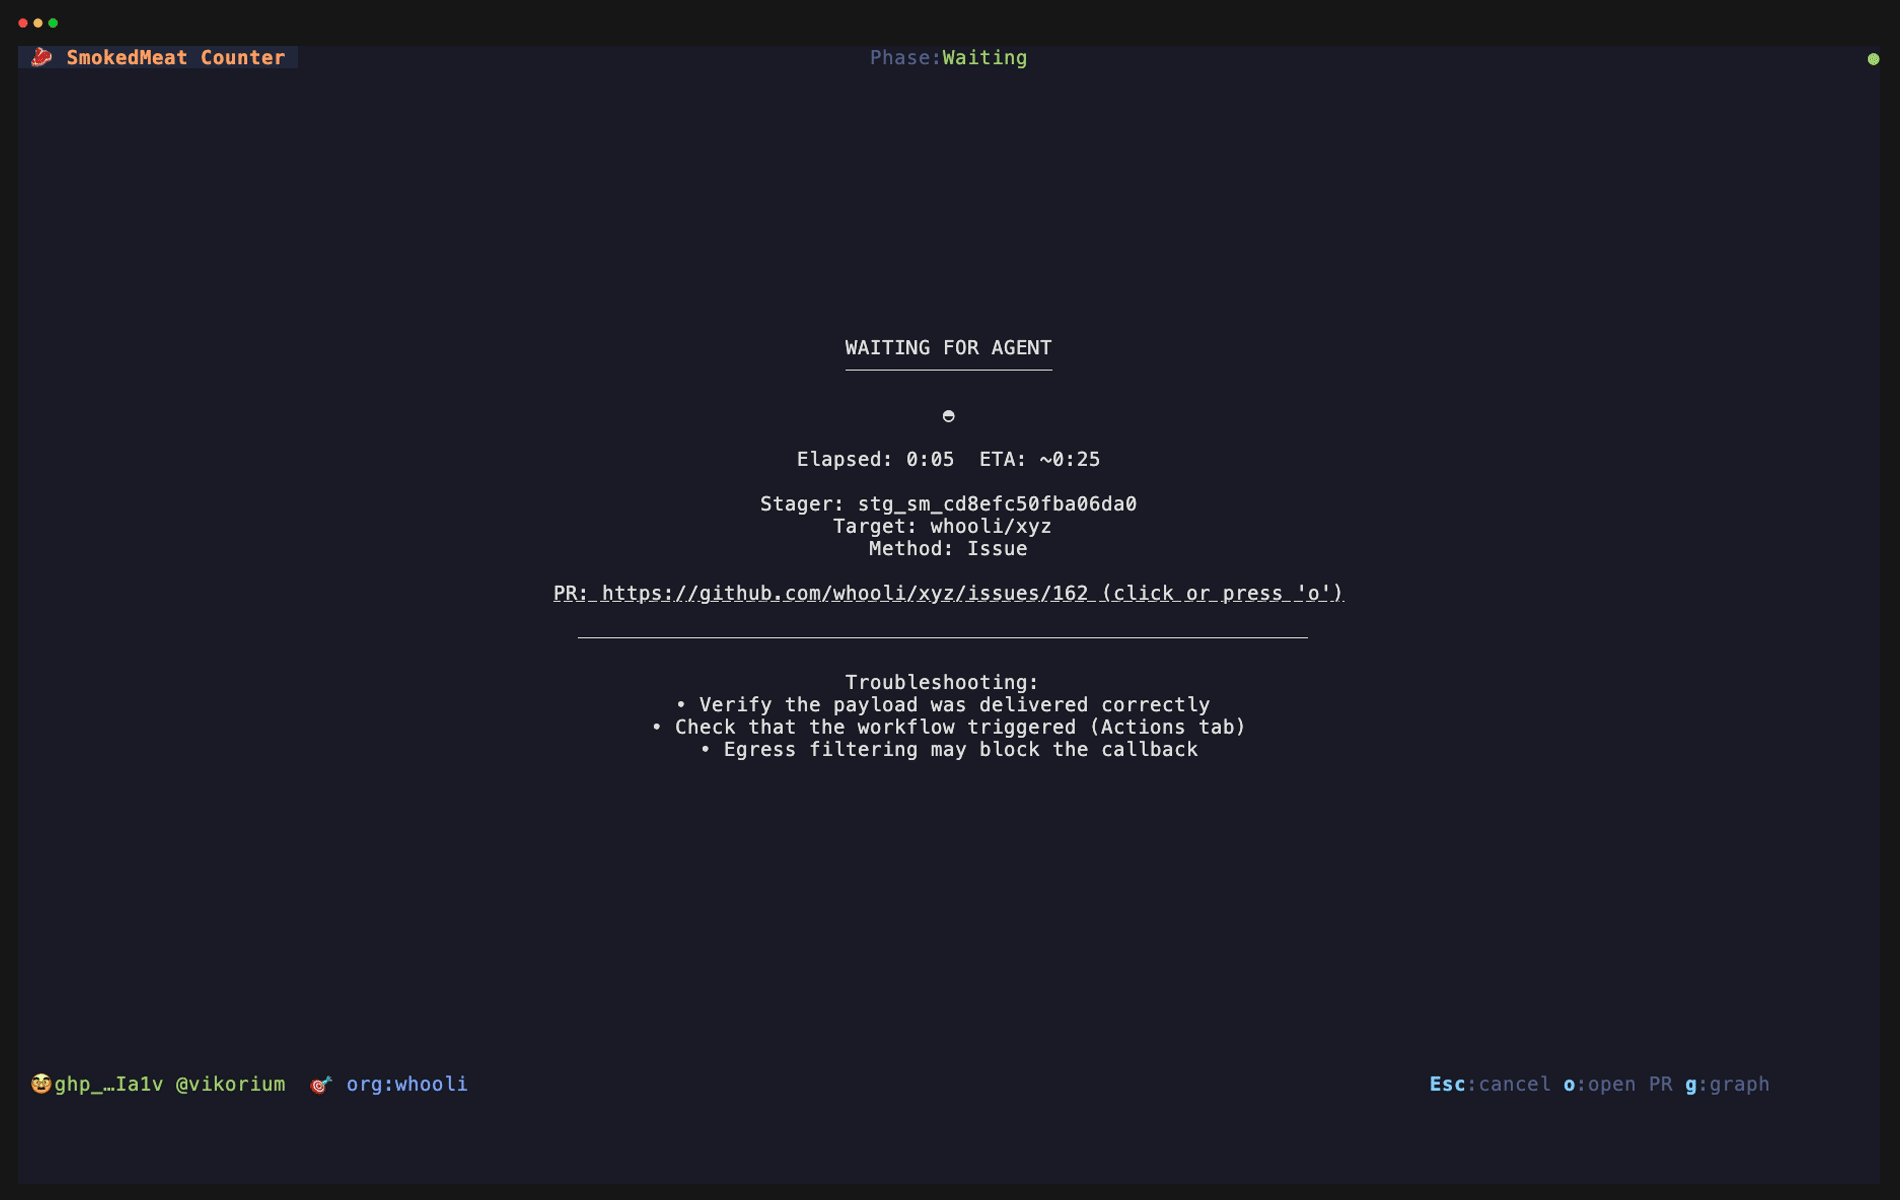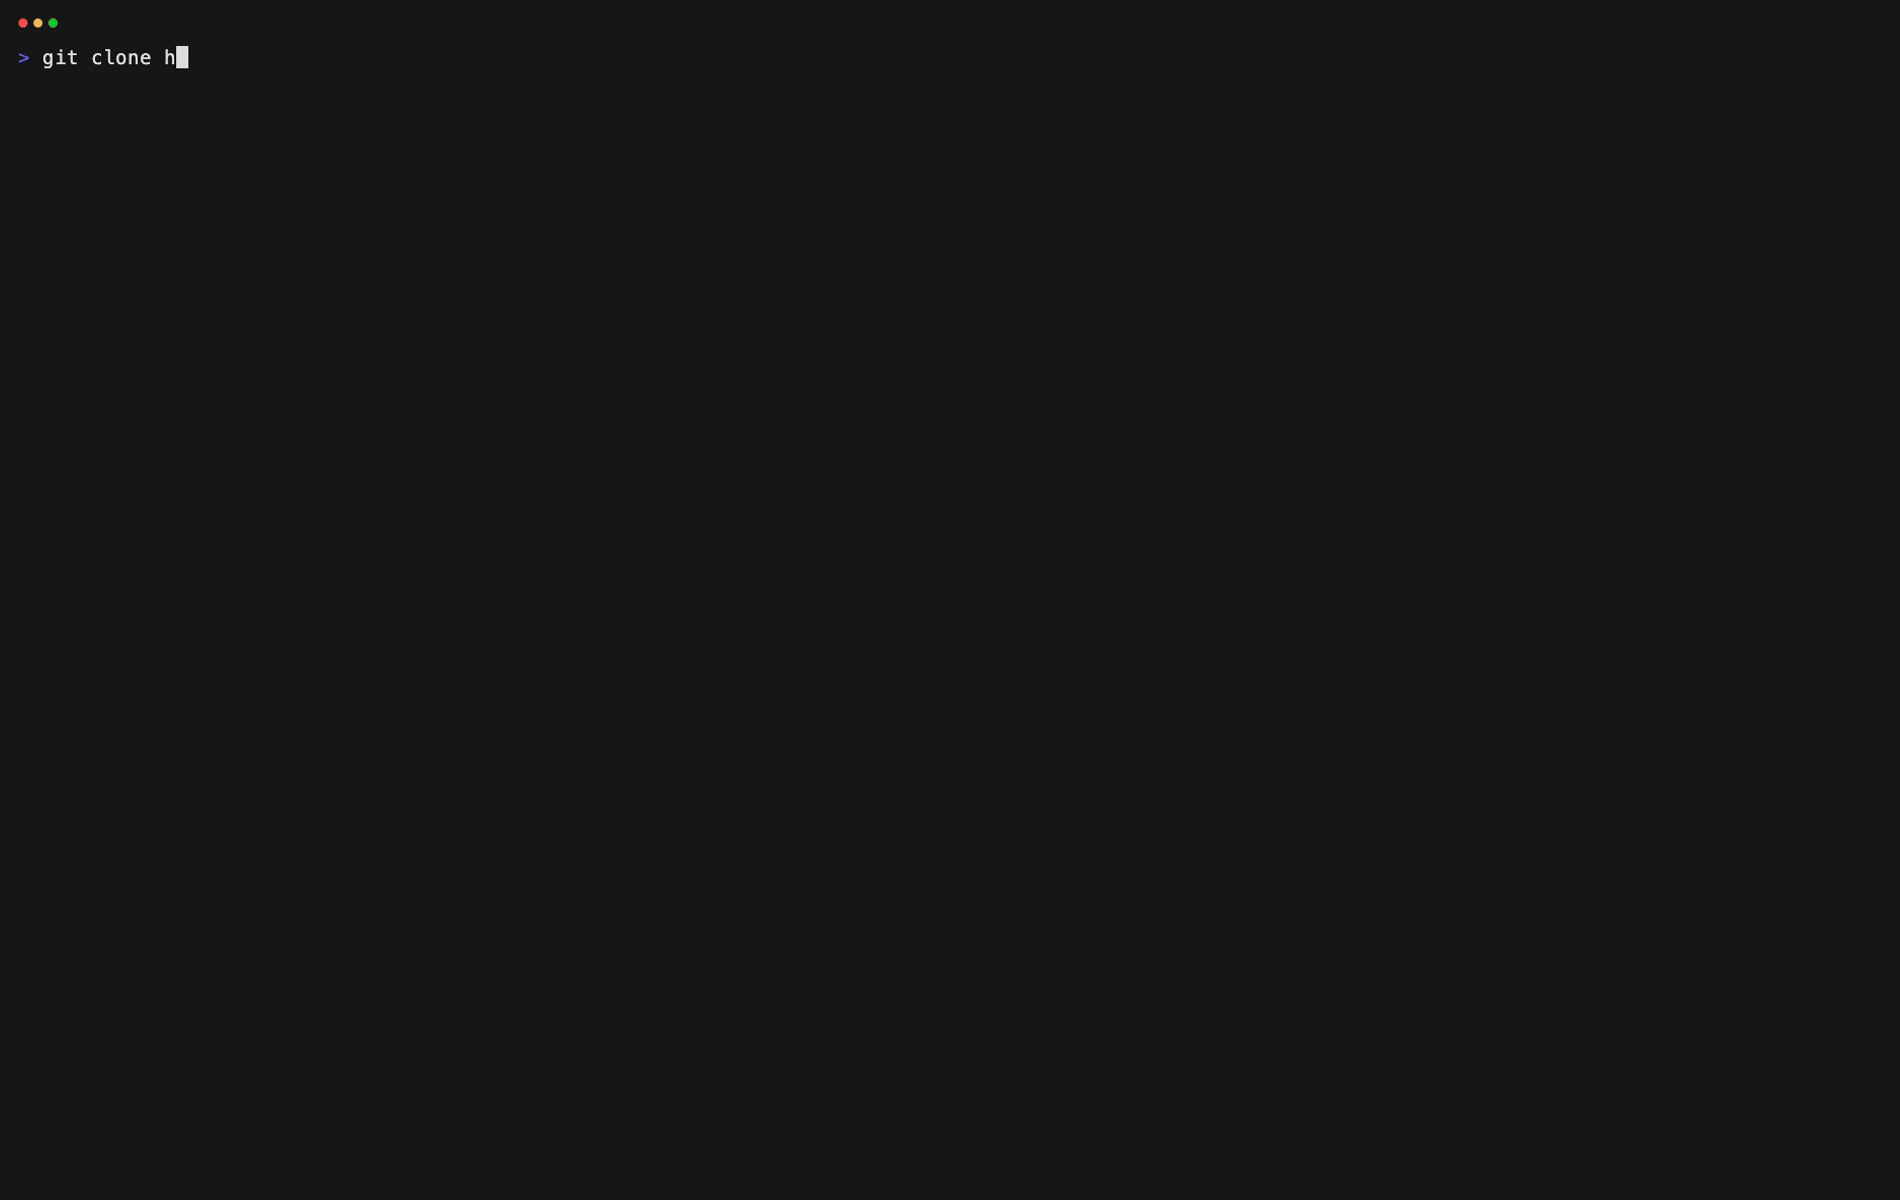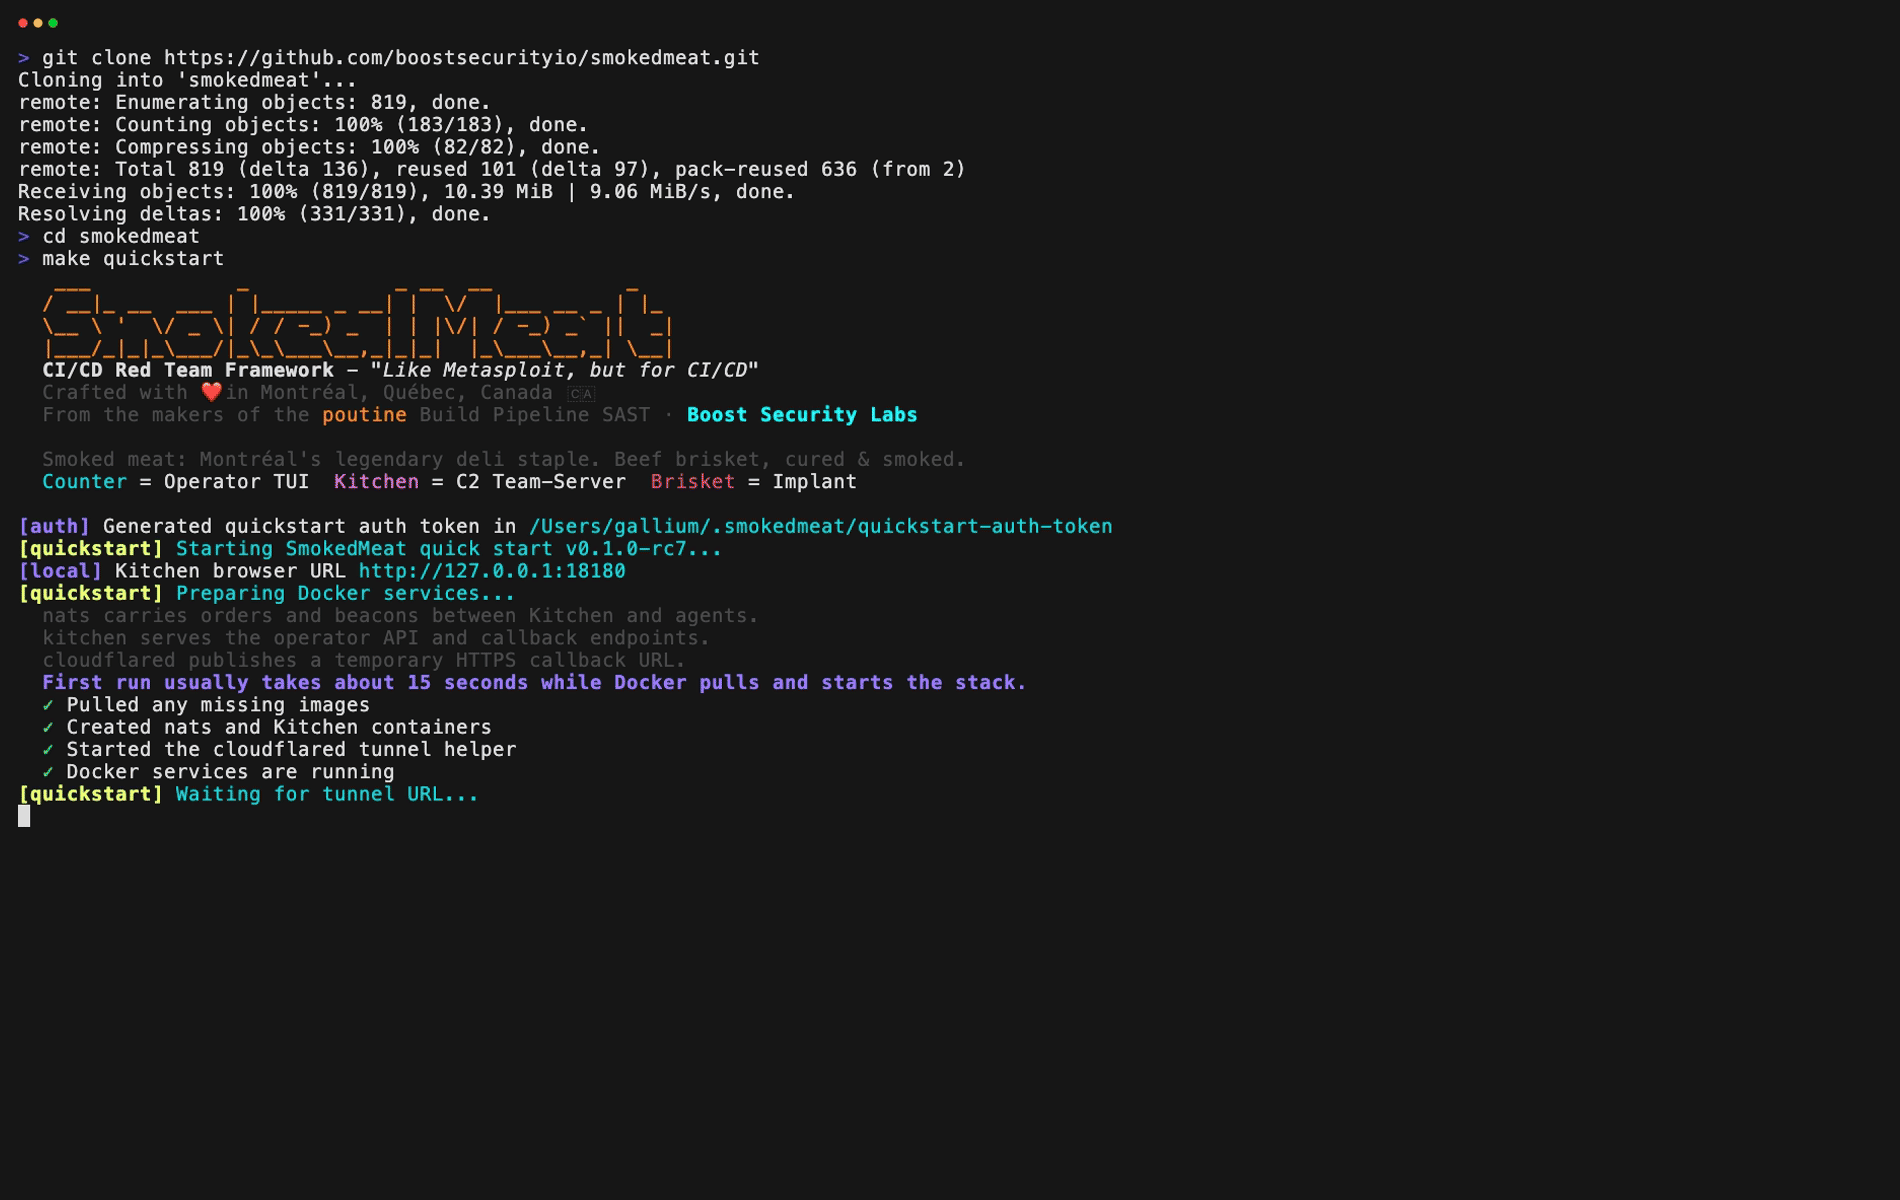 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
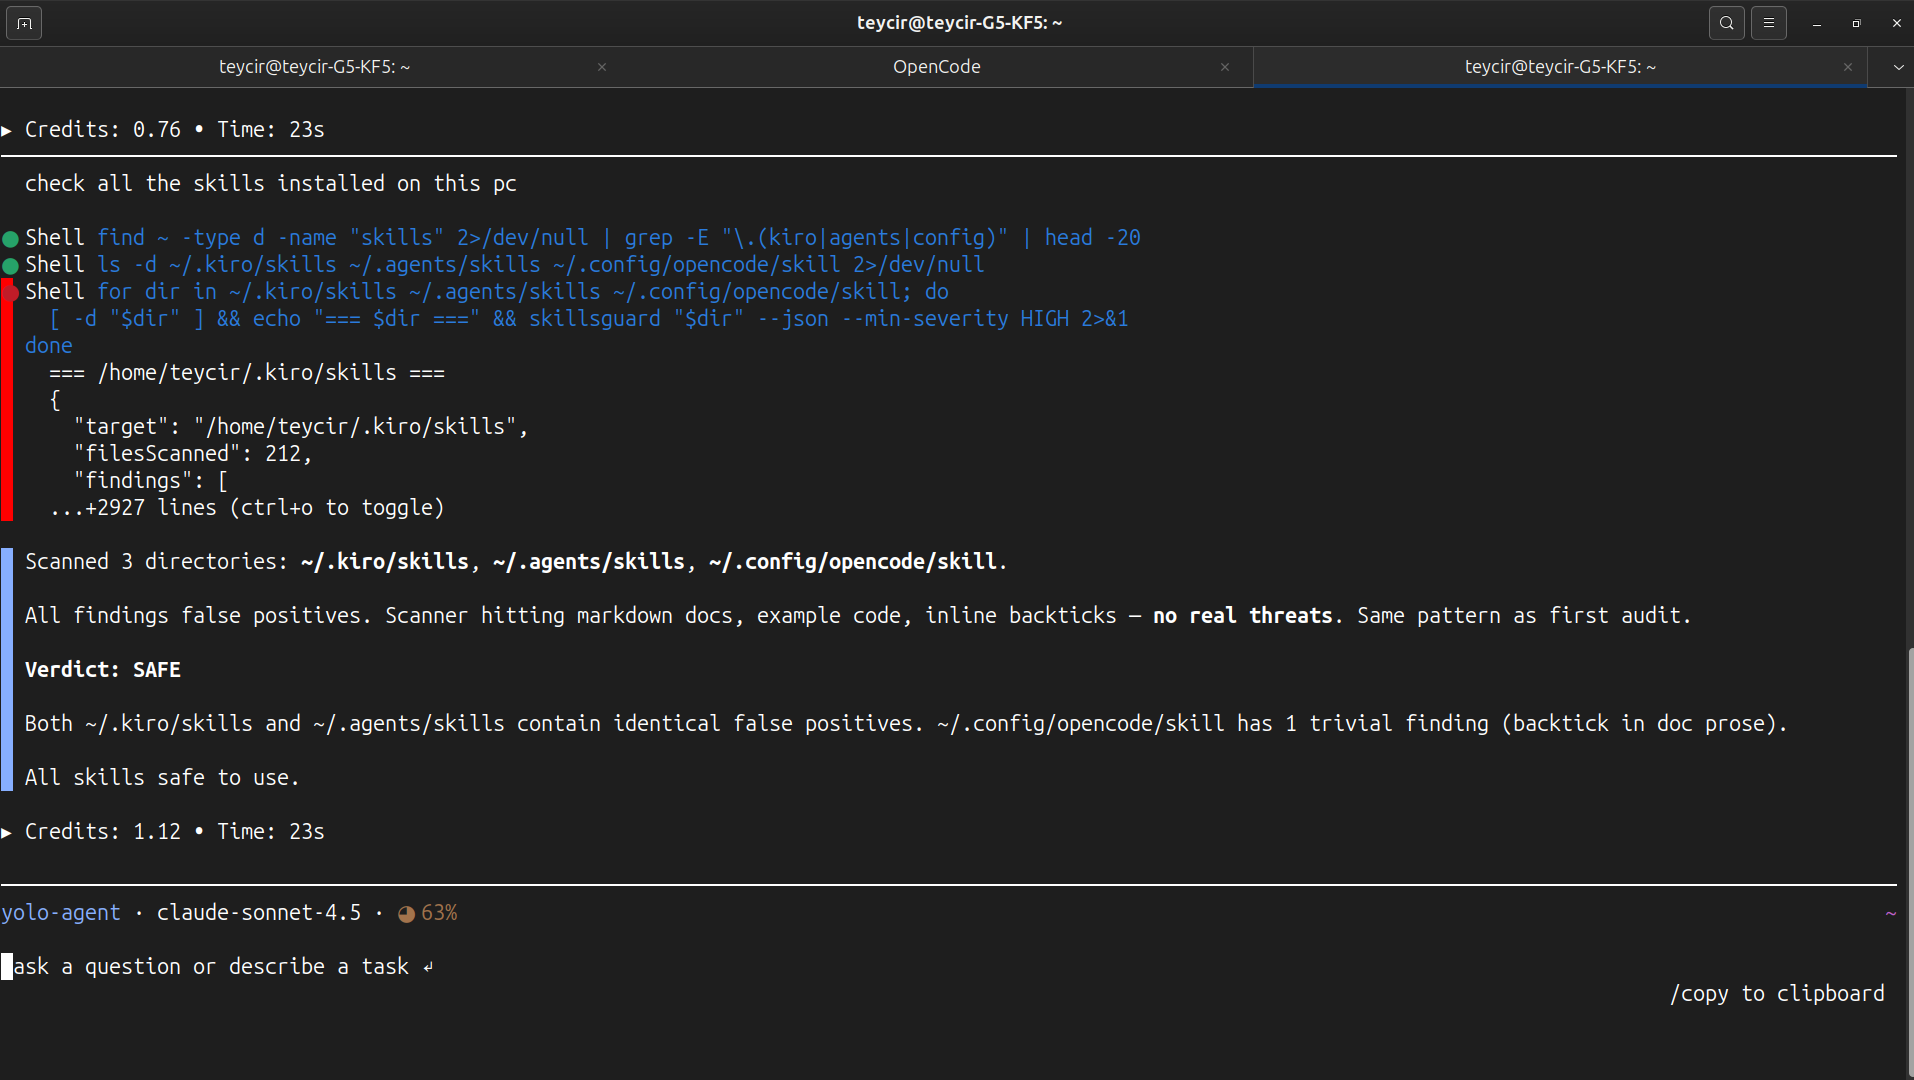 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 synacktiv/sccmsqlclient
MSSQL client for SCCM environments, enabling reconnaissance, remote PowerShell execution on managed clients, and extraction of sensitive secrets such…
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool

 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
 t3l3machus/eviltree
A python3 remake of the classic "tree" command with the additional feature of searching for user provided keywords/regex in files, highlighting those…
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 gquere/pwn_jenkins
Notes about attacking Jenkins servers
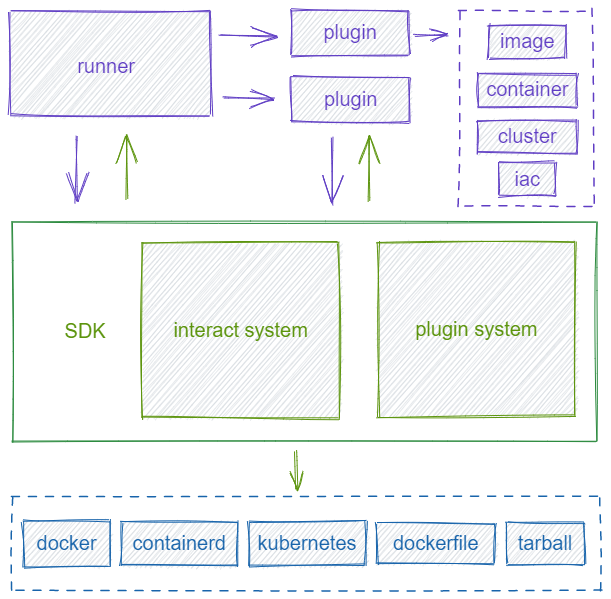 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
