

trufflehog
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
cloud-securitycode-analysisdevsecops+6
trufflesecurity/trufflehogFind, verify, and analyze leaked credentials
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 nvidia/skillspector
Security scanner for AI agent skills. Detect vulnerabilities, malicious patterns, security risks, prompt injection, data exfiltration, and…
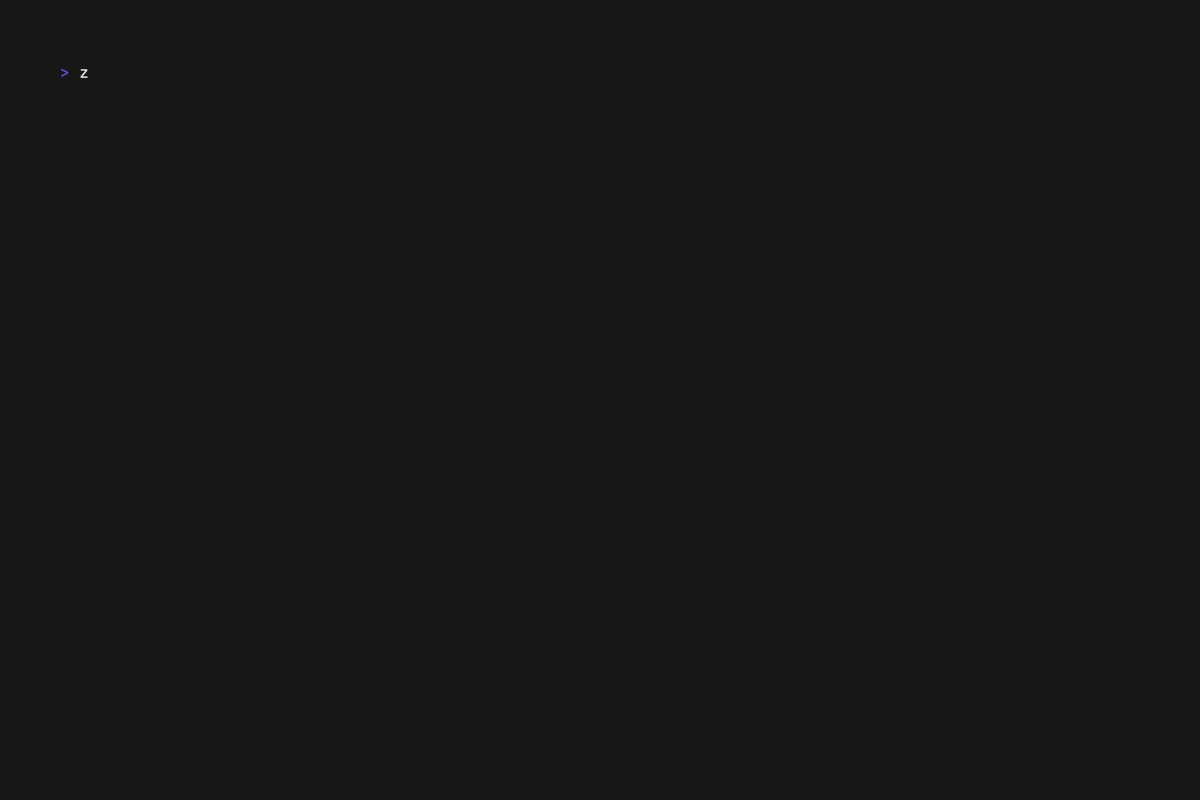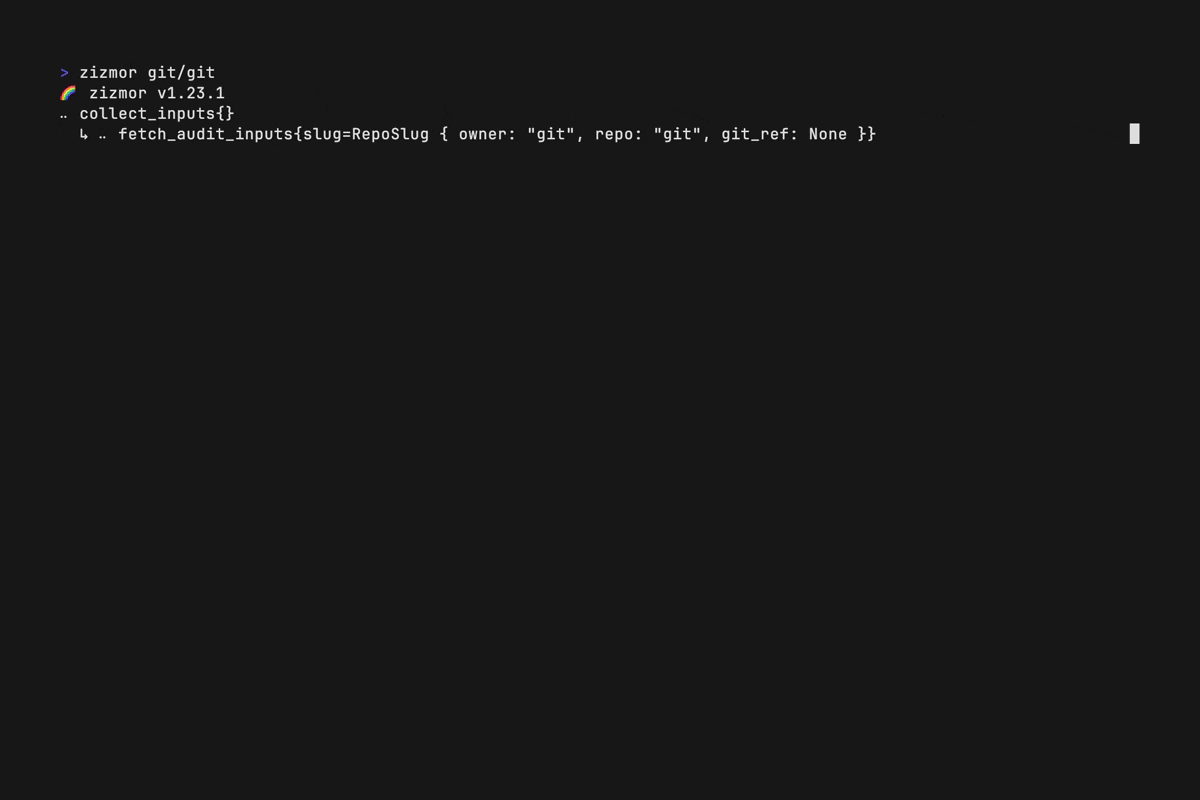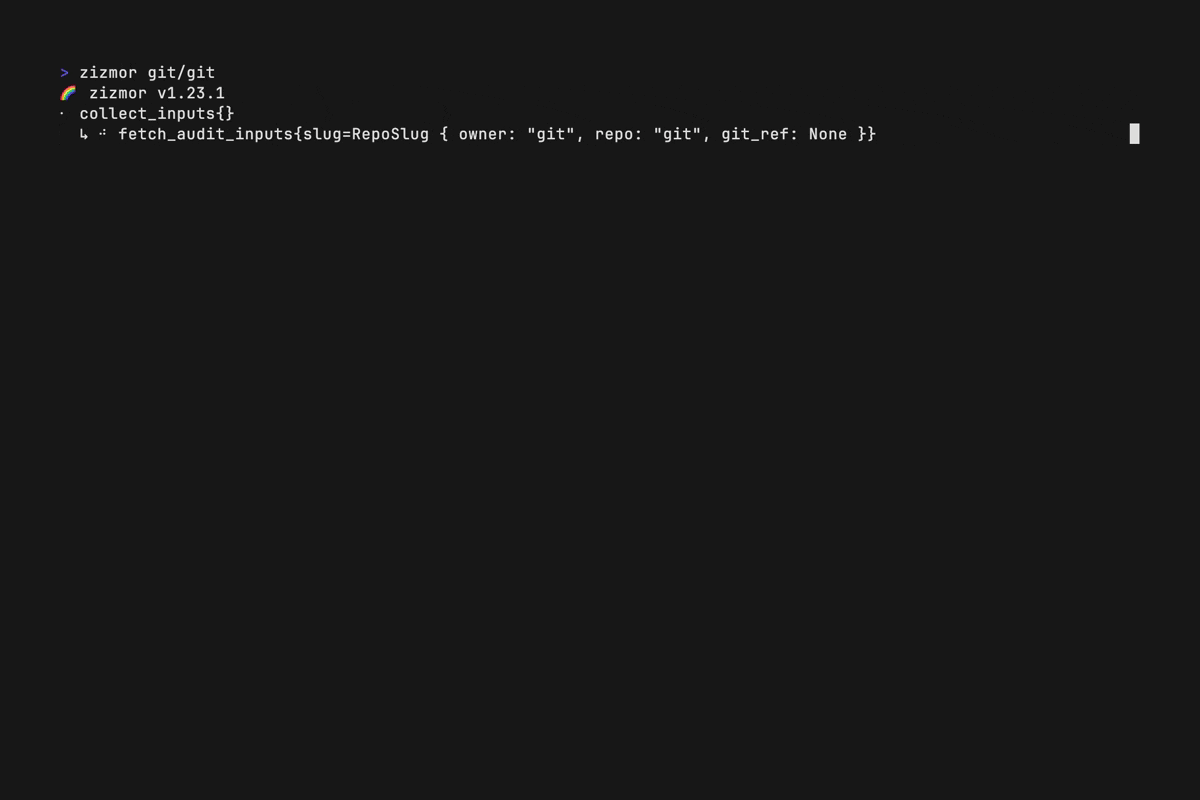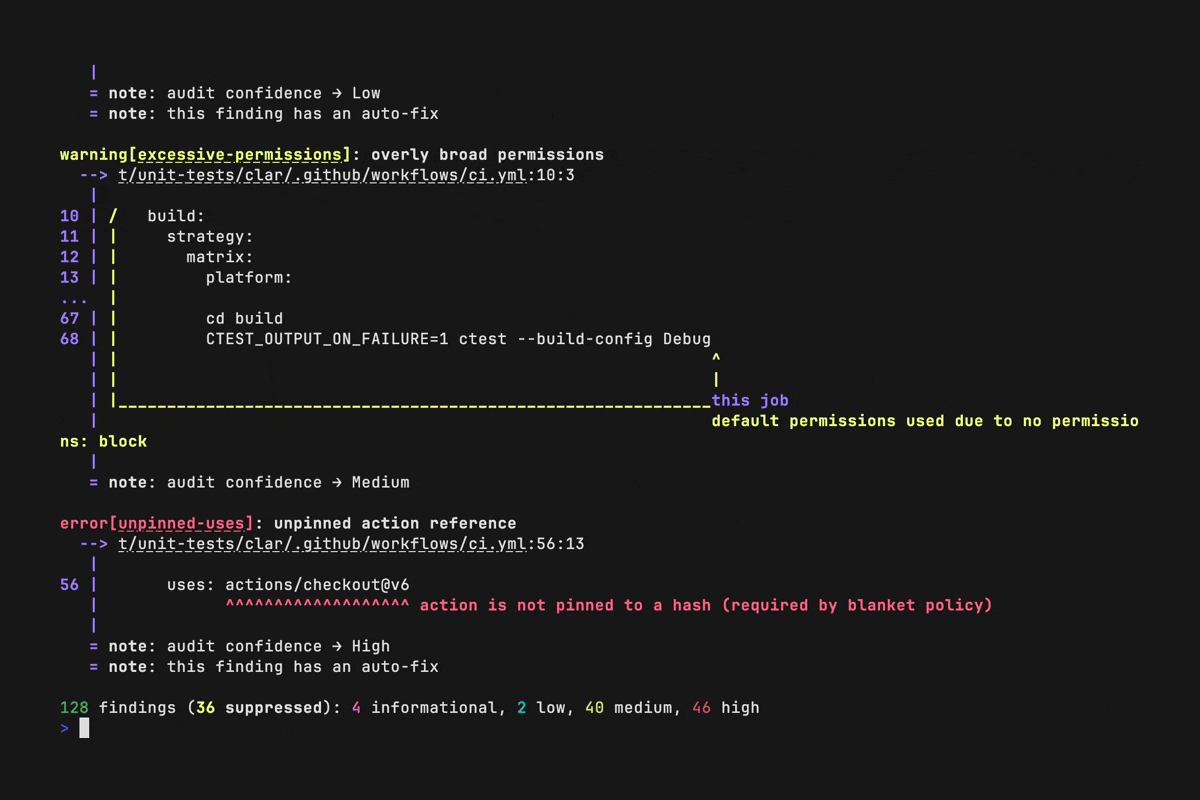 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 secretlint/secretlint
Pluggable linting tool to prevent committing credential.
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 ossf/scorecard
OpenSSF Scorecard - Security health metrics for Open Source
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 snyk/agent-scan
Security scanner for AI agents, MCP servers and agent skills.
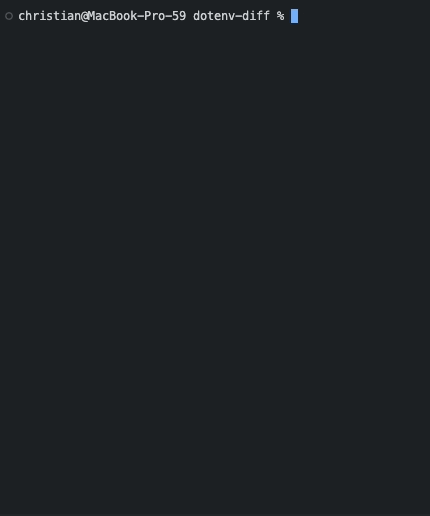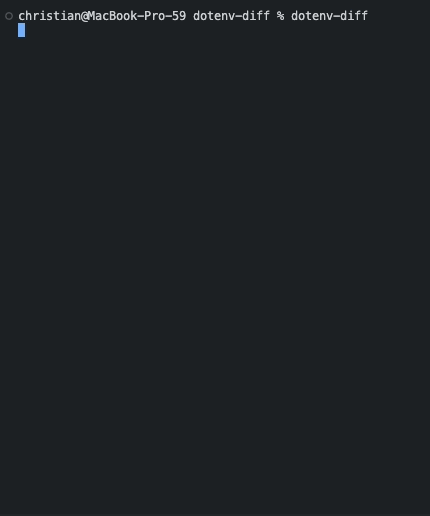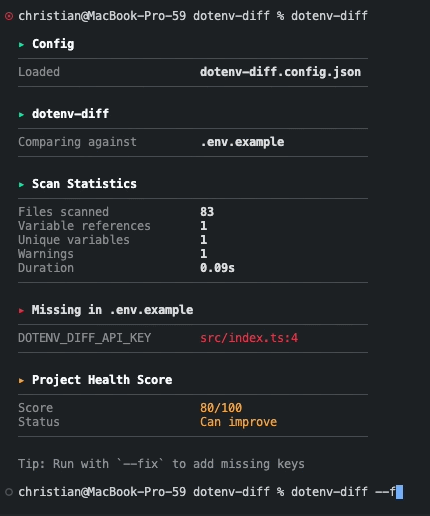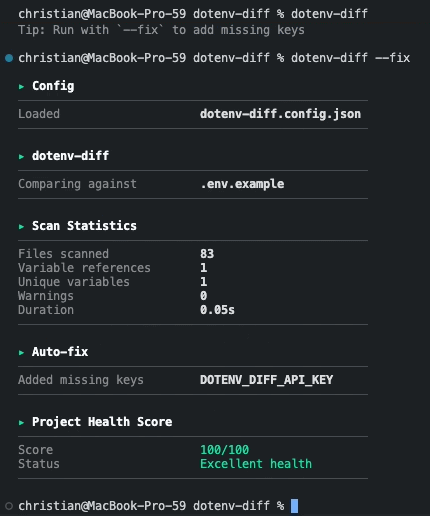 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
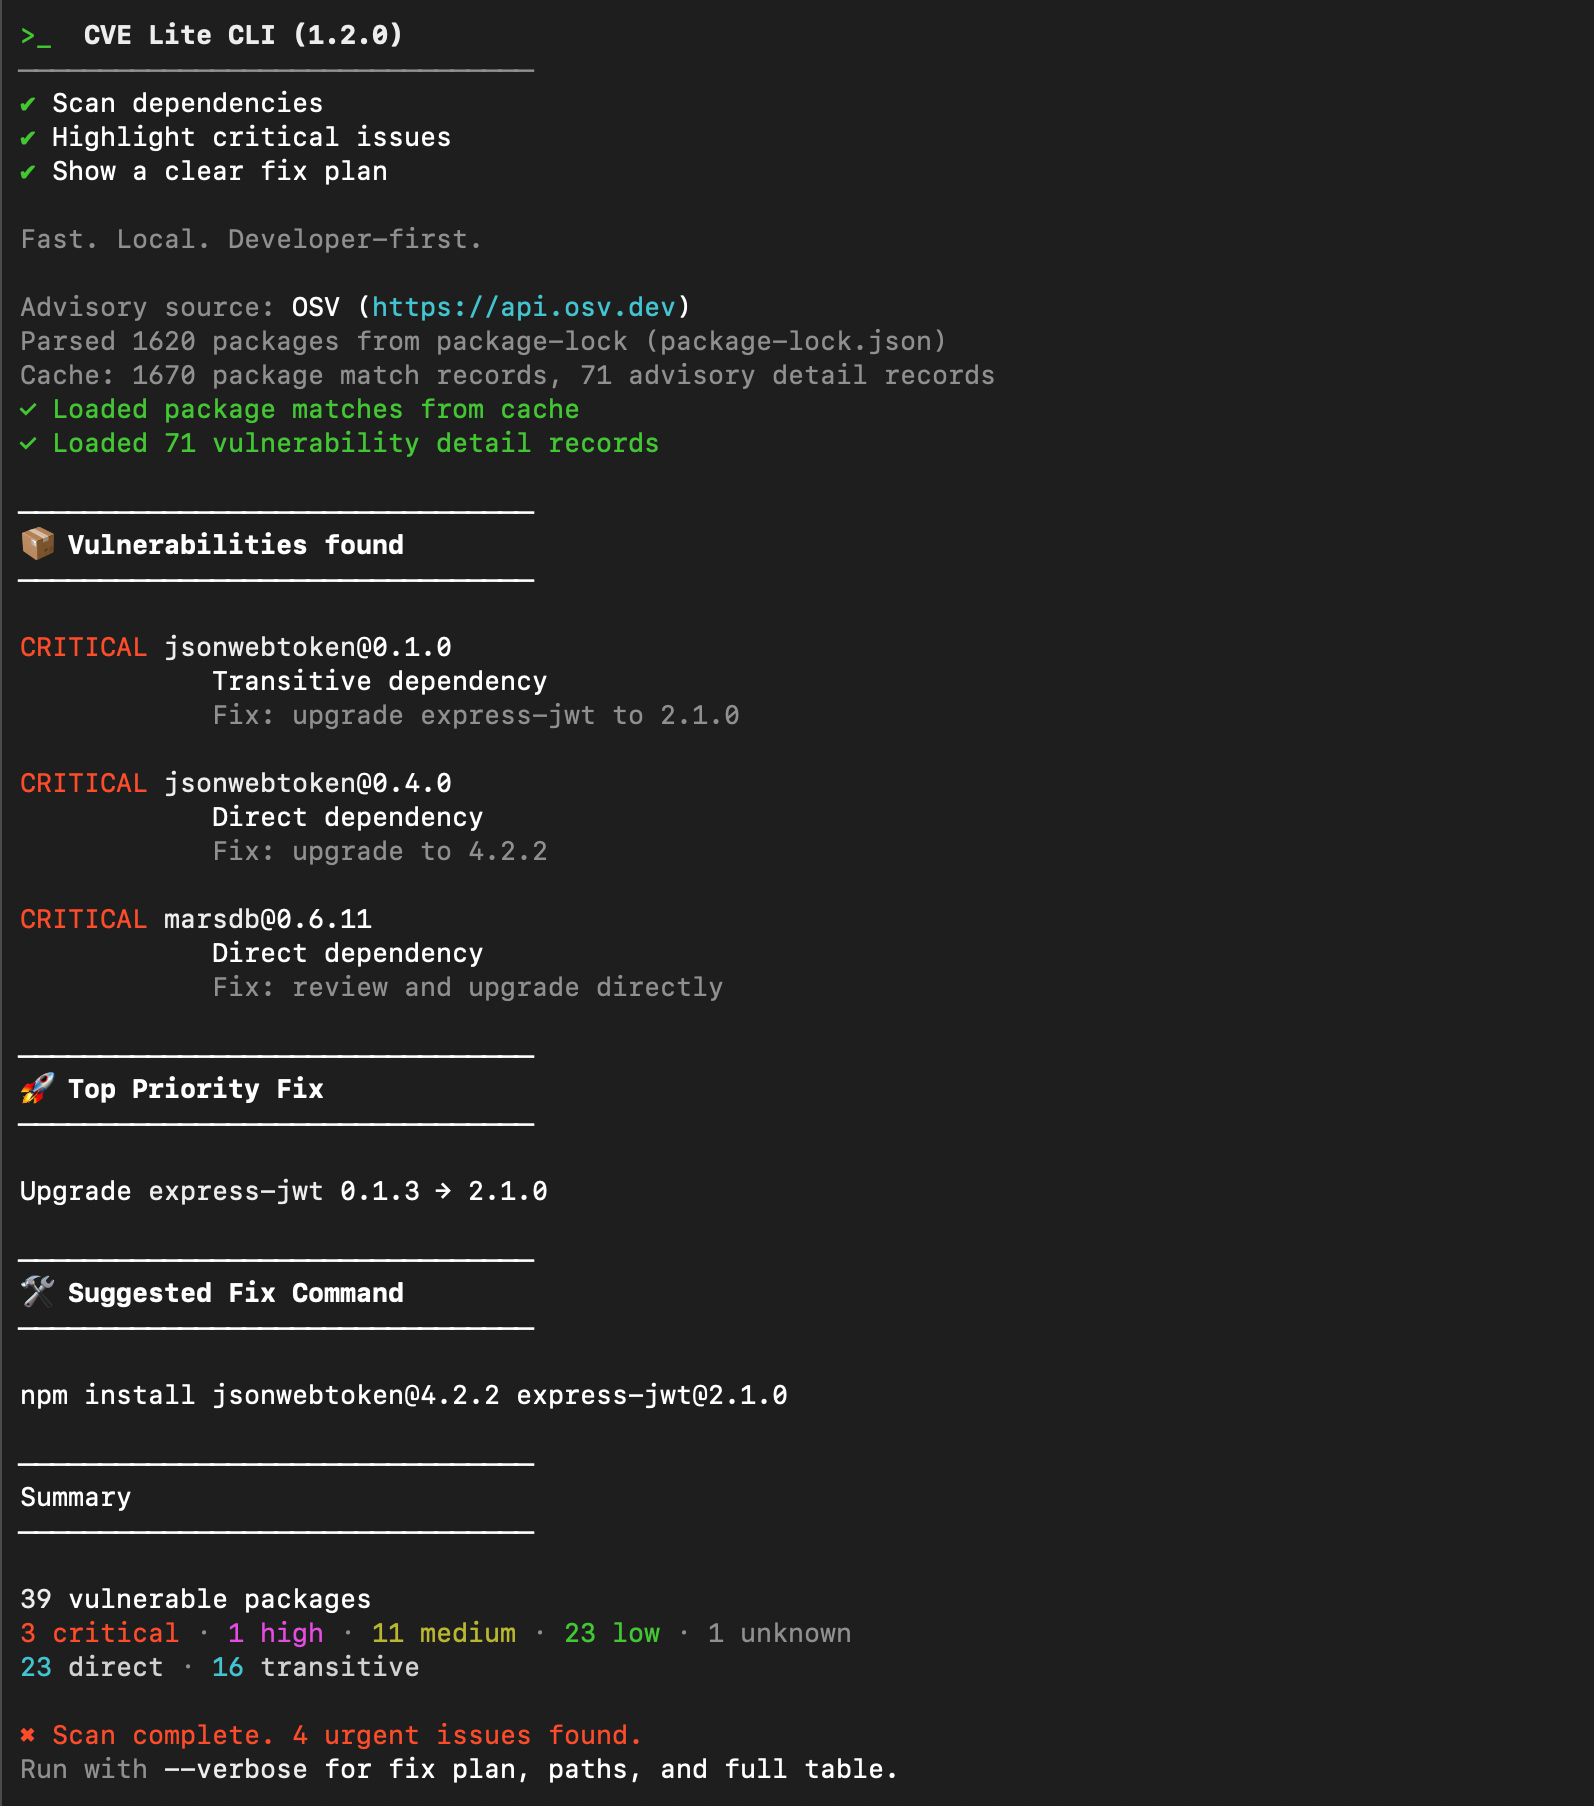 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.