
vault
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
authenticationauthentication-authorizationcloud-security+5
36.4k5h 39m ago
hashicorp/vaultA tool for secrets management, encryption as a service, and privileged access management
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 msaad00/agent-bom
Open-source cloud and AI security platform: scan code, dependencies, containers, cloud and AI agents/MCP into one security graph. Self-host free in…
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 gitguardian/ggshield
Detect and validate 500+ types of hardcoded secrets with advanced checks. Use it as a pre-commit hook, GitHub Action, or CLI for proactive secret…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
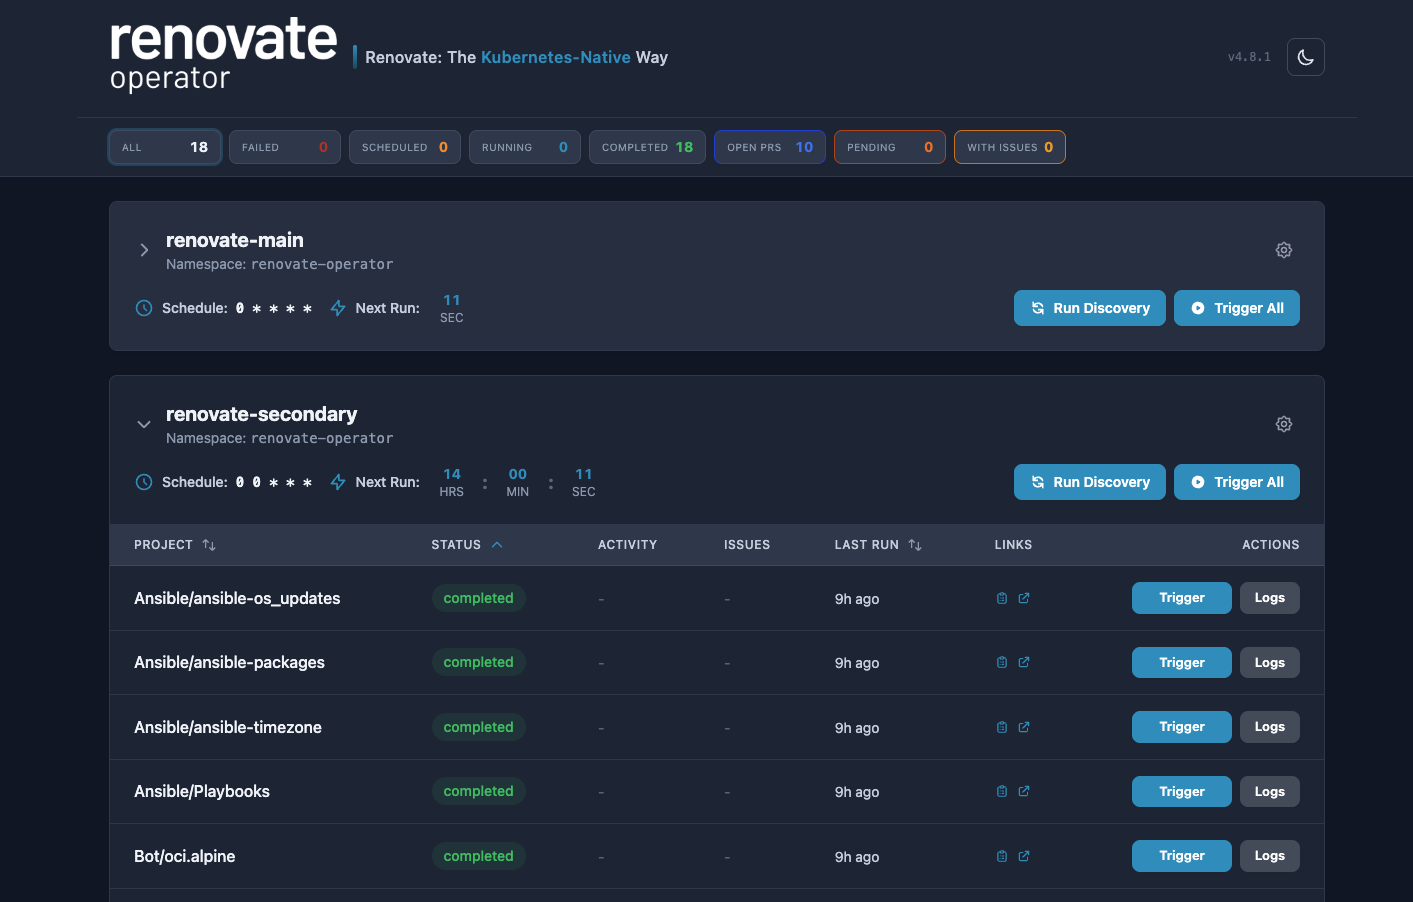 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.

 anchore/grype
A vulnerability scanner for container images and filesystems