

wrongsecrets
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
cloud-securitycontainer-securityctf+5
owasp/wrongsecretsVulnerable app with examples showing how to not use secrets
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
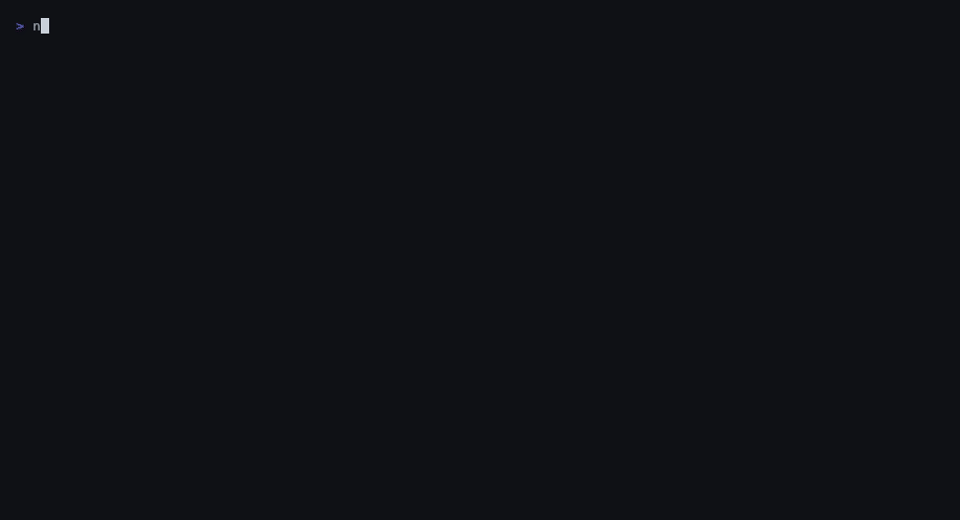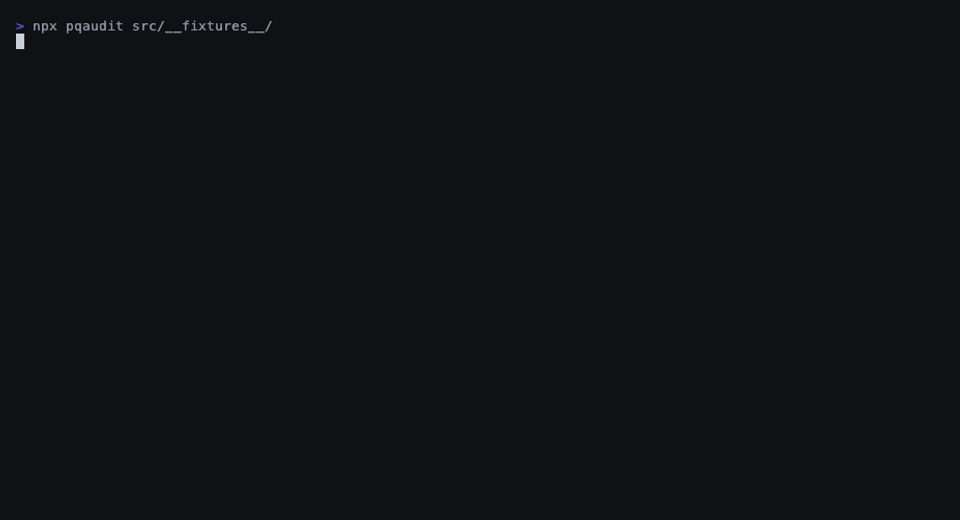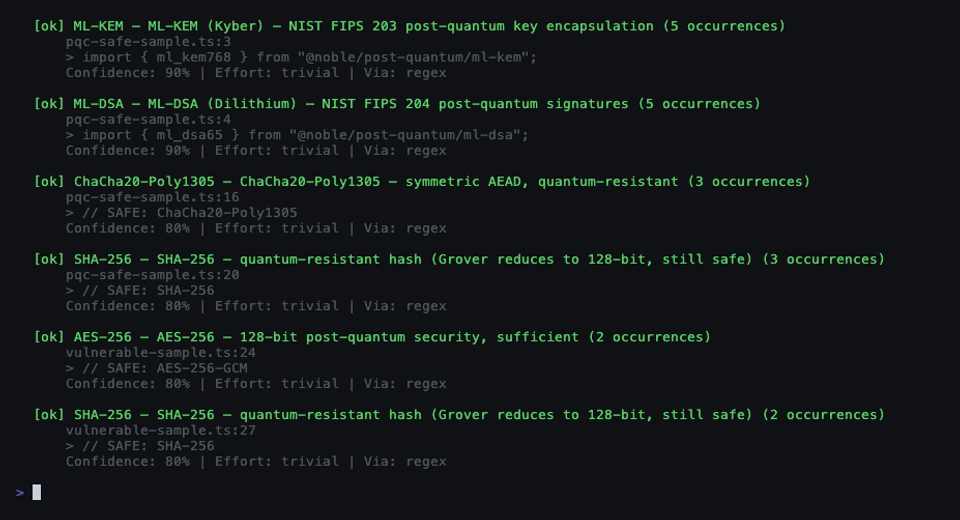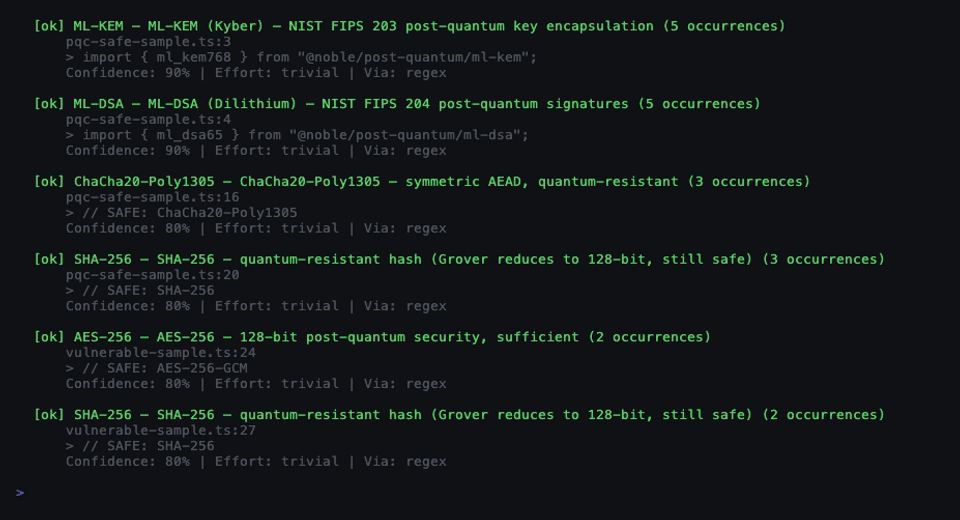 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
 sdushantha/dora
Find exposed API keys based on RegEx and get exploitation methods for some of keys that are found
 jas502n/database-spring-enc
sprint encode (plan text) get enc password
 josue87/givemesecrets
Use regular expressions to get sensitive information from a given repository (GitHub, pip or npm).