

autorun-audit
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
ai-securitycode-analysisconfiguration-auditing+6
ag3ntsc4rn/autorun-auditFind code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
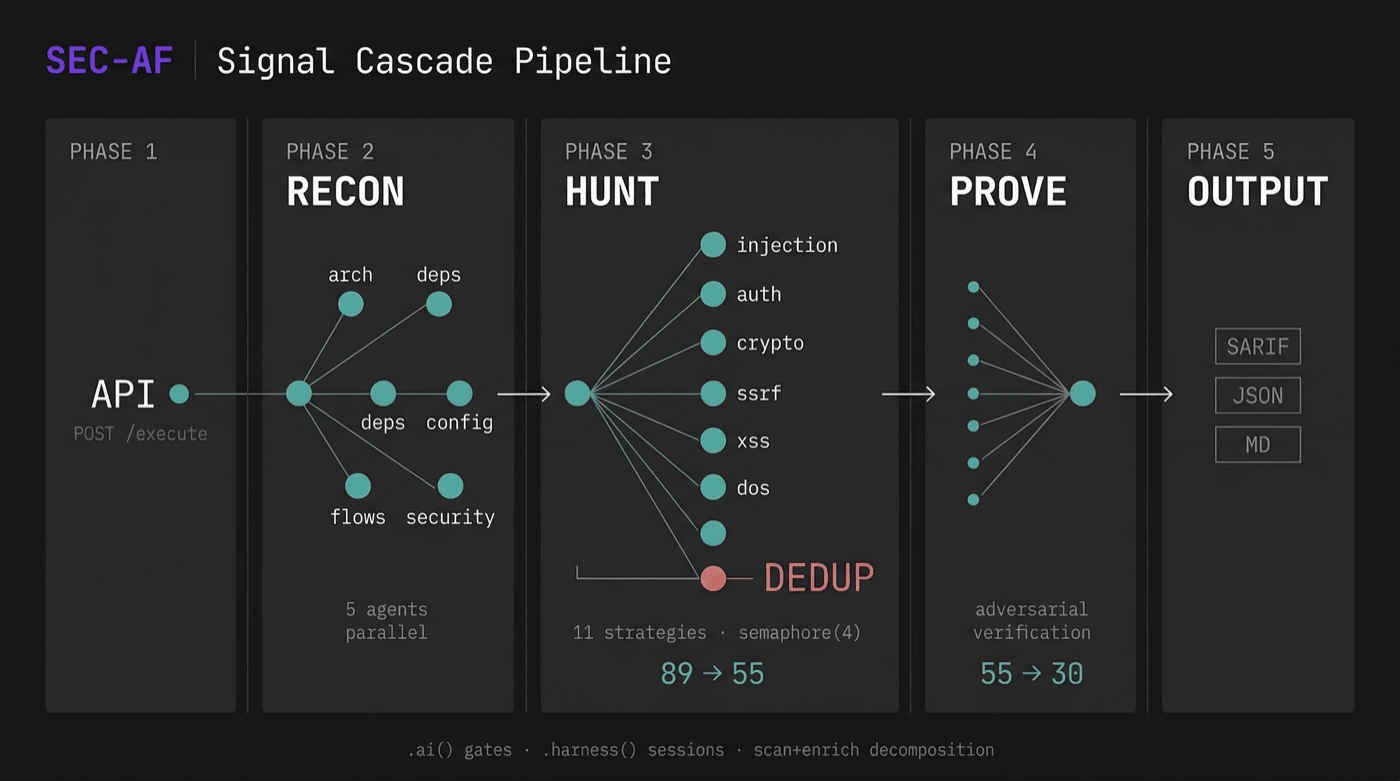 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 xenoncyber/envy
A terminal based tool for managing secrets with both tui and cli support
 anecdotes-yair/trust-my-agent-ai
Security & Compliance bodyguard for OpenClaw agents
 behisecc/vibesec-skill
This skill helps Claude write secure code and prevent common vulnerabilities.
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner