

training-application-security
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
api-securitydevsecopseducation+7
18
ransomleak/training-application-securityInteractive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 thewhiteh4t/llmreaper
Passive LLM Conversation Capture & Sensitive Data Exposure Research
 sivaadityacoder/cve-2026-22038
Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
 jchable/miasma-toolkit
Detection & remediation toolkit for the Miasma / Shai-Hulud worm and CVE-2026-35603 (AI-agent/IDE config injection)
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
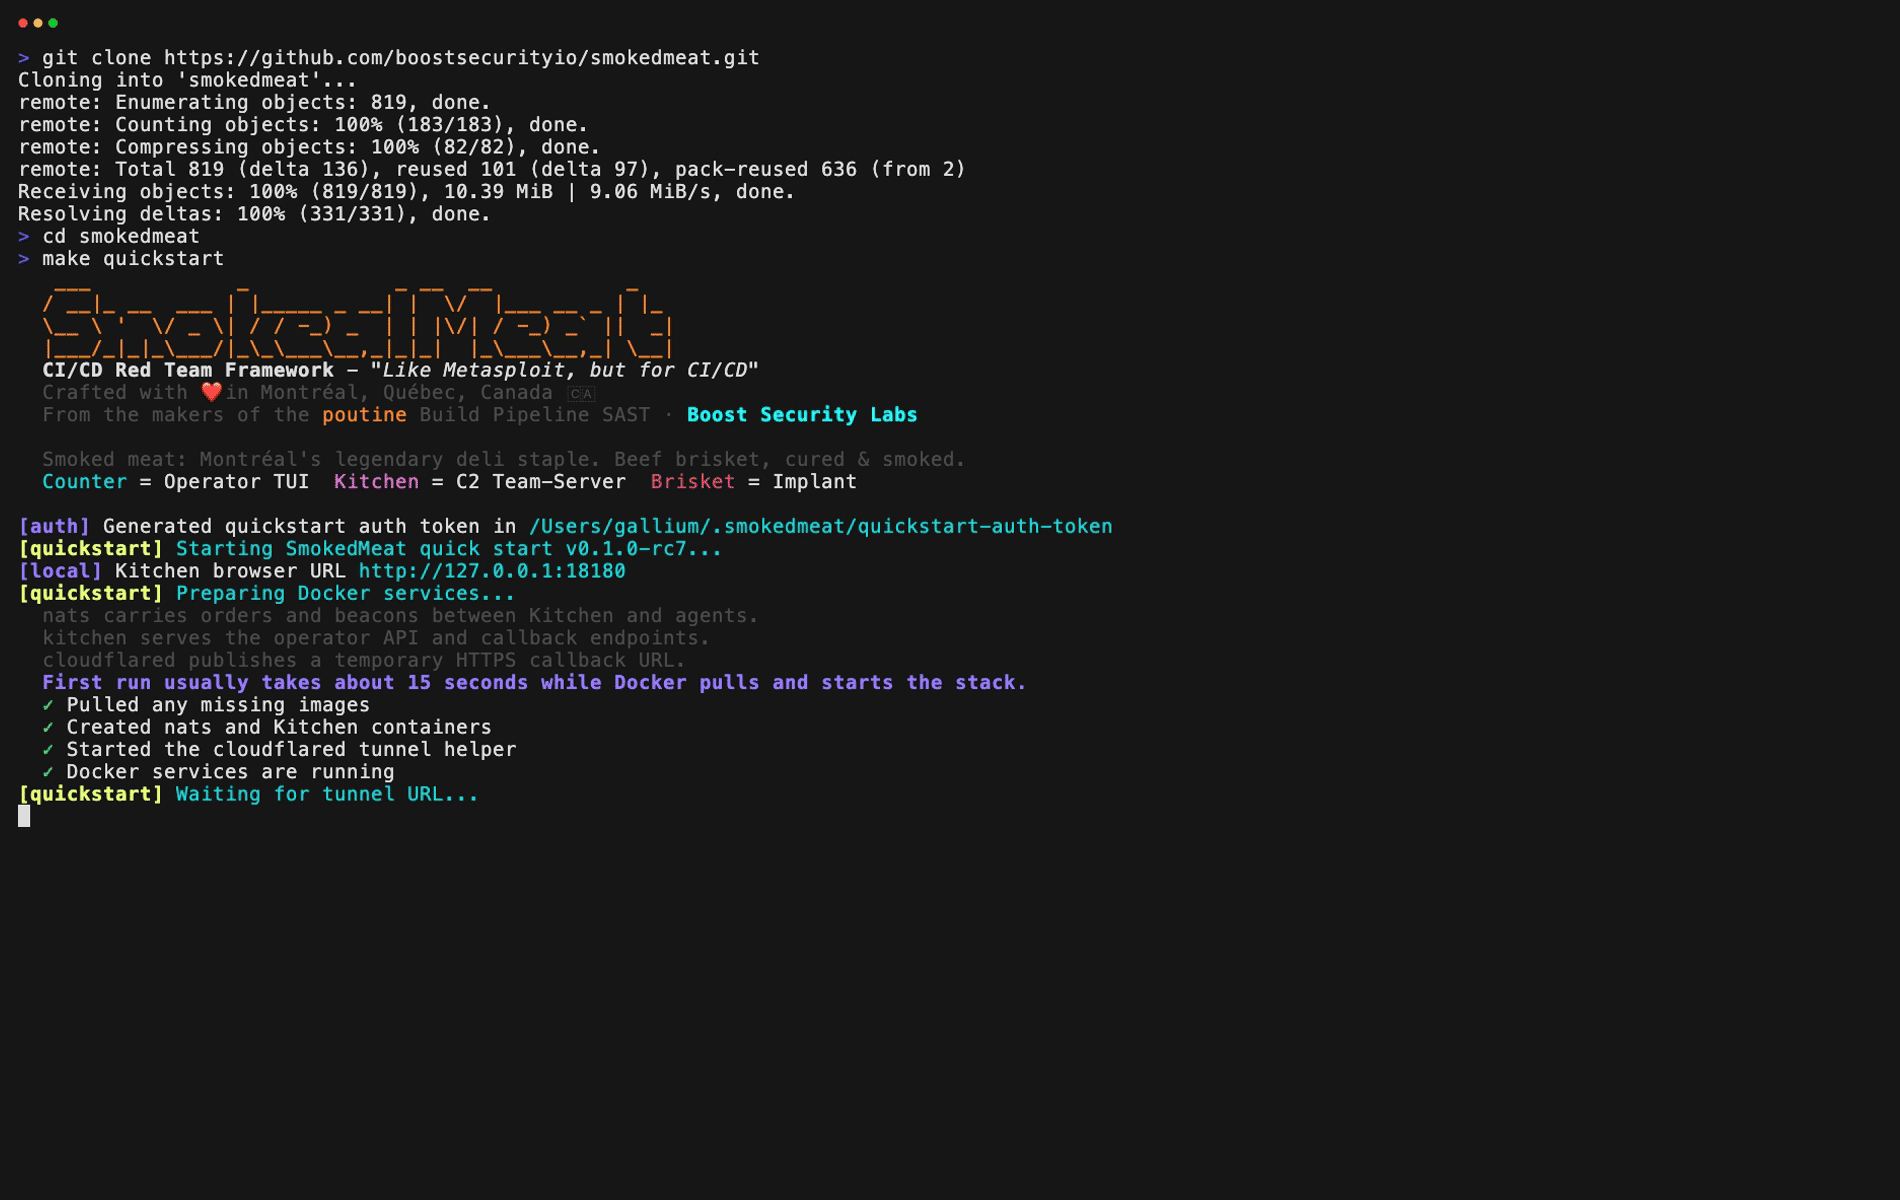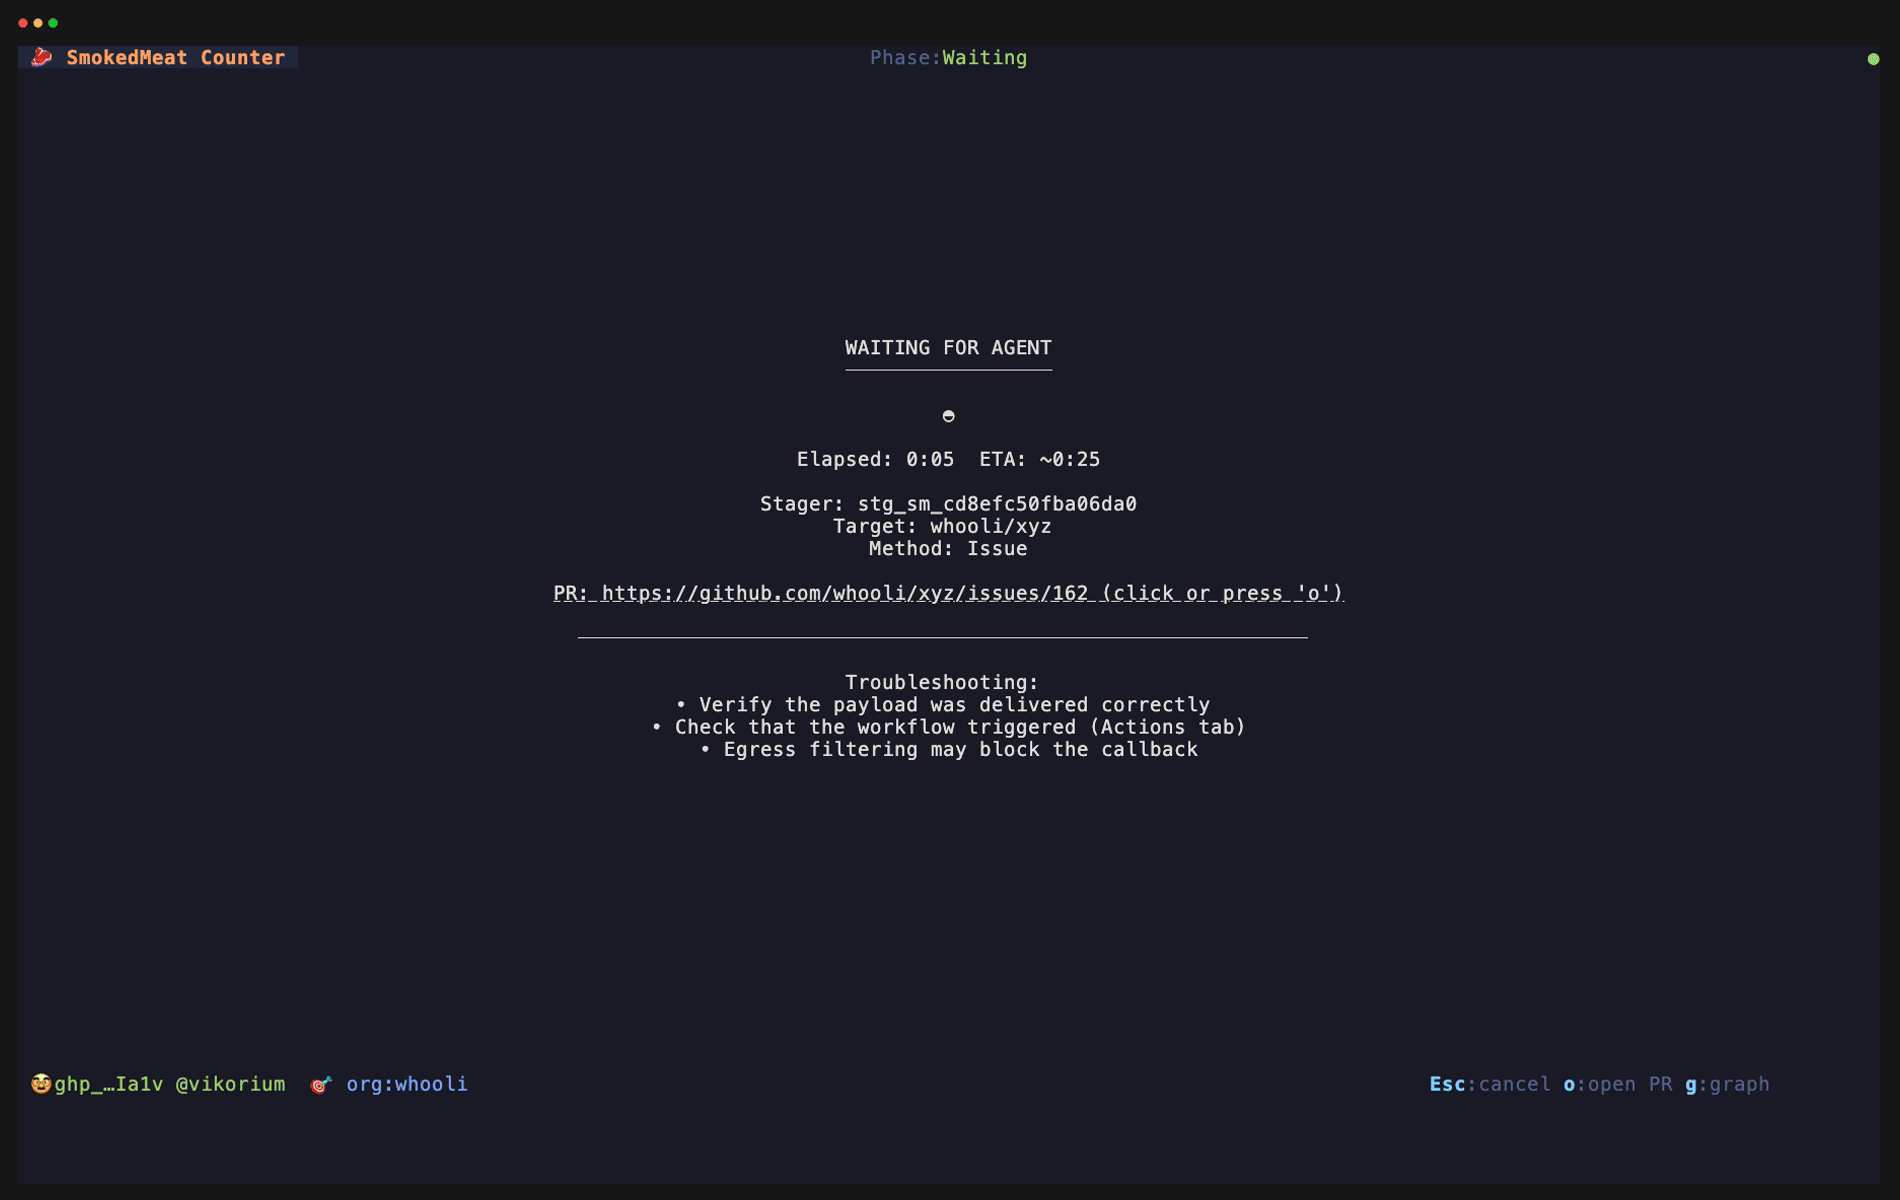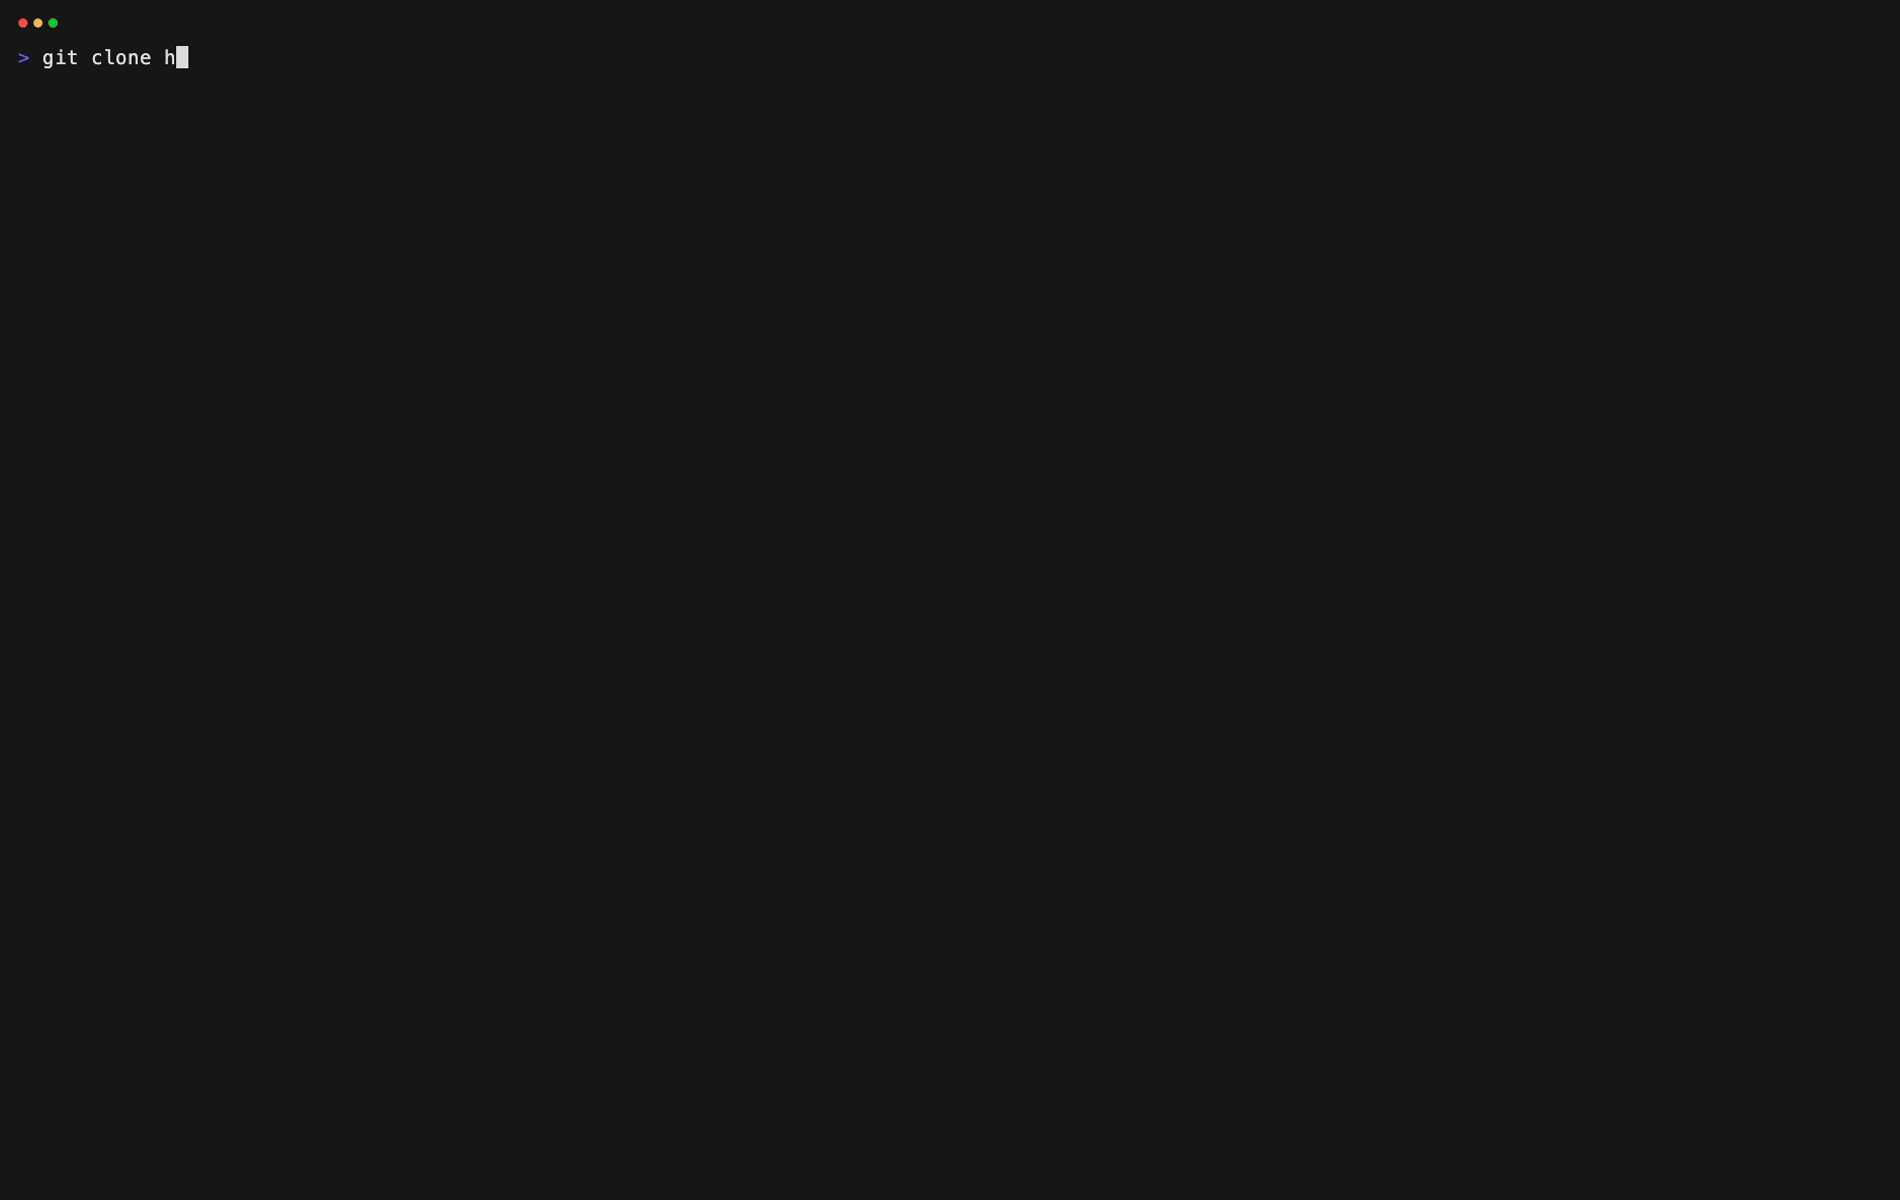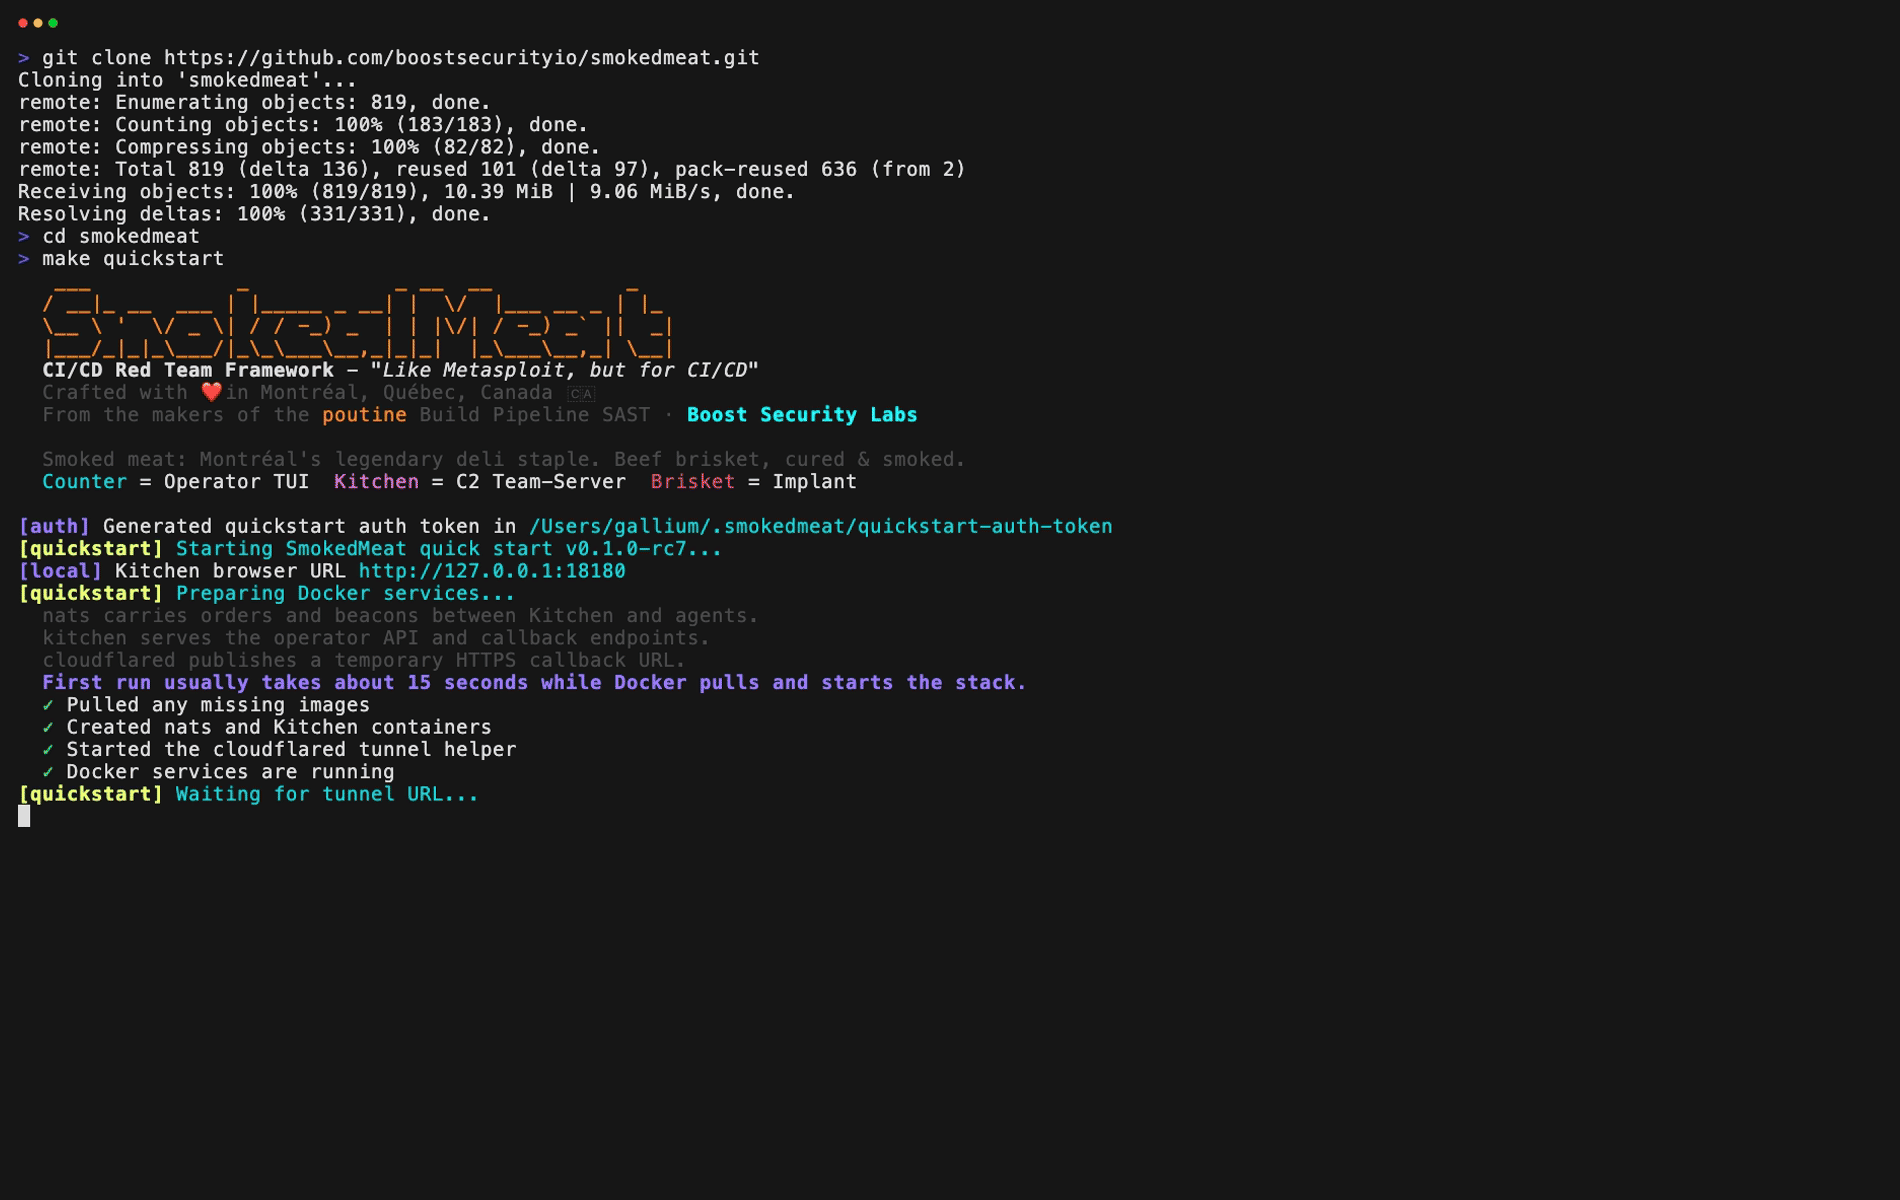 boostsecurityio/smokedmeat
A CI/CD Red Team Framework for demonstrating Build Pipeline security risks.
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
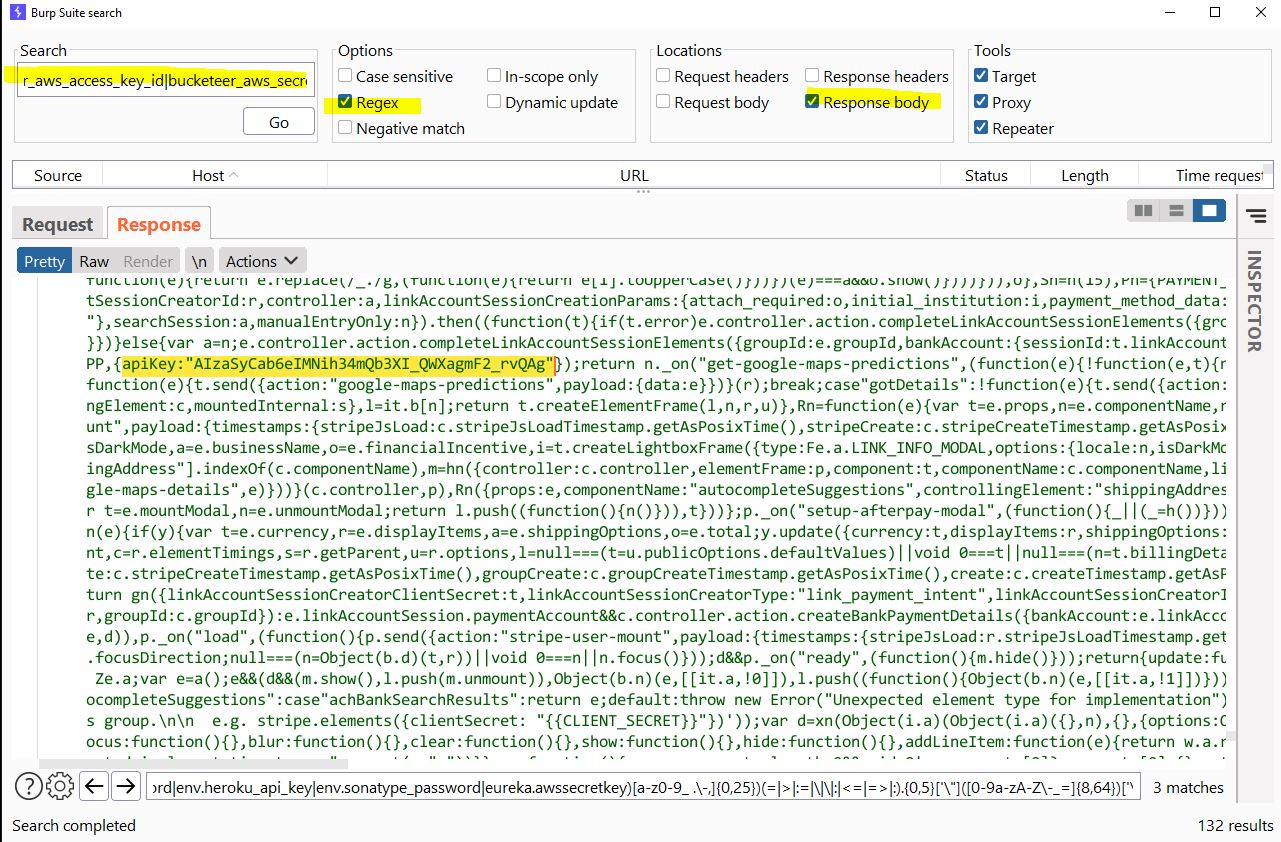 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
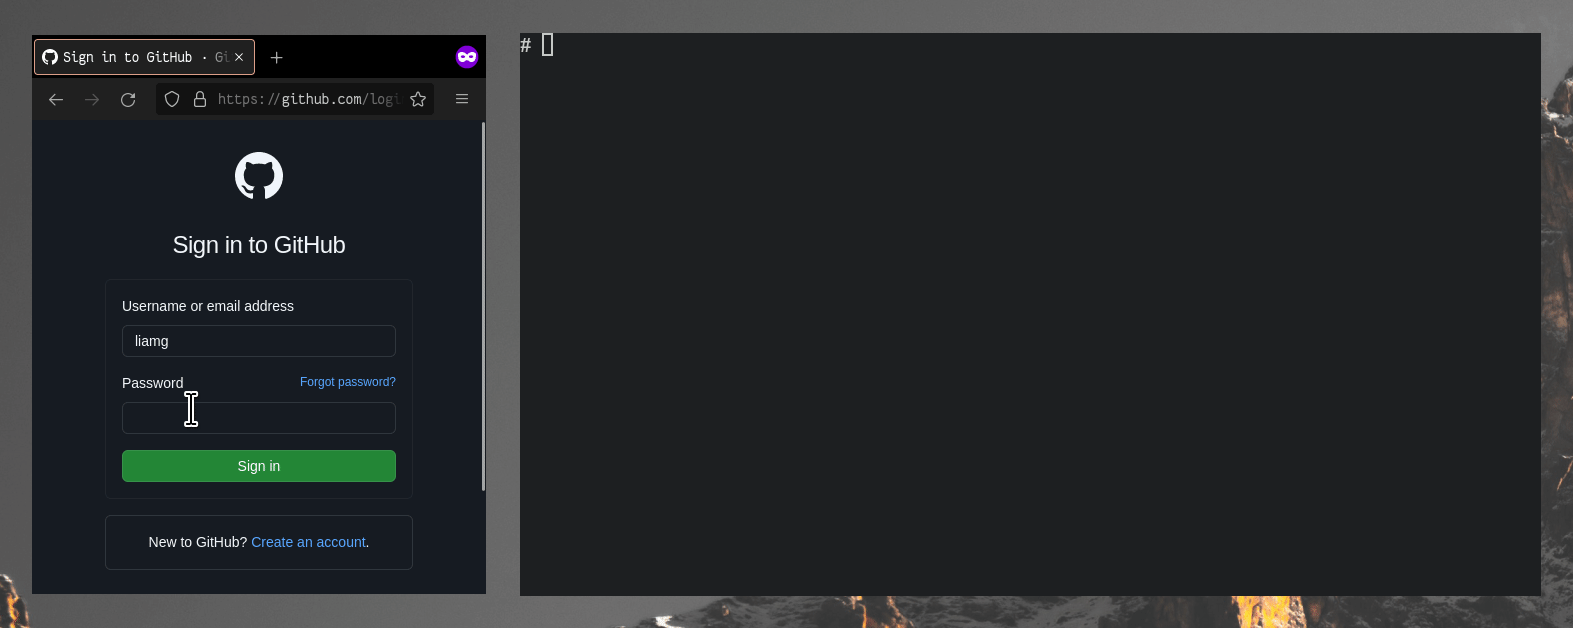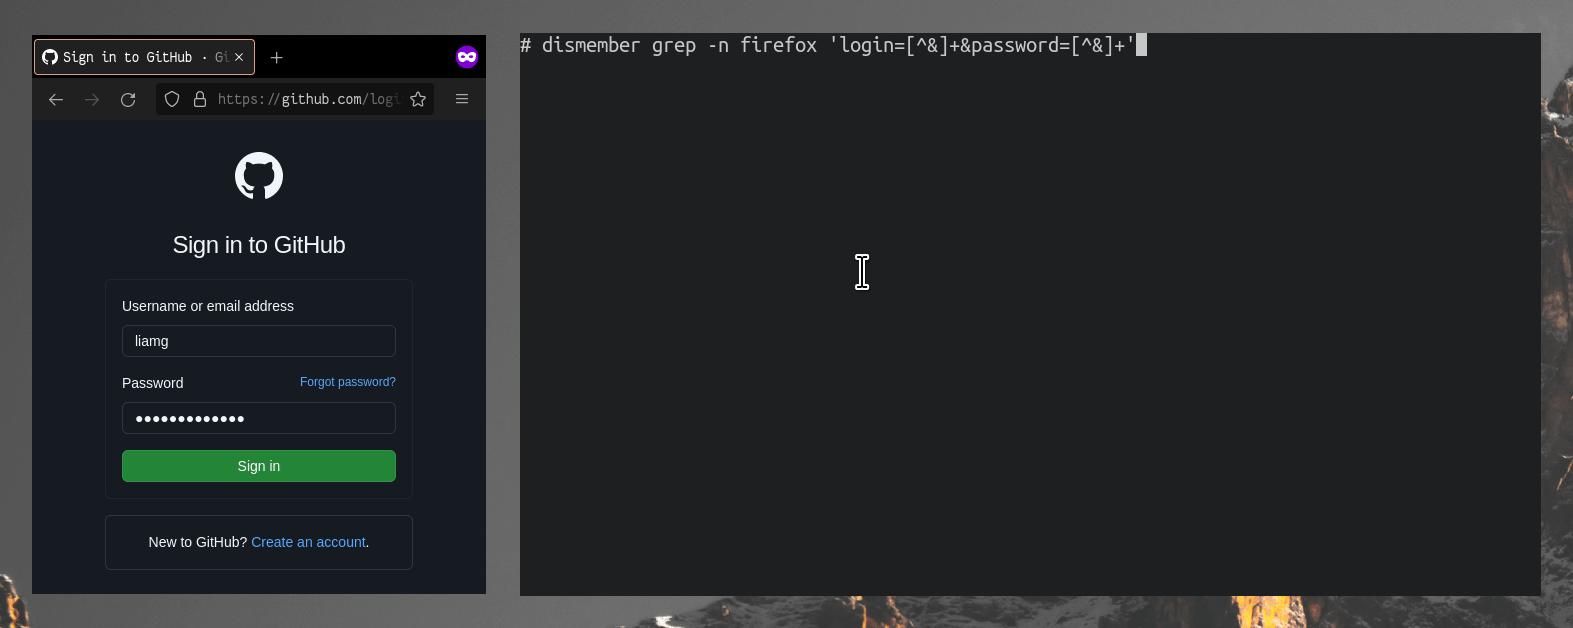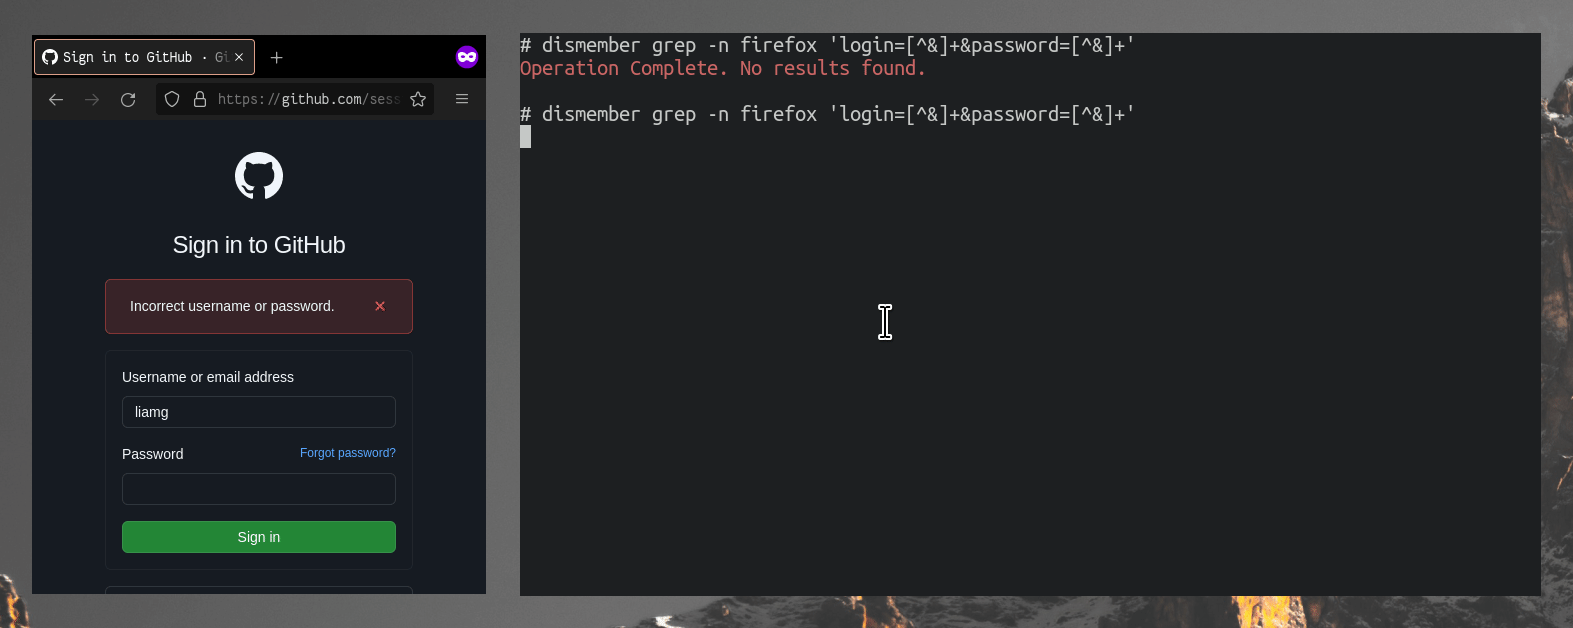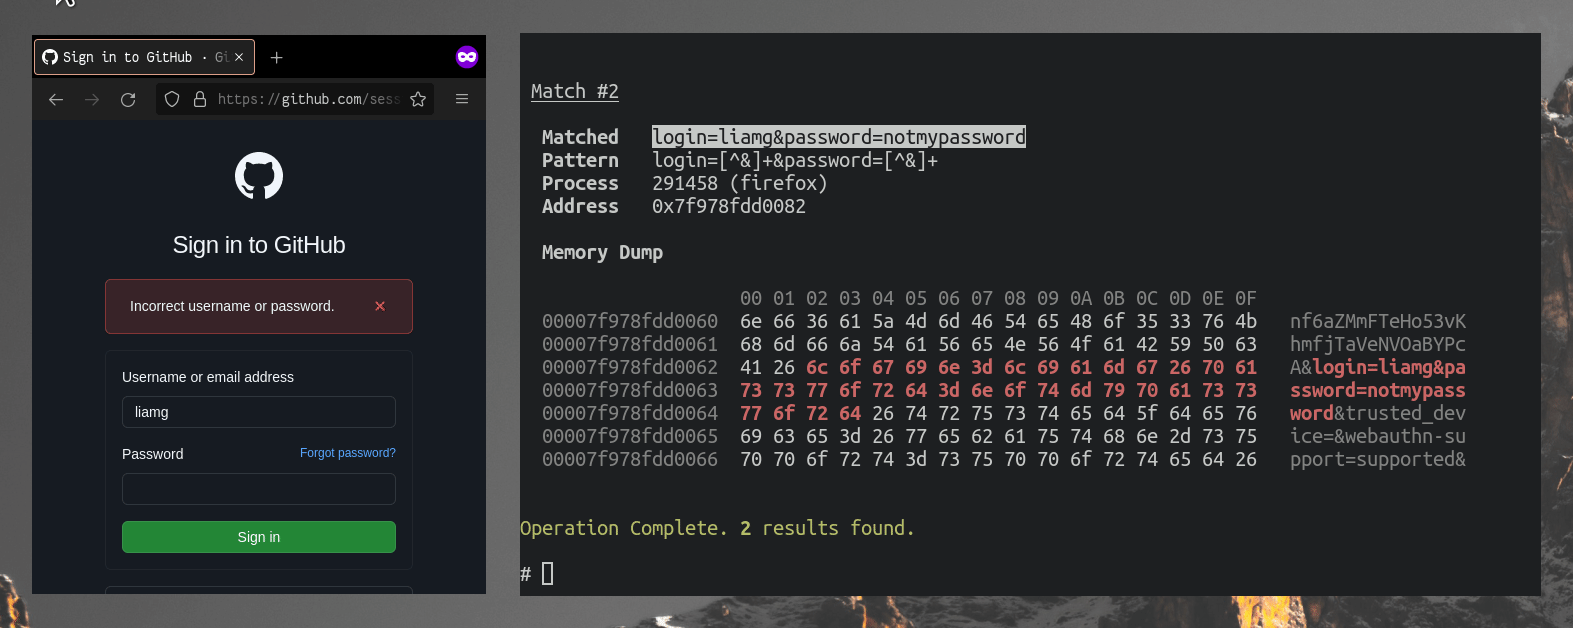 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 mcp-shark/mcp-shark
Wireshark-like forensic analysis for Model Context Protocol communications Capture, inspect, and investigate all HTTP requests and responses between…
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…

 randomrobbiebf/cve-2024-0368
Hustle Plugin <= 7.8.3 contains hardcoded HubSpot API credentials in inc/providers/hubspot/hustle-hubspot-api.php