

semgrep
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
api-securityapi-security-testingcode-analysis+9
17.3k1 day ago
semgrep/semgrepLightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 stuxctf/mhf
Mobile Helper Framework (mhf) is a tool that automates the process of identifying the framework/technology used to create a mobile application.…
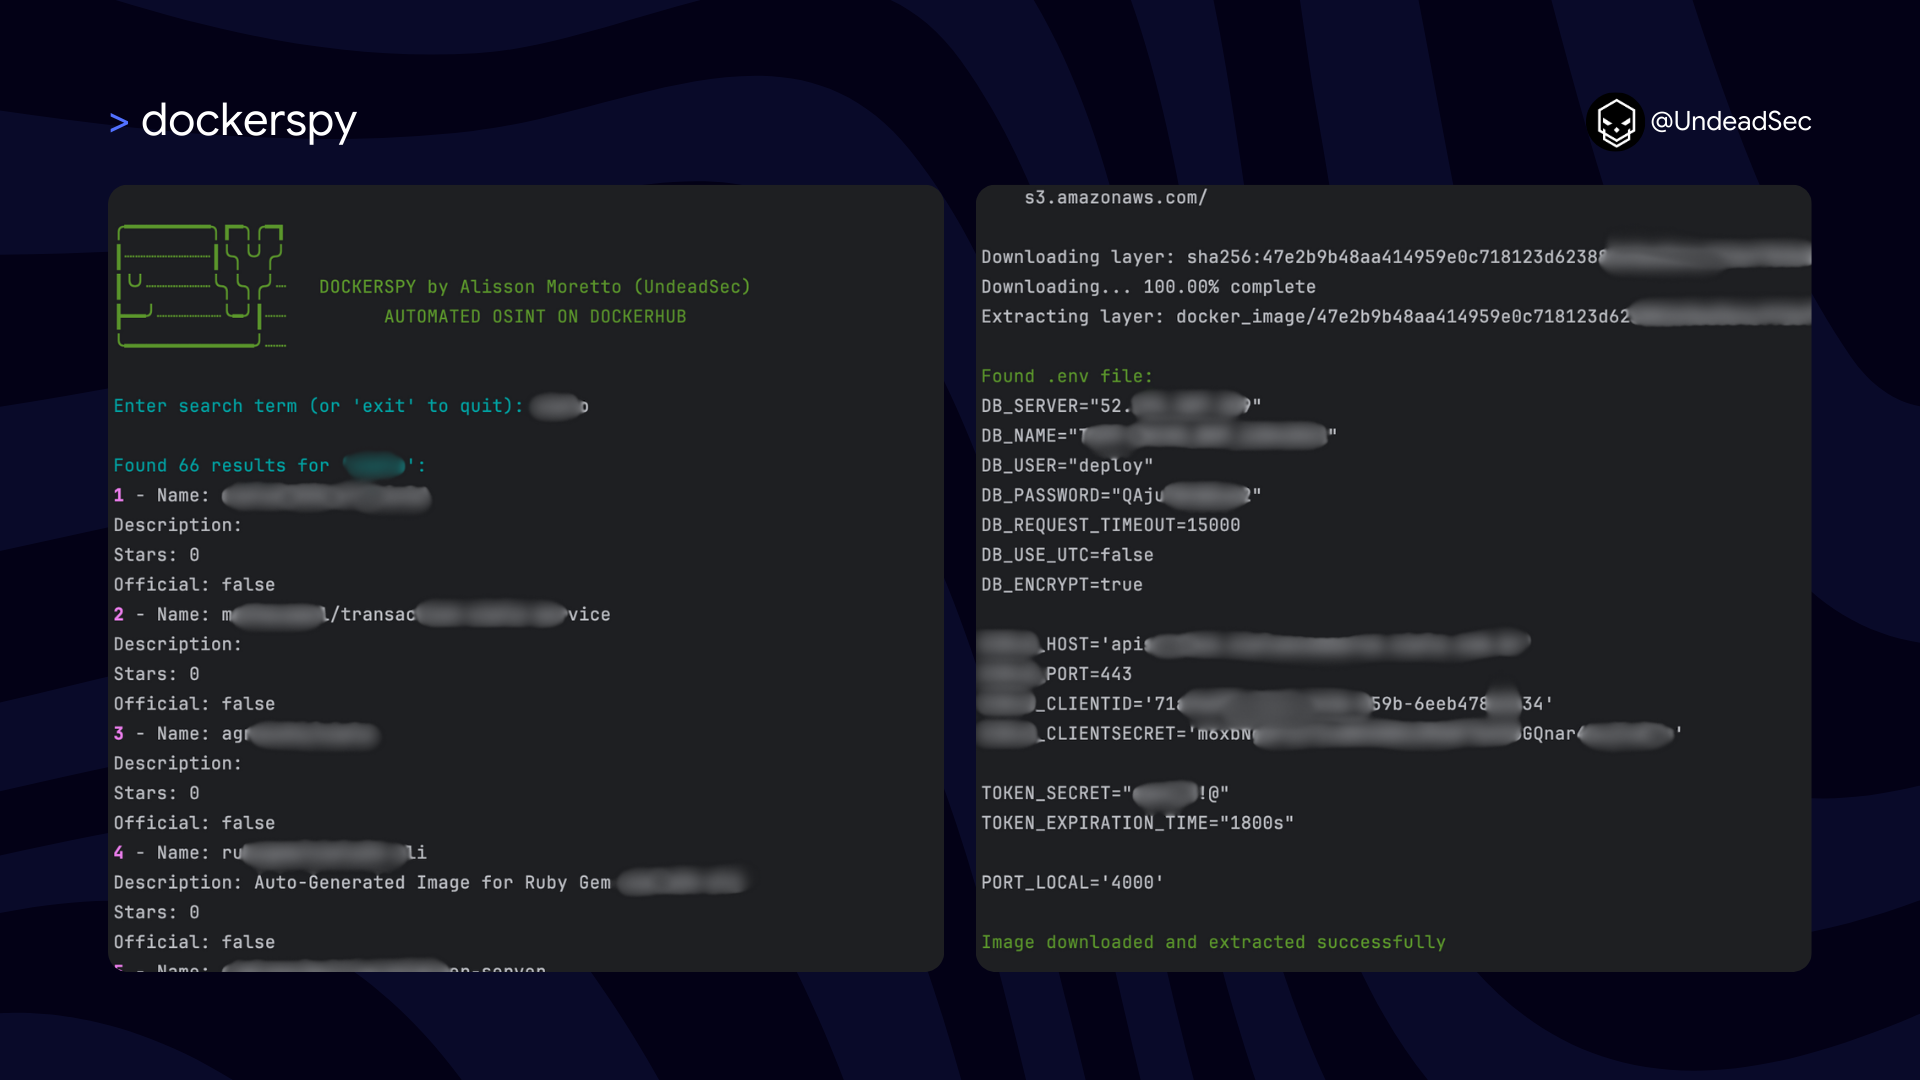 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 sourcecode-ai/aura
Python source code auditing and static analysis on a large scale
 sivaadityacoder/cve-2026-22038
Detailed analysis of CVE-2026-22038, a high-severity vulnerability in AutoGPT Stagehand blocks that logs API keys in plaintext, including root cause,…
 yeee3642/edu-recon
Authorized education-sector recon & triage orchestrator (nmap/dirsearch/sqlmap/hydra + CVE-2024-4577, secret/API-key leak, XSS, wp2shell) with a web…
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
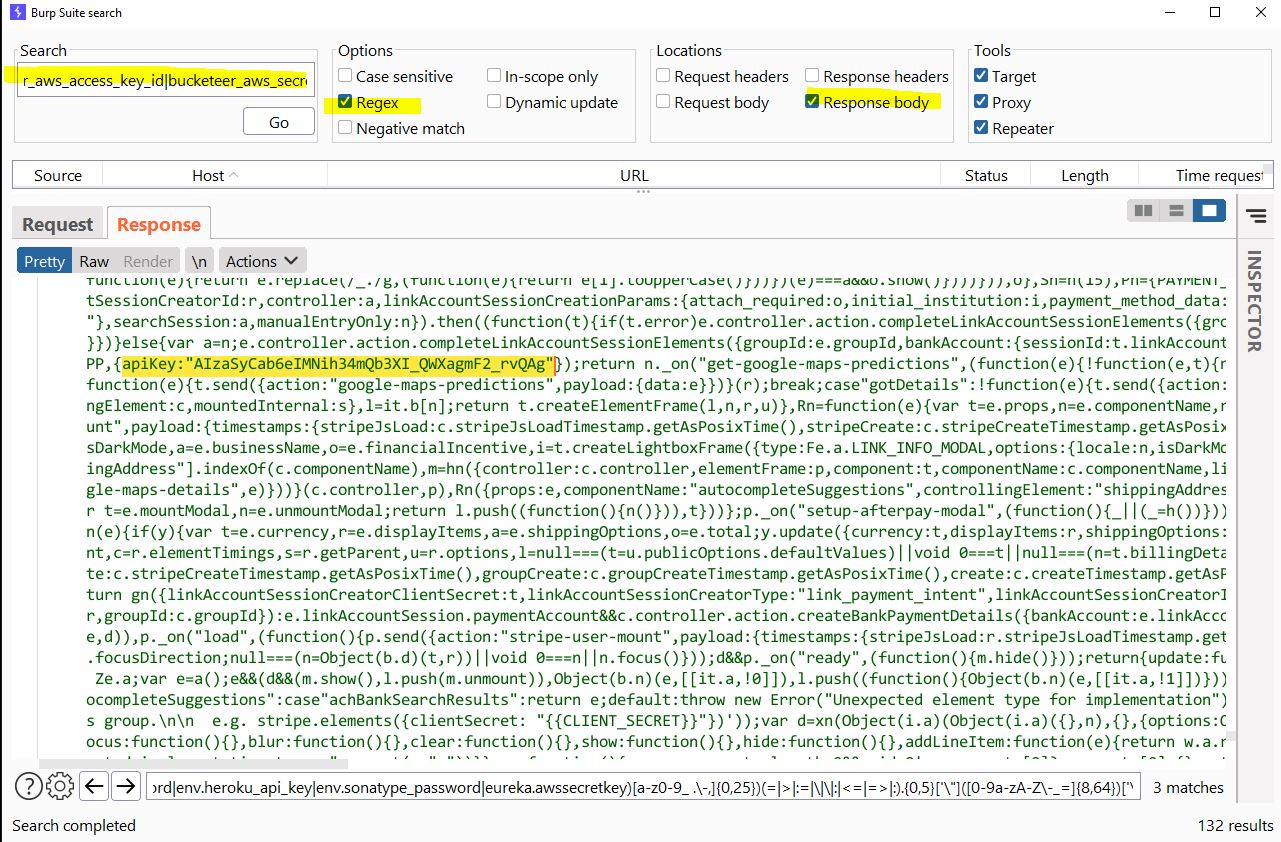 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
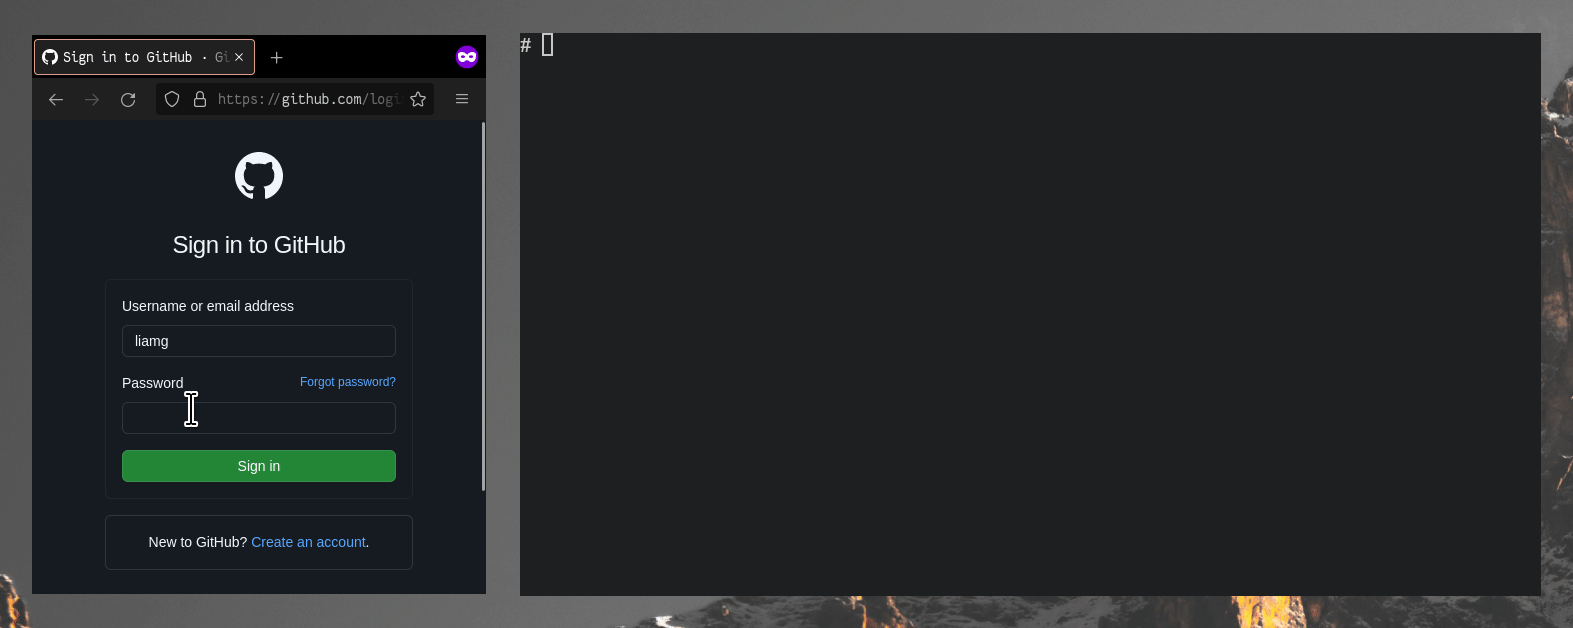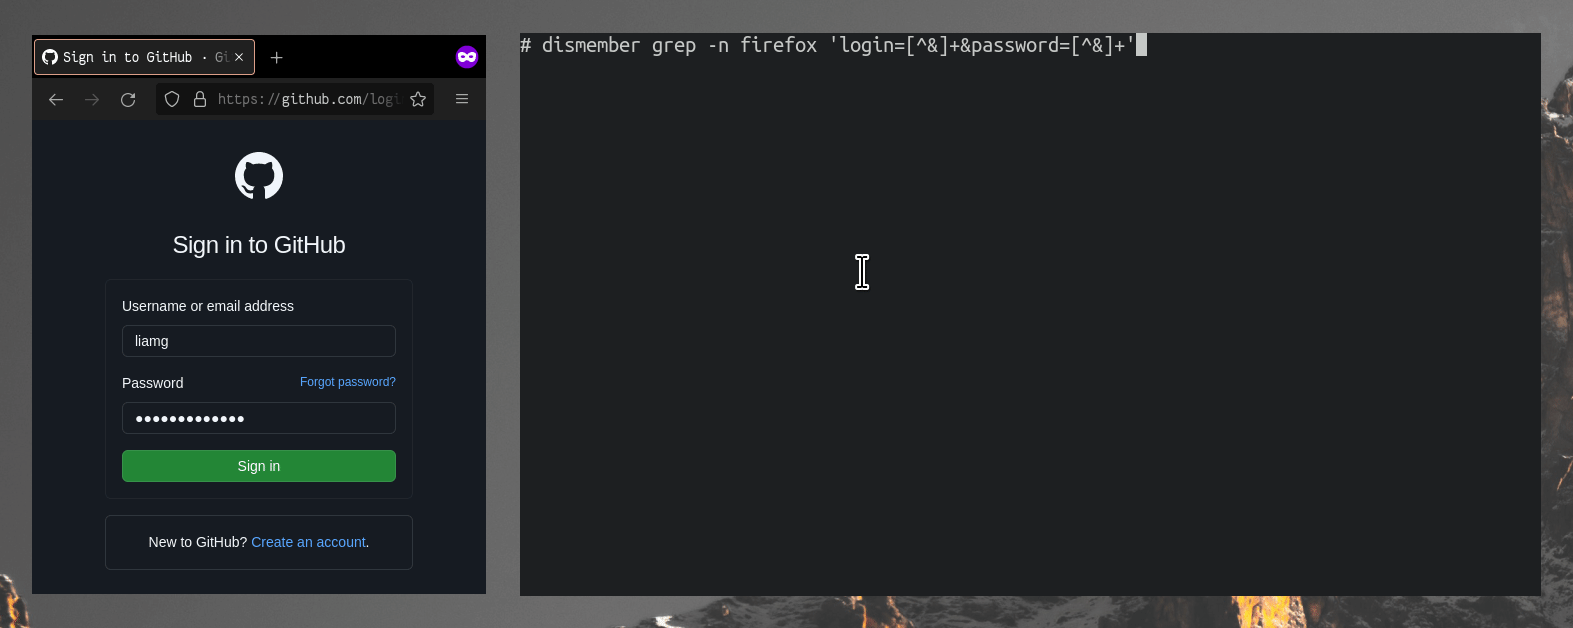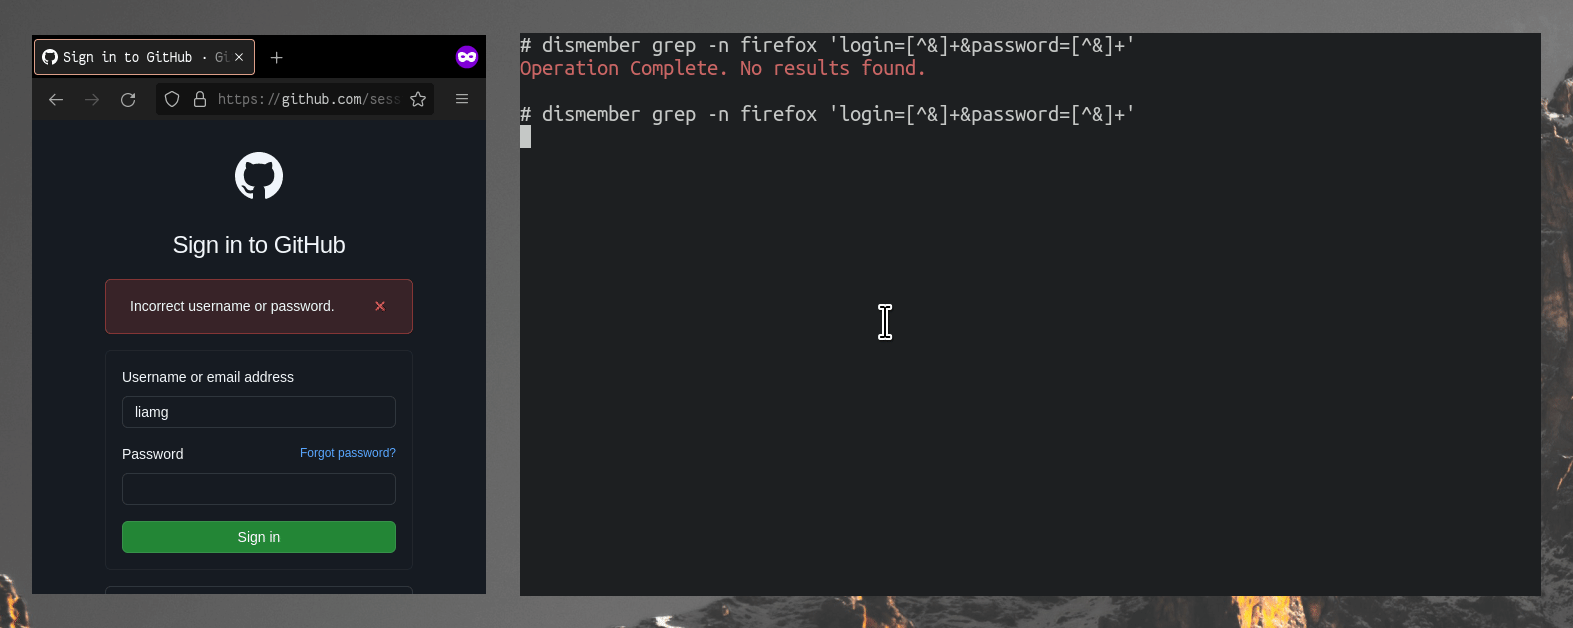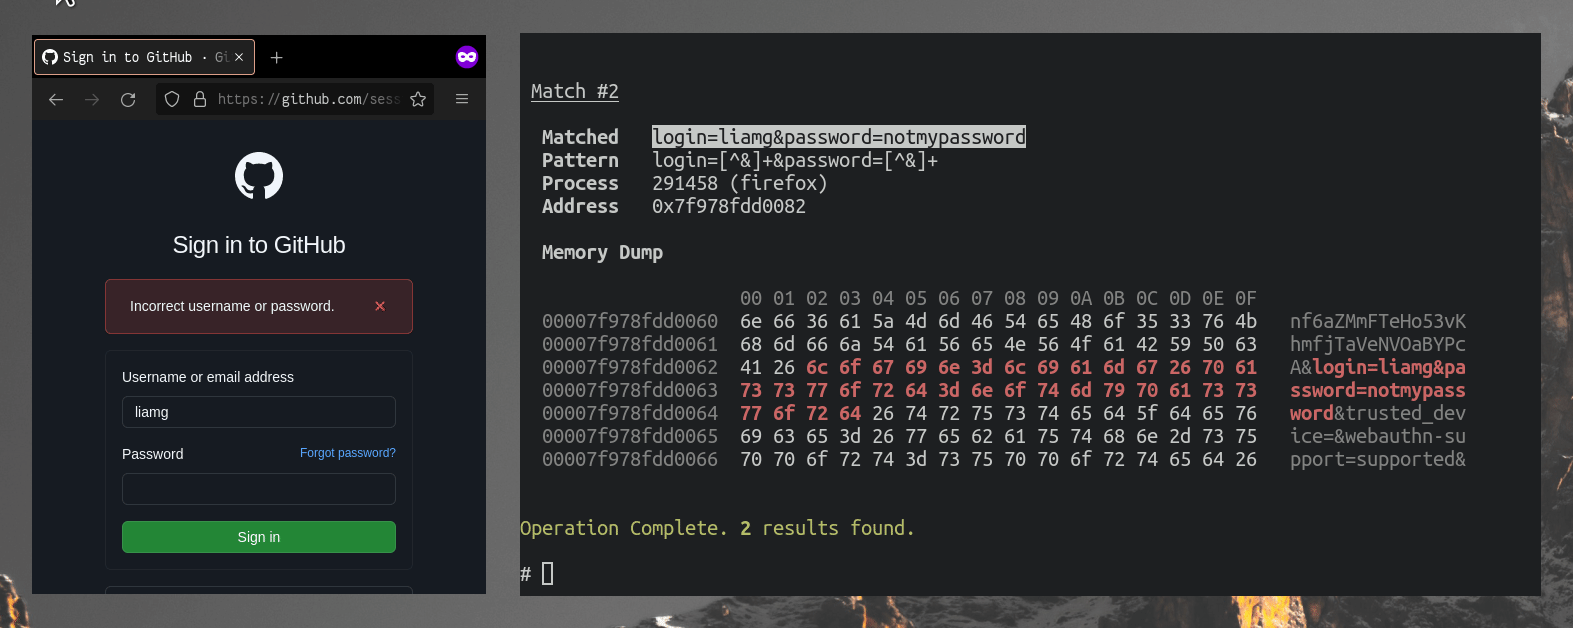 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 randomrobbiebf/cve-2024-0368
Hustle Plugin <= 7.8.3 contains hardcoded HubSpot API credentials in inc/providers/hubspot/hustle-hubspot-api.php
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 centisgood/duo-agentflow-auditor
AI Code Security — four agents that catch what SAST misses in AI-generated code. Built on GitLab Duo Agent Platform.
 simoesctt/ctt-heartbleed-temporal-resonance-memory-leak-exploit-heartbleed-cve-2014-0160
Heartbleed (CVE-2014-0160) was devastating because it leaked adjacent memory. CTT-Heartbleed goes further—it uses 33-layer temporal resonance to map,…
 calusdotai/anticipator
Anticipator is an open-source threat detection platform for multi-agent AI systems.