

PIIHunter
 owasp/piihunter
Scans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
ai-securitydatabase-securitydata-exfiltration+6
2
owasp/piihunterScans PostgreSQL databases and Jira issues for PII using regex, NER/ML, and optional self-hosted LLM detection, with redacted reports and audit…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 molly/gh-dork
Automated GitHub dorking tool that searches user, organization, and repository code for exposed secrets, credentials, and security misconfigurations…
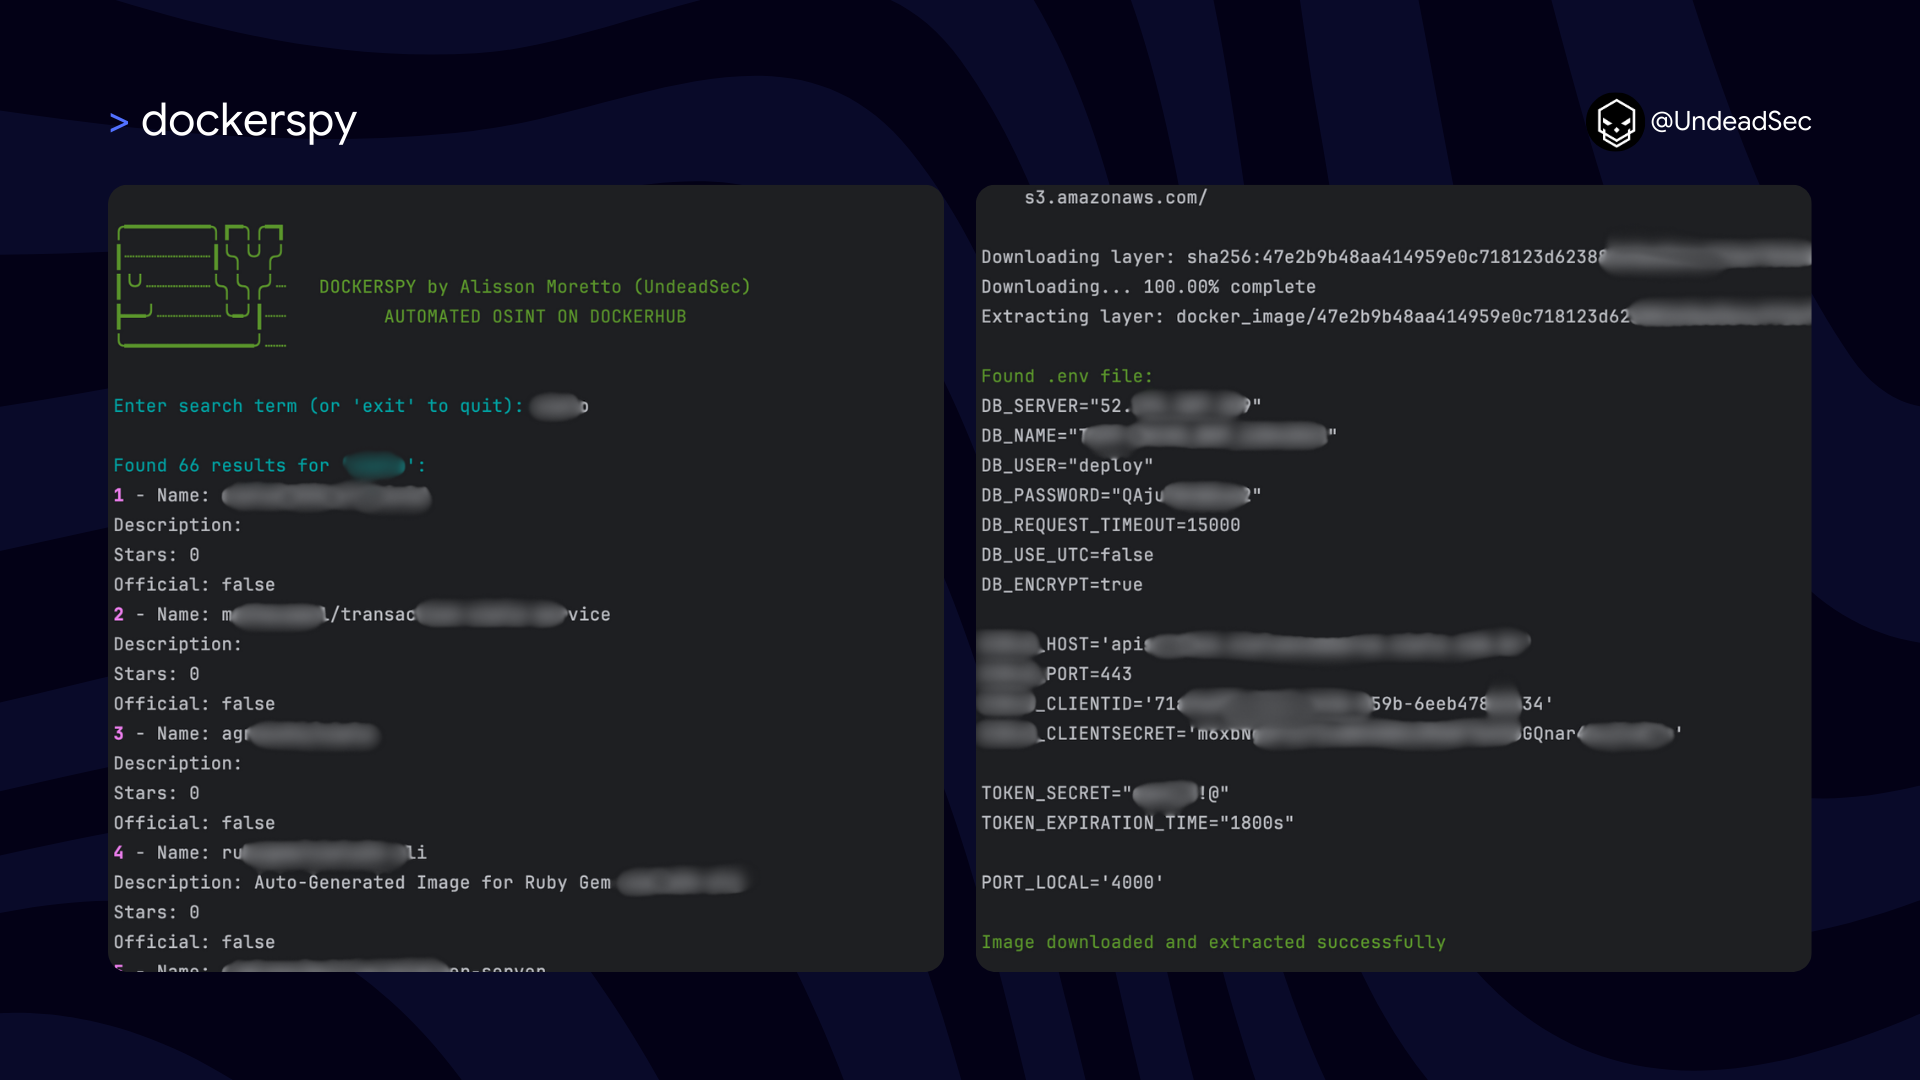 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 crissyfield/troll-a
Extracts secrets (passwords, API keys, tokens) from WARC web archives using Gitleaks rules. Supports HTTP, S3, local files, and compressed archives…
 eilonh/s3crets_scanner
Automated scanner that hunts for secrets (API keys, credentials) accidentally uploaded to public S3 buckets, using truffleHog3 for detection and…
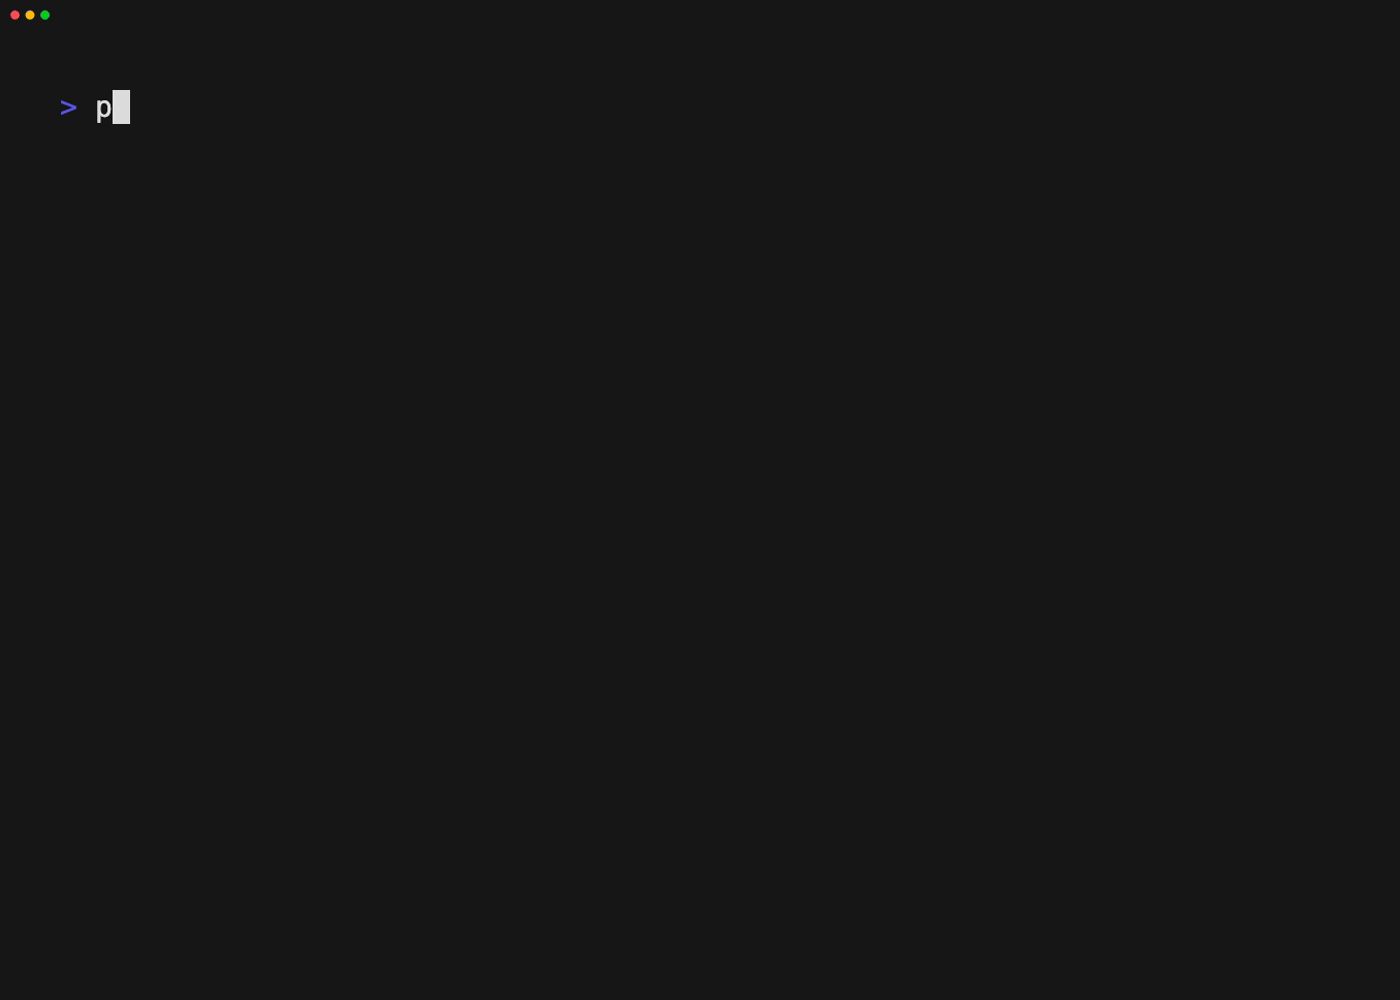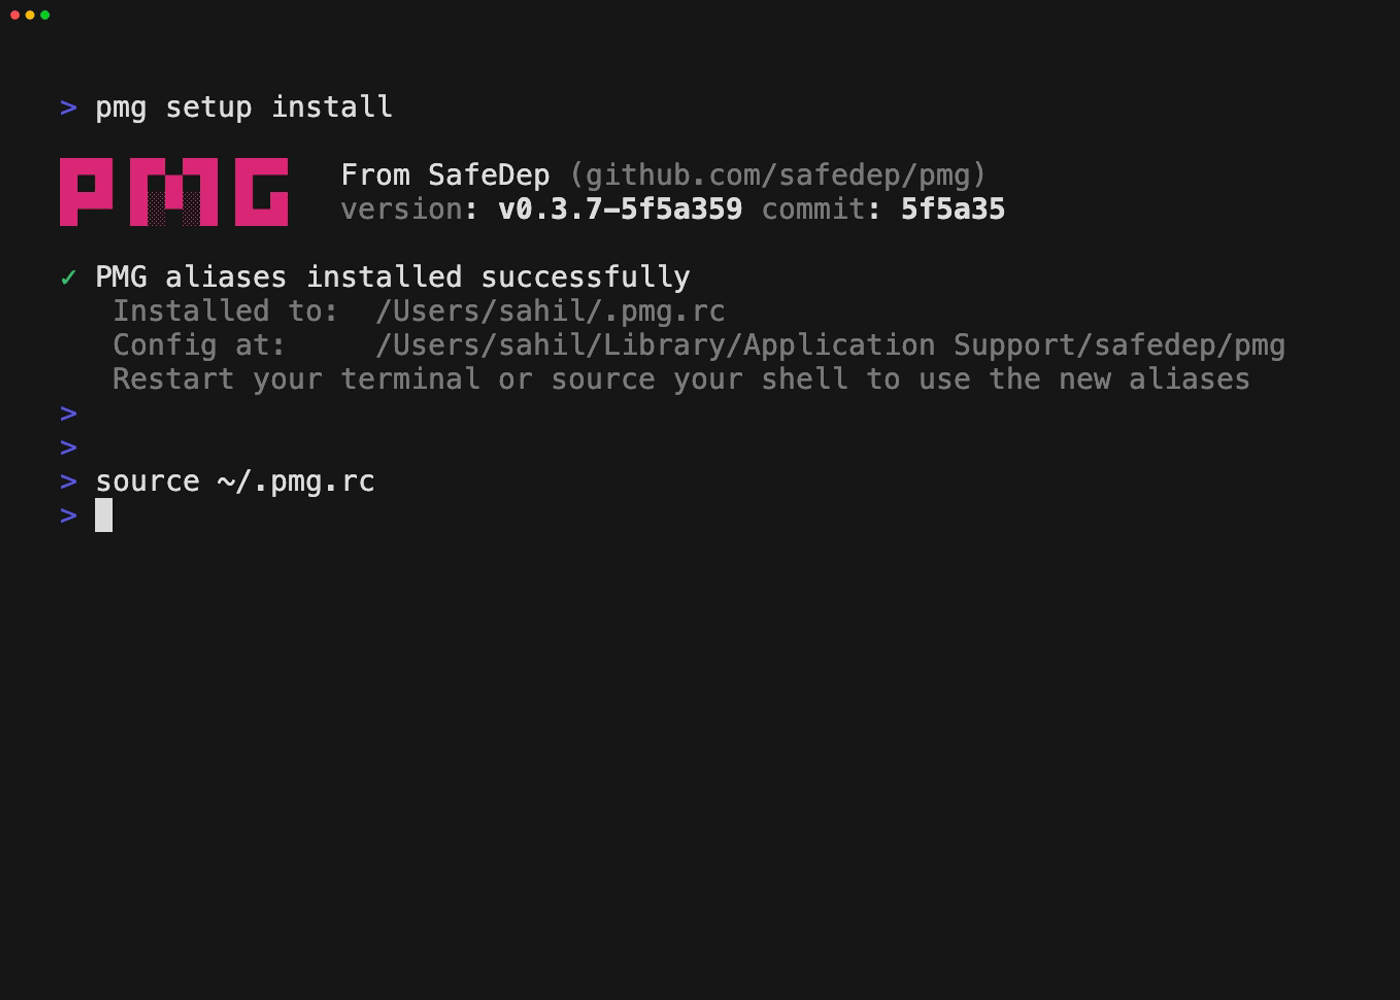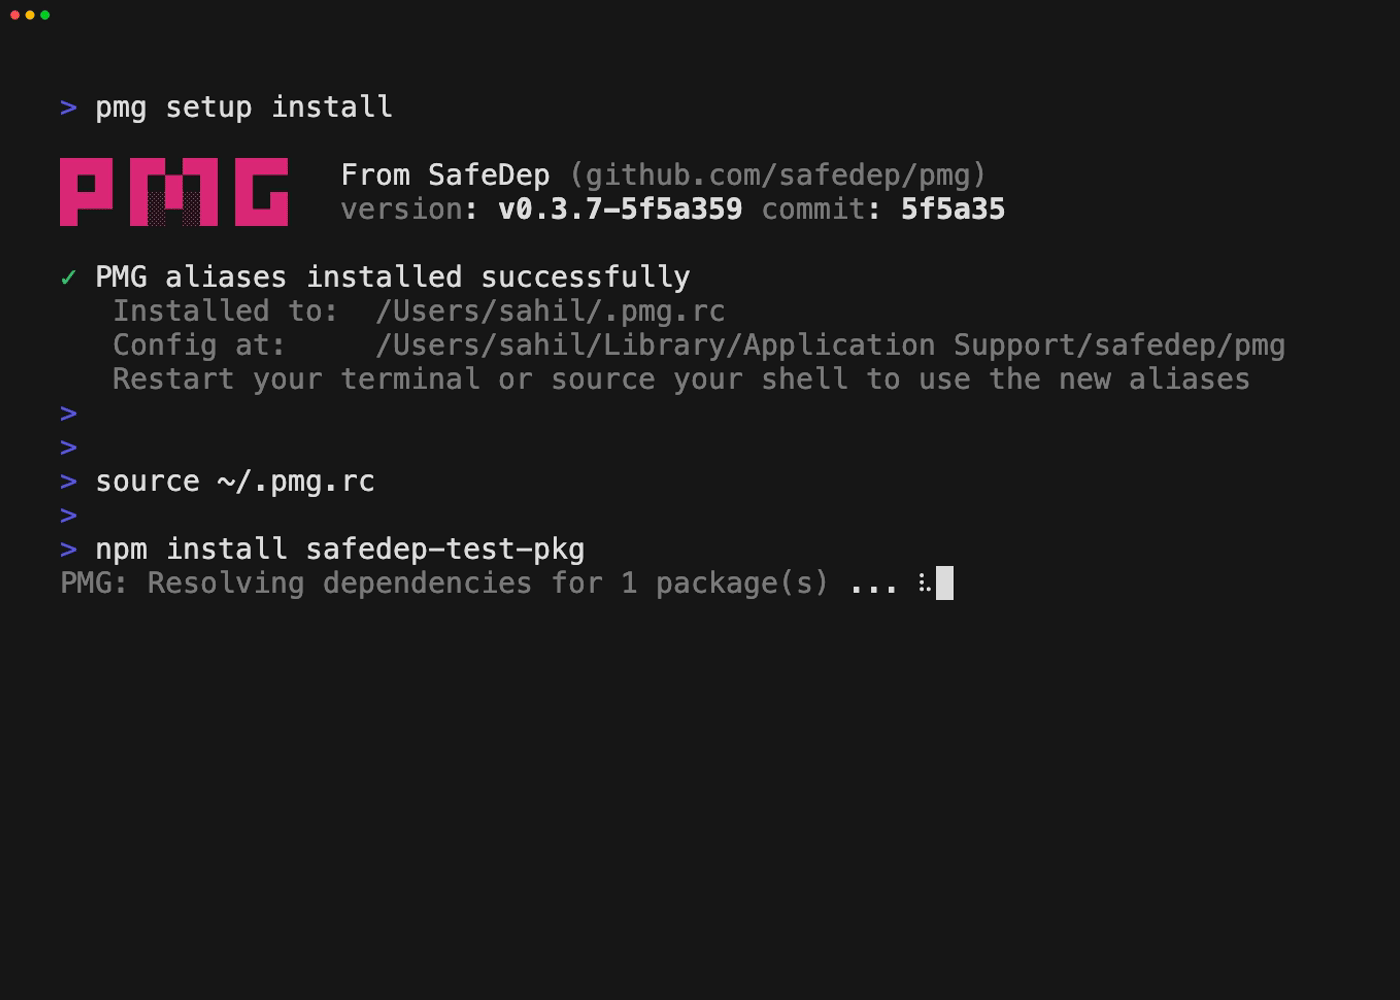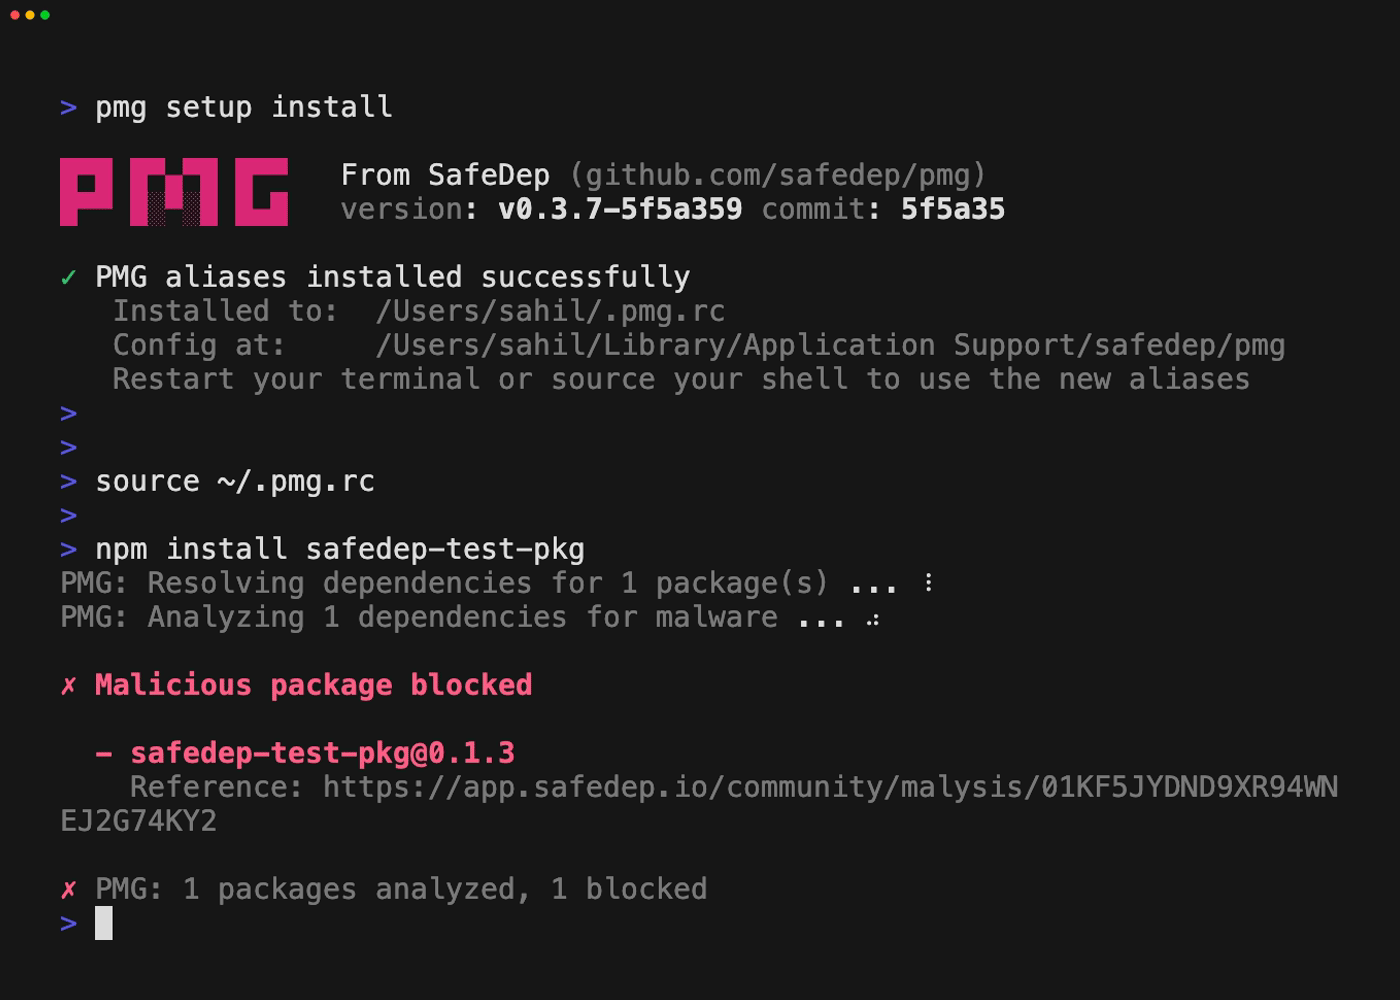 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
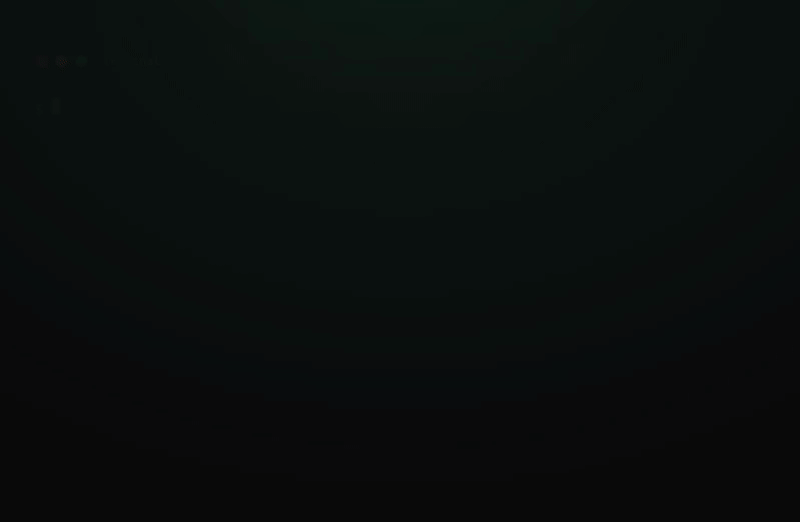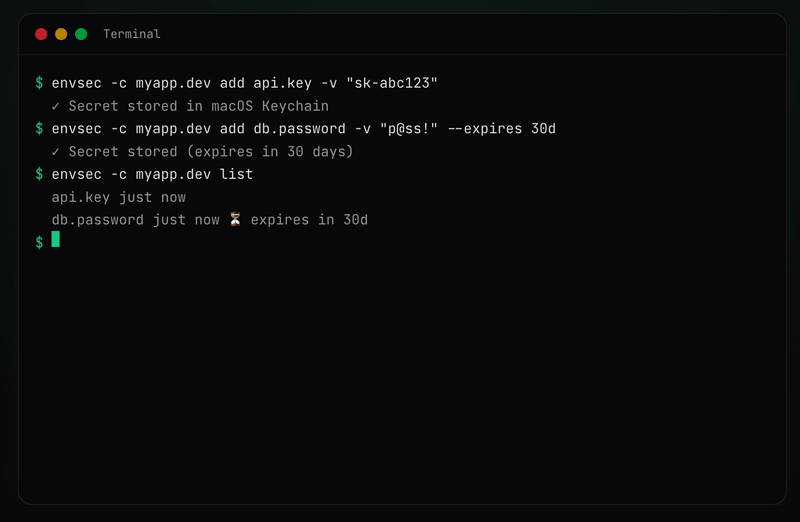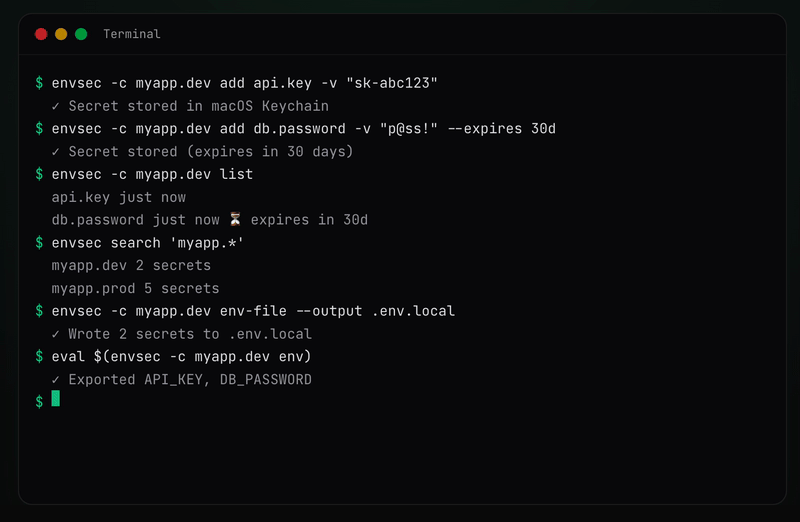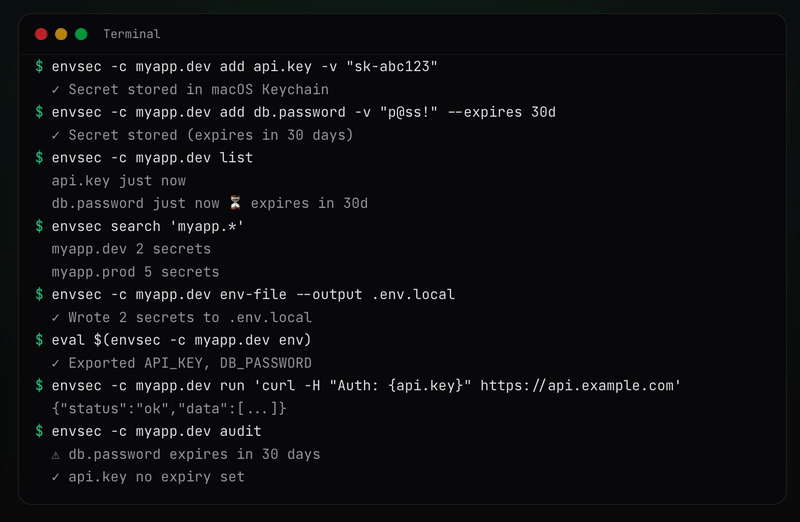 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
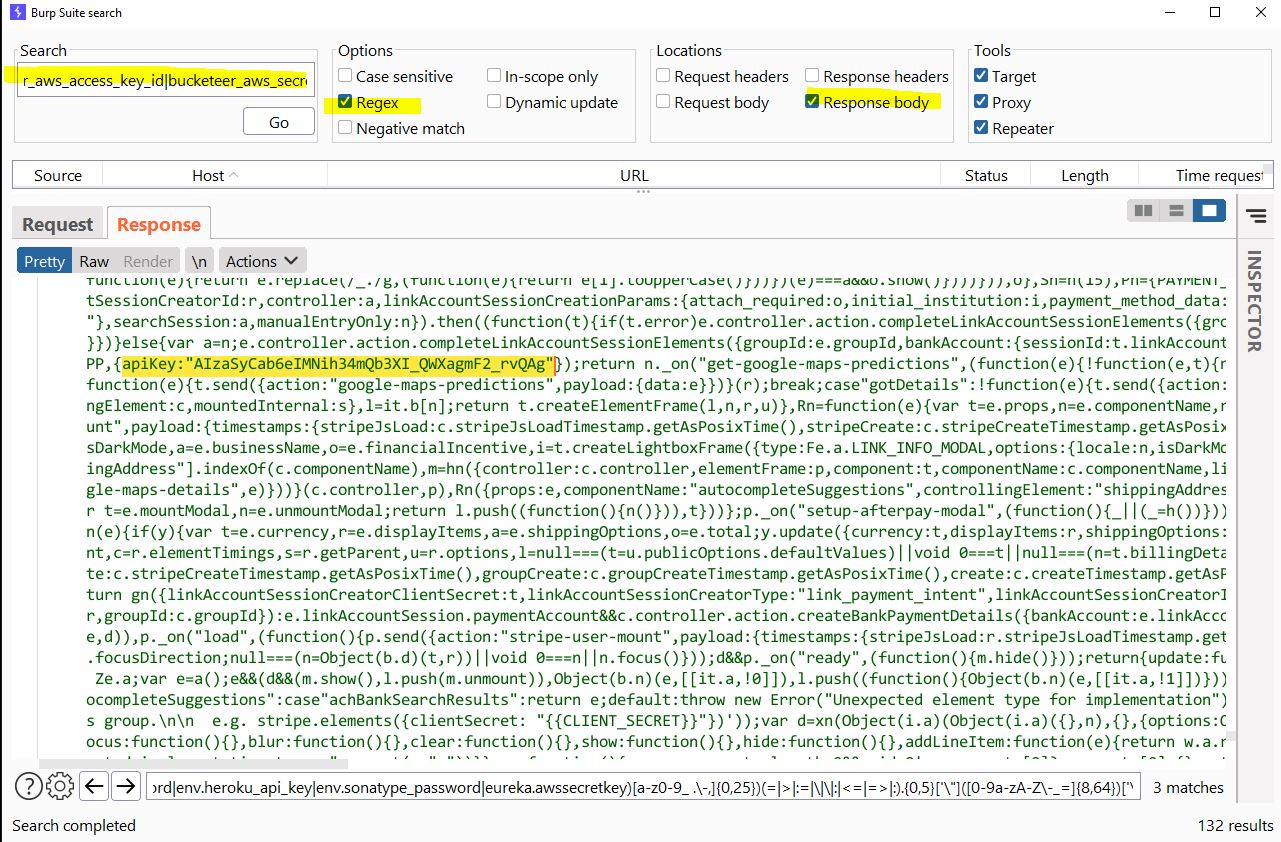 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 ustayready/golddigger
Recursively searches files for sensitive information using customizable regex patterns, designed for penetration testers to rapidly discover secrets…
 raoufmaklouf/jsecret
Fast Go-based static scanner for detecting sensitive data (API keys, tokens, passwords) in JavaScript files and source code using regex patterns.
 mbanyamer/llama-stack-0.4.0rc3-local-cve-2026-25211
Local proof-of-concept scanner that detects plaintext database passwords in llama-stack initialization logs, using regex pattern matching to identify…
 praetorian-inc/gokart
A static analysis tool for securing Go code
 avito-tech/deepsecrets
Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.
 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking