
Archived
CVE-2017-9798
 nitrado/cve-2017-9798
Checks a shared hosting environment for CVE-2017-9798
misconfigurationscripting-automationvulnerability-analysis+1
nitrado/cve-2017-9798Checks a shared hosting environment for CVE-2017-9798
 infiniroot/nginx-mitigate-log4shell
Mitigate log4shell (CVE-2021-44228) vulnerability attacks using Nginx LUA script
 alexandreheroux/fix-cve-2021-44228
Apply class remove process from ear/war/jar/zip archive, see https://logging.apache.org/log4j/2.x/
 hazemkya/cve-2024-3094-checker
Bash script to detect and remediate CVE-2024-3094, a critical supply-chain vulnerability in the XZ Utils library, with automatic safe version…
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
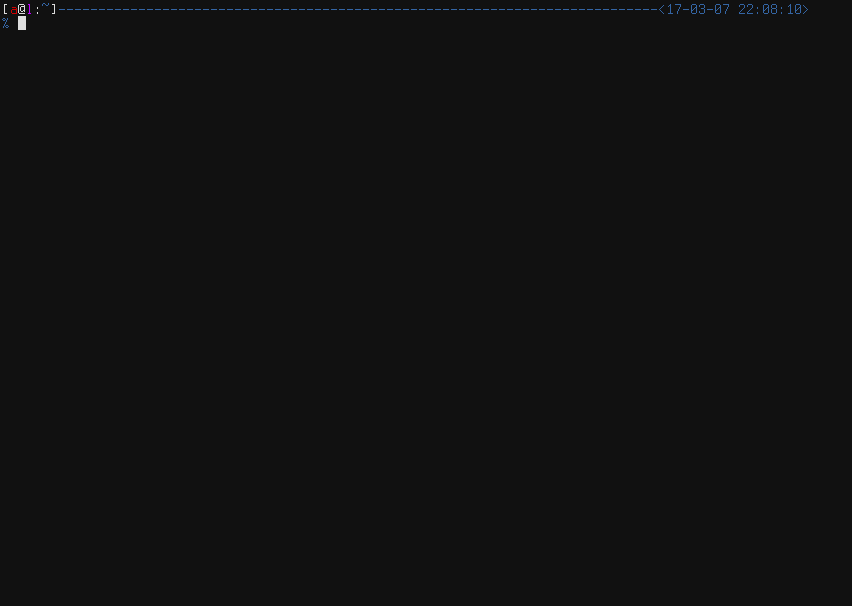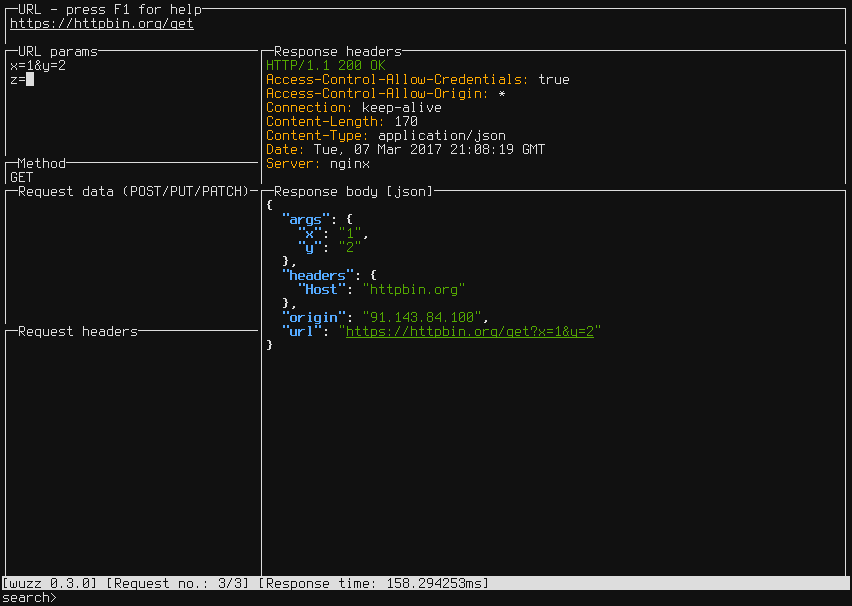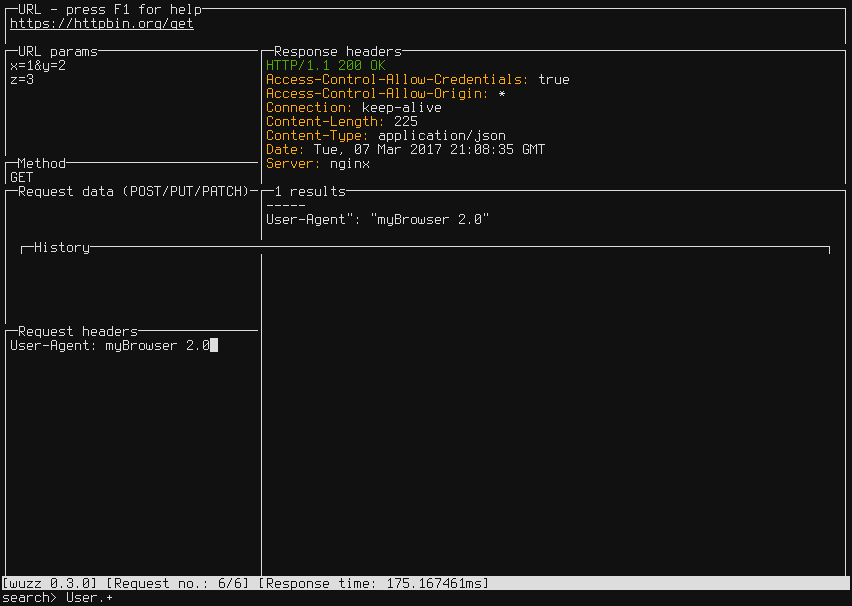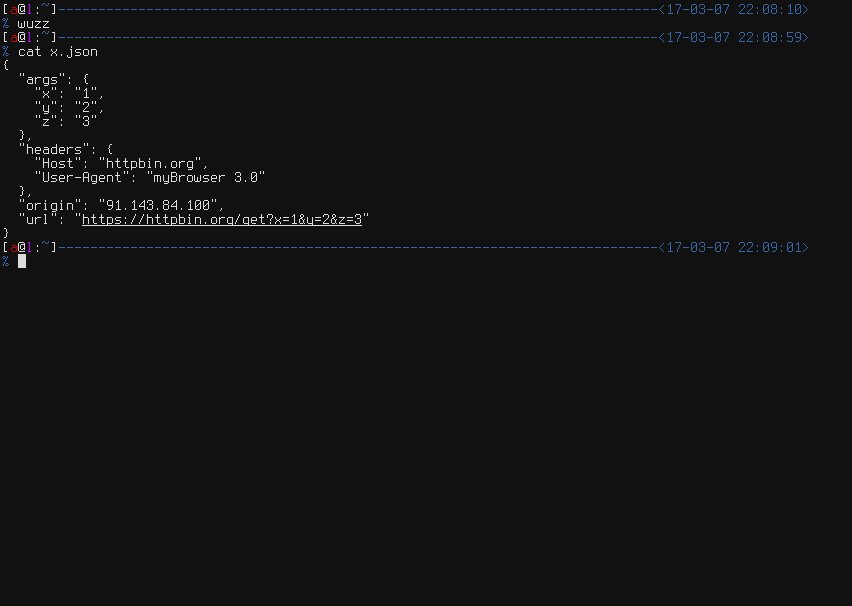 asciimoo/wuzz
Interactive cli tool for HTTP inspection
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
 mrgoofydev/zx-ddos
Python-based DDoS stress testing tool for educational and authorized network security evaluation, supporting configurable workers and request counts.
 tw1sm/badger-builder
badger-builder is an AI-assisted tool for generating dynamic Brute Ratel C4 profiles

 tapanmeena/azpim
A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.
 gmh5225/f31
Tool for hiding Kali Linux on the network
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 gmh5225/domain-enumeration-sicarius
Another tool for subdomain enumeration with some magics 🧙🏻♂️
 elsanose01/cve-2021-43798-grafana-path-traversal-tester
Automated path traversal testing tool for Grafana plugin endpoints using curl and Bash.