

OpenHunterAI
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
ai-securityapi-securityapi-security-testing+9
324
lumoslab-innovation/openhunteraiLocal-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 ice-wzl/hacknetics
Contained is all my reference material for my OSCP / Red Teaming. Designed to be a one stop shop for code, guides, command syntax, and high level…
 redsiege/aggressorassessor
Aggressor scripts for phases of a pen test or red team assessment
 lorentzenman/sheepl
Emulates realistic user behavior in Active Directory lab environments for red and blue team tradecraft development. Generates random benign user…
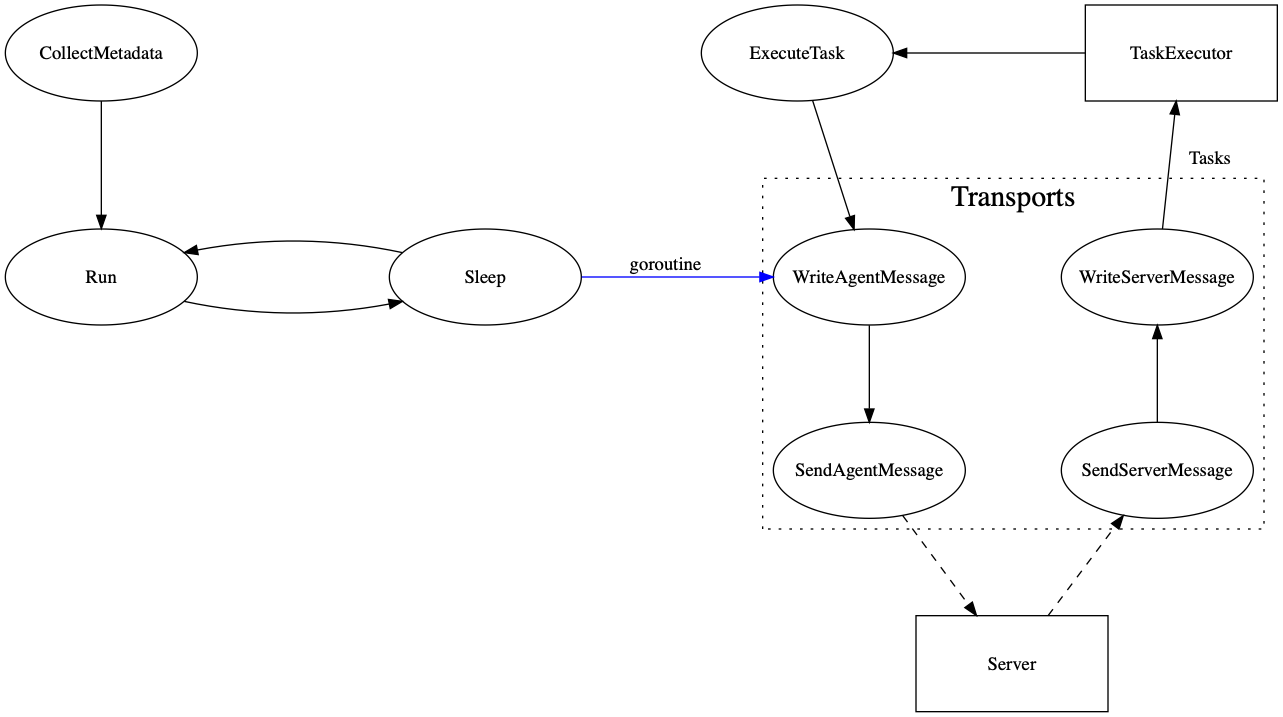 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 cwolff411/powerob
An on-the-fly Powershell script obfuscator meant for red team engagements. Built out of necessity.
 1n3/powerexfil
A collection of data exfiltration scripts for Red Team assessments.
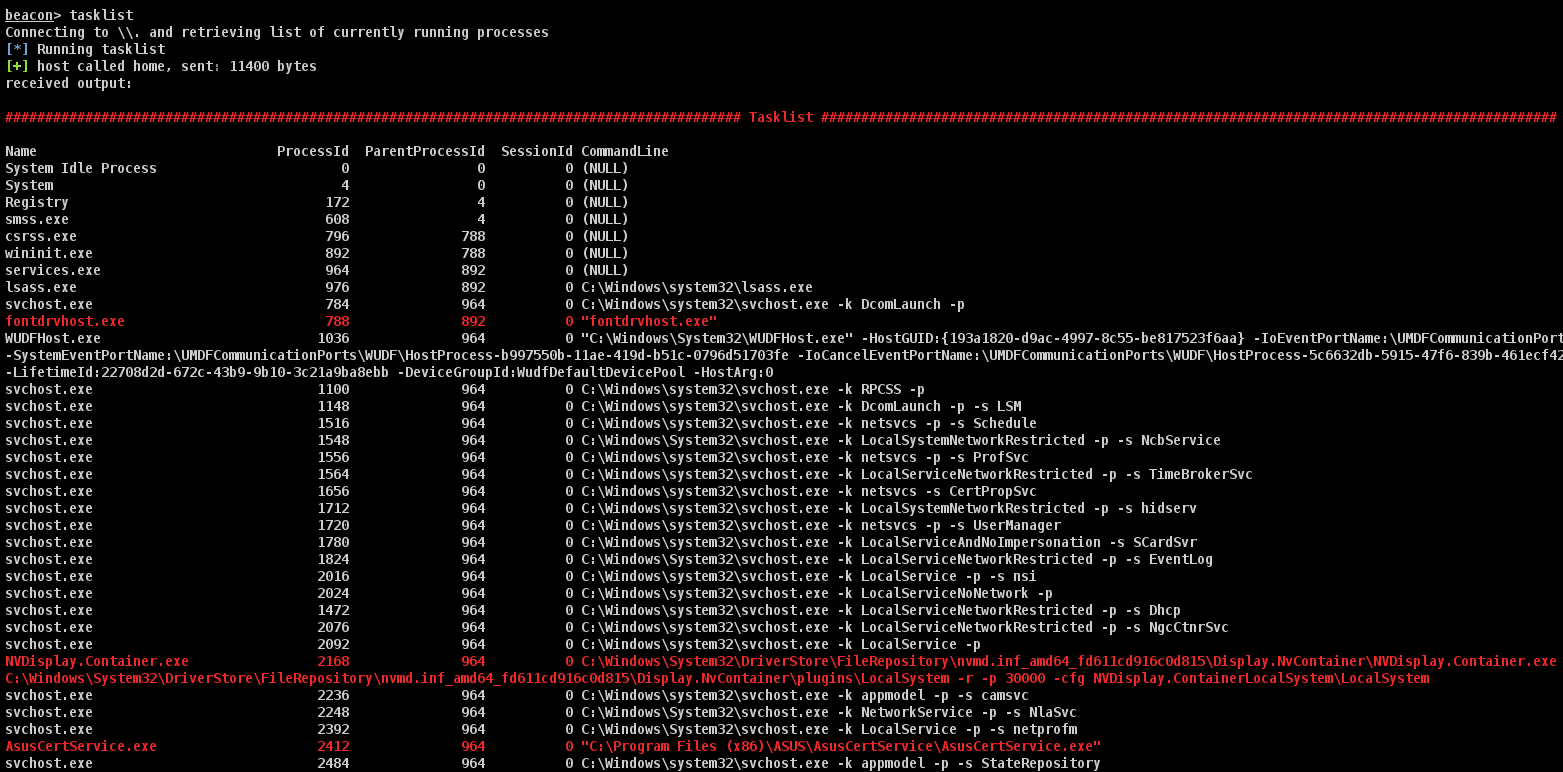 octoberfest7/cohab_processes
A small Aggressor script to help Red Teams identify foreign processes on a host machine
 blacksnufkin/pt-toolkit
Exploits Scripts and other tools that are useful during Penetration-Testing or Red Team engagement
 lucab85/log4j-cve-2021-44228
Ansible playbook automating Red Hat's Log4j detector script to scan Linux hosts for CVE-2021-44228 (Log4Shell) vulnerability with GPG verification.
 tevora-threat/rt_redirectors
Ansible role to configure redirectors for red team C2
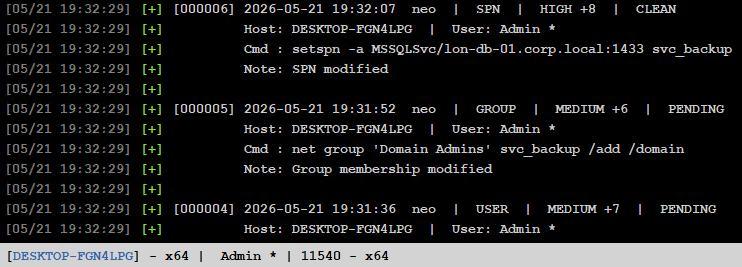 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 niccox/patch-openssl-cve-2014-0291_cve-2015-0204
Ansible playbook to patch OpenSSL against CVE-2014-0291 and CVE-2015-0204 on Red Hat family servers, with automated service restart and verification.
 swimlane/atomic-operator
A Python package is used to execute Atomic Red Team tests (Atomics) across multiple operating system environments.
 bishopfox/sliver
Adversary Emulation Framework
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.