CVE-2025-1974_IngressNightmare_PoC

Automates sending JSON payloads to multiple IPs via curl to test for CVE-2025-1974 (IngressNightmare), classifying responses and generating XML…

Automates sending JSON payloads to multiple IPs via curl to test for CVE-2025-1974 (IngressNightmare), classifying responses and generating XML…

Command-line packet analyzer for network monitoring and data acquisition, capturing and displaying network traffic for troubleshooting and security…

Collection of 60 Python-based DDoS attack tools for network stress testing and security assessment, featuring automated packet flooding scripts to…

Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…

scripts associate with bourne shell EVN function parsing vulnerability CVE-2014-6271

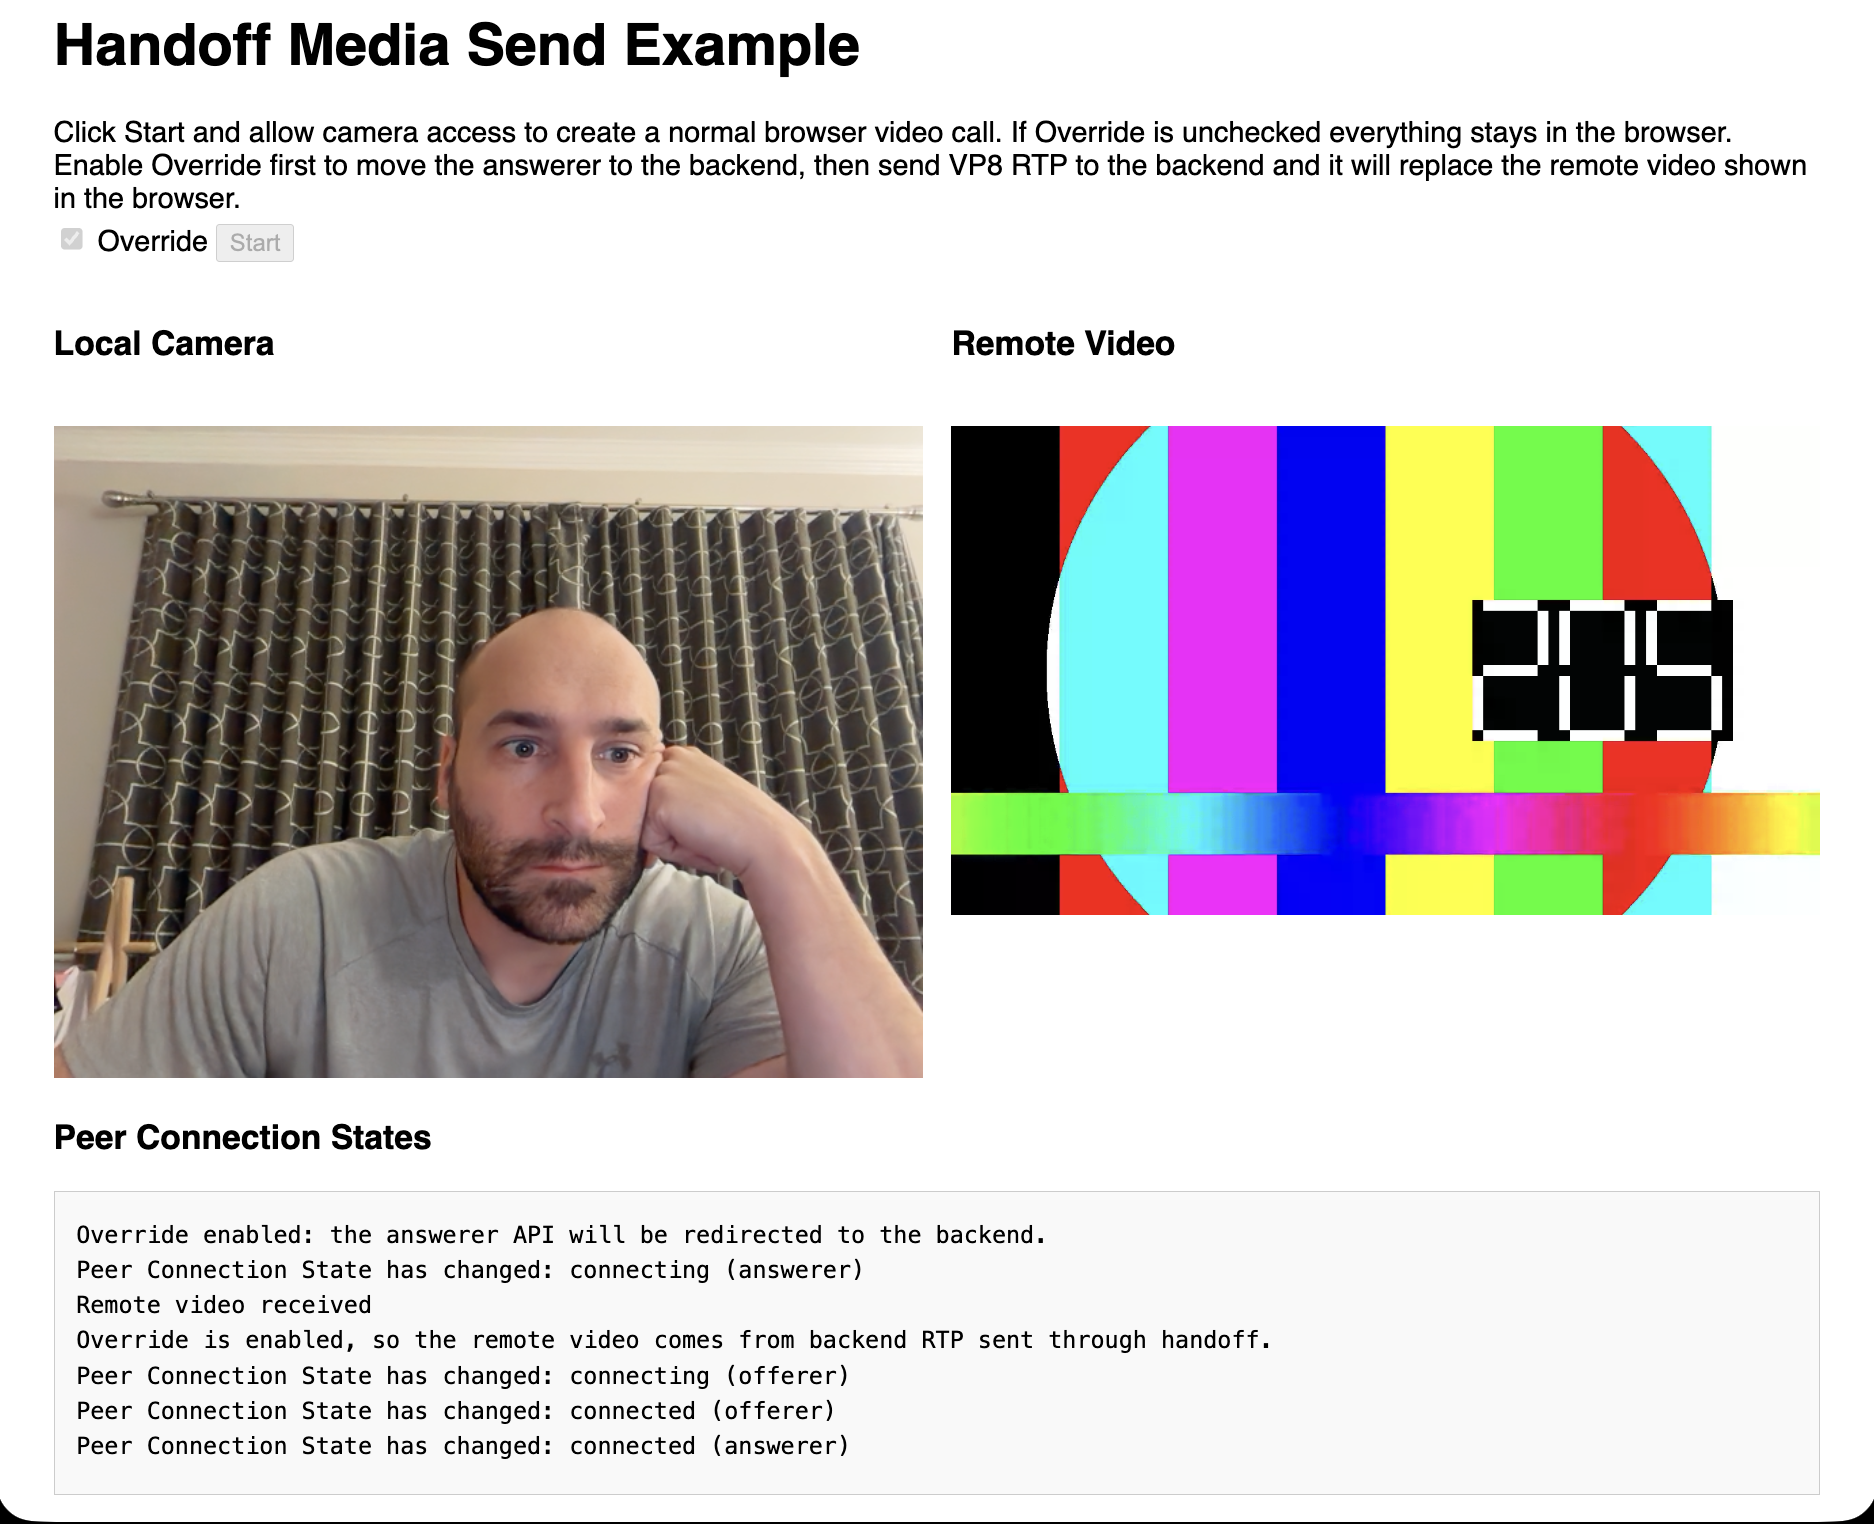
Start WebRTC in the browser—run it somewhere else

Easily turn single threaded command line applications into a fast, multi-threaded application with CIDR and glob support.

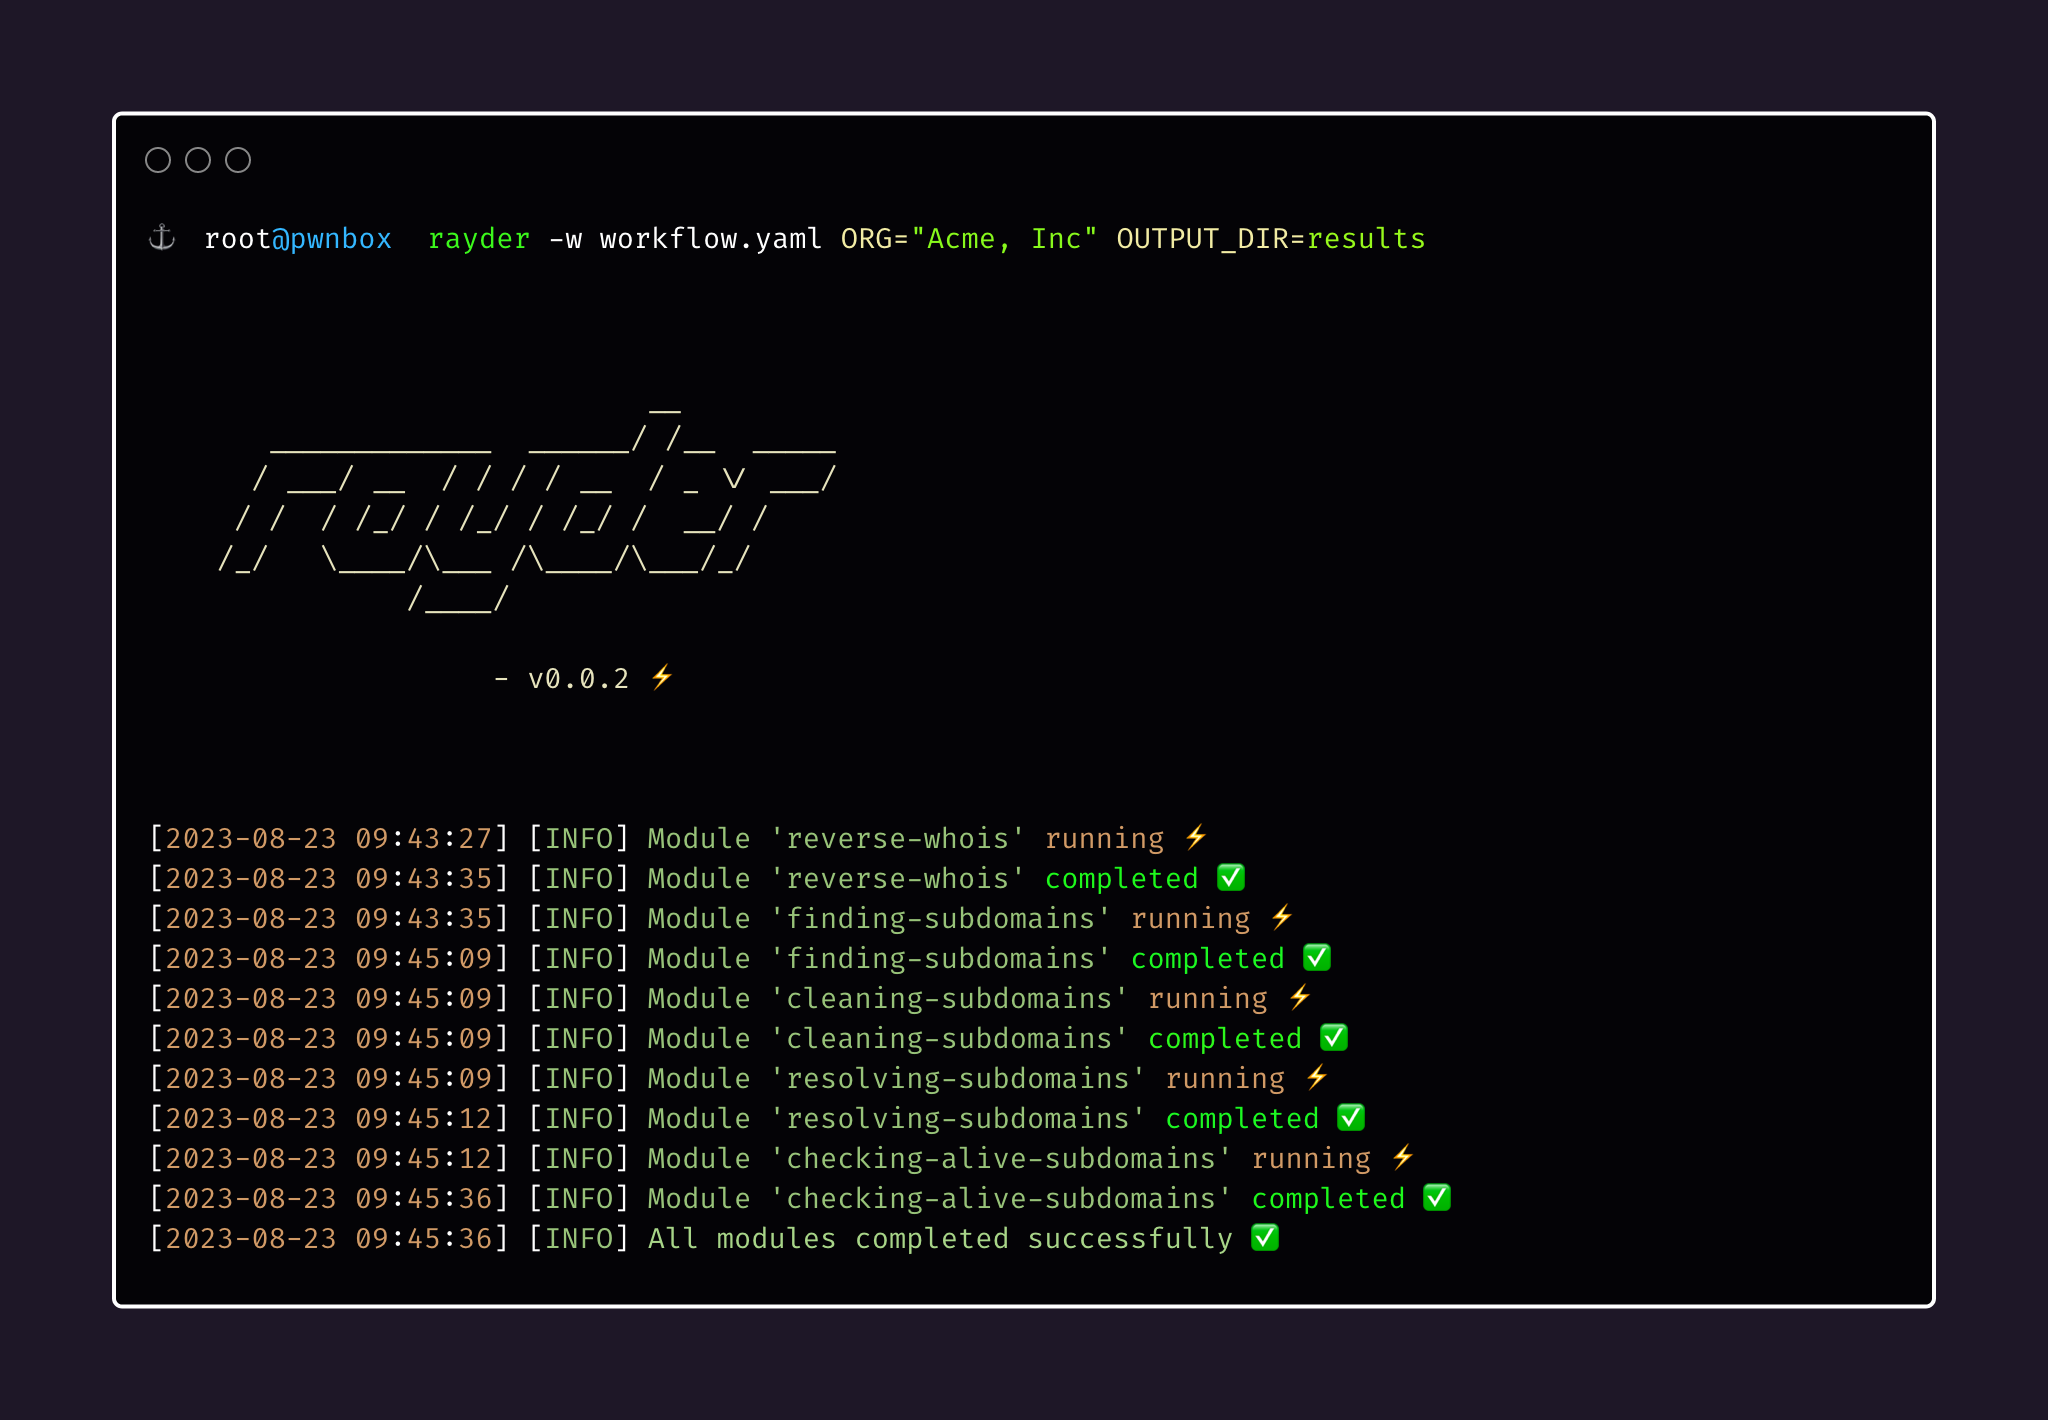
A lightweight tool for orchestrating and organizing your bug hunting recon / pentesting command-line workflows

BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…

Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…

Automates downloading and running an Nmap NSE script to scan hosts for CVE-2020-3452 vulnerability, using a list of target hosts.

SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。

Simple Automation script for juniper cve-2023-36845

Simple script realizado en bash, para revisión de múltiples hosts para CVE-2021-41773 (Apache)