

resterm
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
api-security-testingcloud-securitydevsecops+3
1.9k
unkn0wn-root/restermTerminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 tomnomnom/anew
A tool for adding new lines to files, skipping duplicates
 postmodern/ruby-nmap
A Ruby interface to nmap, the exploration tool and security / port scanner. Allows automating nmap and parsing nmap XML files.
 zeroecco/holos
Declarative KVM/QEMU VM orchestration tool using YAML compose files. Manages multi-VM stacks with cloud-init, SSH, PCI passthrough, and image…
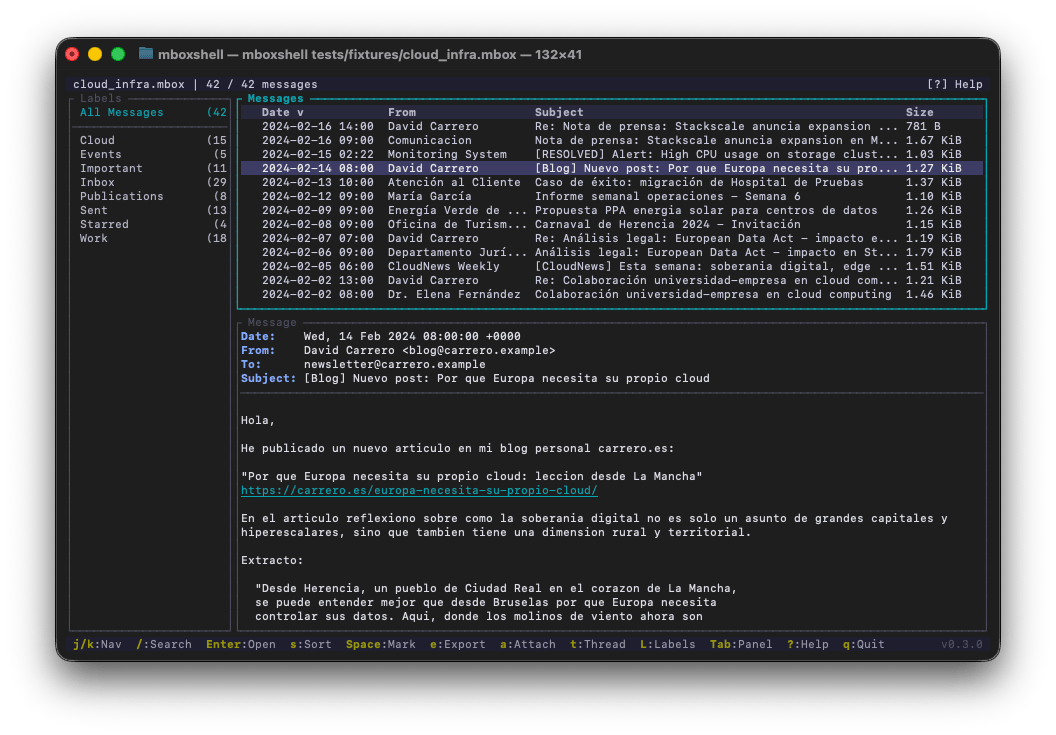 dcarrero/mboxshell
mboxShell. Fast terminal viewer for MBOX files of any size. Open, search and export emails from Gmail Takeout backups (50GB+) without loading them…
 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 guettli/fix-cve-2020-15228
Python script that automatically patches GitHub Actions workflow files to replace deprecated and insecure ::set-env and ::add-path commands with the…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 pmontesd/log4j-cve-2021-44228
Very simple Ansible playbook that scan filesystem for JAR files vulnerable to Log4Shell
 elevenpaths/metashield-clean-up-sdk-python
Python SDK for removing hidden metadata from files (PDF, Office, images) to protect privacy and prevent data leakage via automated cleaning workflows.
 a-real-virus/stealthcrypter
AES-256 file and directory encryption tool with interactive CLI, progress bar, and optional secure deletion of originals. Supports large files and…
 kaysec/hybrid-submit
A script that automatically submits files to Hybrid Analysis (API)
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…
 sfitpro/cve-2017-8529
My CVE-2017-8529 files
 intel-xeon/cve-2021-44228---detection-with-powershell
PowerShell-based scanner to detect Log4j CVE-2021-44228 vulnerability by searching directories and log files for exploitation indicators.
 winkler-winsen/scan_ghostscript
Scan for GhostScript files affected to CVE-2023-36664
 winkler-winsen/scan_winrar
Scan for WinRAR files affected to CVE-2023-40477
 dansi/powershell-log4j-scanner
can find, analyse and patch Log4J files because of CVE-2021-44228, CVE-2021-45046