
hackersh
 ikotler/hackersh
A free and open source command-line shell and scripting language designed especially for security testing
penetration-testingpenetration-testing-frameworksscripting-automation+3
127
ikotler/hackershA free and open source command-line shell and scripting language designed especially for security testing
 quaerendir/cve-2026-98432-audit
Read-only bash audit script that triages CVE-2026-98432, a Linux kernel IPv4 TCP use-after-free, by checking kernel changelogs, distro fix matrices,…
 bitwire-it/probe-cve-2026-98432
Local kernel version checker, remote MPTCP capability probe, and interactive scan-and-probe CLI for assessing exposure to the Linux kernel IPv4 TCP…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
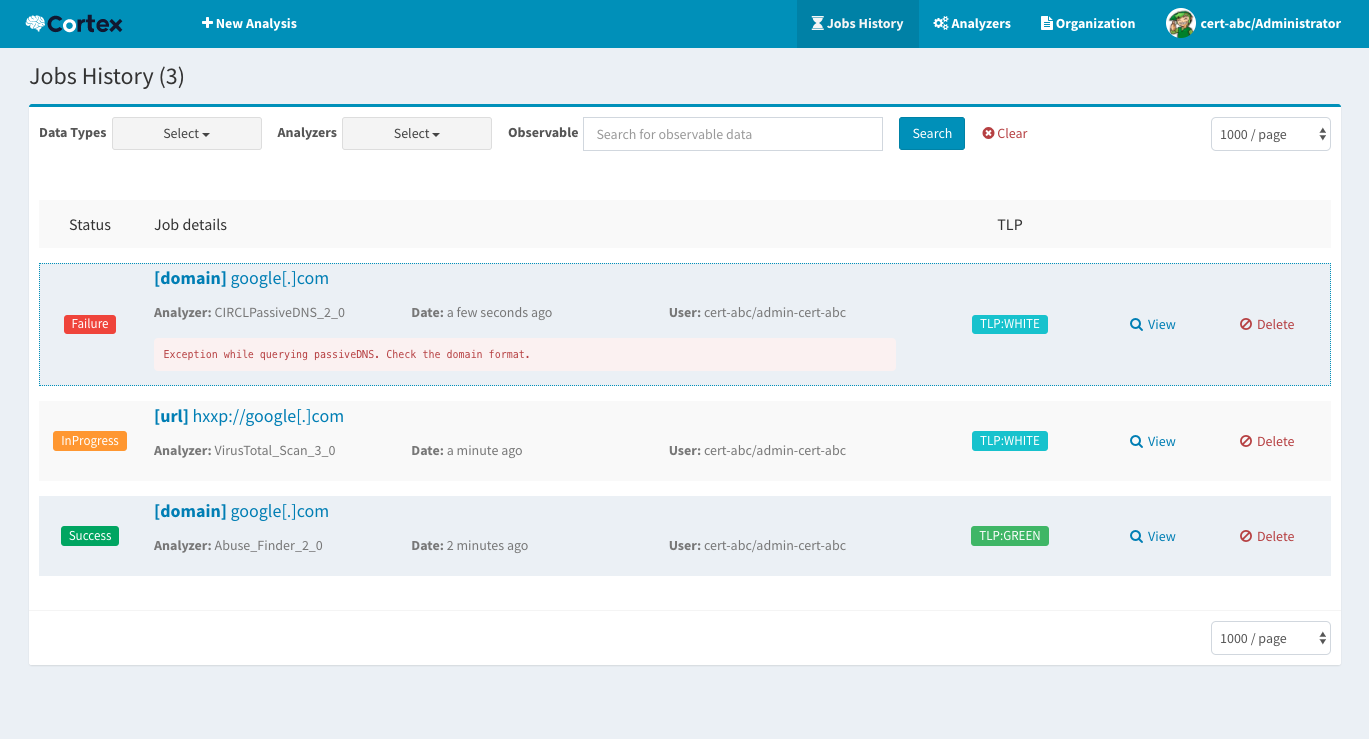 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 postmodern/ruby-nmap
A Ruby interface to nmap, the exploration tool and security / port scanner. Allows automating nmap and parsing nmap XML files.
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
 bankkroll/quickcheck-cve-2025-55182-react-and-cve-2025-66478-next.js
Script to quick check CVE-2025-55182 (React) and CVE-2025-66478 (Next.js) - Critical unauthenticated RCE vulnerabilities in the React Server…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 gmh5225/ollama-hunter
Scans Shodan for publicly exposed Ollama and llama.cpp servers, enumerating hosts, locations, and available models for security research.
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
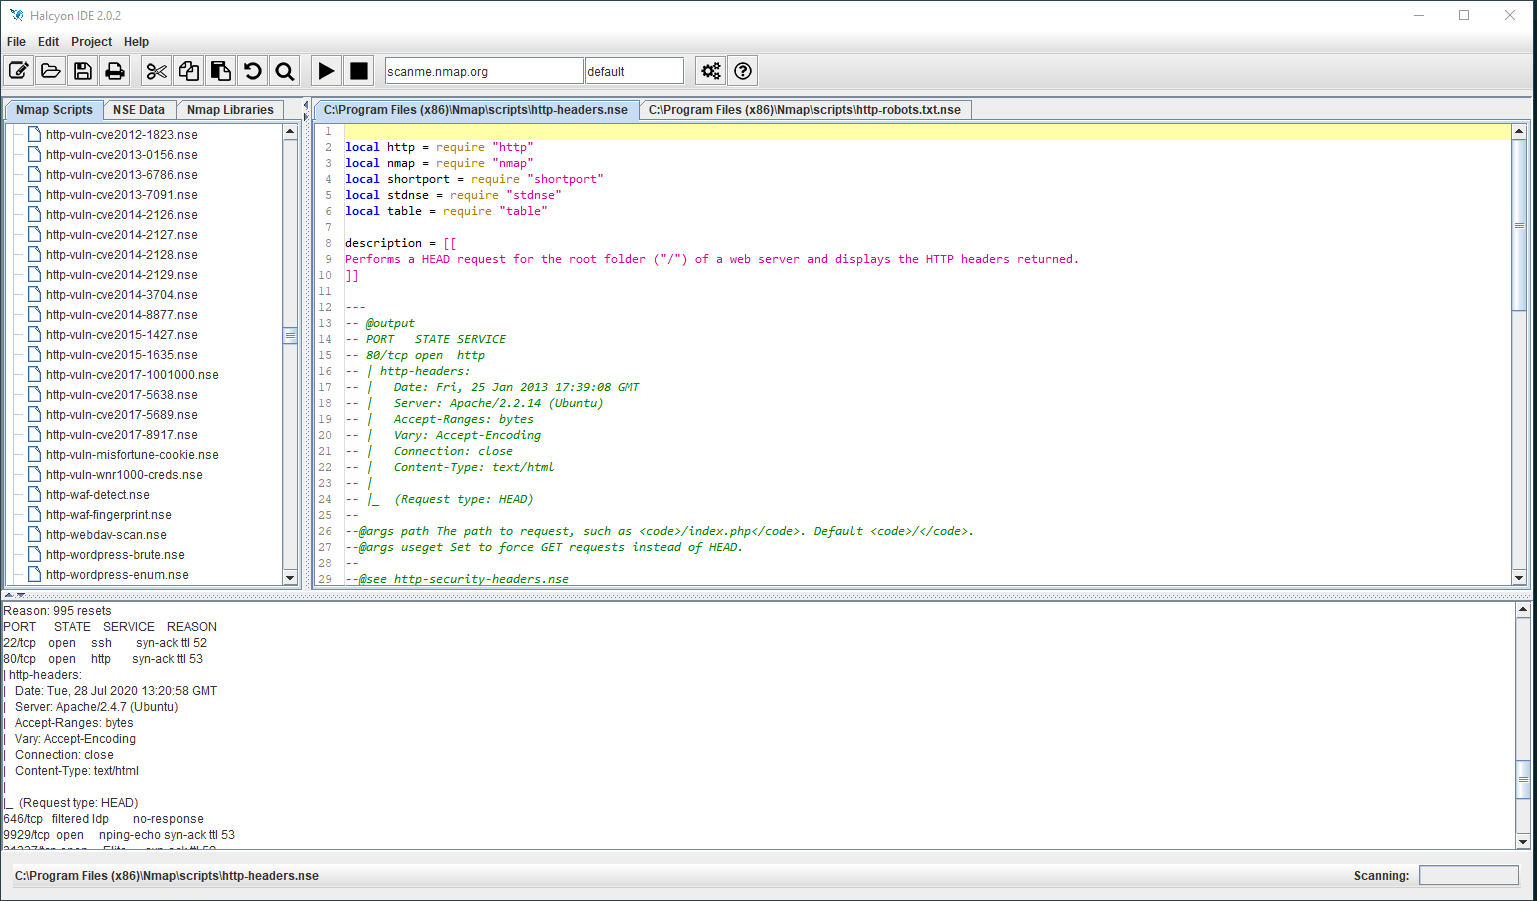 s4n7h0/halcyon-ide
First IDE for Nmap Script (NSE) Development.
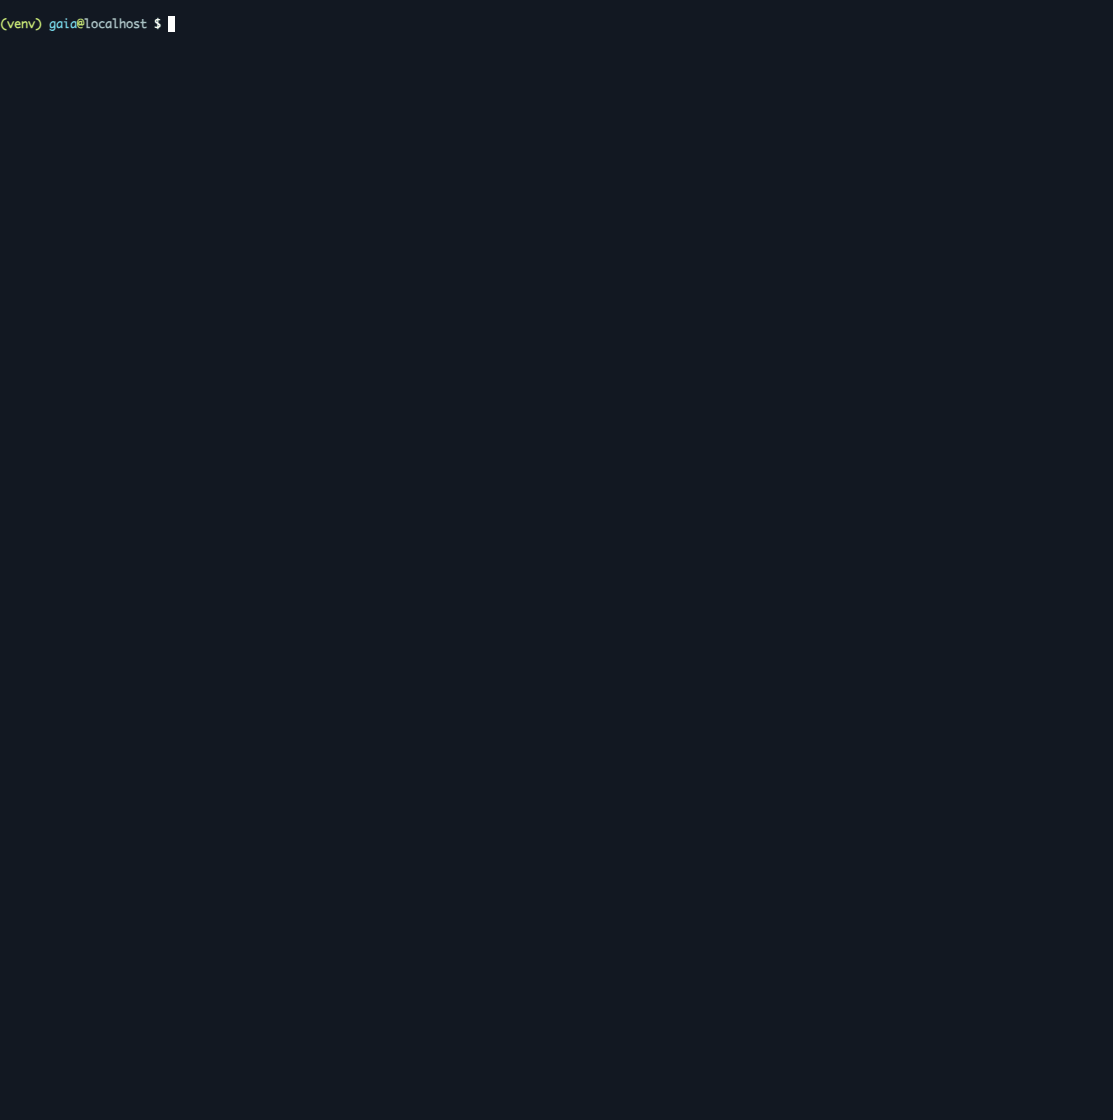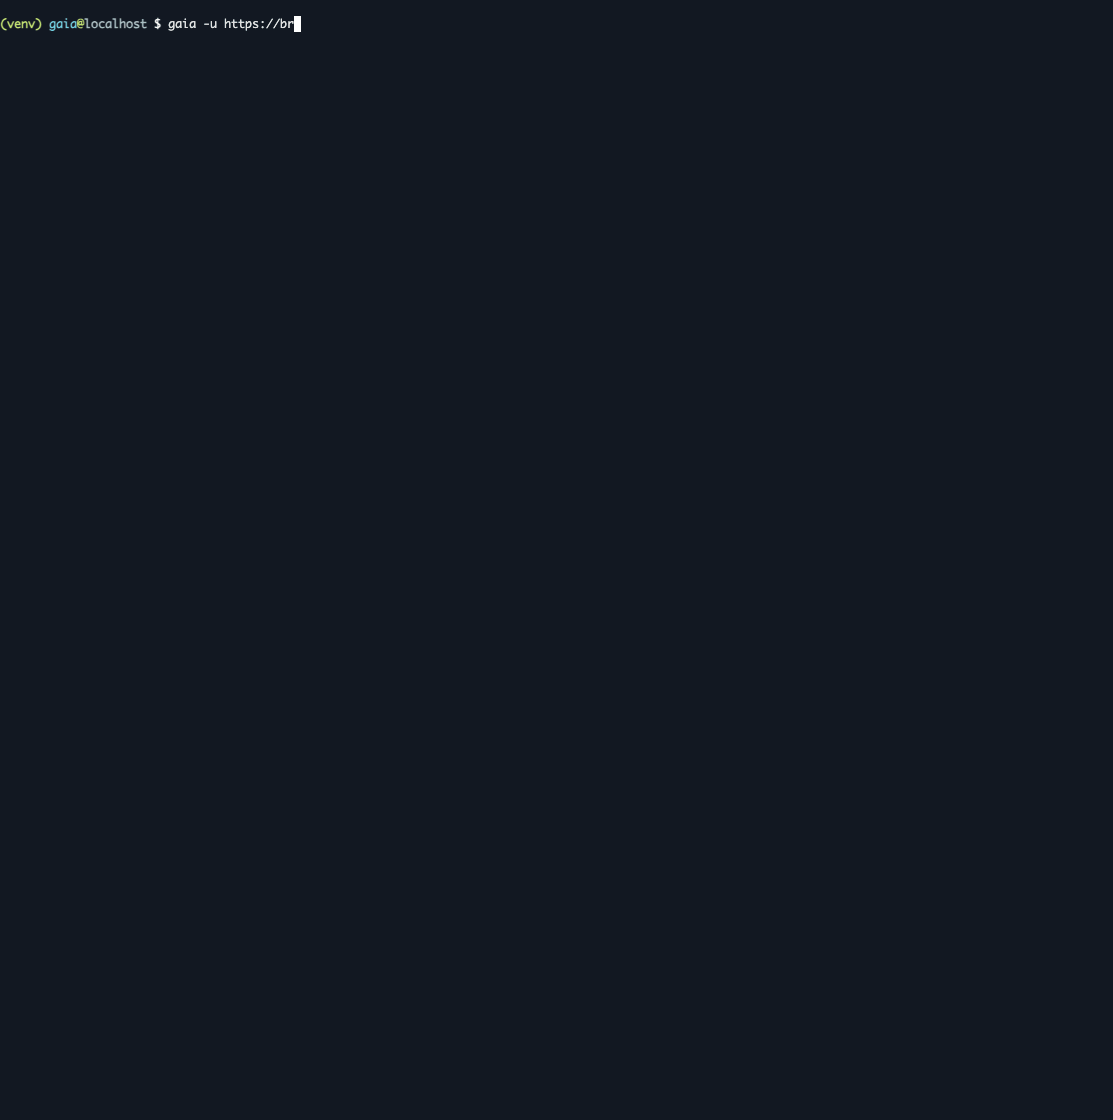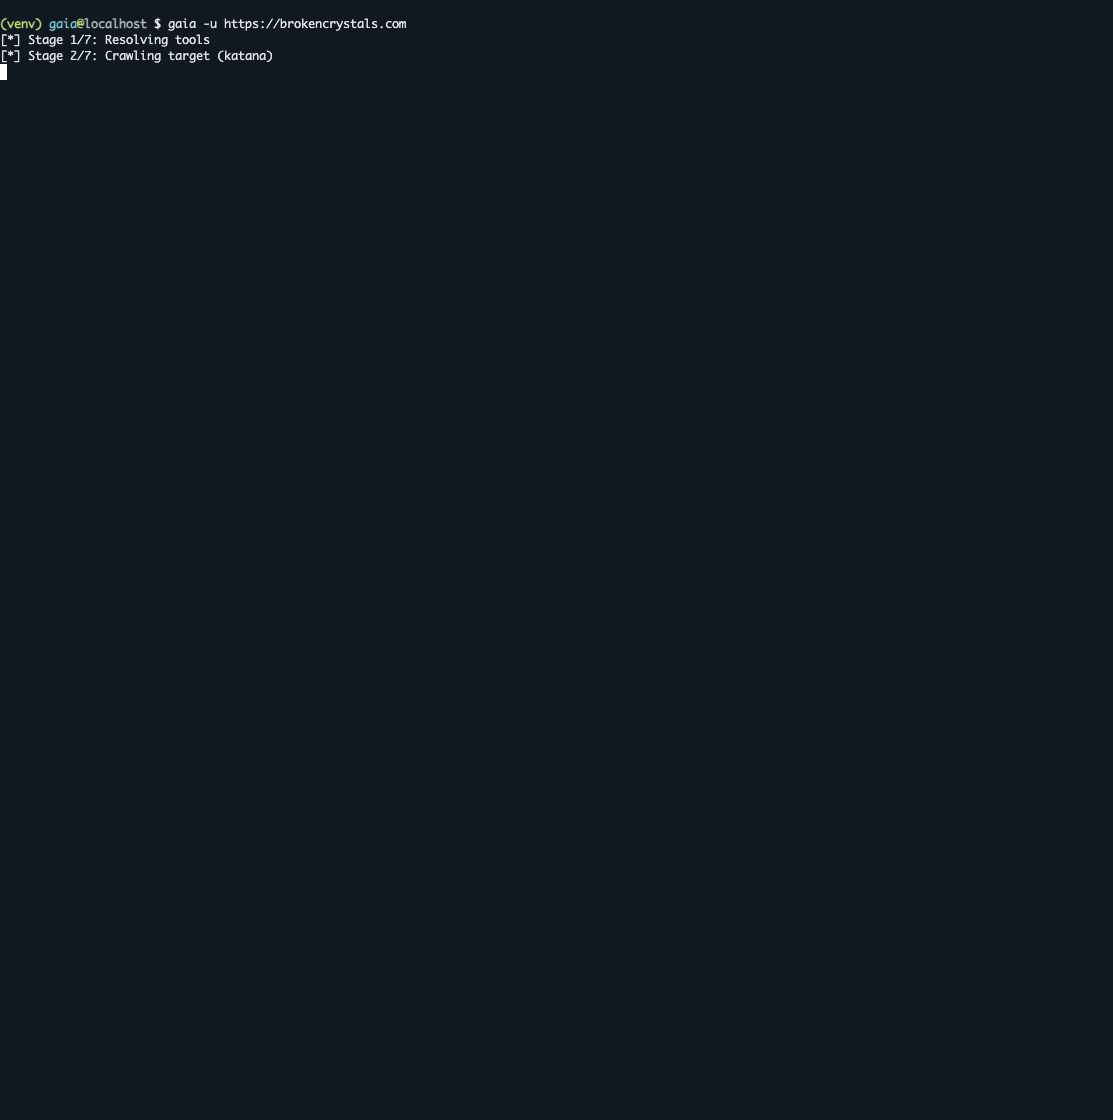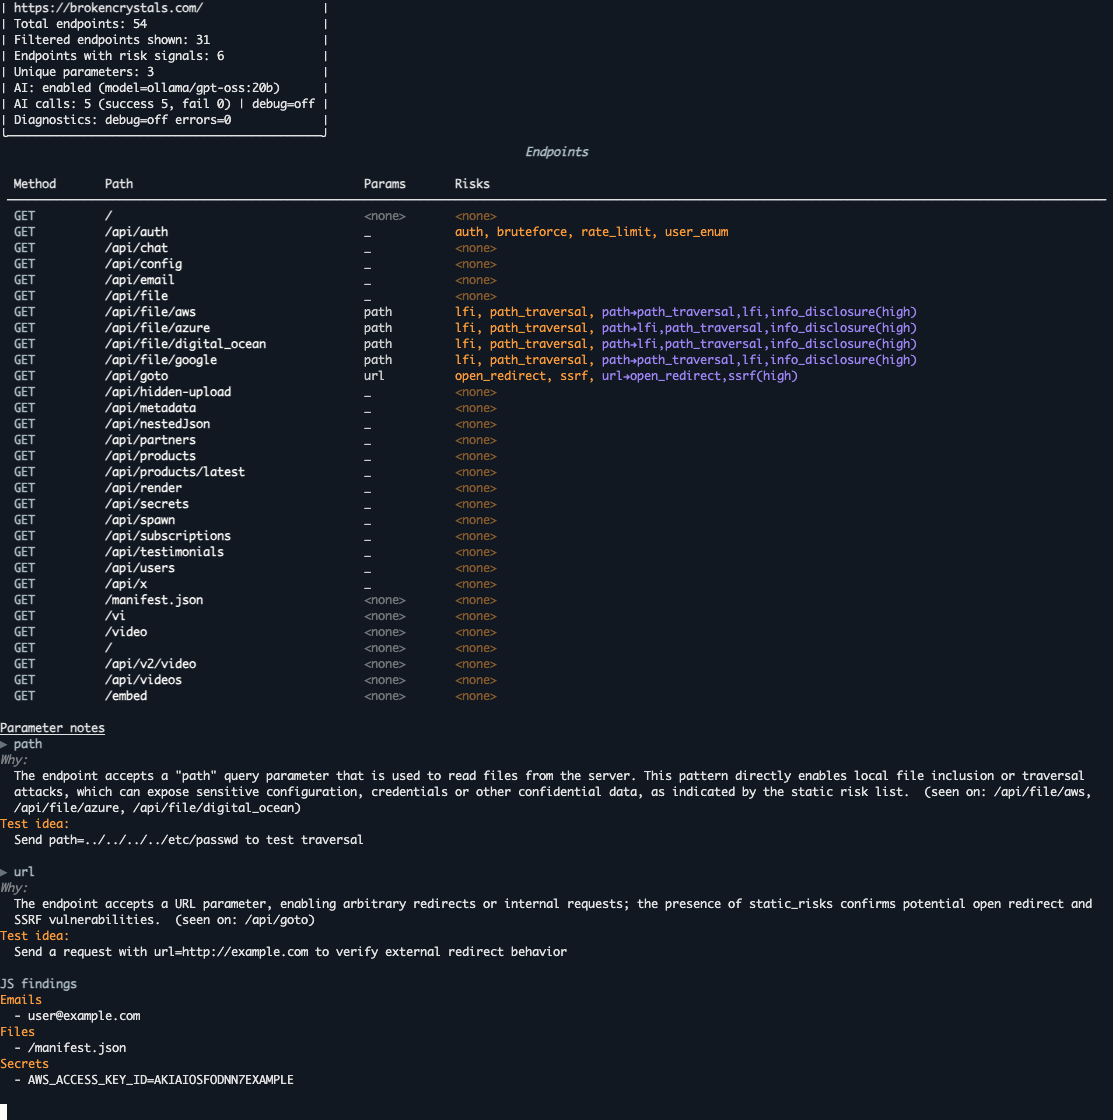 oksuzkayra/gaia
Attack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.
 matijamiki/ranwhat
Flight recorder and secret scanner for AI coding agents. Reads what Claude Code, Codex, Gemini CLI and 17 more ran, and flags risky actions and…
 murrez/cve-2026-101110
Python 3 PoC and mass exploit for CVE-2026-101110, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Book Library <=6.4.6 via…
 dedsecinside/torbot
Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT…
 ejfkdev/dj
Extracts dynamically loaded JavaScript files by statically analyzing website HTML and JS, detecting webpack chunks, import() lazy loading, and source…