

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 rand0m1ze/ezsploit
Linux bash script automation for metasploit
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
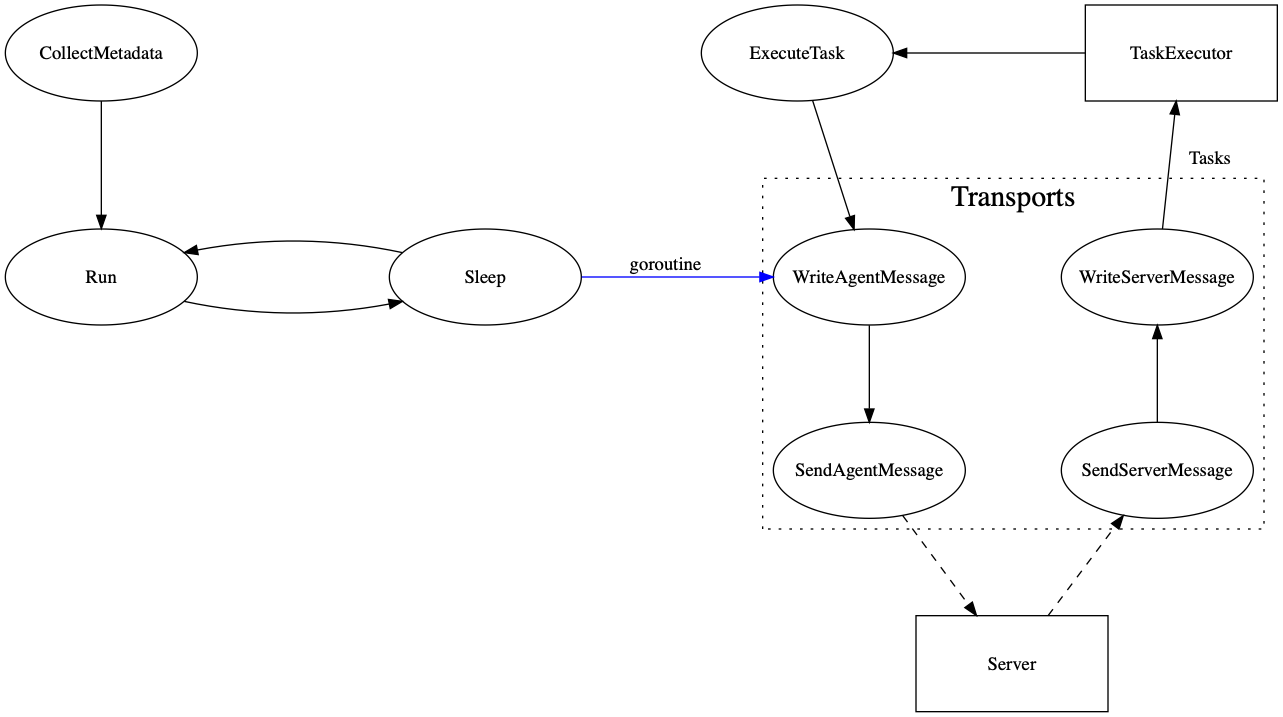 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…