log4j-patched
 aschen/log4j-patched
Provide patched version of Log4J against CVE-2021-44228 and CVE-2021-45046 as well as a script to manually patch it yourself
curated-resourceseducationscripting-automation+2
1
aschen/log4j-patchedProvide patched version of Log4J against CVE-2021-44228 and CVE-2021-45046 as well as a script to manually patch it yourself
 solomonsklash/chomp-scan
A scripted pipeline of tools to streamline the bug bounty/penetration test reconnaissance phase, so you can focus on chomping bugs.
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 dansi/powershell-log4j-scanner
can find, analyse and patch Log4J files because of CVE-2021-44228, CVE-2021-45046
 bishopfox/sliver
Adversary Emulation Framework
 9aylas/shortcut-payload-generator
AutoIt HackTool, Shortcuts .lnk Payloads Generator As LNK-KISSER.

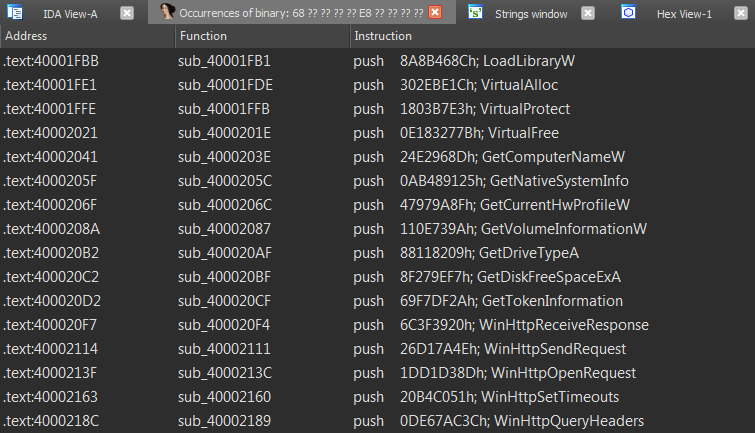 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
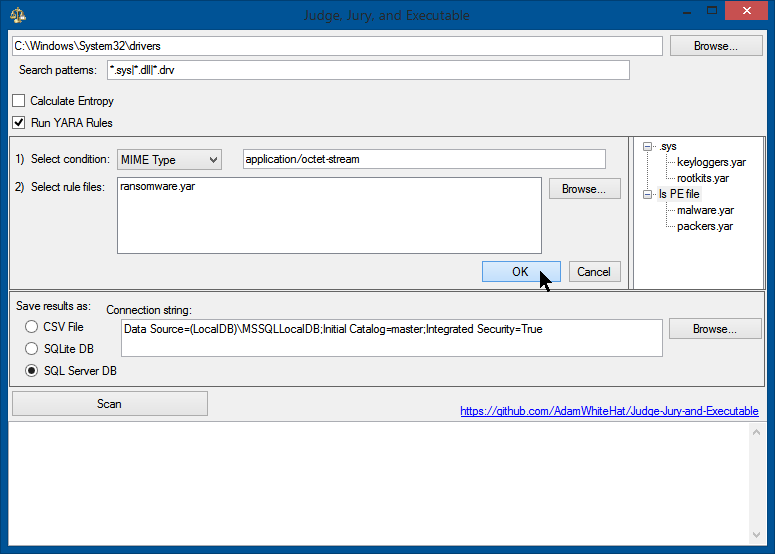 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 an00byss/thecl0n3r
TheCl0n3r will allow you to download and manage your git repositories.
 screetsec/brutesploit
BruteSploit is a collection of method for automated Generate, Bruteforce and Manipulation wordlist with interactive shell. That can be used during a…
 stevemcilwain/quiver
Quiver is the tool to manage all of your tools for bug bounty hunting and penetration testing.
 m108falcon/sudo-cve-2019-14287
Scripts to verify and execute CVE-2019-14287 as part of Research
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
 codeskipper/python-patrol
Scan for python installations on macOS, and run CVE-2015-20107.py script to report if patching is needed
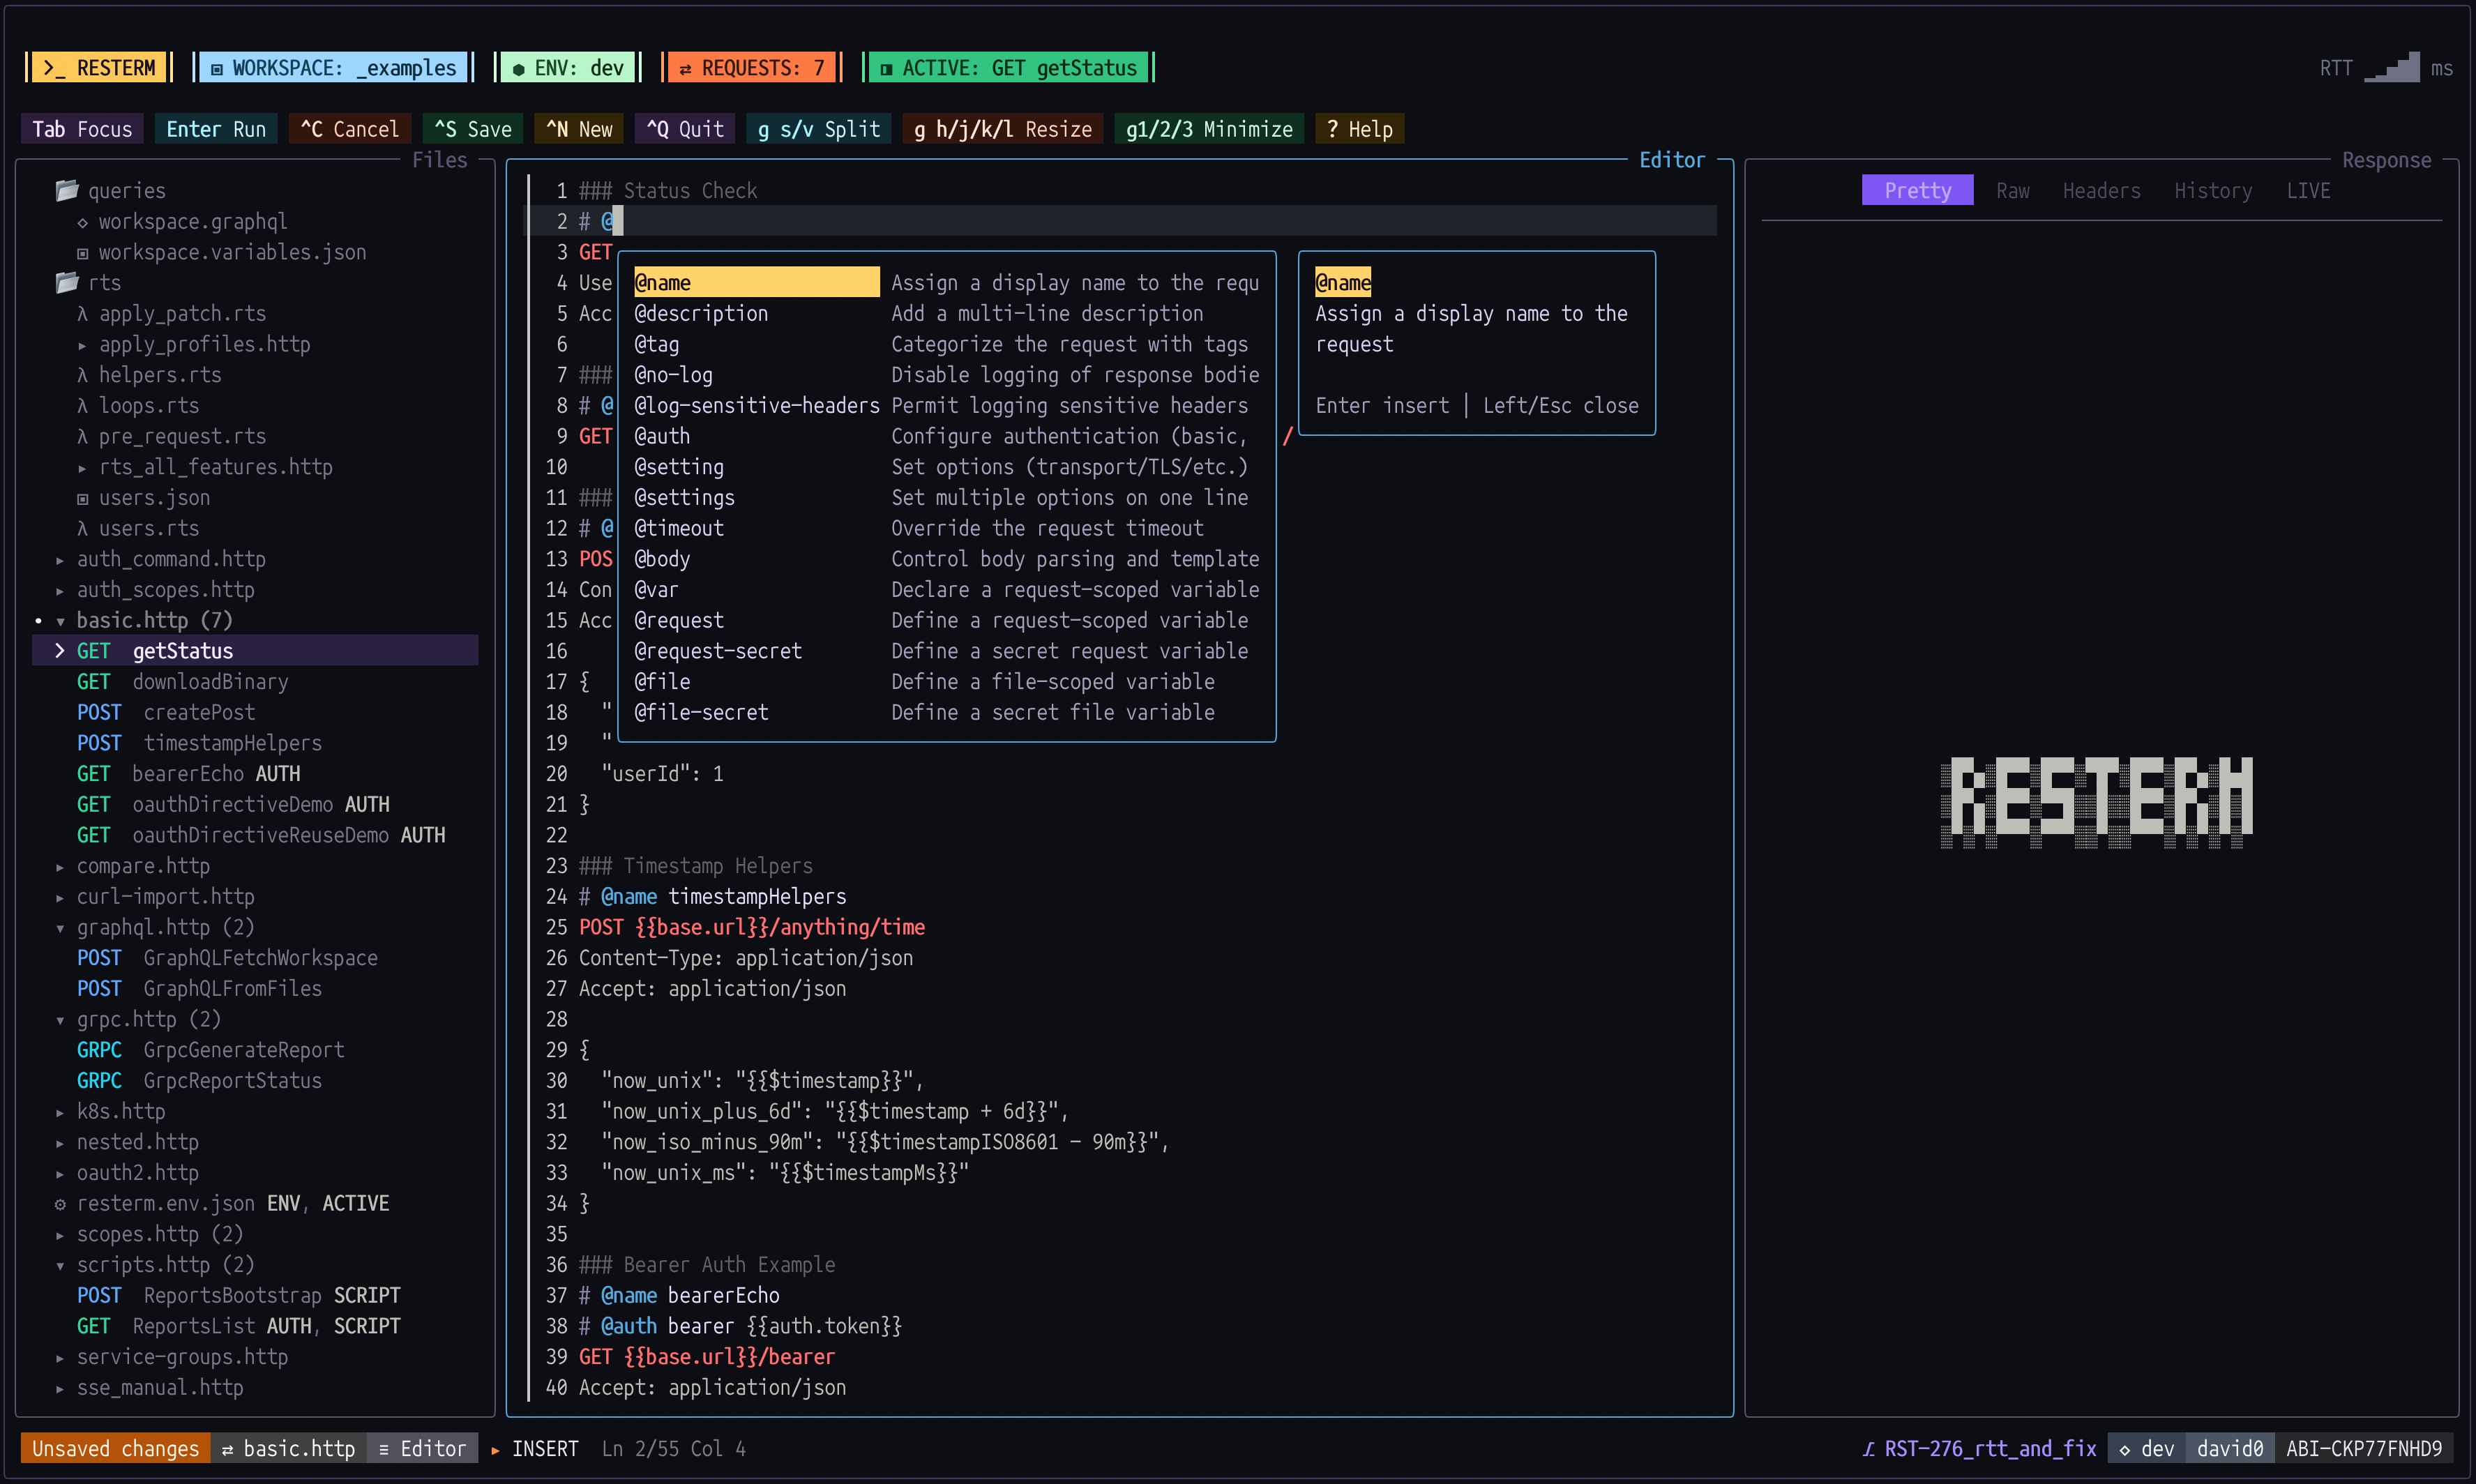 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 digital-dev/log4j-cve-2021-44228-remediation
This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…