

WinDbg-Samples
 microsoft/windbg-samples
Sample extensions, scripts, and API uses for WinDbg.
curated-resourcesdebuggersdynamic-code-analysis+2
82118 days ago
microsoft/windbg-samplesSample extensions, scripts, and API uses for WinDbg.
 arnavps/ctf-web-exploitation
A comprehensive collection of 12 containerized web exploitation challenges covering CVE-2023-25690, WebAuthn bypasses, HTTP/3 smuggling, and advanced…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 portswigger/bambdas
Bambdas collection for Burp Suite Professional and Community.
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 firefart/hashcollision-dos-poc
Proof of Concept for the PHP and JAVA Hashcollision Denial of service attack
 chessredoffsec/cve-2023-26209
Python script with a Tkinter GUI for sending automated payloads of configurable size to a login endpoint, designed for educational testing of server…
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
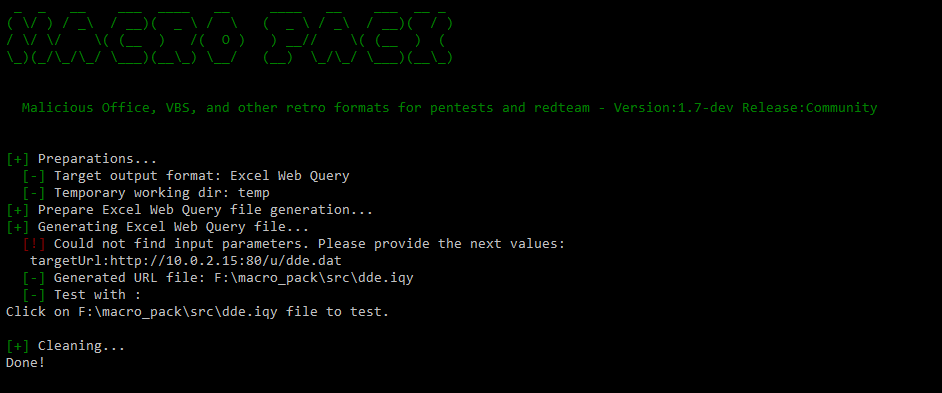 sevagas/macro_pack
macro_pack is a tool by @EmericNasi used to automatize obfuscation and generation of Office documents, VB scripts, shortcuts, and other formats for…
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
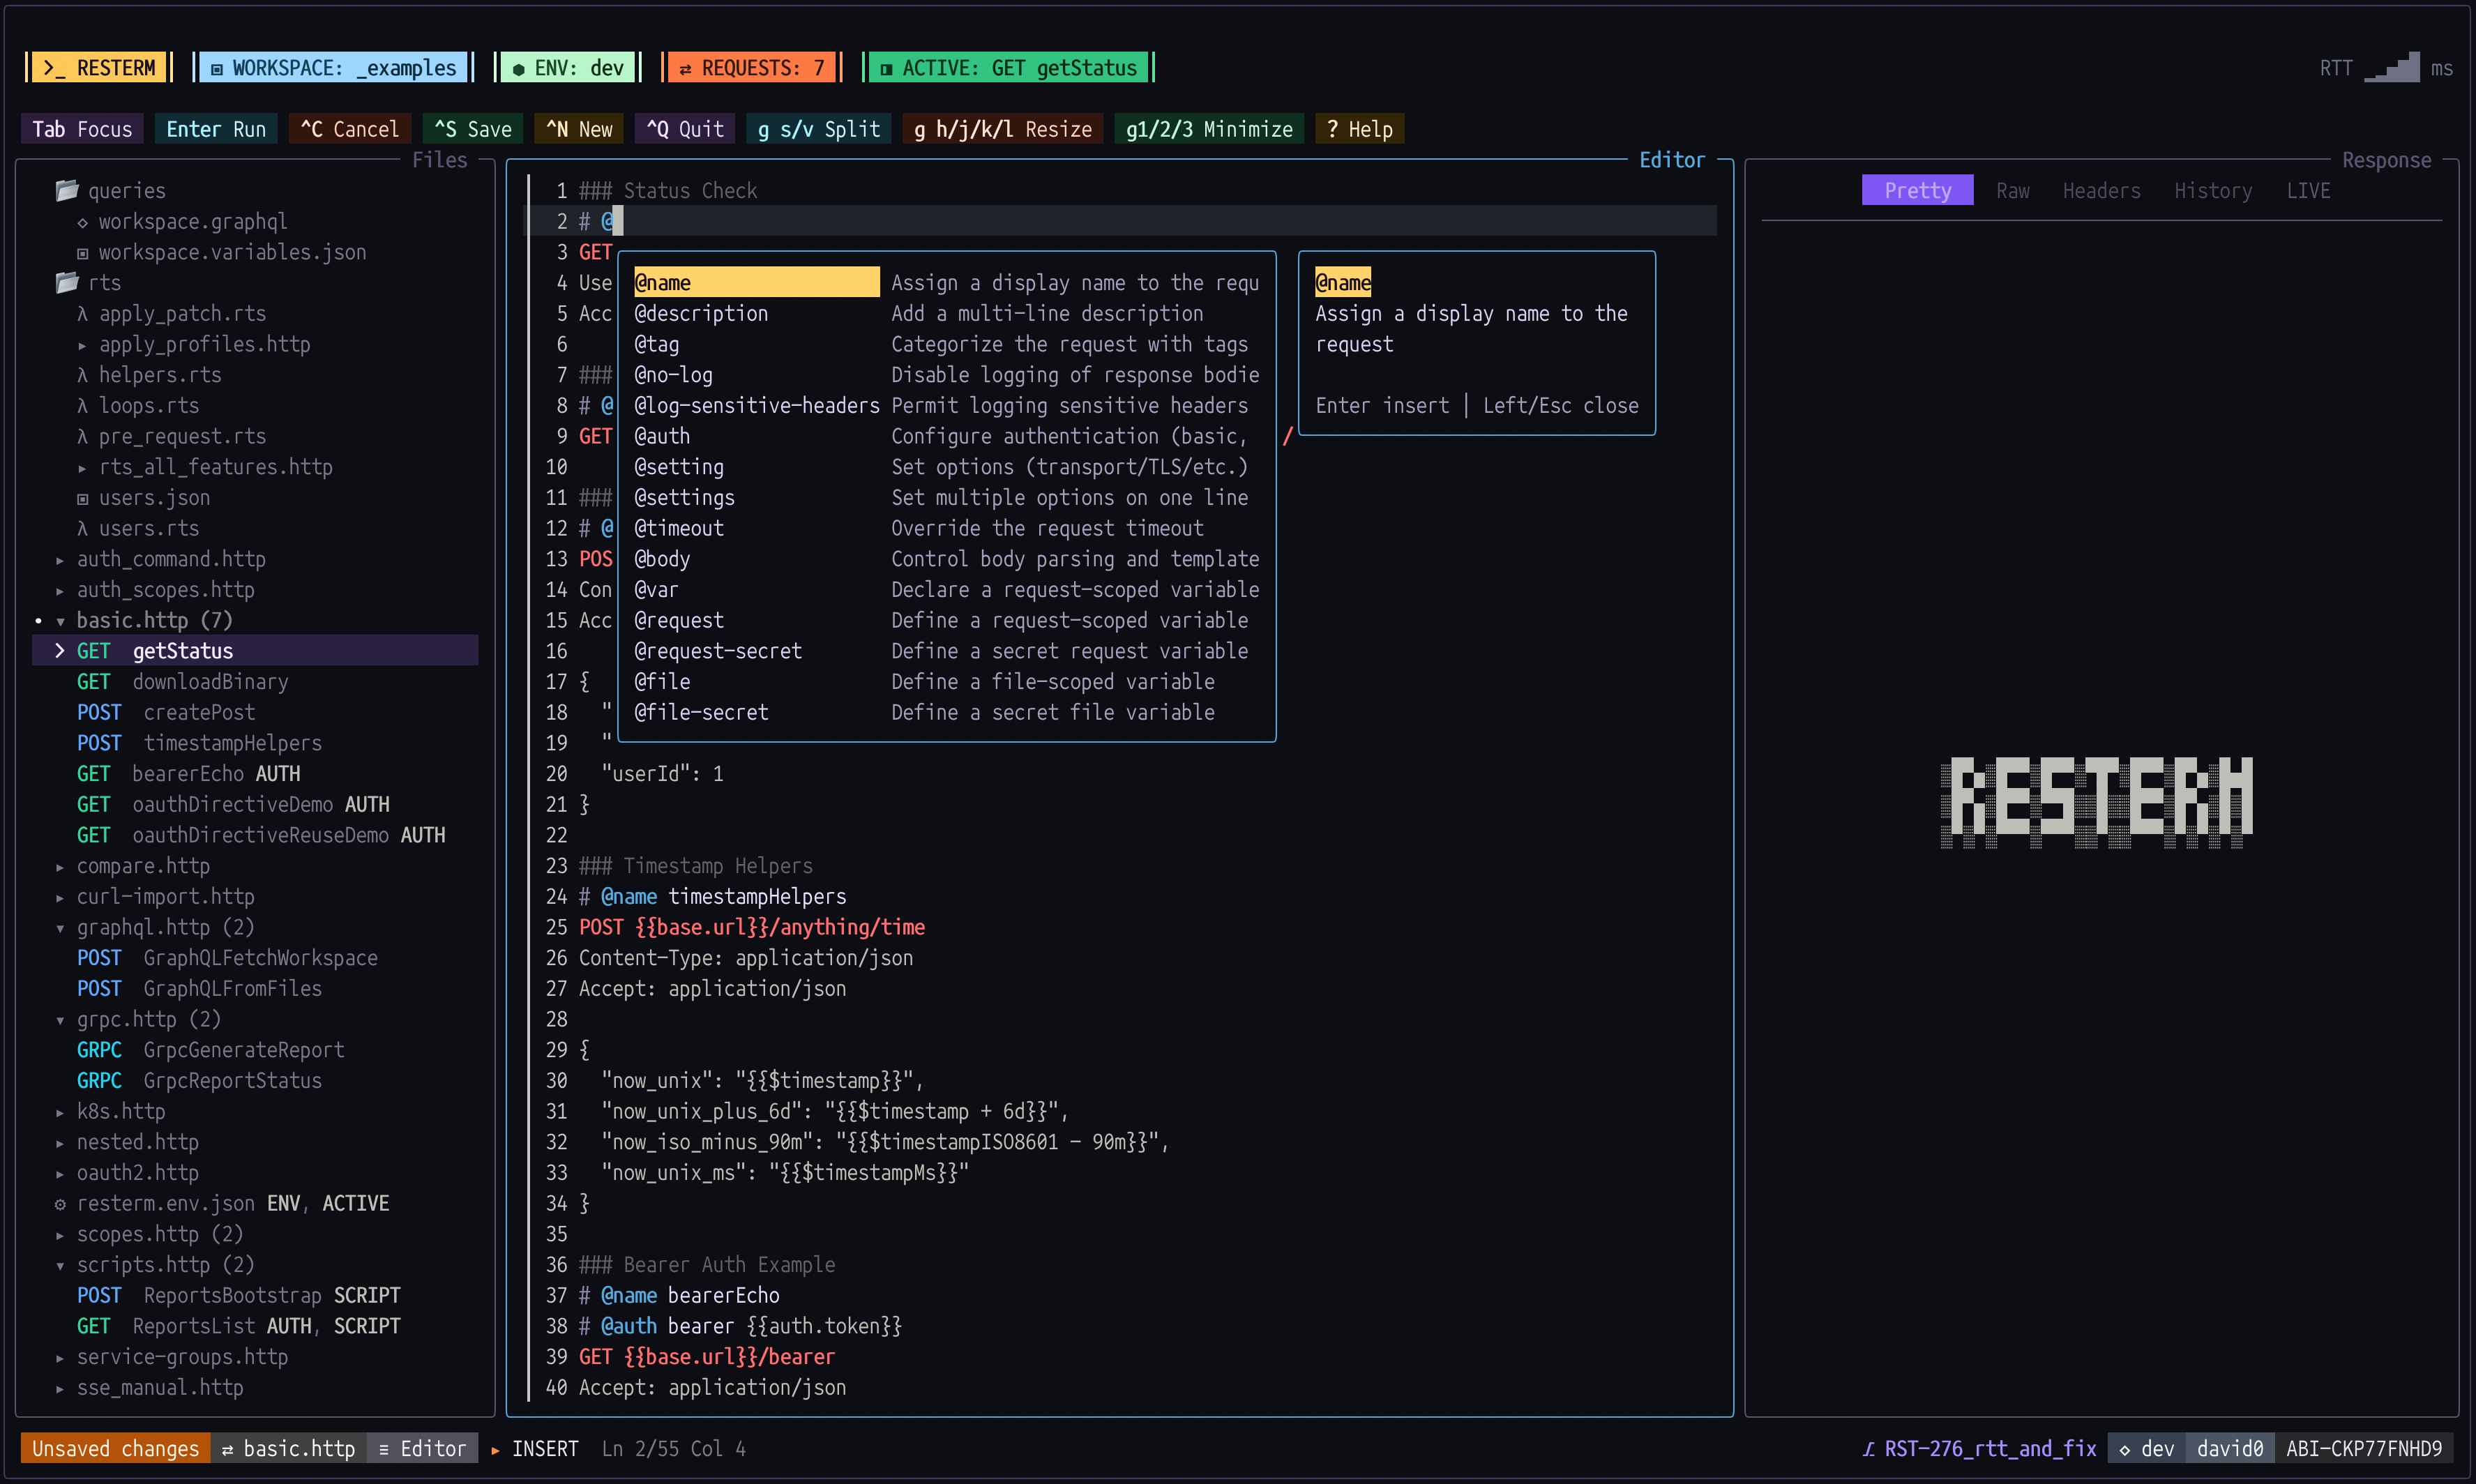 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…