
gaia
 oksuzkayra/gaia
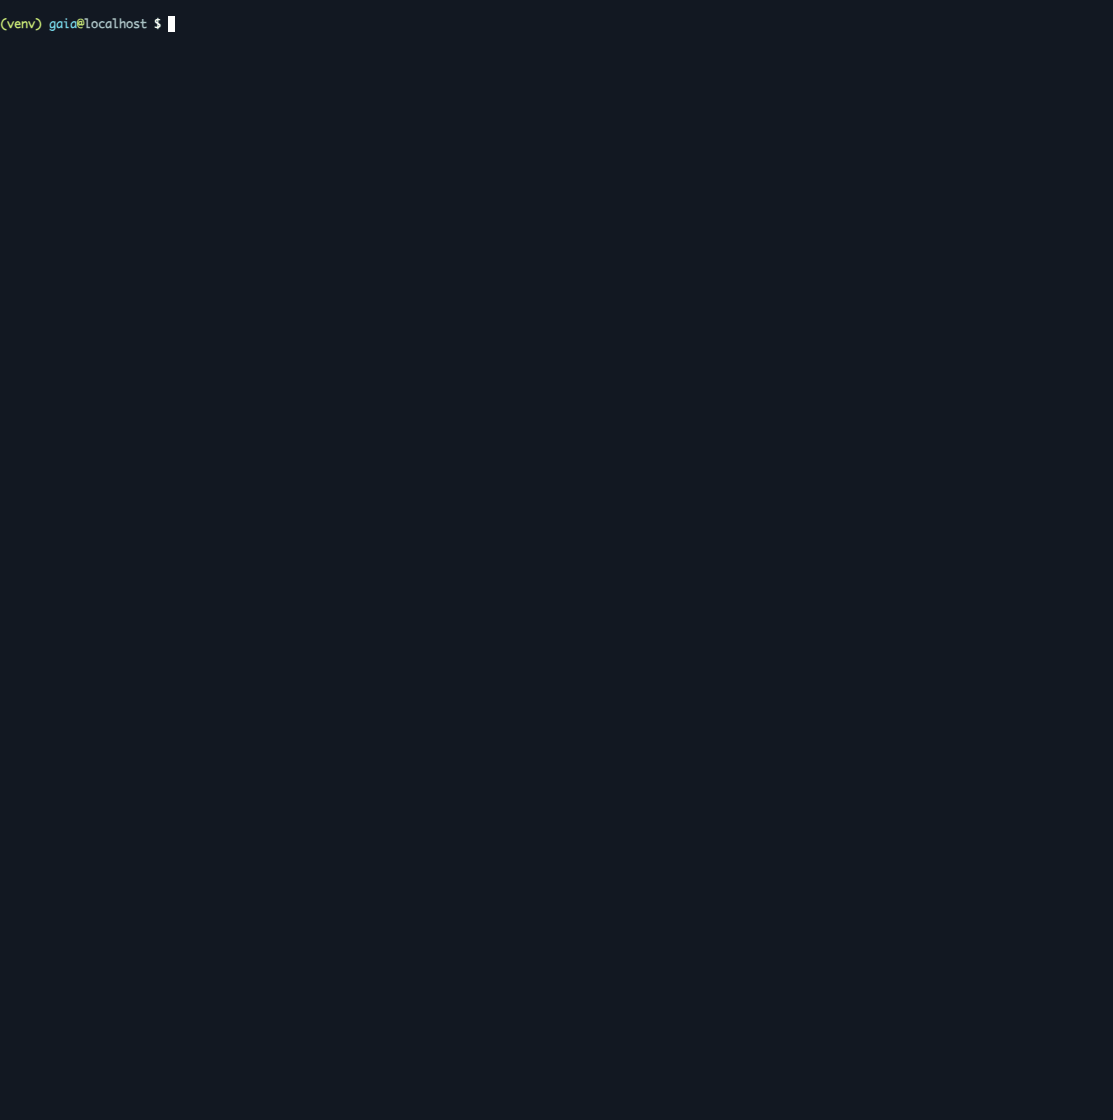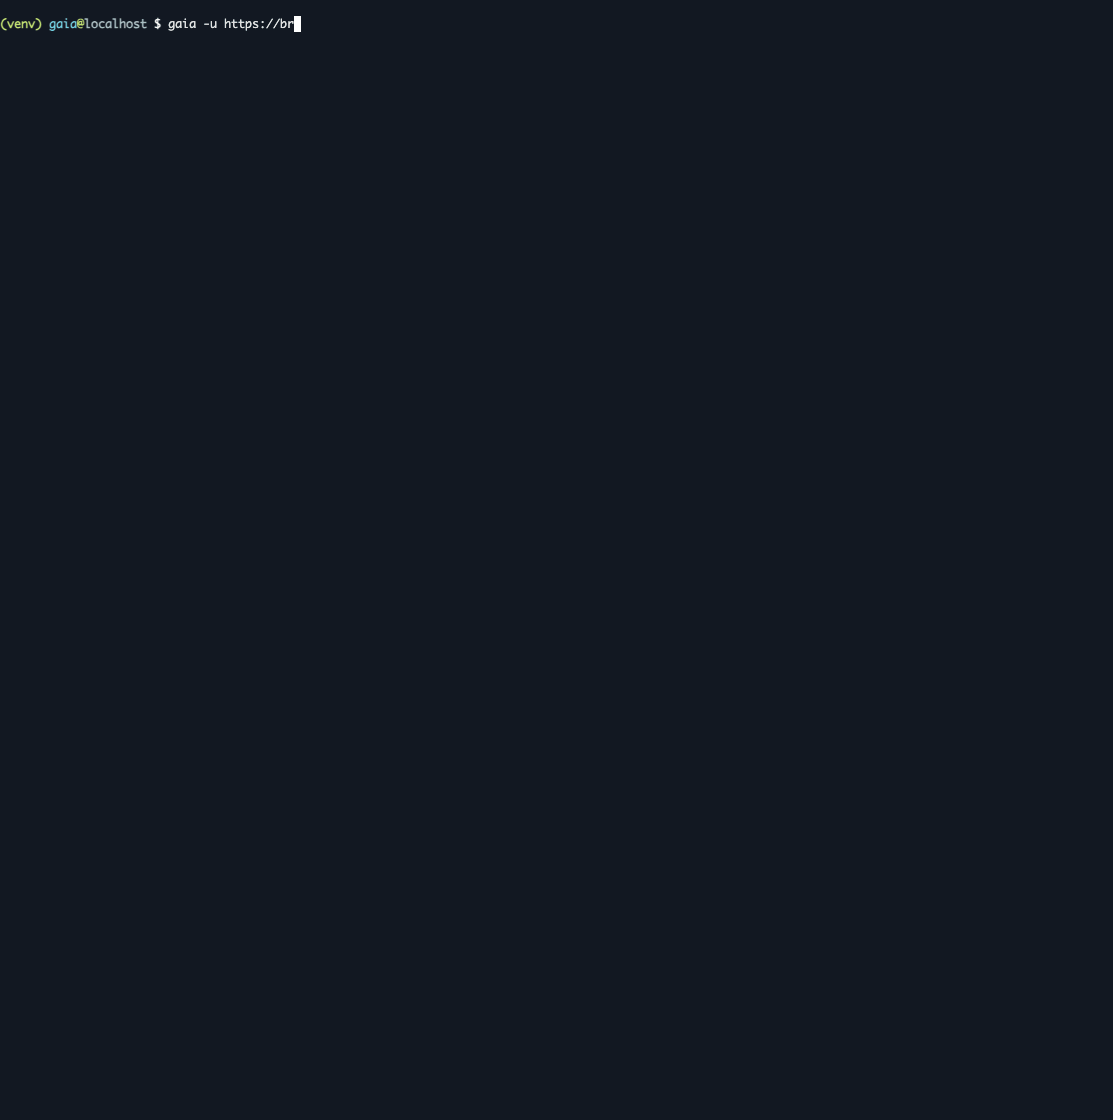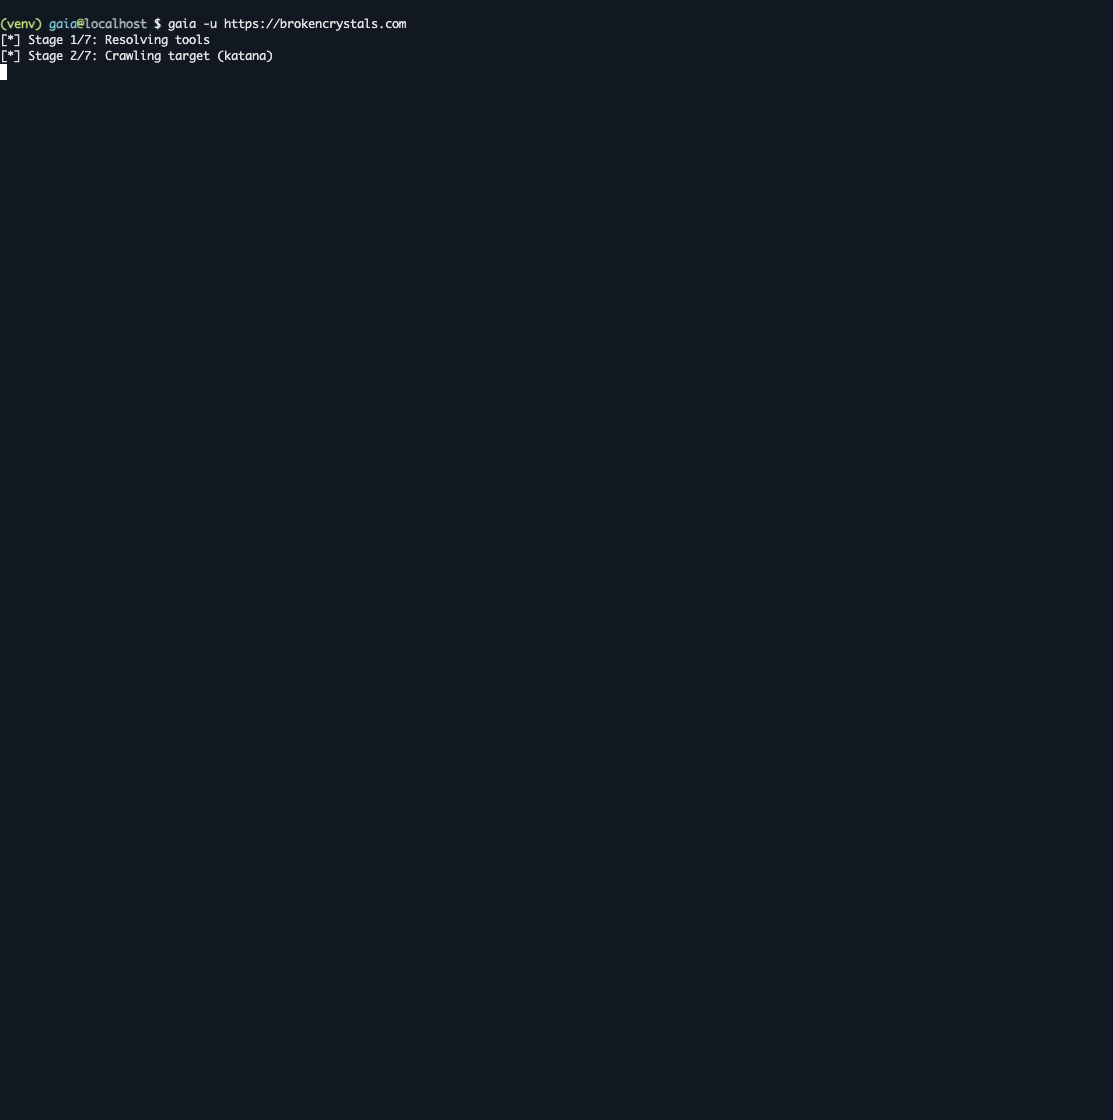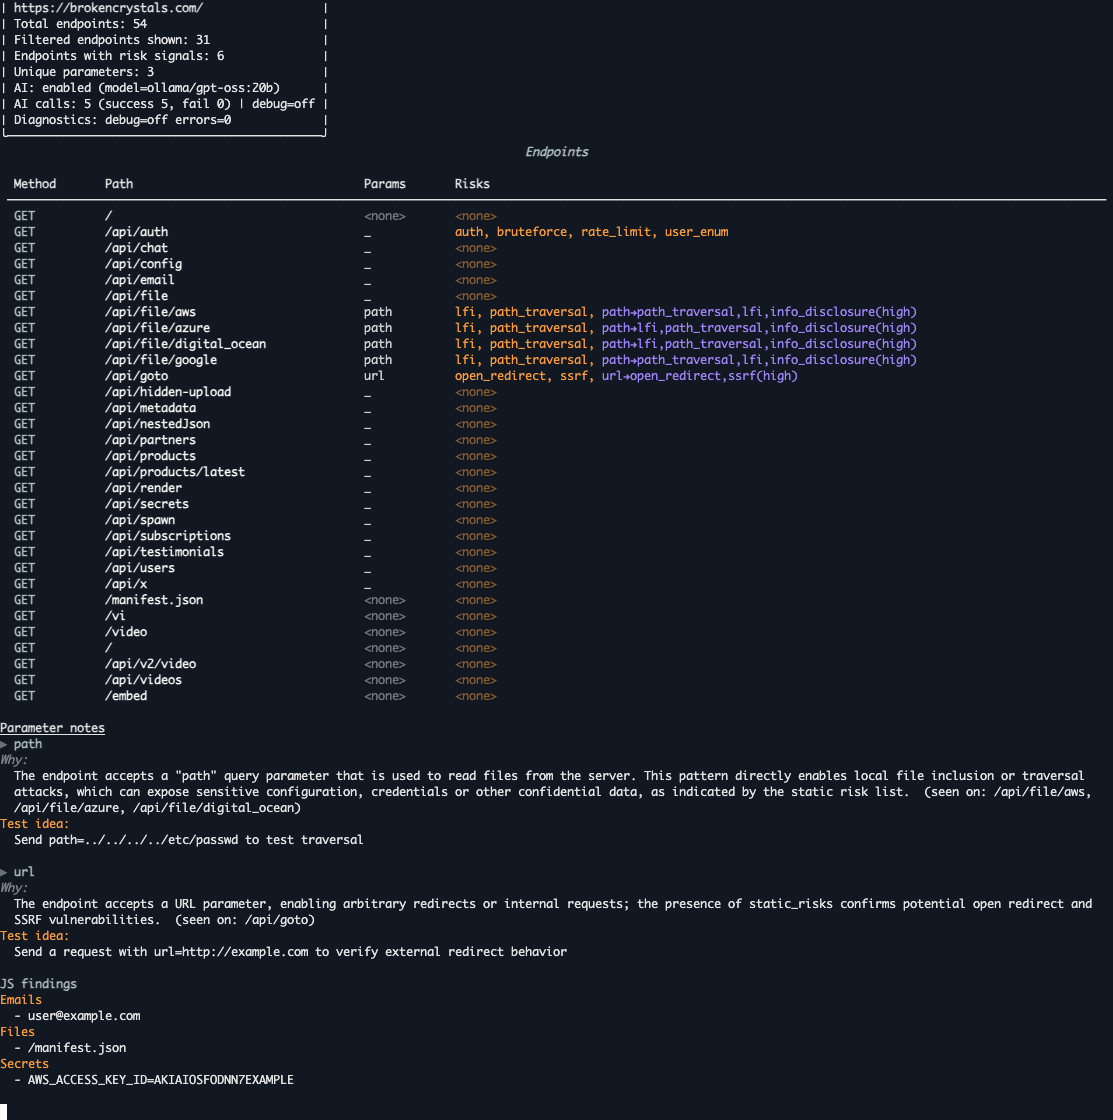
Attack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.
ai-securitycrawlerinformation-gathering+7
oksuzkayra/gaiaAttack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.
 mthcht/purpleteam
Purpleteam scripts simulation & Detection - trigger events for SOC detections
 smicallef/spiderfoot
Automates OSINT data collection and analysis for threat intelligence, attack surface mapping, and reconnaissance. Integrates 200+ modules for DNS,…
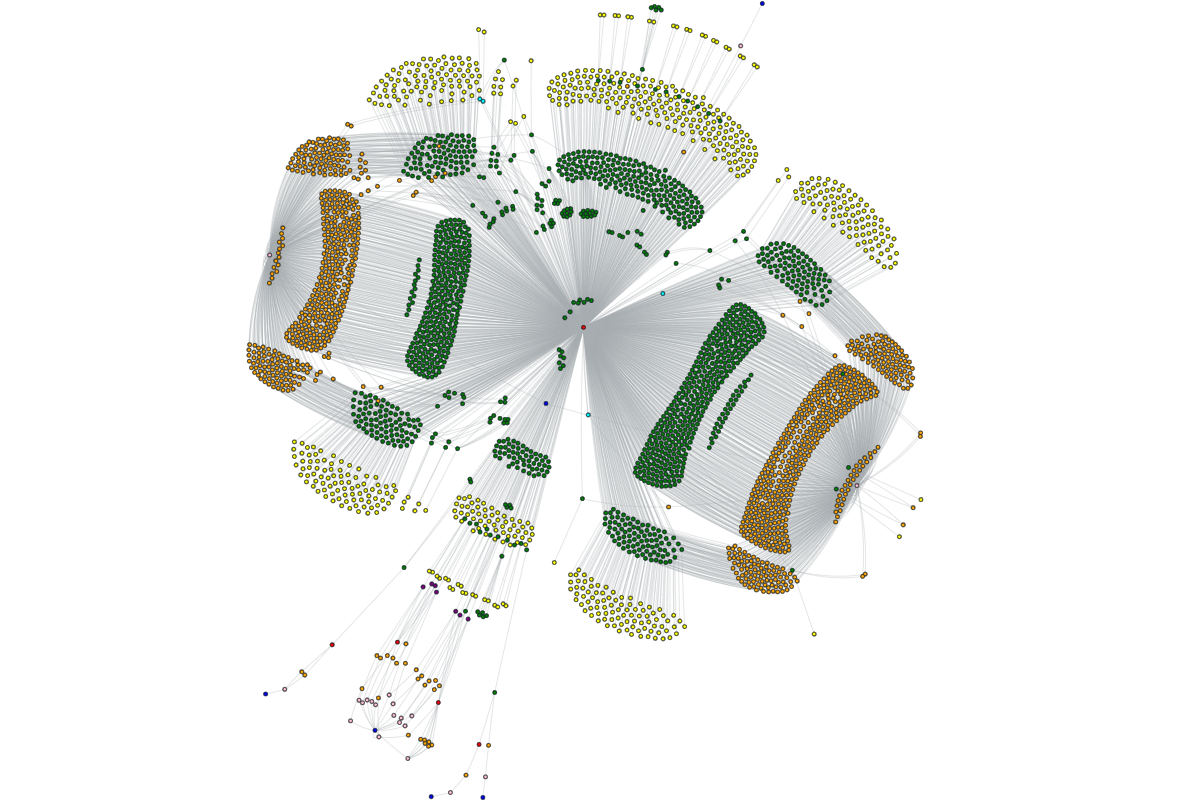 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 ishaklaz/hash-eye
**HashEye** is a powerful Python CLI tool for instantly detecting and analyzing hash types. It provides detailed information about hash formats,…
 codingo/interlace
Easily turn single threaded command line applications into a fast, multi-threaded application with CIDR and glob support.
 devanshbatham/rayder
A lightweight tool for orchestrating and organizing your bug hunting recon / pentesting command-line workflows
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
 xdev05/cve-2020-3452-poc
Automates downloading and running an Nmap NSE script to scan hosts for CVE-2020-3452 vulnerability, using a list of target hosts.
 abrewer251/cve-2025-1974_ingressnightmare_poc
Automates sending JSON payloads to multiple IPs via curl to test for CVE-2025-1974 (IngressNightmare), classifying responses and generating XML…
 murrez/cve-2026-84434
Python PoC scanner and exploit for CVE-2026-84434, an unauthenticated arbitrary file upload in Gravity Forms <=3.1.0.4 via hidden File Upload fields.…
 ianxtianxt/sleuthql
SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。
 guokers/aioscan_cve-2020-0796
基于asyncio(协程)的CVE-2020-0796 速度还是十分可观的,方便运维师傅们对内网做下快速检测。
 asbawy/automation-for-juniper-cve-2023-36845
Simple Automation script for juniper cve-2023-36845
 jheeree/simple-cve-2021-41773-checker
Simple script realizado en bash, para revisión de múltiples hosts para CVE-2021-41773 (Apache)
 ap0dexme0/cve-2024-6387
OpenSSH RCE Massive Vulnerable Scanner
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).