
screenpipe
 screenpipe/screenpipe
YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
ctfcurated-resourceseducation+8
20.9k
screenpipe/screenpipeYC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 symfony/symfony
The Symfony PHP framework
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 openclaw/openclaw
The AI that really does things. Any OS. Any Platform. The lobster way. 🦞
 nousresearch/hermes-agent
The agent that grows with you
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 pydantic/monty
A secure Python sandbox, written in Rust, for code written by AI.
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
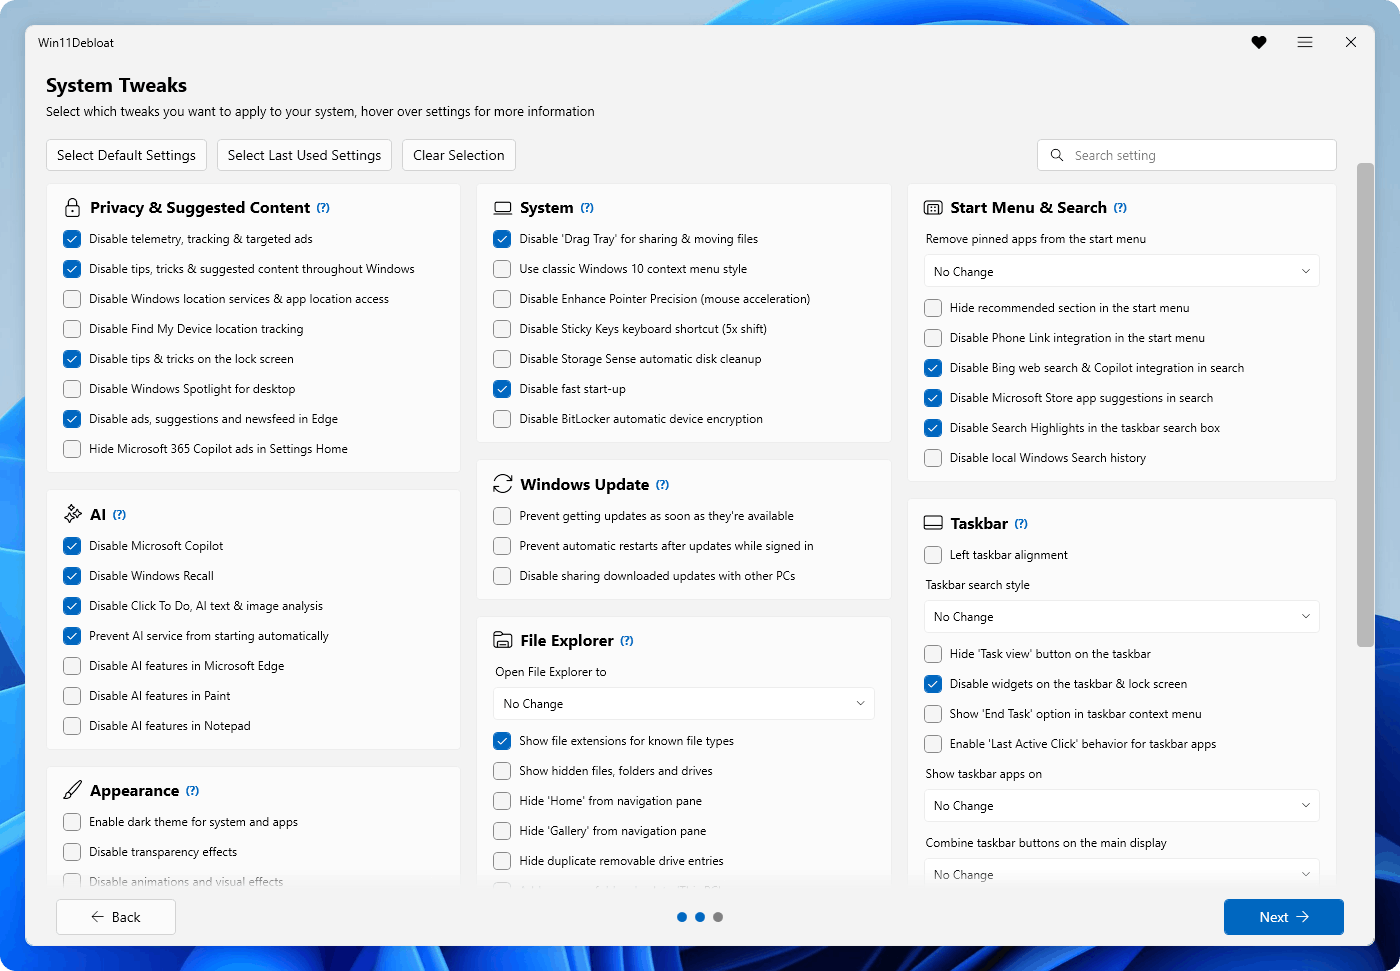 raphire/win11debloat
A simple, lightweight PowerShell script that allows you to remove pre-installed apps, disable telemetry, as well as perform various other changes to…
 microsoft/playwright
Browser automation framework with a single API for Chromium, Firefox, and WebKit. Supports web testing, scraping, screenshots, and network…
 athena-os/athena
Athena OS is a Arch/Nix-based distro focused on Cybersecurity. Learn, practice and enjoy with any hacking tool!
 0xcub3/wblock
Free, open-source Safari ad blocker for macOS, iOS, iPadOS and visionOS. Up to 750,000 rules, custom filter lists, userscripts and userstyles. No…
 praetorian-inc/capability-sdk
Shared Go SDK defining a standard capability interface for security scanners, with multi-format finding output (terminal, JSON, NDJSON, Markdown,…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…