

evil-winrm-py
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
authenticationcommand-and-controllateral-movement+7
413
adityatelange/evil-winrm-pyExecute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 iterat0r/cnaemulator
Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
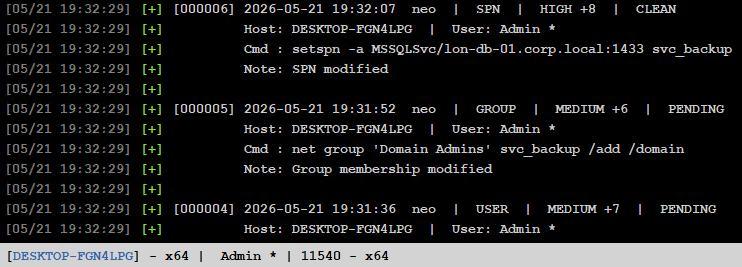 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 onescripter/wmiexec
Execute Windows commands remotely and capture output using only WMI and PowerShell (not remoting).
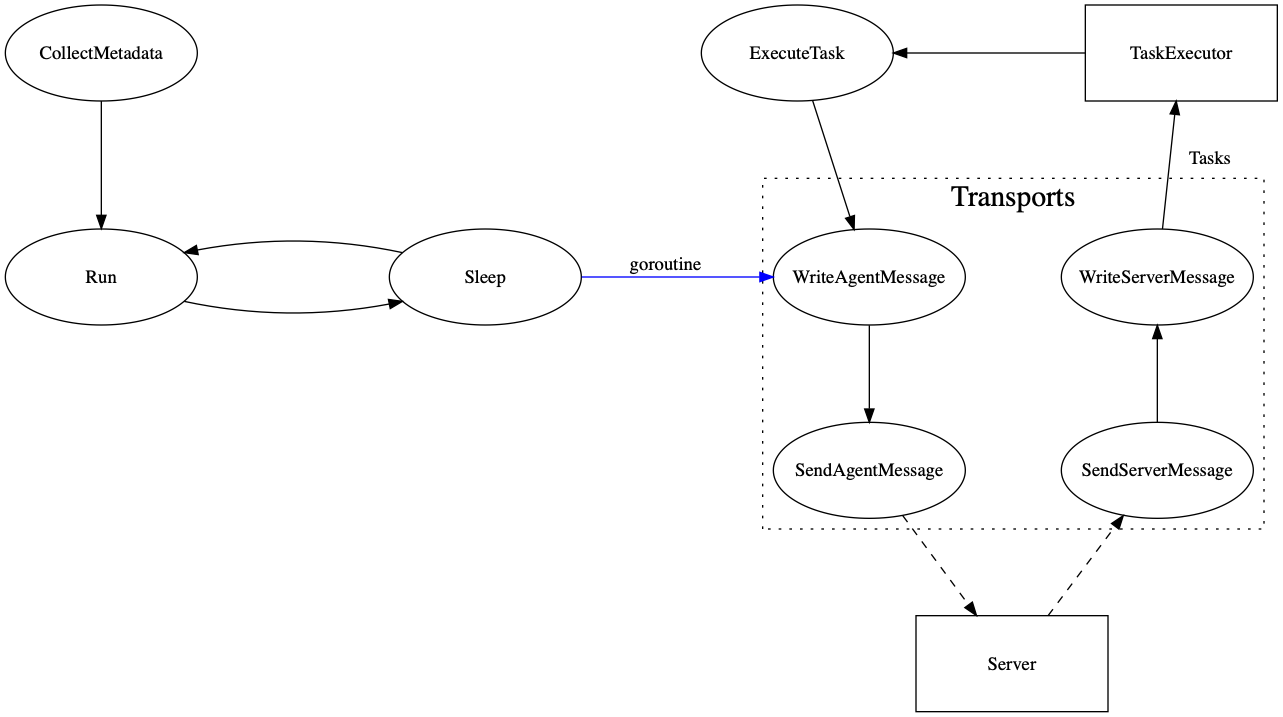 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 codextf2/cobaltstrike-headless
Aggressorscript that turns the headless aggressor client into a (mostly) functional cobalt strike client.
 emcghee/payloadautomation
Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 rand0m1ze/ezsploit
Linux bash script automation for metasploit