
nebula
 berylliumsec/nebula
AI-powered penetration testing assistant for automating recon, note-taking, and vulnerability analysis.
ai-securityexploit-frameworksinformation-gathering+5
1.1k
berylliumsec/nebulaAI-powered penetration testing assistant for automating recon, note-taking, and vulnerability analysis.
 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
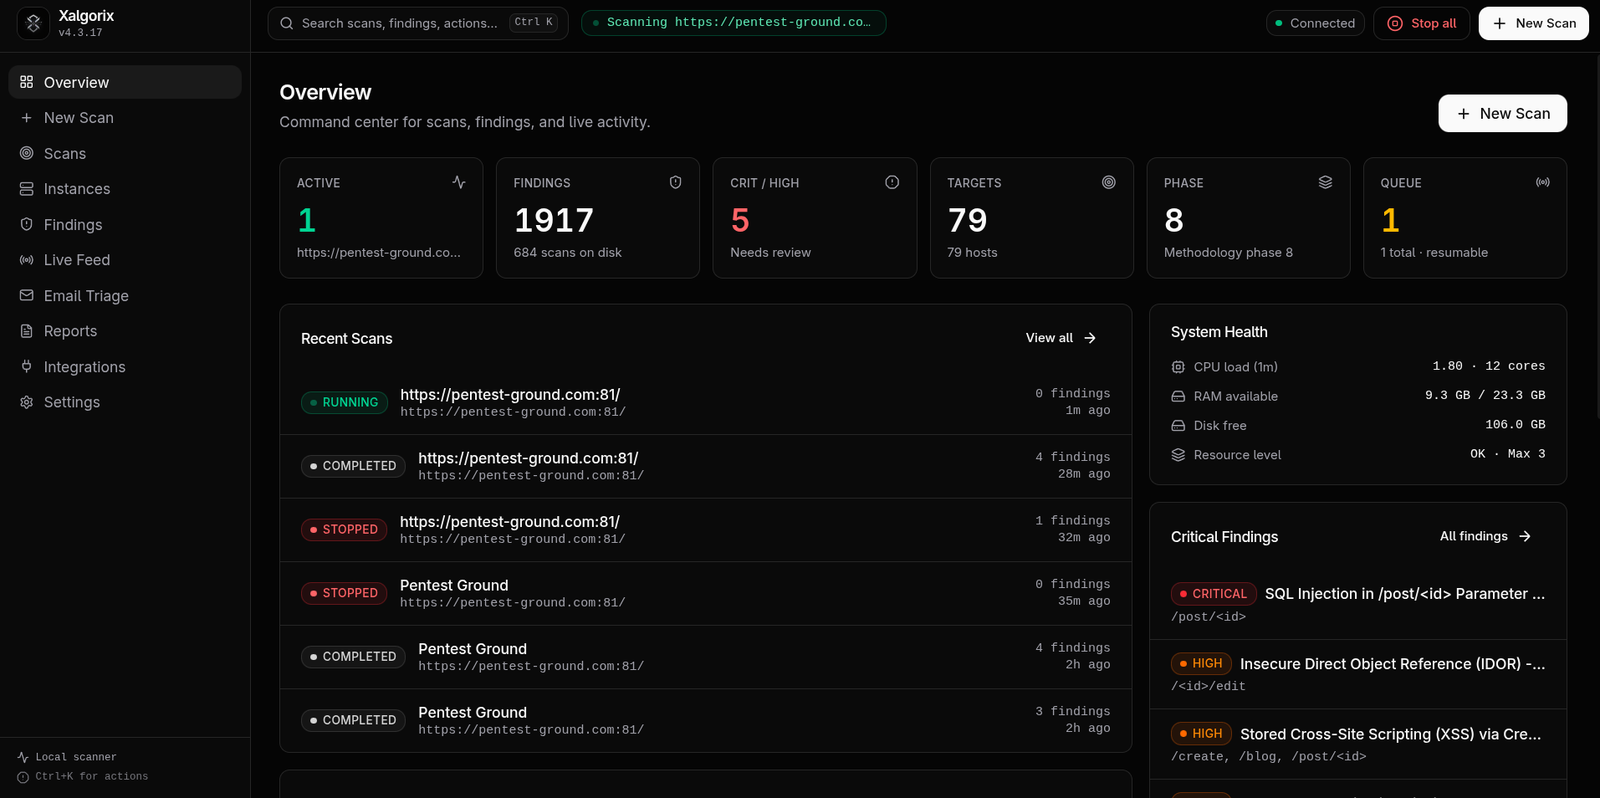 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
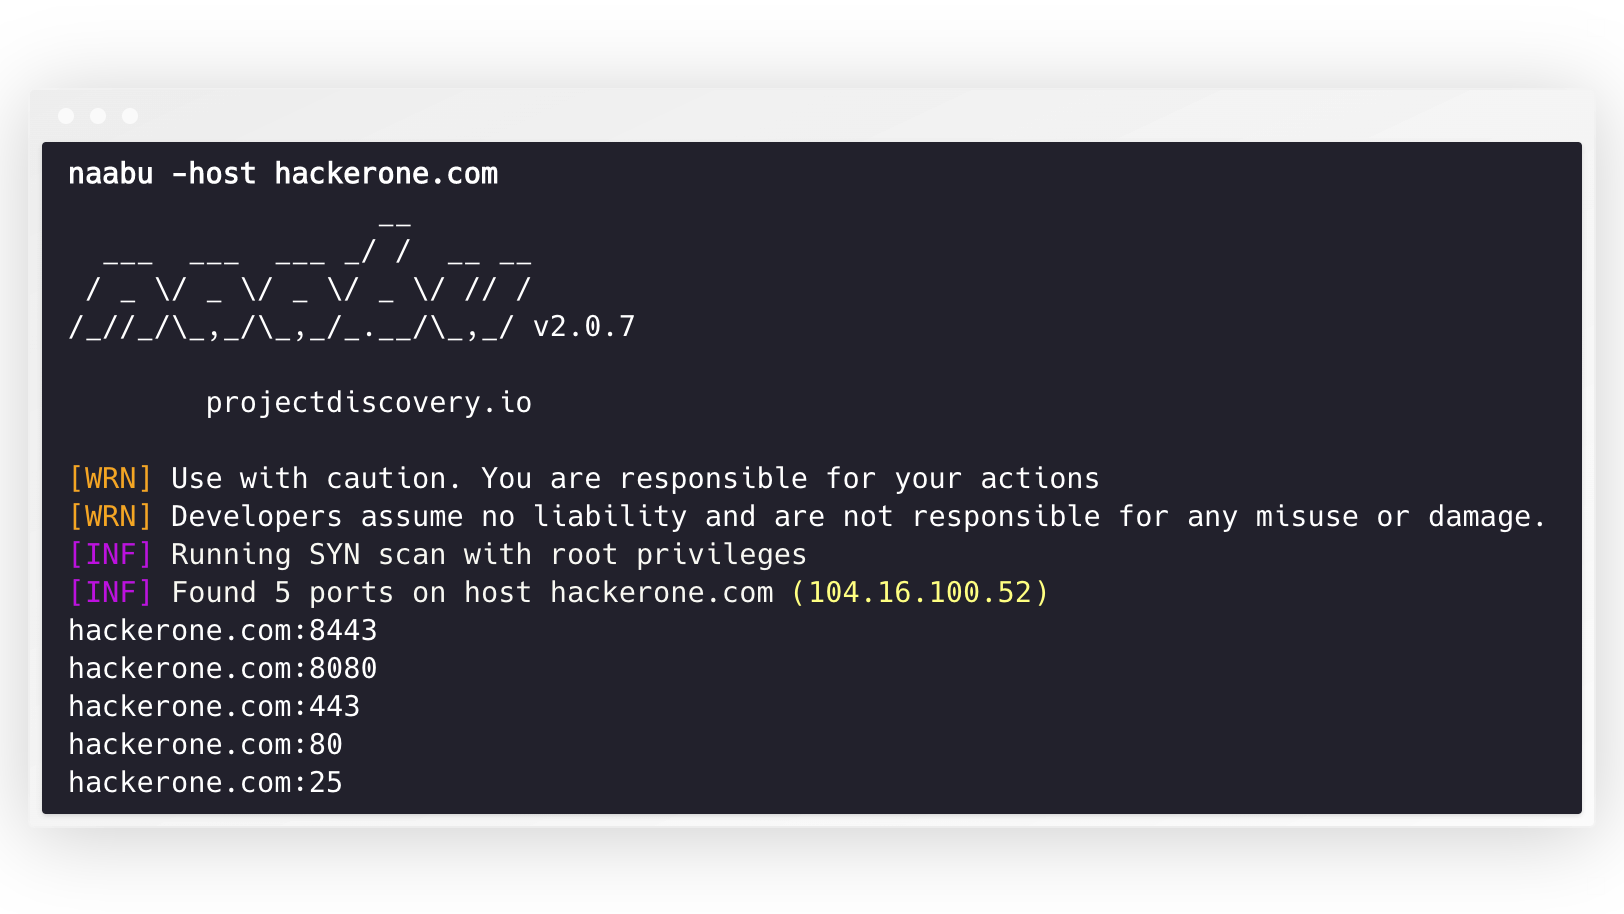 projectdiscovery/naabu
A fast port scanner written in go with a focus on reliability and simplicity. Designed to be used in combination with other tools for attack surface…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 ginlix-ai/langalpha
Automated OSINT framework for reconnaissance, data harvesting, and threat intelligence gathering with modular crawlers, scanners, and extraction…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.

 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 rthalley/dnspython
Python DNS toolkit supporting queries, zone transfers, dynamic updates, TSIG, EDNS0, DNSSEC, DNS-over-HTTPS, and DNS-over-QUIC with high- and…

 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…