

gori
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
api-security-testingfuzzinginformation-gathering+8
hahwul/goriA fast, keyboard-driven HTTP intercepting proxy and pentesting toolkit for the terminal built for humans and AI agents alike.
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
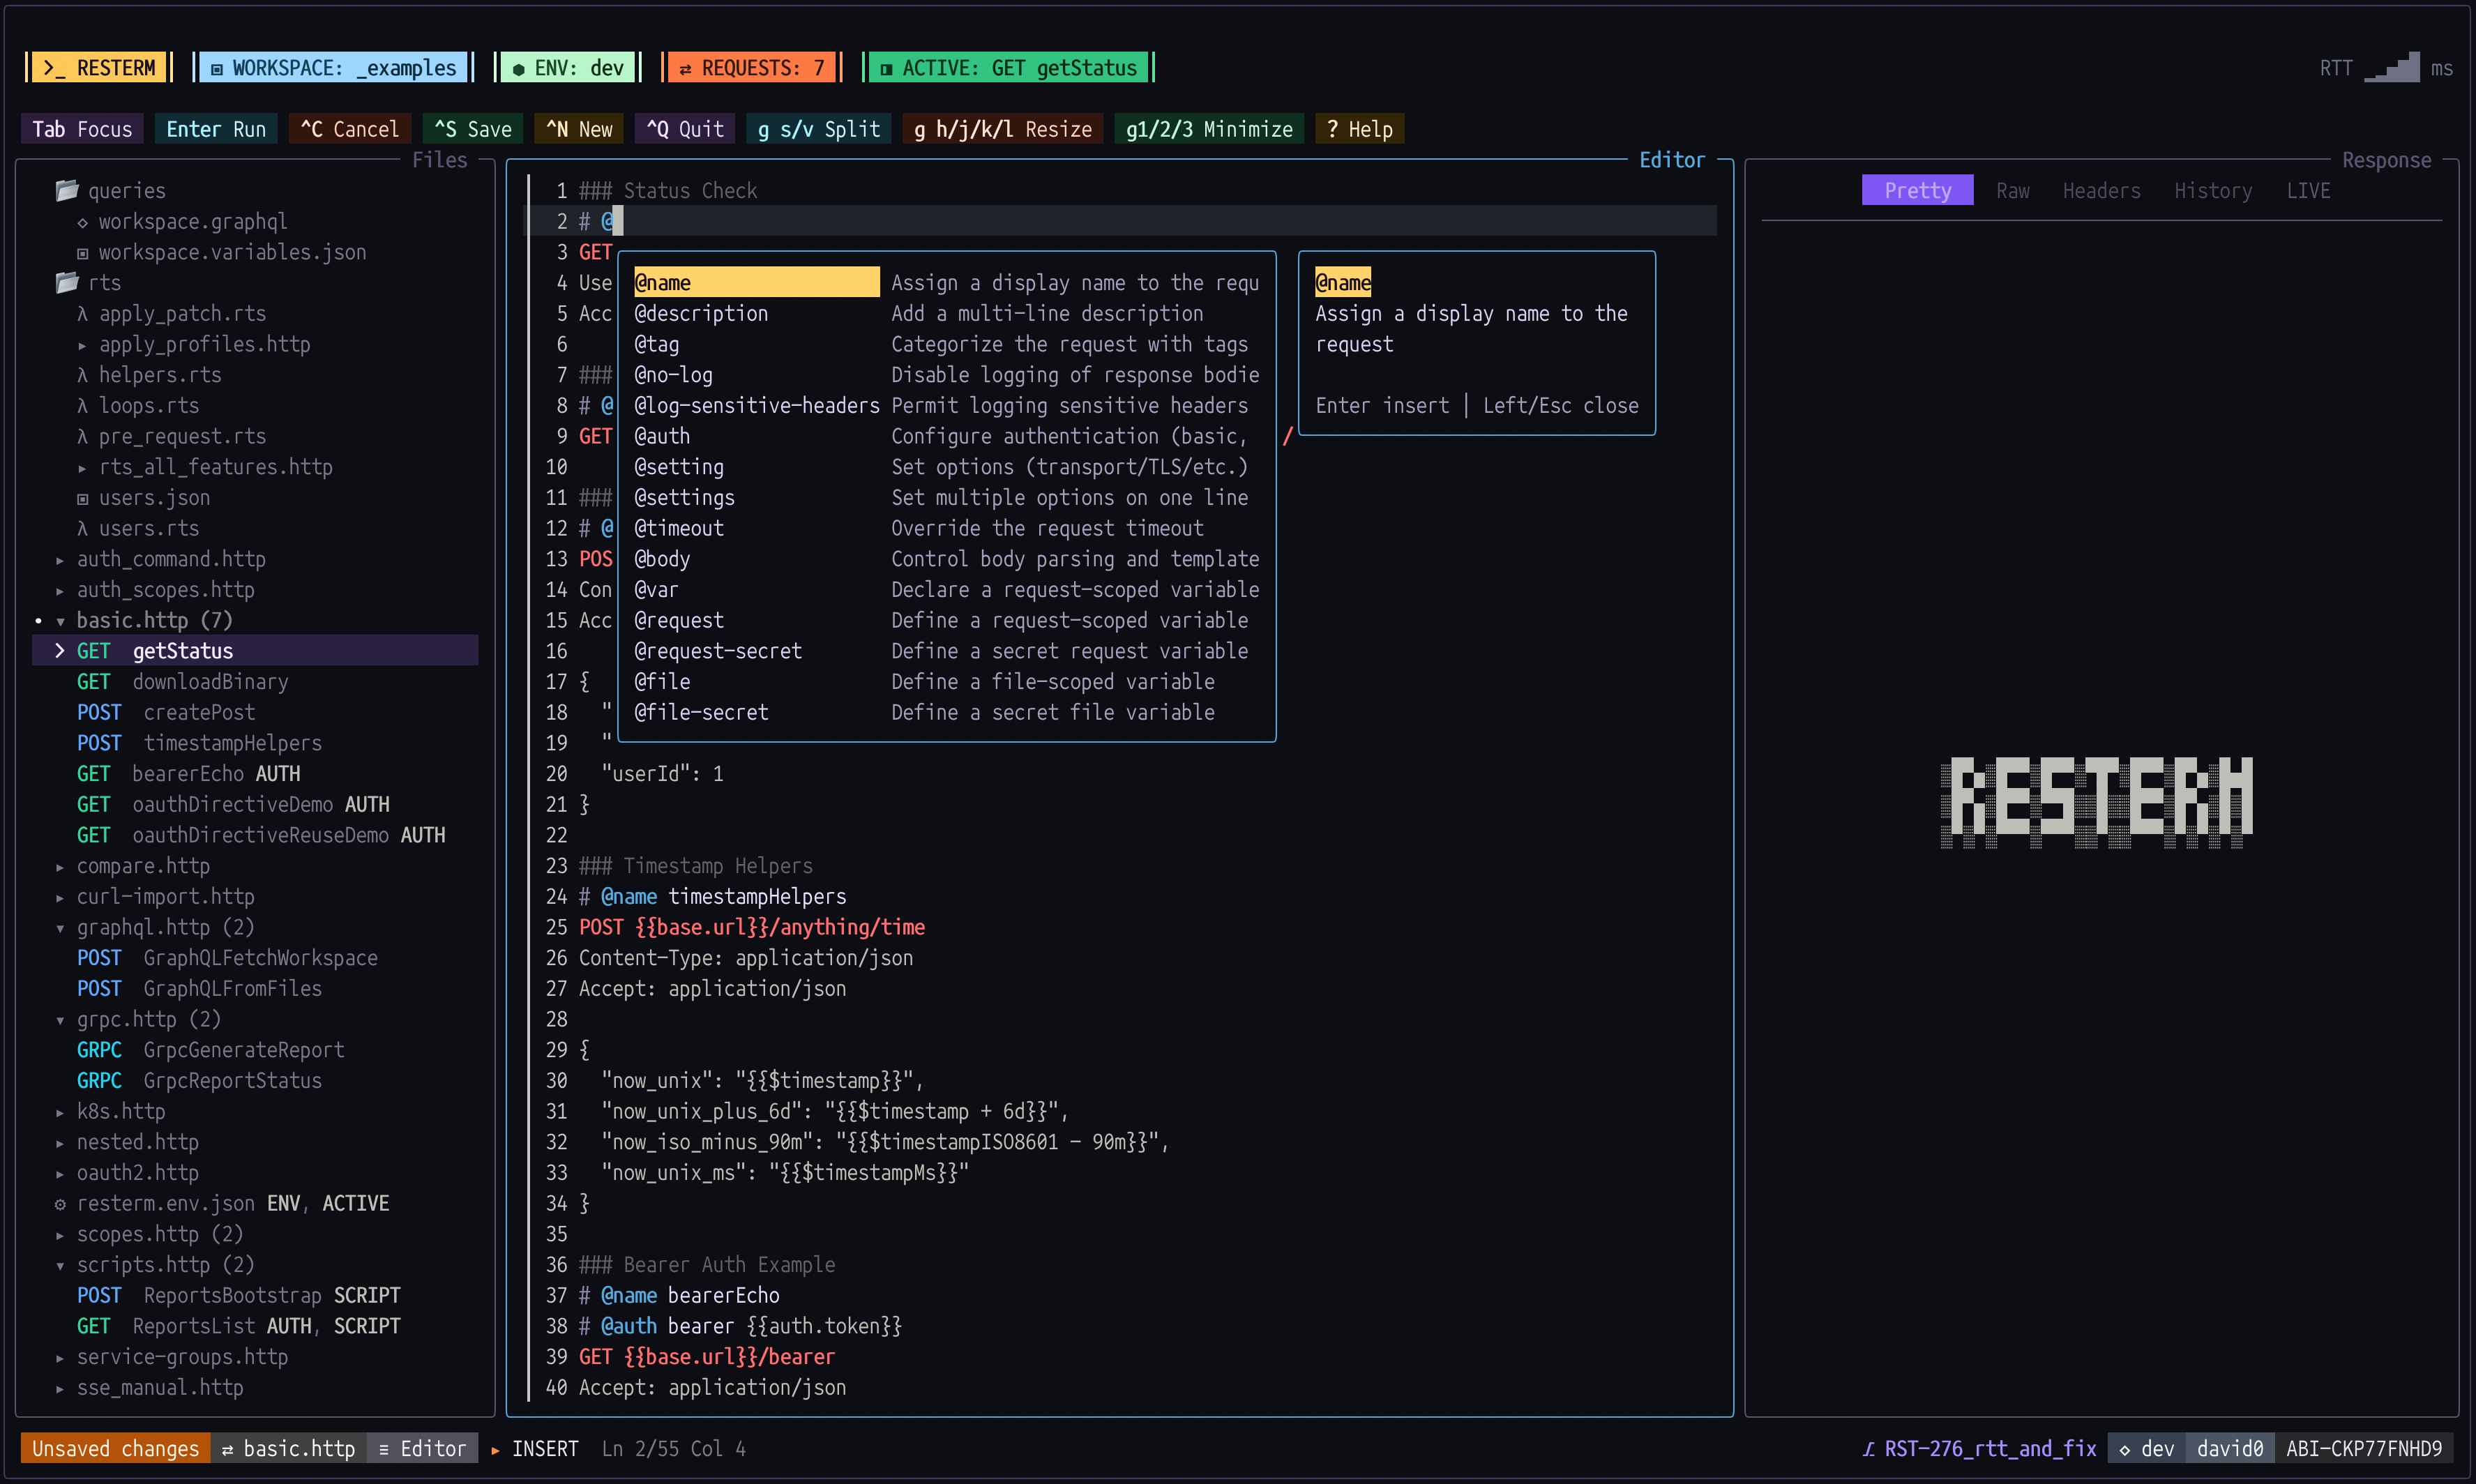 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL, gRPC, WebSocket and SSE. Plain .http files you can diff and version, with scripted tests, workflows, mocks,…
 xalgorix/xalgorix
Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF…
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 bifrost-proxy/bifrost
High-performance HTTP/HTTPS/SOCKS5 MITM proxy in Rust with TLS interception, rule-based request rewriting, traffic capture, breakpoints, script…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
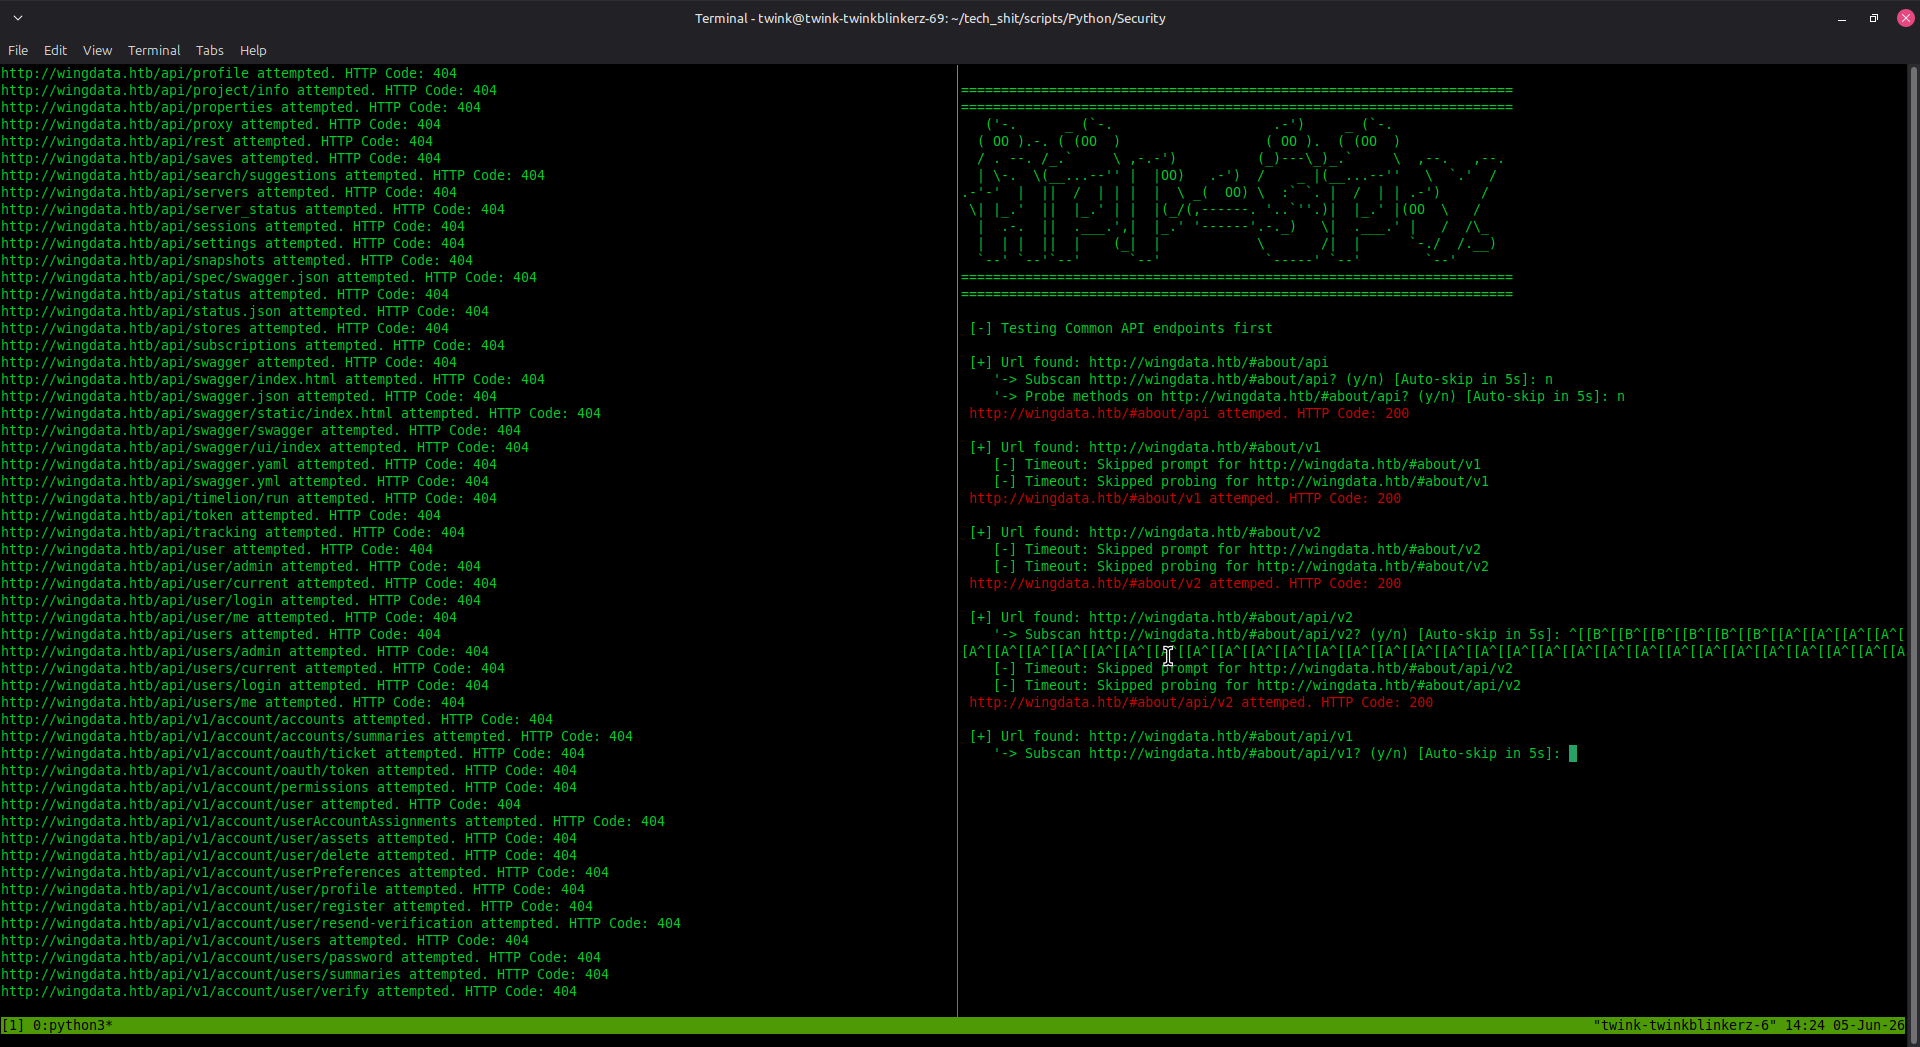 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.