
sleigh
 lifting-bits/sleigh
CMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
binary-analysiscode-analysisdynamic-code-analysis+4
191
lifting-bits/sleighCMake build of Ghidra's SLEIGH processor specification library, providing standalone disassembly and p-code lifting engines for reverse engineering…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 lolcaken/javascript-deobfuscator
Deobfuscator for javascript-obfuscator 5.x output (string arrays, control-flow flattening, self-defending, RC4/base64)
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 12000 CVEs
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 murrez/cve-2026-101110
Python 3 PoC and mass exploit for CVE-2026-101110, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Book Library <=6.4.6 via…
 murrez/cve-2026-100752
Python 3 PoC and mass exploit for CVE-2026-100752, an unauthenticated SQL injection in OrdaSoft Joomla Real Estate Manager <=6.7.8 via the…
 murrez/cve-2026-100721
Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
 antid00t/cve-2026-15989
Python PoC scanner for CVE-2026-15989, exploiting unauthenticated role injection in WordPress Super Forms to create admin accounts and verify access.
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 devcop95/bugbounty-lab101
A complete bug bounty workspace for HackerOne researchers. Includes scope enforcement, automated recon/vuln pipeline (400+ tools), report templates,…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
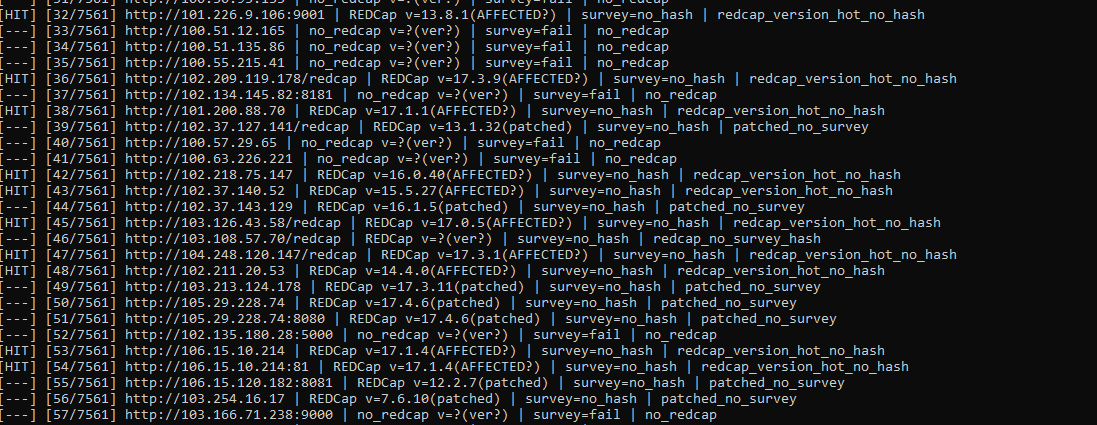 yulisec/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…
 murrez/cve-2026-13355
Python PoC scanner and exploit for CVE-2026-13355, an unauthenticated admin privilege escalation in Meta Box AIO WordPress plugins, with FOFA mass…