
CVE-2026-101110
 murrez/cve-2026-101110
Python 3 PoC and mass exploit for CVE-2026-101110, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Book Library <=6.4.6 via…
exploitationinformation-gatheringpenetration-testing+6
murrez/cve-2026-101110Python 3 PoC and mass exploit for CVE-2026-101110, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Book Library <=6.4.6 via…
 danielmadsendk/servicenow-cve-2025-11449-cve-2025-11450-mitigation-script
Automated detection and remediation of ServiceNow UI Macro vulnerabilities (CVE-2025-11449, CVE-2025-11450) by encoding sysparm_ parameters to…
 ianxtianxt/sleuthql
SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。
 m0rath/detect-log4j-exploitable
Bash script to detect Log4j (CVE-2021-44228) exploitable systems by scanning running Java processes for vulnerable log4j-core components without…
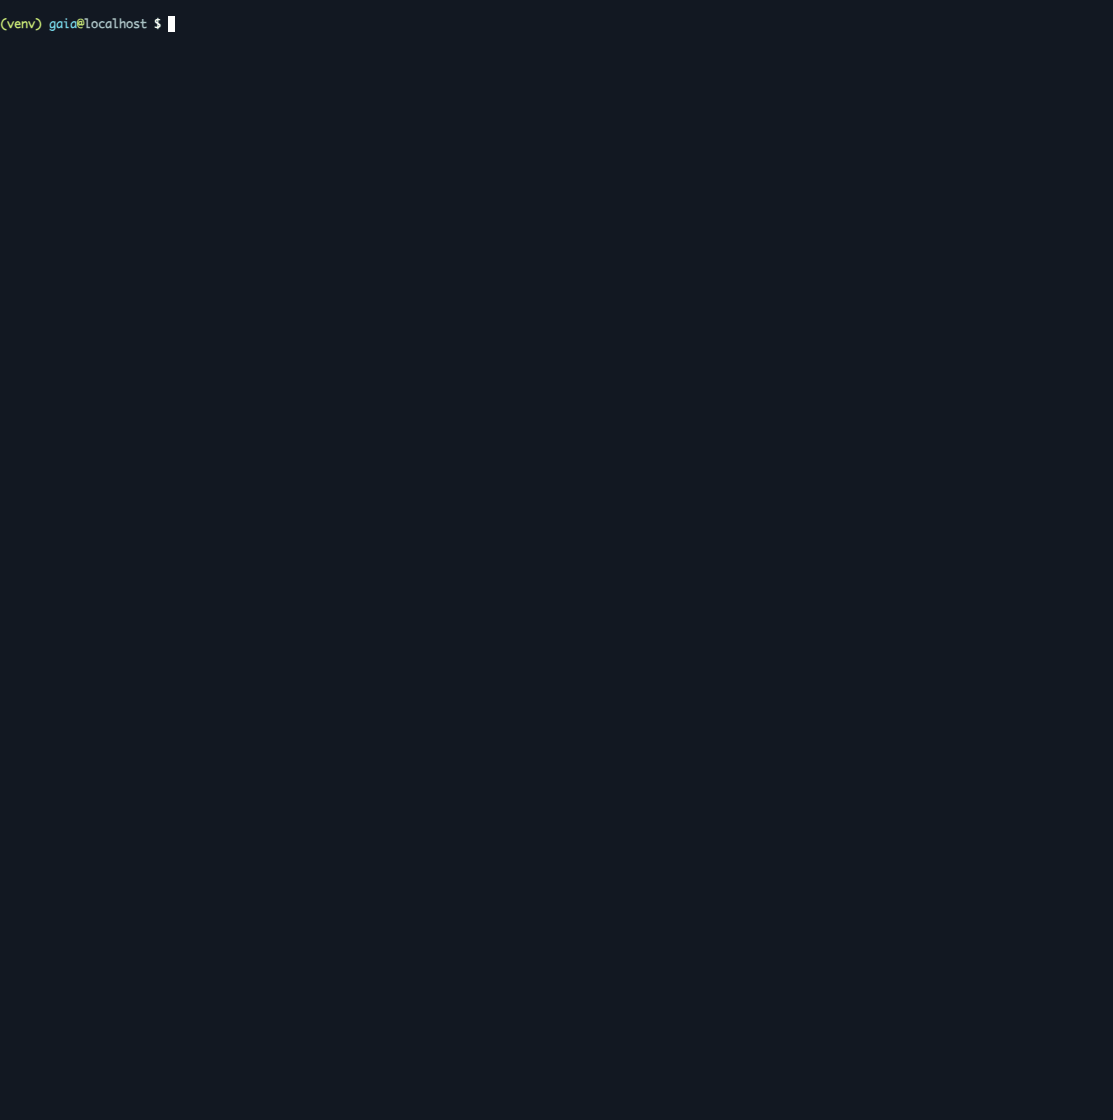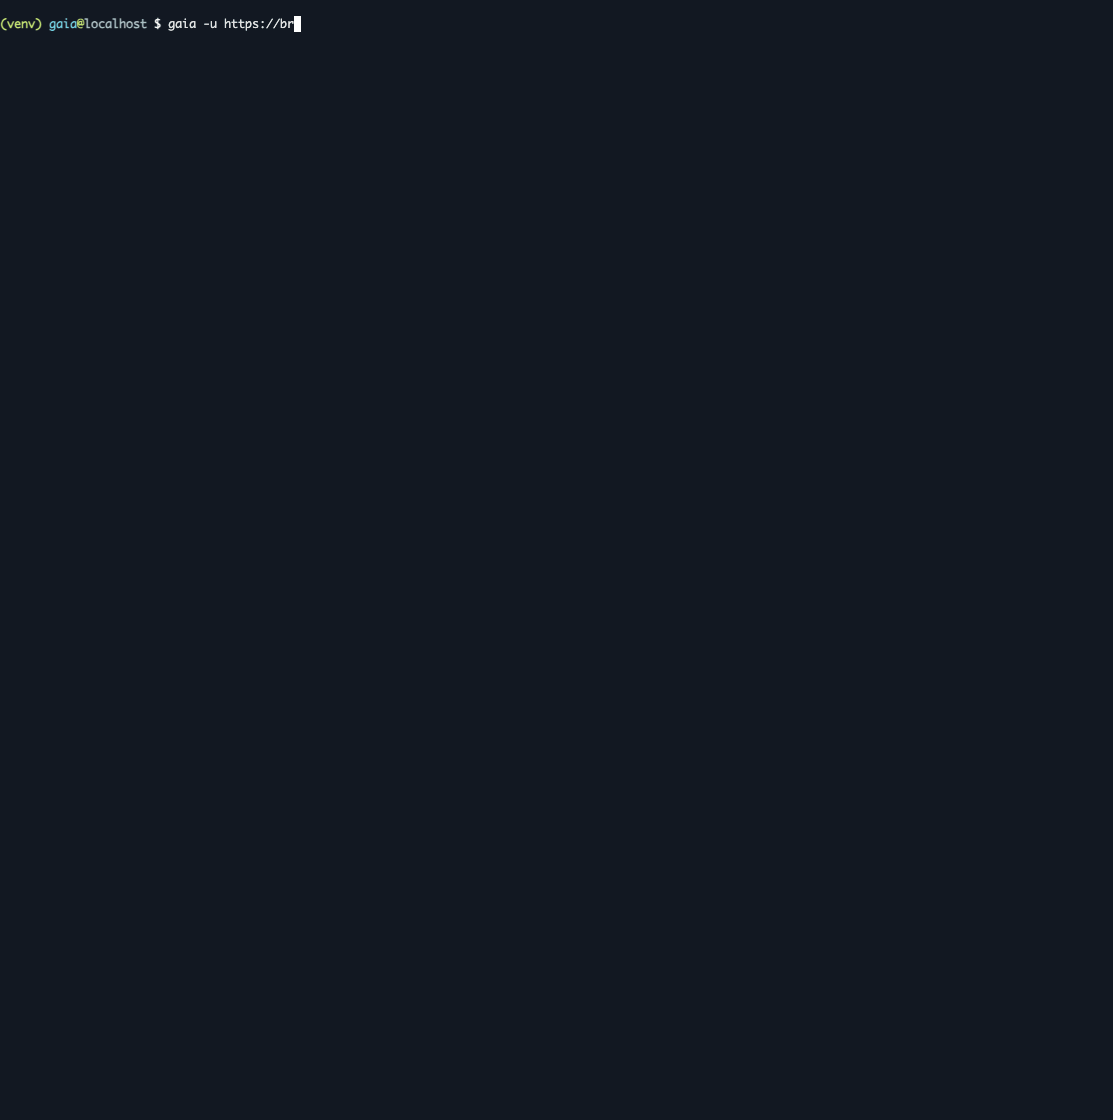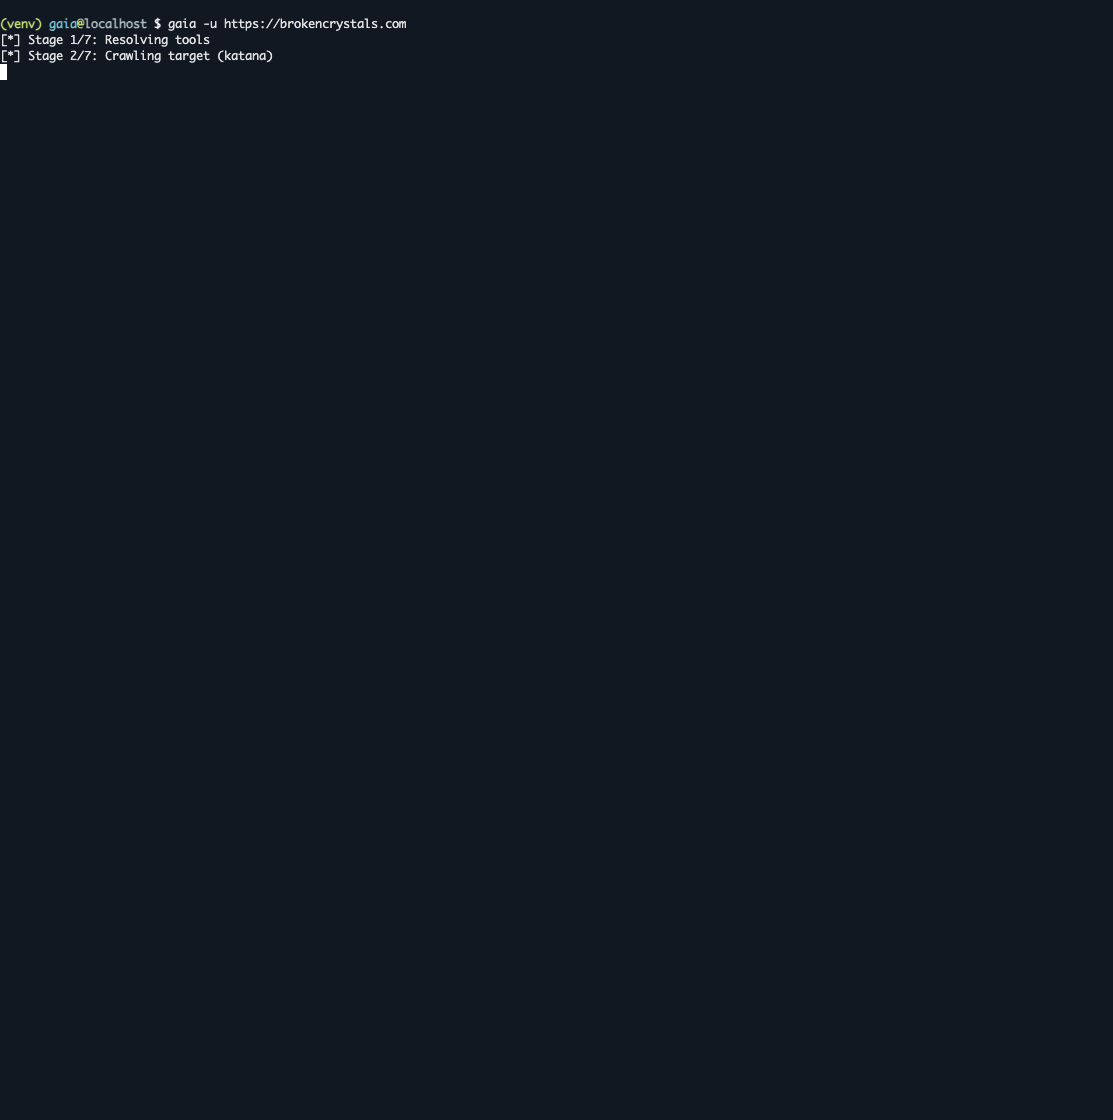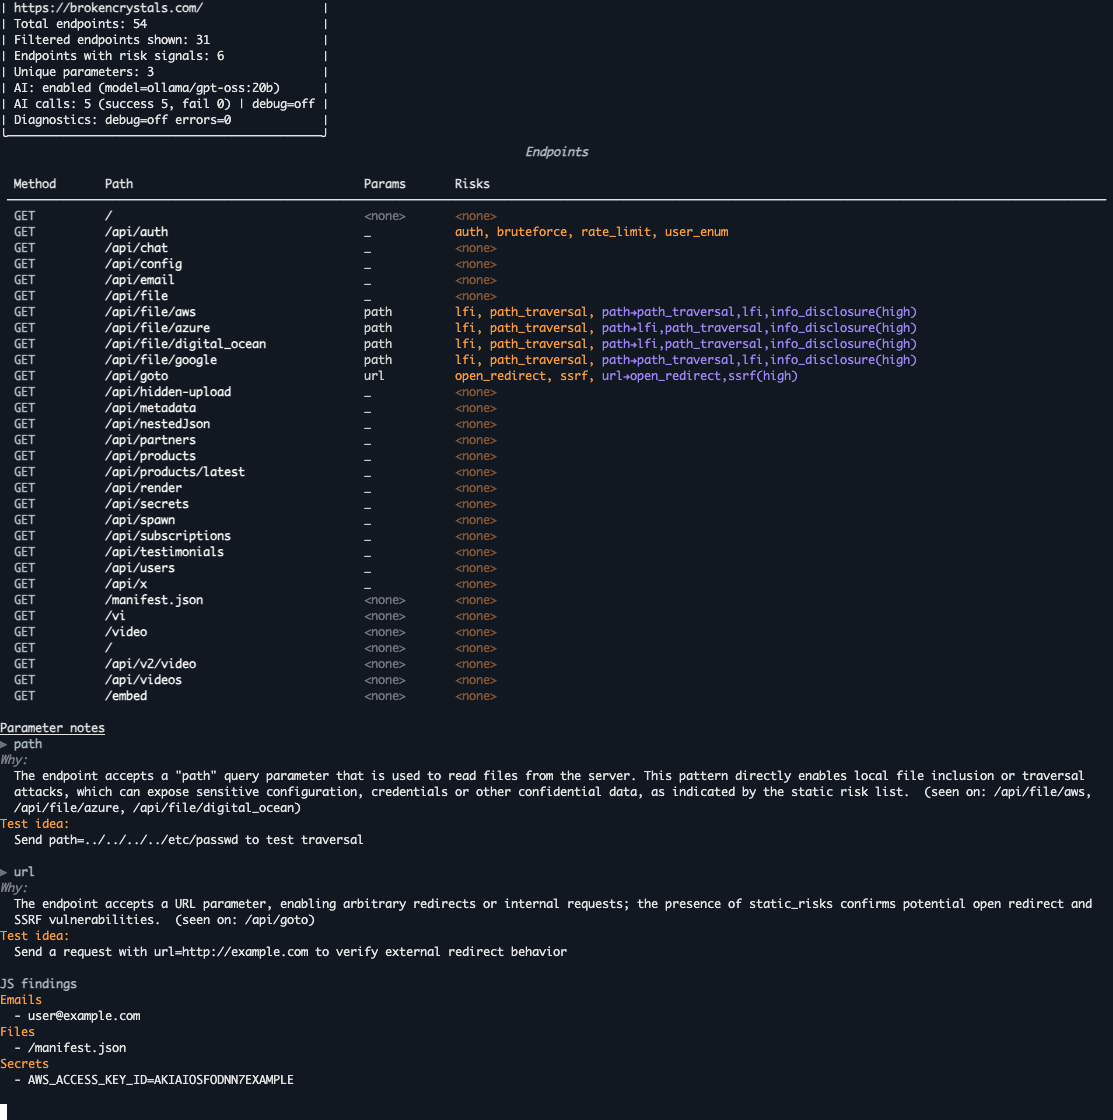 oksuzkayra/gaia
Attack surface discovery and AI-assisted triage for security researchers. Endpoint & parameter mapping with actionable testing hints.
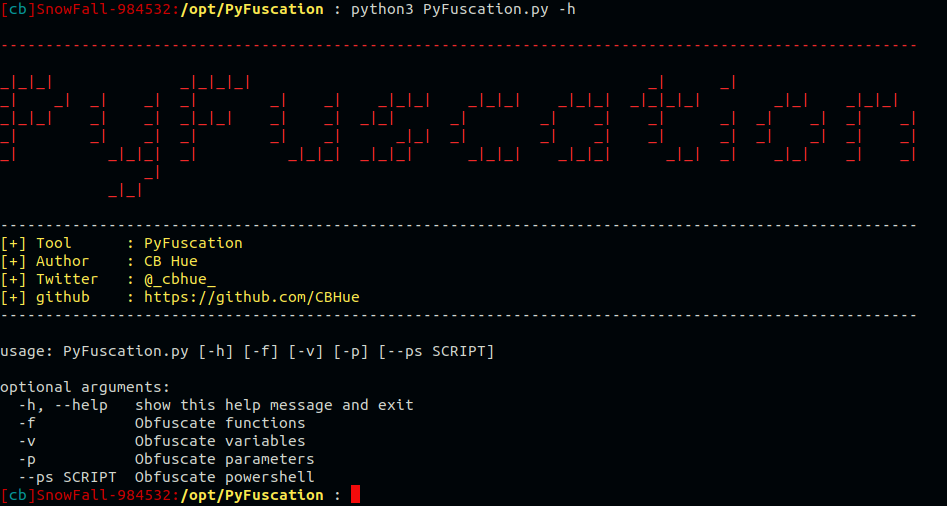 cbhue/pyfuscation
Obfuscate powershell scripts by replacing Function names, Variables and Parameters.
 naibowang/easyspider
A visual no-code/code-free web crawler/spider易采集:一个可视化浏览器自动化测试/数据采集/网页爬虫软件,可以无代码图形化的设计和执行爬虫任务。别名:ServiceWrapper面向Web应用的智能化服务封装系统。