

QuietPhase
 d3lightfu1/quietphase
Pwsh tool for AD Group Enumeration Auditing
configuration-auditingdefensive-toolsidentity-management+5
d3lightfu1/quietphasePwsh tool for AD Group Enumeration Auditing
 baarai/artex
LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and…
 trickest/inventory
Automated attack surface inventory for 800+ public bug bounty programs, running scheduled subdomain enumeration, permutation, DNS and web server…
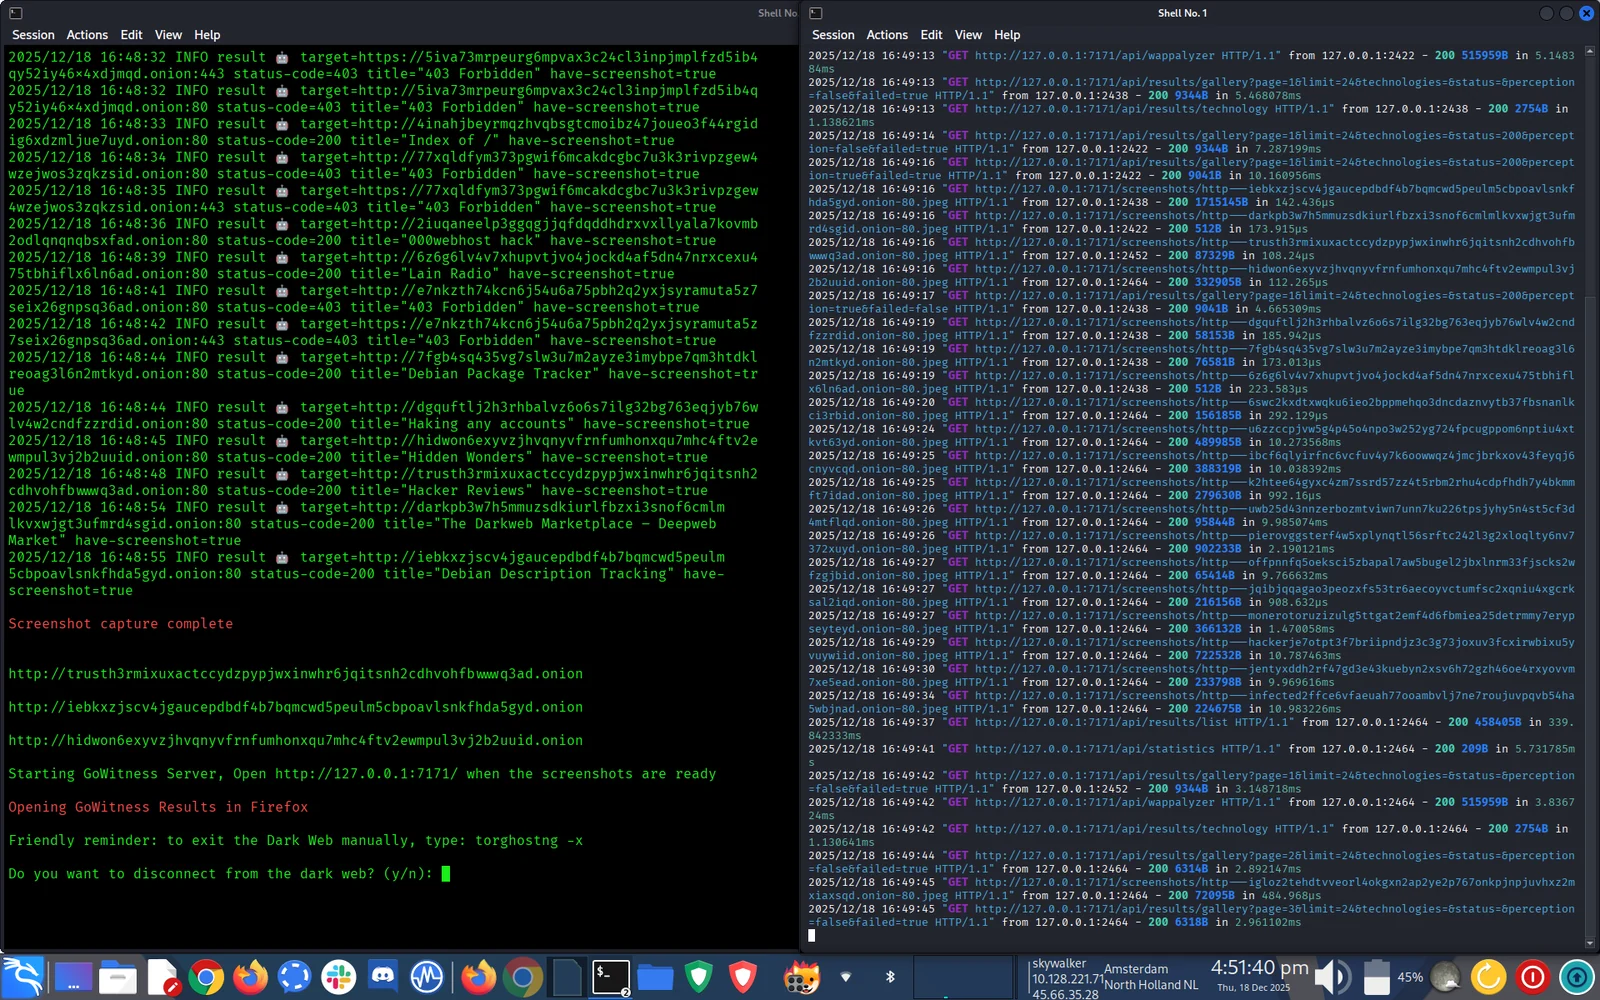 aryanguenthner/darkfox
CTI Cyber Threat Intelligence OSINT Dark Web Deep Web Research. Ransomware gang information gathering tool.
 mikemeliz/torcrawl.py
Crawl and extract (regular or onion) webpages through TOR network
 jarryshaw/darc
Darkweb crawler that uses requests and Selenium workers to fetch pages, capture headers and cookies, extract links, and save rendered screenshots for…
 dedsecinside/torbot
Crawls .onion sites over Tor to collect page titles, hostnames, and link relationships, exporting JSON trees and visualizations for dark web OSINT…
 andreyglauzer/vigilantonion
🐍 - Crawler on tor network sites, searching for keywords.
 cro-thehacker/v1ew-s0urce
Python-based penetration testing framework and reconnaissance toolkit offering port scanning, information gathering, and network scanning modules for…
 gmh5225/ollama-hunter
Scans Shodan for publicly exposed Ollama and llama.cpp servers, enumerating hosts, locations, and available models for security research.
 1n3/sn1per-mcp
MCP server that lets AI assistants drive a self-hosted Sn1per install, running scoped, audited scans and returning findings, ports, subdomains and…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.
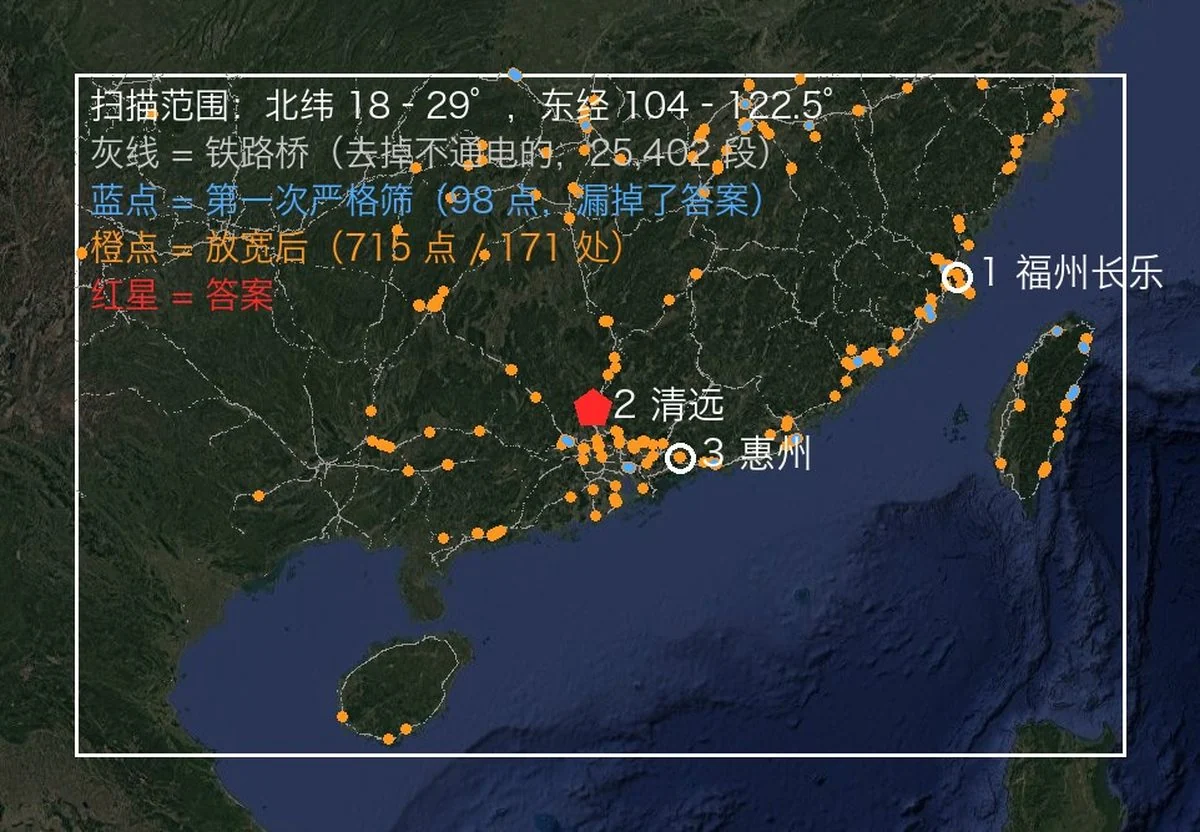 oldcircle/geo-sleuth
An agent skill that finds where a photo was taken — OpenStreetMap geometry, elevation skylines, satellite imagery and street view — and shows its…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 vulncheck-oss/go-exploit-cache
A utility for producing an HTTP cache database to use with go-exploit
 trustedsec/spoonmap
Python wrapper around masscan and nmap for large-scale port discovery, host discovery, banner grabbing, and NSE-based vulnerability scanning across…
 vqkro/higernes
a passive OSINT toolkit in python and c++ usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…