

ADRecon
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
defensive-toolsdigital-forensicsincident-response+6
980
adrecon/adreconPowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 wayang1337/cve-2026-80099
Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated
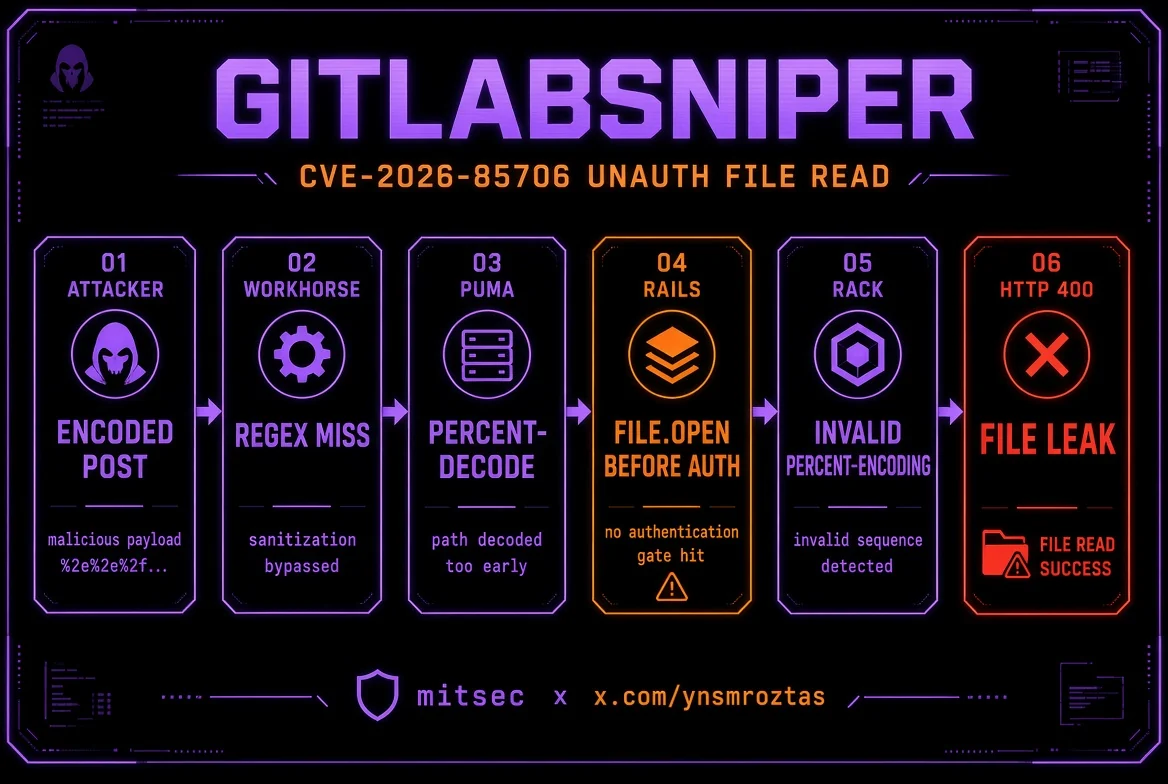 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 virustotal/vt-py
The official Python 3 client library for VirusTotal
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 bishopfox/proxylistreliabilitycheck
Perl script to test the reliability of a list of open web proxies.
 ianxtianxt/sleuthql
SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
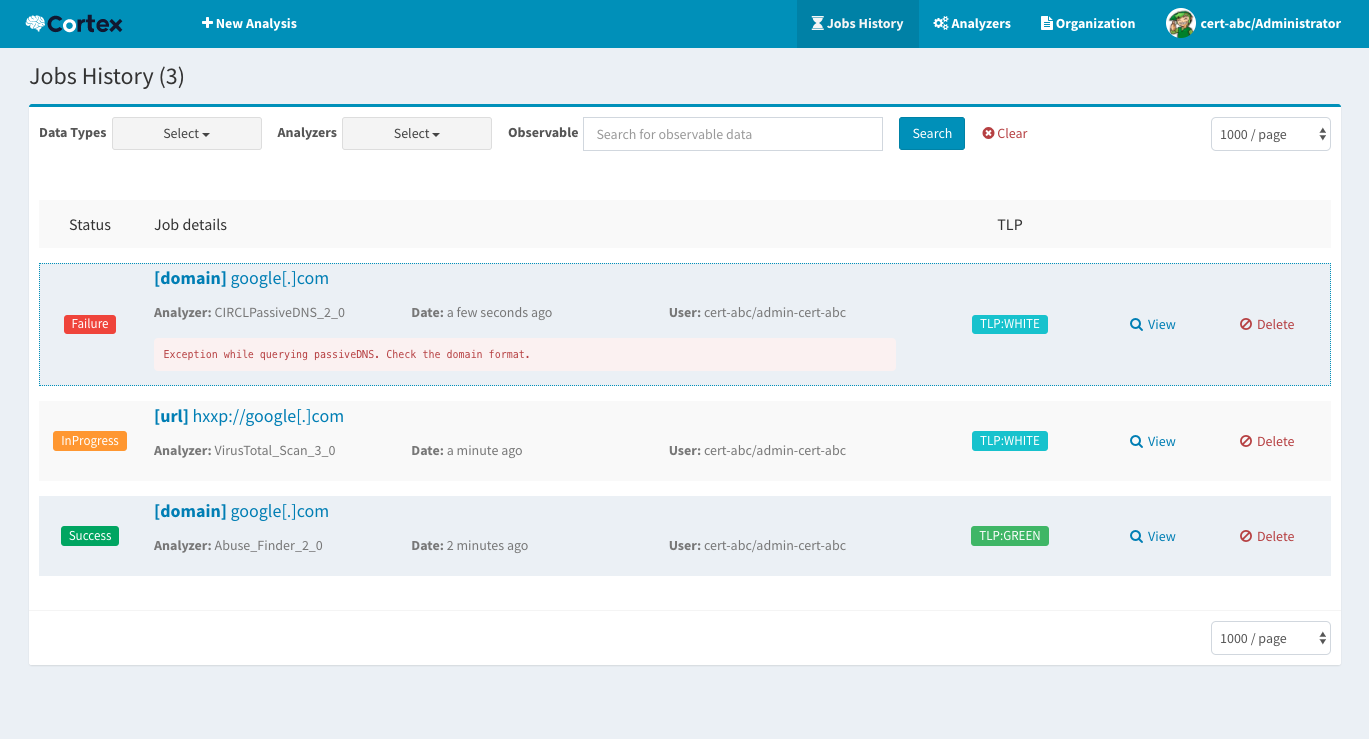 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
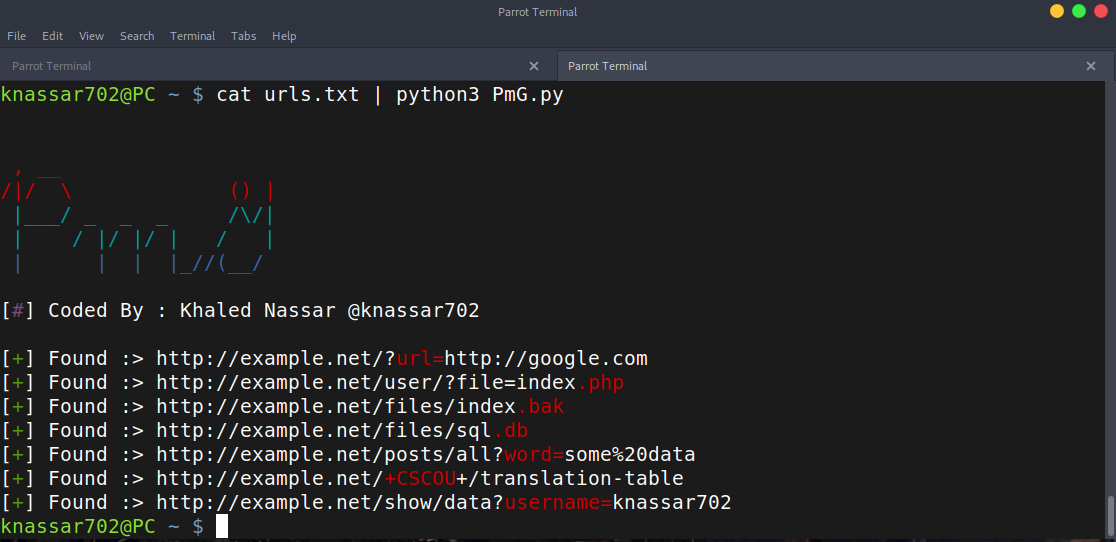 mindpatch/pmg
Extract parameters/paths from urls
 nu11secur1ty/burpsuite-grand-master-tools
Modular toolkit for pentesters that converts Burp Suite captured HTTP requests into browsable URLs and automates workflow actions with auditable…
 nu11secur1ty/dns-resolve-checker
Bash script for DNS resolution checking, enabling quick domain-to-IP lookups and basic network reconnaissance from the command line.
 projectdiscovery/httpx-action
HTTP Web Server probing
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.
 danmcinerney/elite-proxy-finder
Finds public elite anonymity proxies and concurrently tests them