

CanoP
 openbreach/canop
Static analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
ai-securitycode-analysisdefensive-tools+7
4
openbreach/canopStatic analysis CLI that scans AI-generated code for vulnerabilities like SQL injection, unsafe reflection, and hardcoded secrets, with SARIF export…
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 ianxtianxt/sleuthql
SleuthQL是基于python3所开发的一款,用于批量爬行站点可能存在sql的地址。并且可以配合burp+sqlmap进行批量注入。 对比sqlmap手动单线程一个一个注入点的去识别,方便了很多。
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 phxbandit/scripts-and-tools
Scripts and utilities to help your hacking needs
 dzonerzy/gowapt
Go Web Application Penetration Test
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 neo23x0/mongobleed-detector
Detection Script for MongoBleed Exploitation
 tjnull/cygor
An modular asset discovery framework written in python to automate the repeating manual work
 adrees-basheer/wp2shell-vulnerability-scanner
Scan WordPress installations for wp2shell vulnerabilities (CVE-2026-63030 + CVE-2026-60137). Identifies full RCE and SQL injection risks across…
 77philly/cve-2024-7456scripts
Bash and Node.js scripts to automate SQL injection exploitation against vulnerable web applications, targeting CVE-2024-7456.
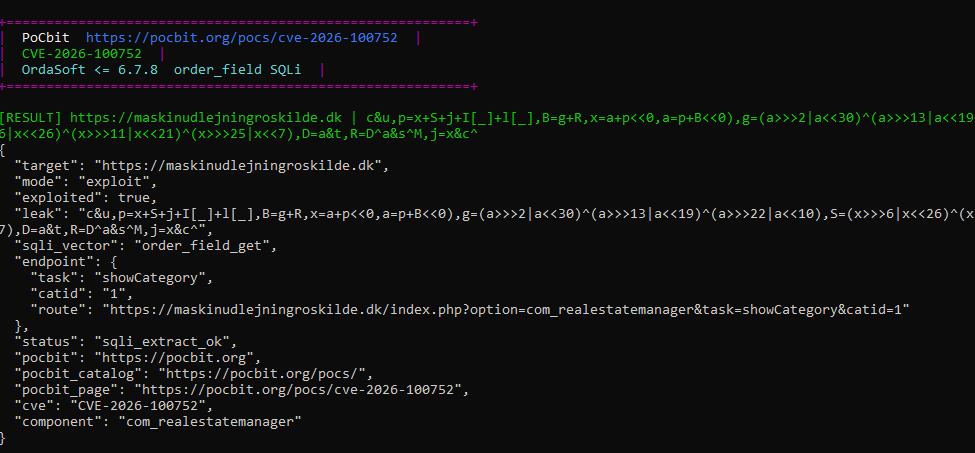 murrez/cve-2026-100752
Python 3 PoC and mass exploit for CVE-2026-100752, an unauthenticated SQL injection in OrdaSoft Joomla Real Estate Manager <=6.7.8 via the…
 murrez/cve-2026-101110
Python 3 PoC and mass exploit for CVE-2026-101110, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Book Library <=6.4.6 via…