
discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
api-security-testingcloud-securitycontainer-security+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
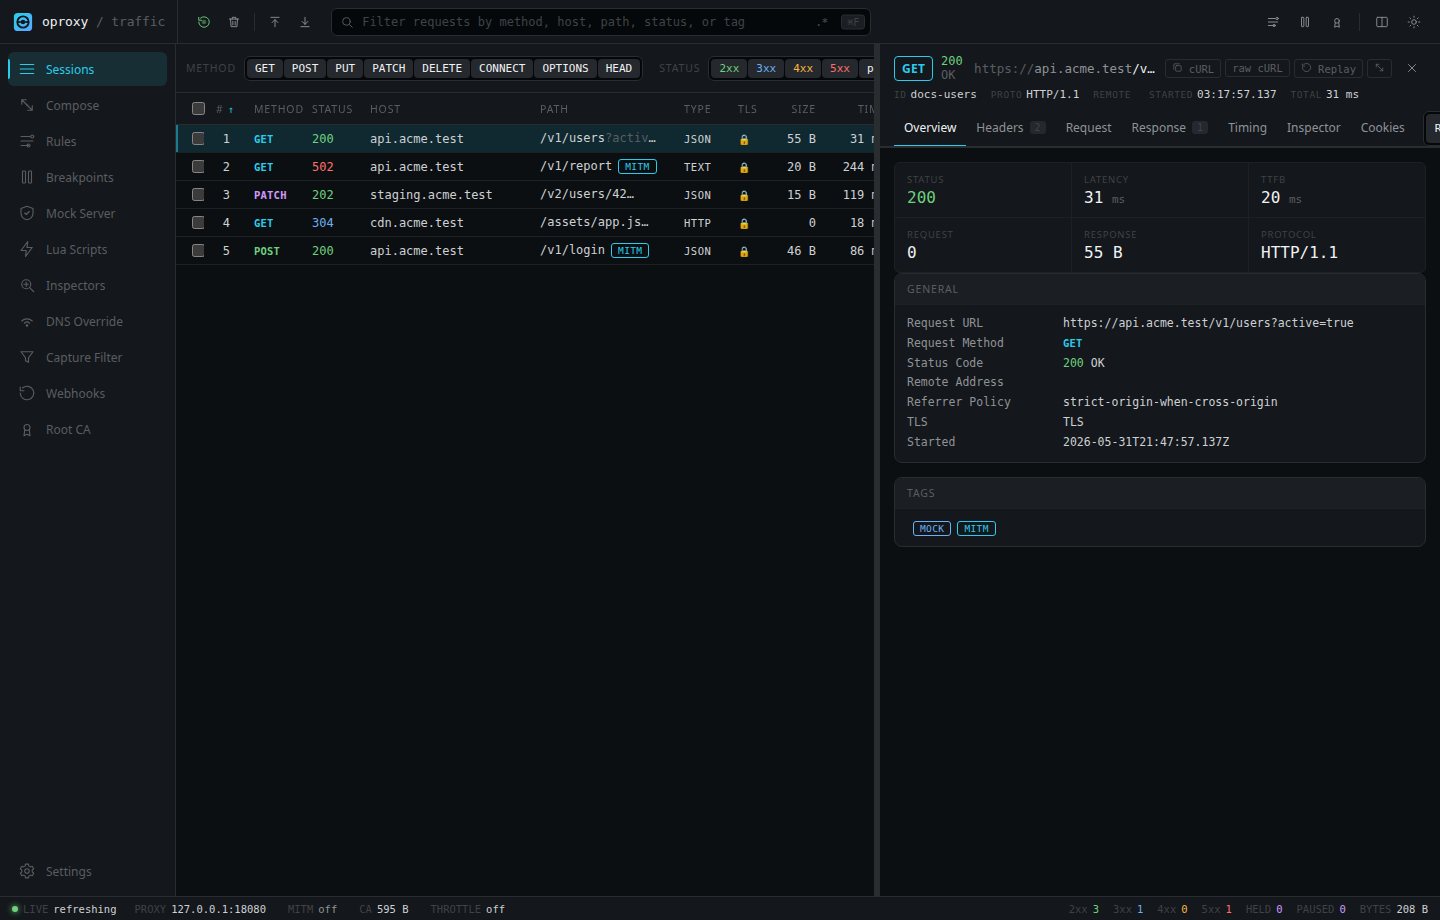 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
 infobyte/alexafaraday
Alexa skill example for Faraday API
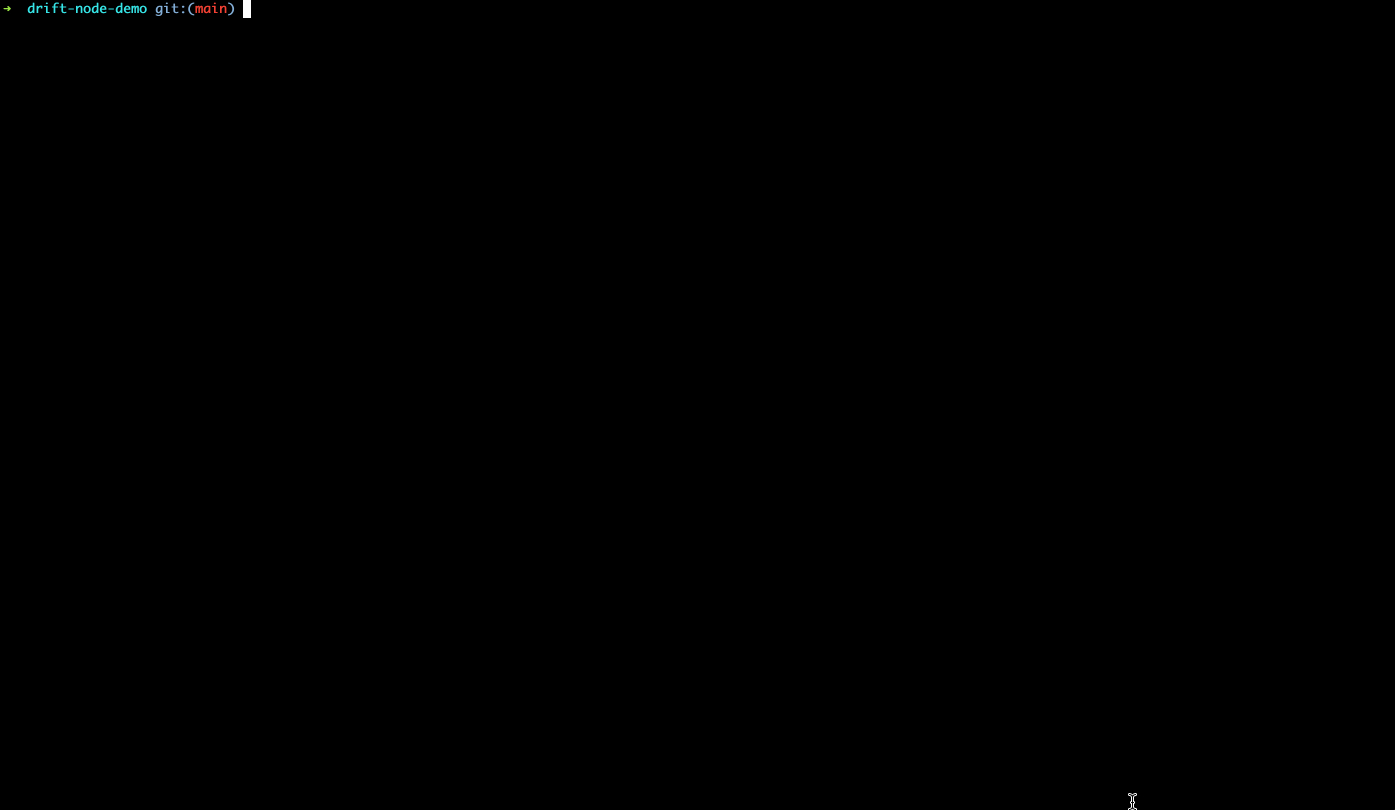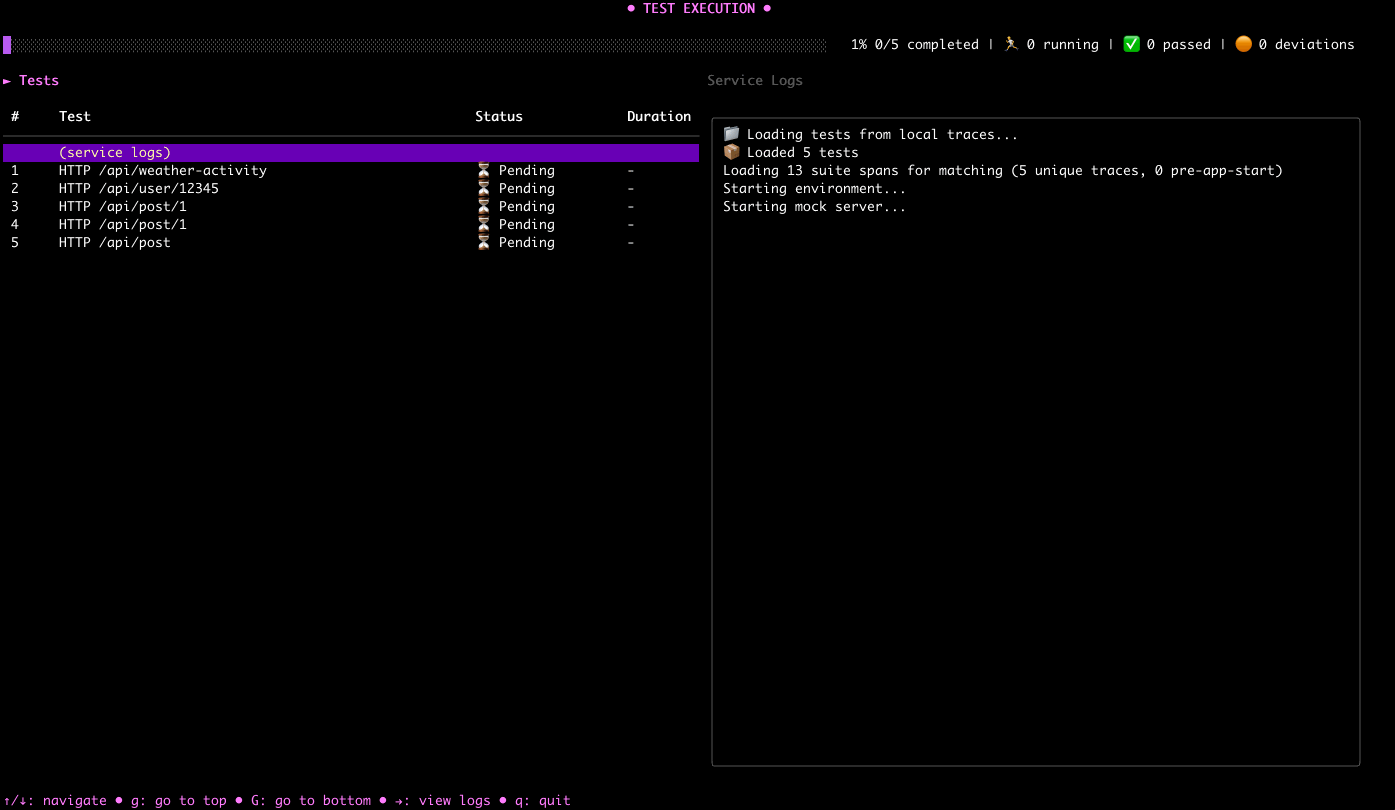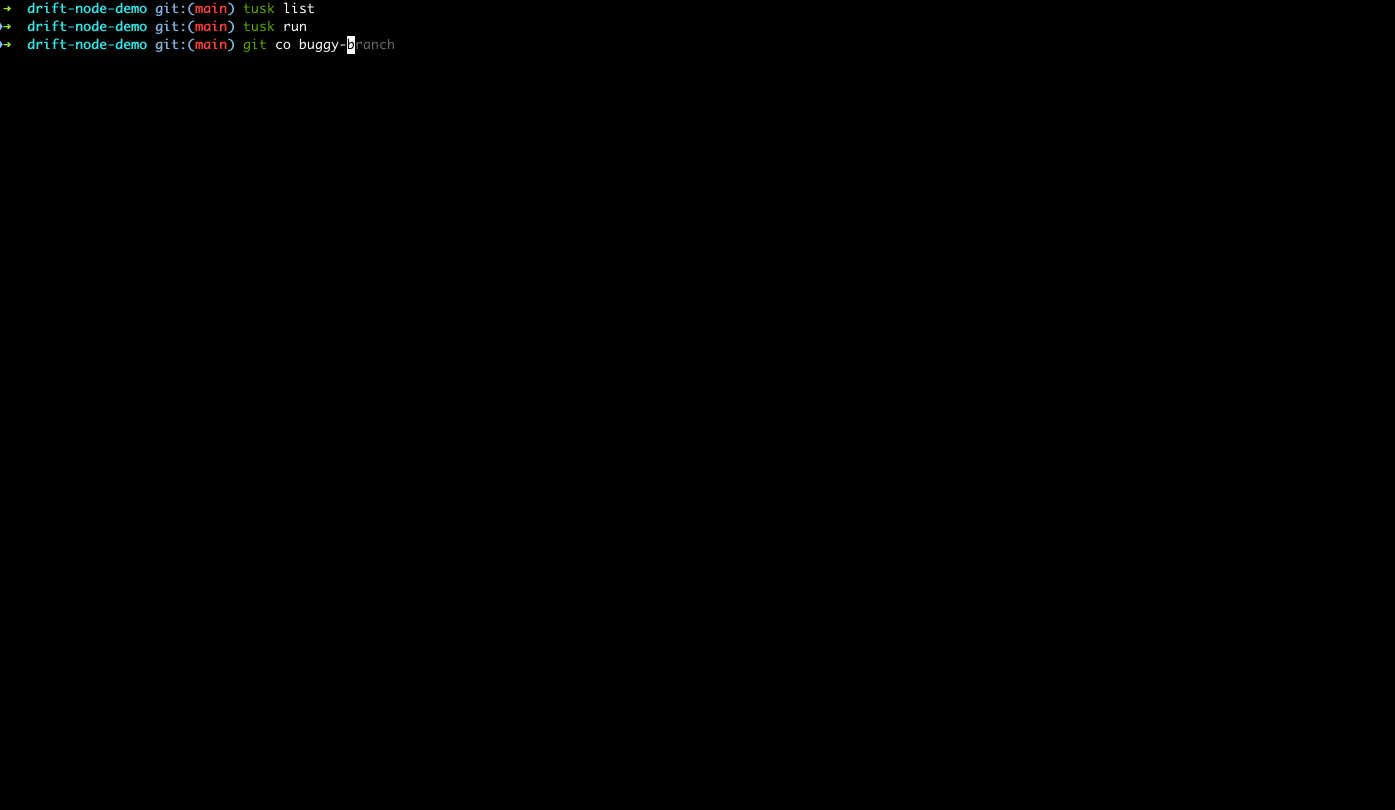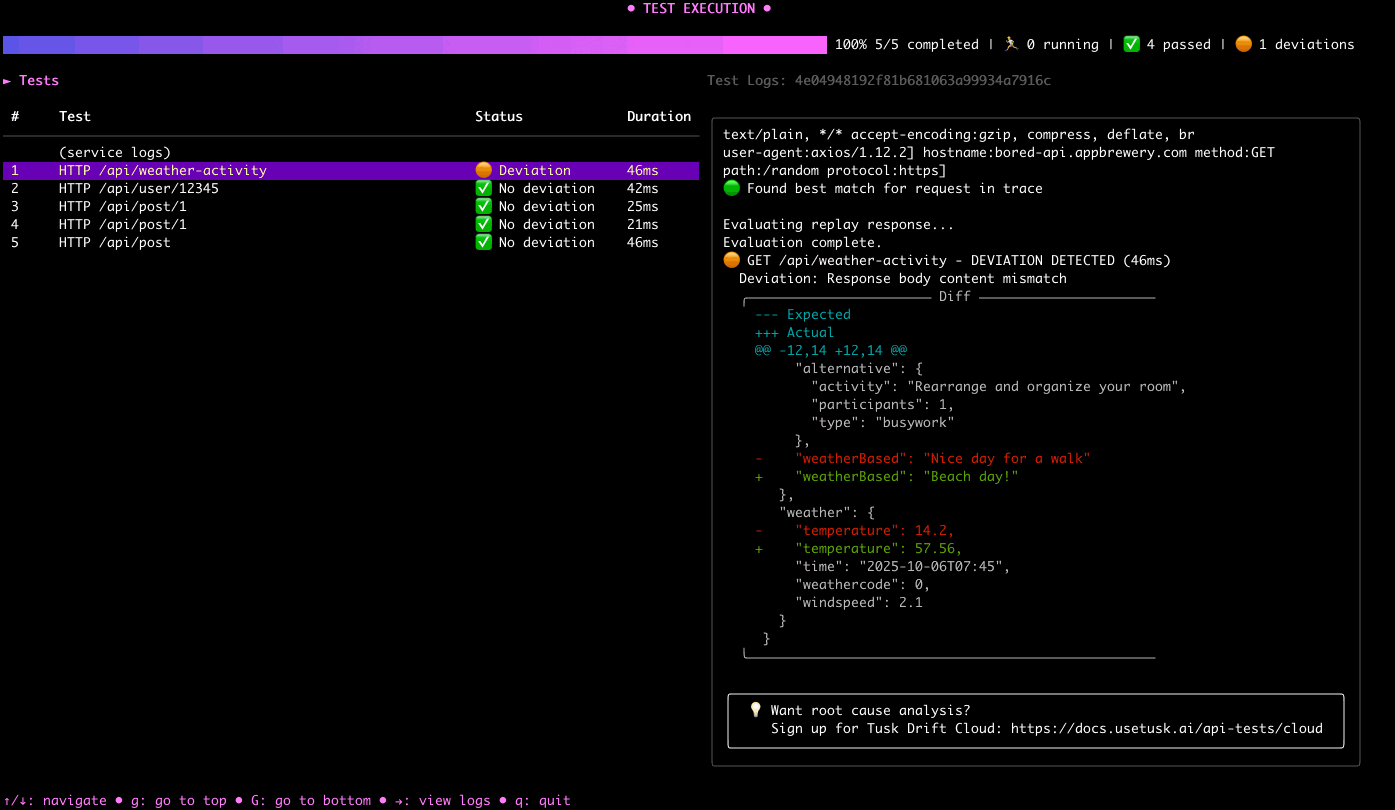 use-tusk/drift-node-sdk
Node.js SDK for capturing and replaying API calls made to/from your service
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
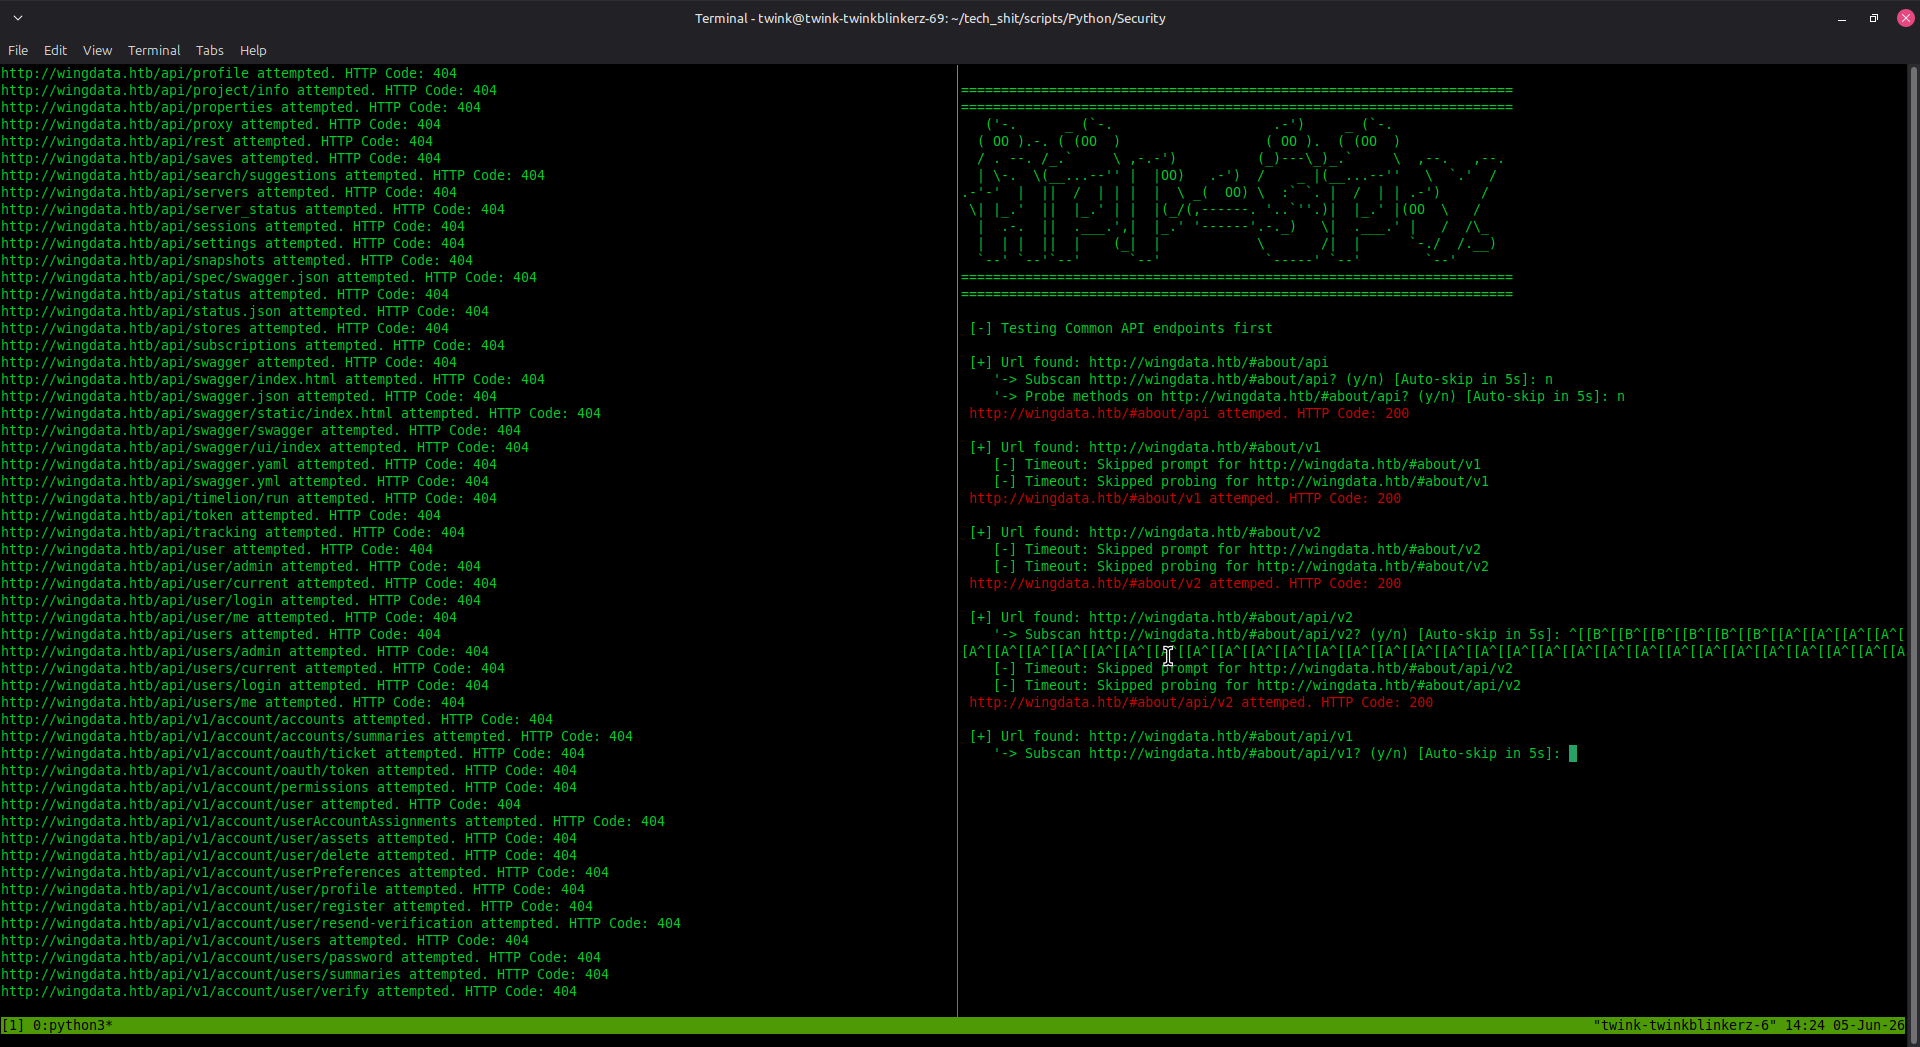 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 owasp/zsc
OWASP ZSC - Shellcode/Obfuscate Code Generator https://www.secologist.com/
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 pentestgeek/burpcommander
Ruby command-line interface to Burp Suite's REST API
 saffron-health/libretto
The AI toolkit for building reliable browser automations
 vertexcover-io/strot
API Scraper Agent for Web API's
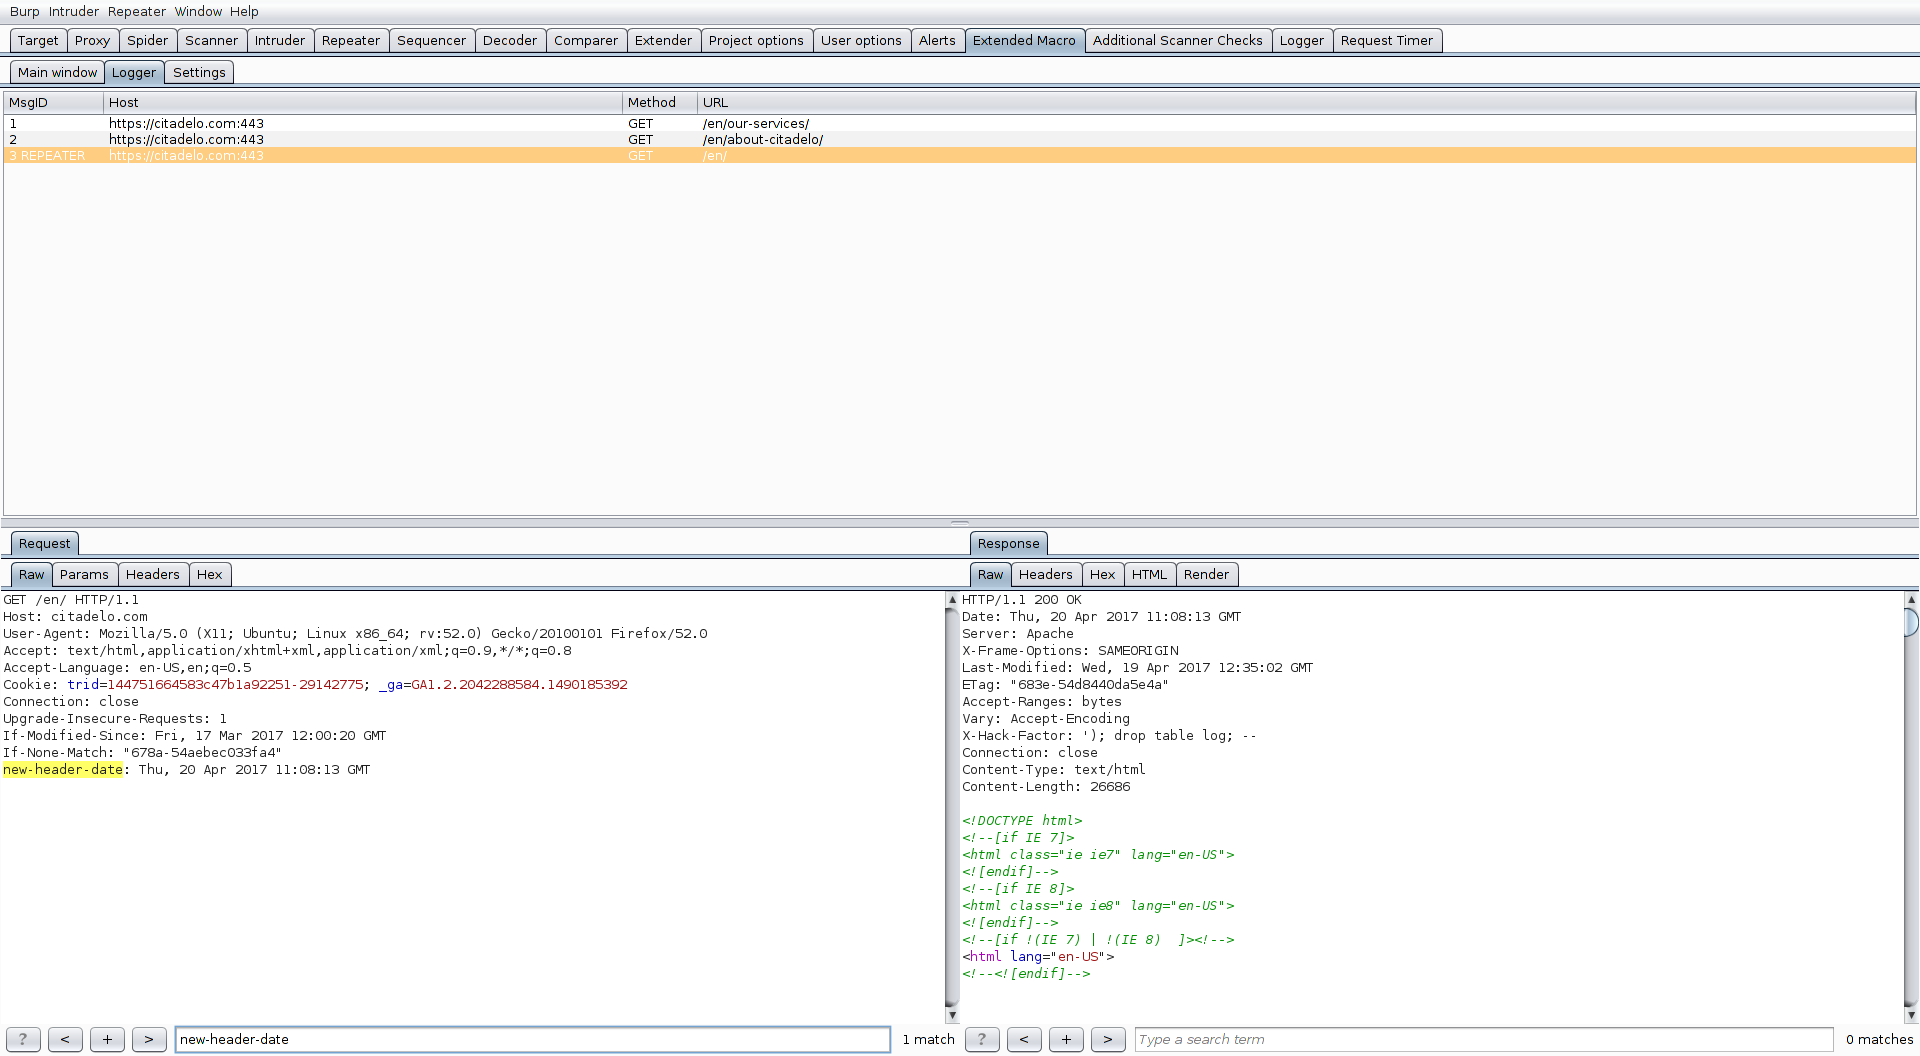 fruh/extendedmacro
ExtendedMacro - BurpSuite plugin providing extended macro functionality
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.