

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 facebookincubator/ttpforge
The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
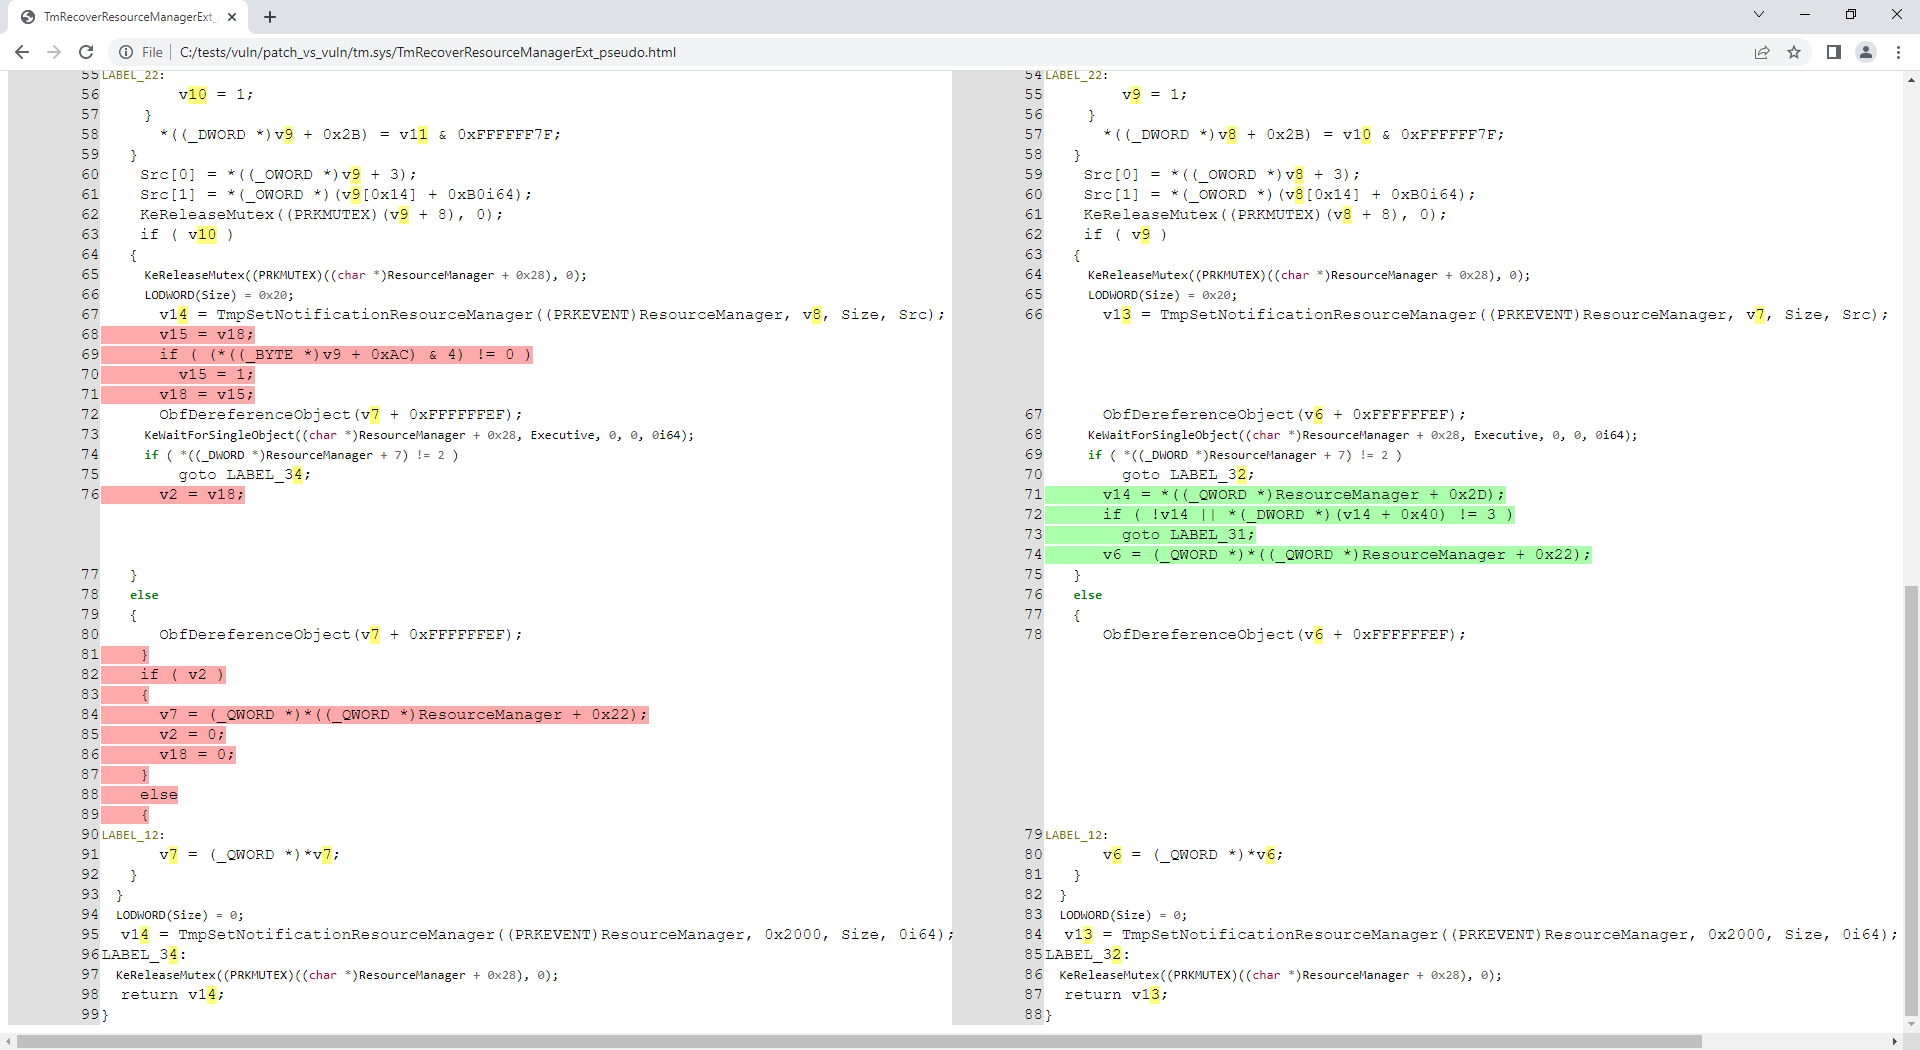 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 gmh5225/aggressor-aggregator
A helper script for consolidating Aggressor and BOF repositories into a single CNA for Cobalt Strike.
 randomrobbiebf/wordpress-php-object-helper
Know a plugin has a php object exploit but need to find which lib to use?
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 skiller9090/lucifer
A Powerful Penetration Tool For Automating Penetration Tasks Such As Local Privilege Escalation, Enumeration, Exfiltration and More... Use Or Build…
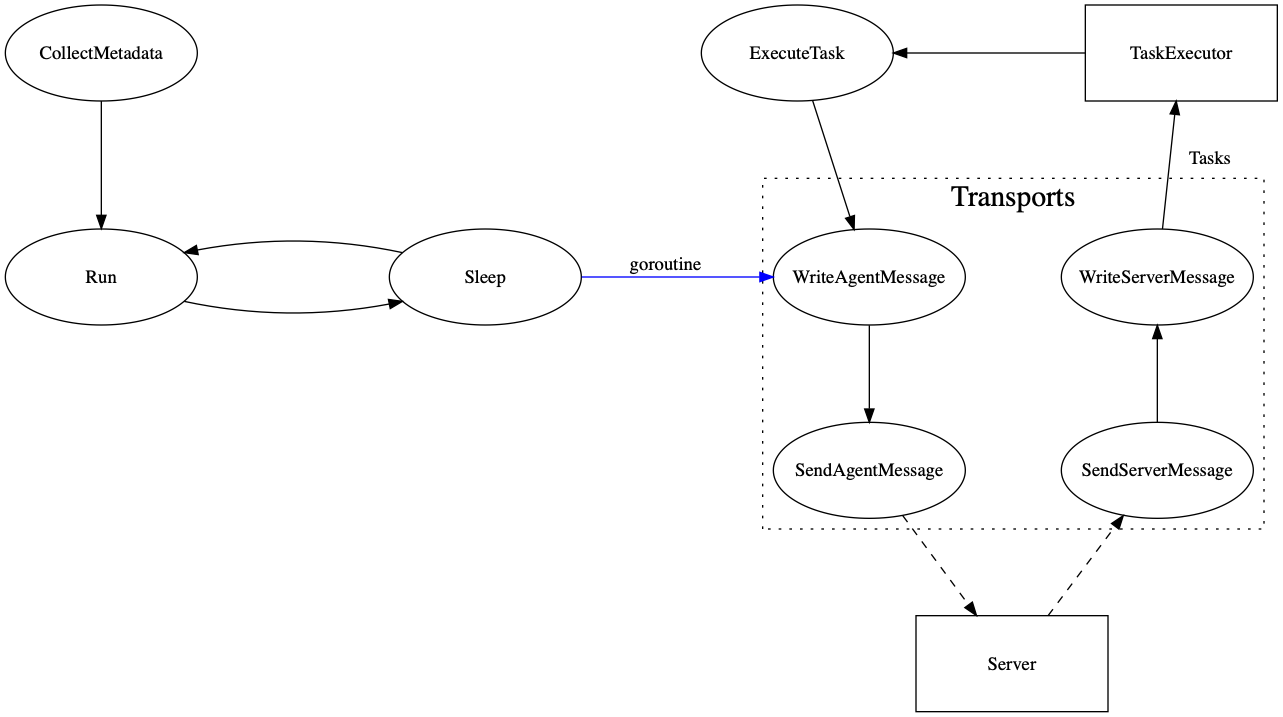 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 horizon3ai/h3-cli
CLI tool for the Horizon3.ai API
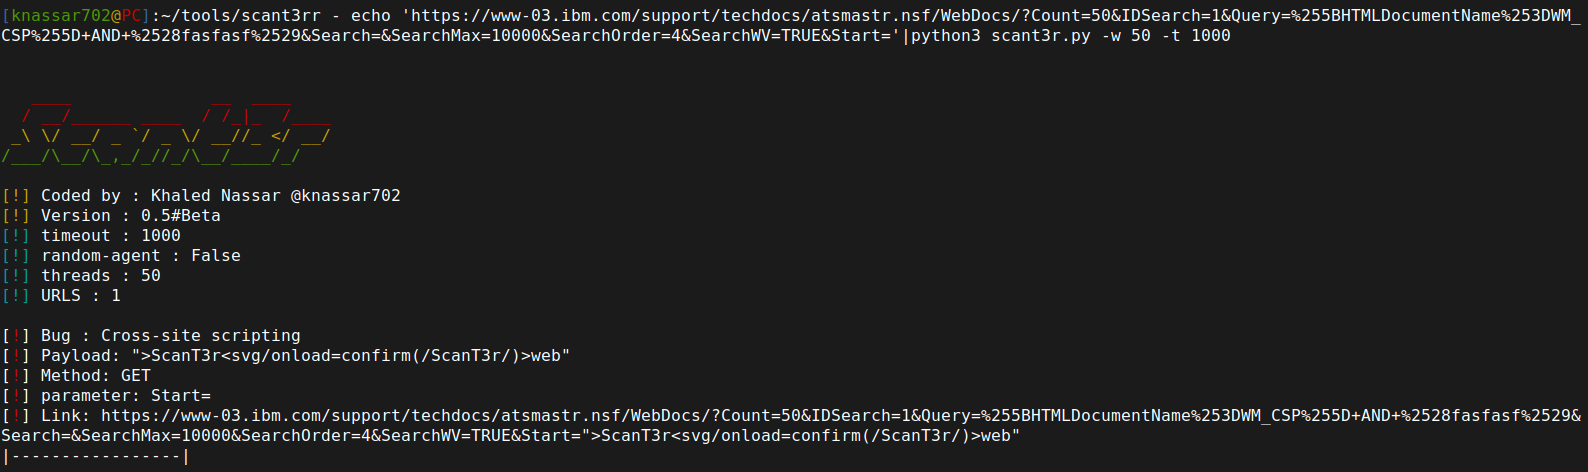 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 trustedsec/ptf
The Penetration Testers Framework (PTF) is a way for modular support for up-to-date tools.
 berylliumsec/nebula
AI-powered penetration testing assistant for automating recon, note-taking, and vulnerability analysis.
 threatexpress/threatbox
Ansible-based attack platform for deploying and managing a standardized Linux penetration testing environment with automated tool installation,…
 nccgroup/autopwn
Specify targets and run sets of tools against them